A pair of serious vulnerabilities in the CreditNirvana platform would have allowed attackers to access troves of detailed sensitive information, including emails, texts, and credit reports.
A flaw in NGINX's HTTP/2 support can allow an attacker to run code on servers with HTTP/2 enabled, without needing to log in.
The decade-old flaw, CVE-2026-123007, dubbed "nginx2root," has been present in NGINX's open-source code since version 1.9.5, released on September 22, 2015. Fixed versions 1.31.9 and 1.30.7 came out today.
F5, the company behind NGINX, says attackers can run code where
Six critical vulnerabilities in F5 BIG-IP allow an attacker to crash the Traffic Management Microkernel (TMM) without logging in, disrupting traffic until the TMM restarts.
Each flaw needs a specific setup on a virtual server: an iRule that uses a particular command, or an APM policy that includes two particular kinds of agent.
F5, which makes BIG-IP, disclosed the flaws today and says they
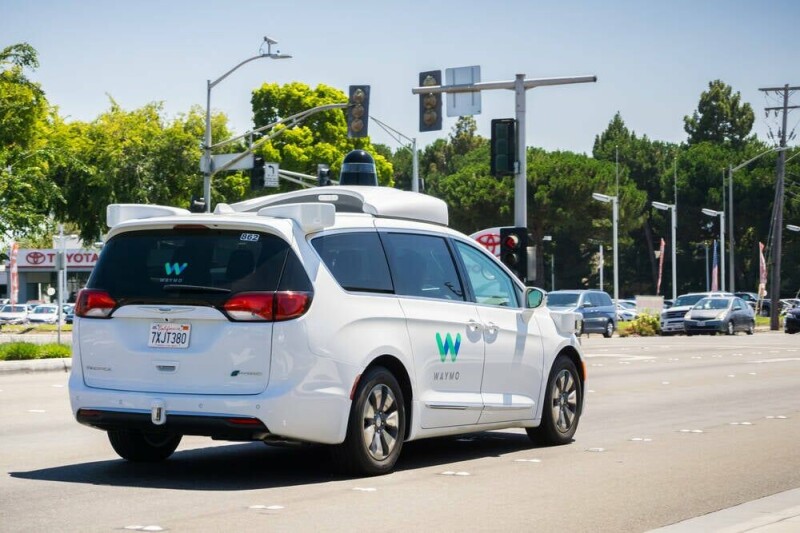
Waymo has suspended driverless freeway rides across the US after California regulators intervened over robotaxis entering construction zones and trying to bypass highway patrol vehicles. California's DMV banned Waymo from offering driverless trips on its freeways on Wednesday, November 11. The same day, Waymo pulled the handbrake on its freeway services countrywide. The move affects all areas in which Waymo operates on freeways, including San Francisco, Los Angeles, Miami, Phoenix, and Austin. The Alphabet-owned company has not indicated how long the suspension will last. Waymo says freeway testing will continue with trained specialists behind the wheel. Jonathan Groveman, spokesperson for the California DMV, told the Associated Press that the organization imposed the ban following two incidents involving Waymo's robotaxis that posed an "imminent hazard to public safety." On November 5, three of the company's driverless cars entered an active construction zone on US 101 near Burlingame, south of San Francisco. The second incident occurred the following day, and in footage shared widely online, a Waymo vehicle can be seen trying to drive around highway patrol vehicles conducting a traffic break – a maneuver used to slow or stop traffic. "The Department determined that Waymo's driverless freeway operations pose an imminent hazard to public safety due to recurring incursions by its vehicles into active construction zones where construction workers, vehicles and equipment are present," Groveman said in the statement. Groveman said the DMV had already imposed restrictions and required corrective action following similar incidents on May 18. Waymo subsequently recalled nearly 4,000 cars after some were caught ignoring road closure signs and cones designating construction zones in Phoenix and San Francisco. A separate recall covered software affecting nearly 3,800 robotaxis over problems including slowing on high-speed roadways and driving into floodwater. A Waymo spokesperson said that despite California's temporary ban, its robotaxis continue to operate on city streets across the US. "Safety is at the foundation of everything we do," they said. "Following recent freeway construction zone encounters on US 101 in California that did not involve any injuries or collisions, the California DMV has implemented an operating restriction on freeway operations in the state. "In alignment with our safety-first principles, we have also temporarily restricted freeway operations across our other operating markets to evaluate our performance. Our ride-hailing service continues to operate safely on surface streets, serving over half a million trips each week. "We are working with the California DMV and other state officials diligently and responsibly to resume freeway operations." Other nuisances and hazards caused by errant Waymos include clogging traffic in thick fog, driving into telephone poles, and killing cats and dogs. ®
Microsoft’s official agent framework package hosted on PyPI has been hijacked and now installs info-stealing malware, multiple security research firms have discovered. CEO Satya Nadella may be on stage trying to wow investors and customers at his company’s annual Ignite conference, but somewhere in the bowels of a building in Redmond his open source team is likely panicking at what appears to be unauthorized access to an administrator account on Microsoft’s Github organization. The problem package is Microsoft’s agent-framework, versions 1.26.1 and 1.26.2, researchers reported late yesterday and this morning. According to OX Security, version 1.26.1 was reverted to a safe version, but the attacker later uploaded 1.26.2 through Microsoft’s official PyPI publisher account, suggesting that, at least at the time of their report, the credentials hadn’t been locked down. Safe to say, but if you find either version in your environment assume you have some account security work to do. Microsoft agent-framework for Python boasts nearly 200,000 downloads a month and is used to build and deploy AI agents. As of those latest releases, it’s also being used to exfiltrate environment variables, credential files, and other secrets for Azure, Git, Docker, Hugging Face, and other sensitive developer services. To make matters worse, the package never needs to be imported to do its dirty work – all it takes is a Python interpreter with the package installed to start up – the infected package still pulls the genuine 1.26.0 version of Microsoft’s agent-framework in order to keep itself running and looking legitimate, while in the background it gathers up credentials, encrypts them as a base64-encoded chunk of JSON, and sends them off to a webhook.site address hard coded into the malware. It appears from researcher accounts that this is made to act fast, as the malware isn’t persistent and only runs as long as the malicious version of the agent-framework remains in a site-packages directory. What it does do, however, is not just look for credentials in the environment: It actually starts calling for new ones and collecting them, too. In particular, the malware requests fresh identity tokens from GitHub Actions, Azure DevOps, and Azure itself, which are exfiltrated to the same webhook site. “That combination of passive theft and active token requests makes it especially dangerous in cloud build environments, because even short-lived tokens are useful when they're exfiltrated right away,” said researchers at OpenSourceMalware. The agent-framework GitHub repo is offline as of writing. It’s been pointed out online that Microsoft’s repo for ONNX Runtime, an AI accelerator, is also offline. Other Microsoft repos remain available, and neither Microsoft nor security researchers have linked the ONNX repo’s pull to the malware campaign. “We have made some repositories private while we investigate malicious content,” a Microsoft spokesperson told The Register. “Our priority is to protect customers and the broader ecosystem. We are working to review and will take further action as needed.”® Updated at 1805 with comment from Microsoft.
A critical security flaw in Apache Roller, an open-source, Java-based blogging platform, has come under active exploitation in the wild, according to the Apache Software Foundation (ASF)
The vulnerability, tracked as CVE-2026-129448 (CVSS score: 9.8), is a case of unauthenticated deserialization in the XML-RPC endpoint that could lead to remote code execution.
"Deserialization of Untrusted
Artex and similar penetration testing tools allow newbie hackers to scan targeted systems for vulnerabilities and successfully wage attacks using prompts fed to chatbots.
Cyber insurance pricing has cooled. Marsh’s Global Insurance Market Index shows global cyber rates falling for a 13th consecutive quarter, with US rates recently stabilizing after the ransomware-driven spikes of 2020 and 2021. Part of the reason rates are lowering is because carriers are imposing stricter requirements that determine if you will qualify at all. A major global carrier recently stopped writing law firms altogether because of claims volume, and brokers expect healthcare and managed service providers (MSPs) to be next. The newest requirement is the one many MSPs are least ready for: proof that you can actually recover. This is what insurers really want to see, and meeting the bar is harder than it sounds. Why insurers stopped taking backups on faith In a recent webinar with cyber insurance provider Beltex, the familiar list of requirements came up first: Multifactor authentication (MFA) on external access and privileged accounts Endpoint detection and response (EDR) on every endpoint A staffed 24/7 team where managed detection and response (MDR) is required, and timely patching. Backup is now joining that list, and for good reason. For years it was assumed that having backups and a green job status was good enough. Claims have shown otherwise. Now, attackers go after backup infrastructure to make their ransomware more effective, and an untested restore can re-infect the production network. Beltex described an MSP that restored a client directly from backup without involving the insurer. The attackers were still in the environment, and the ransom reportedly doubled. So, carriers are asking for proof. Some want evidence of a successful restore within the last six months, and some insurance applications must be signed by a C-level executive rather than the IT director to put ownership behind it. Proof of speed matters as much as proof of recovery Being able to recover is only half the question, because time is where claim costs balloon. Insurers, it turns out, don’t object to paying claims. They object to paying big ones. Beltex’s favorite example involved an 85-person firm hit through a zero-day firewall flaw. Their MDR solution contained the intrusion in about 20 minutes, forensics confirmed two servers were touched, and clean backups had the firm fully functional within 36 hours. The claim came in at around $85,000. Compare that with downtime and business interruption: a firm billing $10,000 a day that is offline for a week loses $70,000 in income before recovery costs and claim submission. Yet large servers can take four to 24 hours to restore. That is why underwriters care how fast you can come back and how successfully. Where you recover is the other half Speed raises a second problem: where do you restore to? Breach counsel treats the first 72 hours as the most critical window, and incident response (IR) teams need to isolate and investigate infected systems during it. Restoring into production too early risks reintroducing the threat and disturbing the evidence investigators need. Waiting for a safe place has the clock running. Recovery that is fast but not safe doesn’t satisfy anyone. Meeting all of this is harder than it looks Put the pieces together and the bar is high: Backups you have actually tested Recovery times you can state and meet And a clean, separate place to recover to Underwriters want to know whether you exercised reasonable care, so a row of green checkmarks won’t do. Run a test restore. Confirm you’re protecting everything that matters, including the server someone labeled “not in production.” Have the business owner, not just IT, confirm the right systems came back within agreed recovery time objectives (RTO) and recovery point objectives (RPO), and keep the logs, screenshots and sign-off in your ticketing system. It doesn’t need to resemble a government audit; Beltex noted that this alone puts you ahead of most organizations. Where cloud disaster recovery fits Cloud-native disaster recovery changes the equation. Cove’s DRaaS solution lets teams stage a pre-recovered VM in the N-able cloud that can be failed over to in about 15 minutes, off the production network. That answers the speed question and the location question together. Forensic investigators can validate and hunt in the sandbox while the business keeps moving, with rollback to earlier points in time. Once everyone agrees the recovery point is clean, workloads can run from the cloud over VPN, and failback uses recovery agents to bring changes home. Where to start Insurance is a financial failsafe, not a substitute for a bad data protection posture. Start by listing what the business couldn’t lose for 72 hours, set recovery targets, test them and document the results. Check the policy itself: a standalone cyber policy rather than a small add-on to a general one, with a limit of at least $1 million, and $2 million as the business scales. And if an incident does hit, disconnect affected machines from the network rather than powering them off, so forensic data survives. N-able Cove Data Protection, recognized as a Champion in the Infotech 2026 Enterprise Backup Data Quadrant, provides cloud-native data protection for organizations. Learn more at n-able.com/products/cove-data-protection. Contributed by N-able.
Cybersecurity has long been a contest between attackers finding new ways in and defenders trying to keep them out. Artificial intelligence is making that contest more complicated, giving cybercriminals new ways to develop and adapt their attacks while putting additional pressure on conventional cyber defences. For enterprise IT leaders, the challenge extends beyond preventing a breach. What happens when an attacker gets through? Can compromised data be identified, clean copies recovered, and essential systems brought back online without prolonged disruption? These questions are becoming increasingly important as organizations confront both traditional threats and emerging AI-powered cyberattacks. A successful defense strategy must, therefore, account for what happens after an incident, not just the measures designed to prevent one. Making recovery part of the defence This is where cyber-resilient enterprise storage has an important role to play. Rather than relying solely on traditional backup processes, organizations need ways to protect critical data, detect potential compromise, establish which copies can safely be recovered, and restore those copies as quickly as possible. Infinidat addresses this challenge through its InfiniBox and InfiniBox SSA enterprise storage platforms, which incorporate the company’s InfiniSafe cyber resilience and recovery software suite. InfiniSafe combines immutable snapshots, which cannot be altered or deleted during their protected retention period, with logical air-gapping to isolate the management plane from the data plane. Fenced forensic environments provide a separate space for validating data before recovery. The technology also supports automated cyber protection, allowing security monitoring data center wide cyber security software applications or a Security Operations Center (SOC) to automatically talk to InfiniBoxes and trigger immutable snapshots when suspicious activity is detected. This helps reduce the window in which critical data might be exposed. For organizations concerned about recovering compromised information, optional InfiniSafe Cyber Detection uses AI-based analysis to help identify cyber affected data and locate the last known good copy of the data for recovery. Speed is another consideration. Infinidat guarantees recovery of immutable snapshots in one minute or less for InfiniBox and InfiniBox SSA, subject to the guarantee’s terms and conditions. Ultimately, cyber resilience isn’t about assuming every cyberattack can be stopped. It’s about ensuring that when defences are breached, organizations have the tools and processes to recover trusted data and limit the operational consequences. For enterprise IT teams, that makes recovery readiness an essential part of the cybersecurity conversation. Sponsored by Infinidat
The suspected Chinese advanced persistent threat (APT) group behind the sophisticated EggStreme malware has rebuilt its toolkit as it continues to target government organizations in the Philippines.
"When attackers are exposed, the cheap response is to rotate," Bitdefender said in a technical report shared with The Hacker News. "A file hash changes with every recompile, a domain costs a few
On AMD-based PCs and some Intel PCs, the TPM lockout for Windows Hello and BitLocker PINs can be reset by someone who opens the PC's case, researchers at Technische Universität Berlin say.
That leaves short PINs open to guessing. In lab tests, the researchers found a four-digit Hello PIN on an AMD laptop and a 6-digit BitLocker PIN on an Intel laptop this way.
Both PINs were set by the
TL;DR
Attackers move first. On average, exploitation now starts before a patch exists (Mandiant M-Trends 2026). In 1H 2026, 23% of vulnerabilities VulnCheck added to its exploited list were hit on or before disclosure day.
AI pentesting vendors aren't interchangeable. Most look convincing in a demo. The gaps show up in your logged-in flows, your coverage, and your production safety.
Make
A Java flaw called Java4Shell can let attackers without an account run their own code on Jira, Jenkins, Keycloak, and three other widely used applications, says Calif, the security research firm that disclosed it this week.
The flaw is present in Java 17.0.6 and later, and the vulnerable code runs only on x86-64 Intel and AMD chips that support the AVX-512 VBMI feature.
Tracked as

 Login