❌

Reading view

The Top 5 Scams Hitting Gen Z Harder Than the Rest of America
Gen Z grew up online. But that isn’t giving them an advantage against the next generation of AI-powered scams, and the data shows it. 

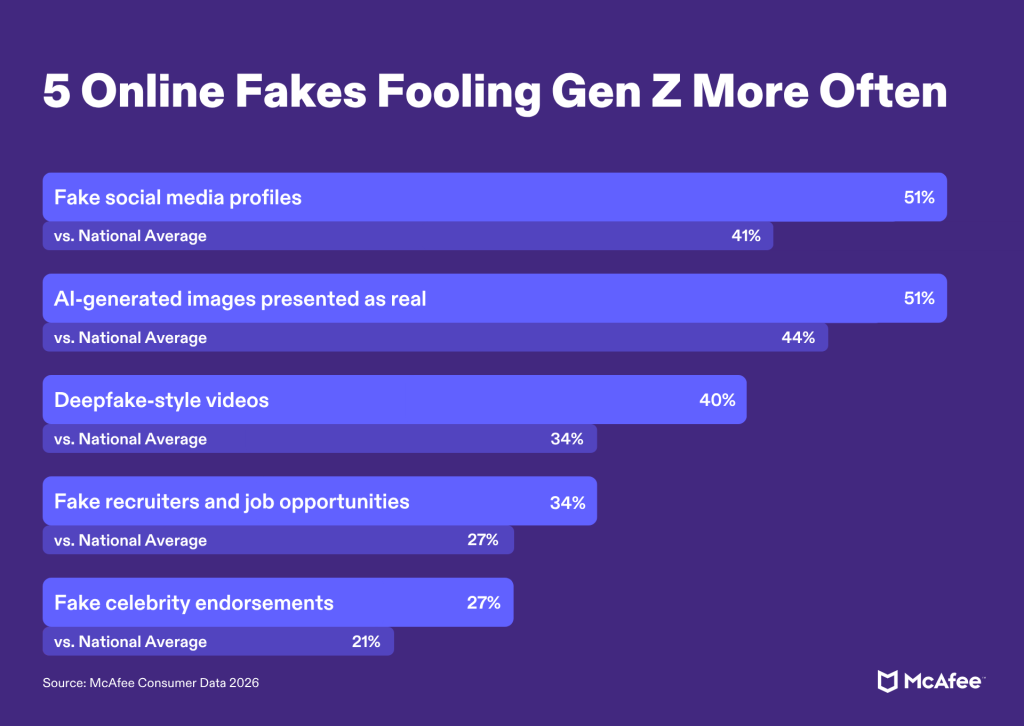
More than one in three Gen Z adults reported losing money to an online scam in the past year. They’re also encountering several types of online fakes at higher rates than Americans overall, including fake social media profiles, fake recruiters, AI-generated images and deepfake-style videos.

The data points to a new reality for a generation that has spent much of its life online: Digital familiarity alone may not be enough when AI is making fake content easier to create and harder to recognize.

Here’s what we found, plus our Head of Threat Research Abhishek Karnik’s key safety takeaways for Gen Z:

 5 Online Fakes Fooling Gen Z More Often
Gen Z Data- Top 5 Online Fakes

1. Fake social media profiles: 51% of Gen Z vs. 41% of Americans overall

More than half of Gen Z adults encountered a fake social media profile in the past year, according to McAfee’s research.

In these instances, someone might impersonate a creator, brand, potential romantic partner or even a person you already know. Once contact is established, the conversation can move toward a suspicious link, request for money, investment opportunity or attempt to collect personal information.

Abhishek’s key takeaway: “Treat unexpected messages regarding requests for money or help, with some level of skepticism, even if it’s from familiar-looking accounts. Account takeovers (where a known contact’s account was compromised) and copycat accounts (impersonated accounts where someone created a similar looking profile) are often tactics used to target victims. Call your friend on a trusted number and confirm if they really need help.”

2. AI-generated images presented as real: 51% vs. 44%

AI image tools can produce realistic-looking people, products, places and events that never existed.

For scammers, that creates another way to manufacture credibility. A fake profile can have convincing photos. A fraudulent product listing can appear to show a real item. An investment or giveaway scam can be dressed up with imagery that looks legitimate at first glance.

Abhishek’s key takeaway: “Look for oddities in the images itself. AI is not always perfect and does make errors. But also look beyond the image. Check the account posting it, the surrounding context and whether reputable sources confirm the claim before acting on it.”

3. Deepfake-style videos: 40% vs. 34%

Two in five Gen Z adults said they encountered deepfake-style videos in the past year.

A deepfake is manipulated or AI-generated media designed to make it appear that a real person said or did something they didn’t. Improvements in AI mean visual oddities alone are becoming a less reliable way to identify one.

Abhishek’s key takeaway: “Not all deepfakes are bad. Some are made for entertainment. However, pause to analyze and consider what the video is asking you to do or believe.

A surprising celebrity investment pitch, urgent request for money or unbelievable announcement deserves independent verification, even when the person on screen looks and sounds convincing.”
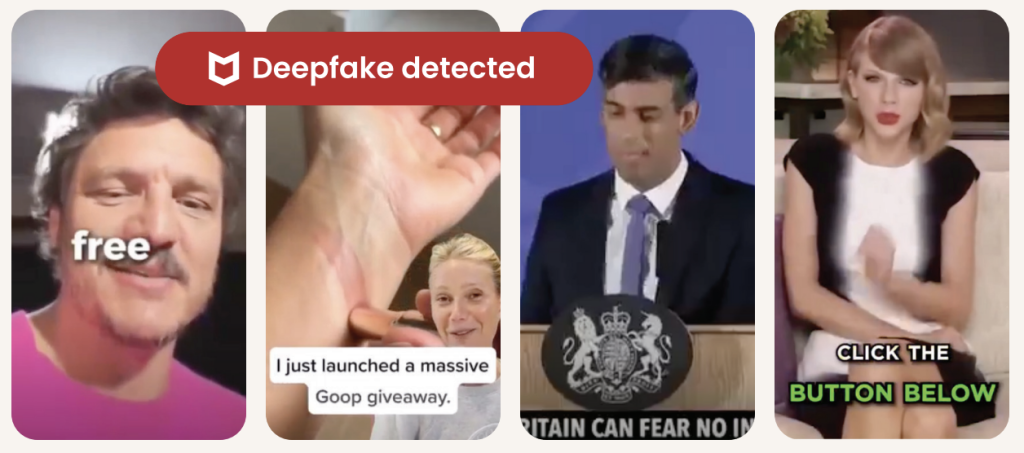
Examples of deepfake videos

4. Fake recruiters and job opportunities: 34% vs. 27%

For Gen Z adults entering or moving through the workforce, job hunting increasingly means interacting with people they have never met through email, social media, job platforms and messaging apps.

Scammers can exploit that normal behavior by posing as recruiters or employers. A convincing company name, professional-looking profile and friendly interview process can make a fraudulent opportunity harder to distinguish from the real thing.

Abhishek’s key takeaway: “Be cautious when a recruiter quickly asks for sensitive personal information, asks you to pay upfront costs or moves the hiring process onto an unusual platform like WhatsApp. Verify the role through the employer’s official website and independently confirm that the recruiter works there.”

5. Fake celebrity endorsements: 27% vs. 21%

AI has also made it easier to put familiar faces and voices behind claims they never made.

Fake celebrity endorsements can appear in investment scams, product promotions and giveaways. What makes them powerful is the borrowed trust. Seeing someone familiar can make an unfamiliar offer feel more credible.

Before buying, investing or sharing information, verify the endorsement through the celebrity’s official channels and independently research the company or offer.

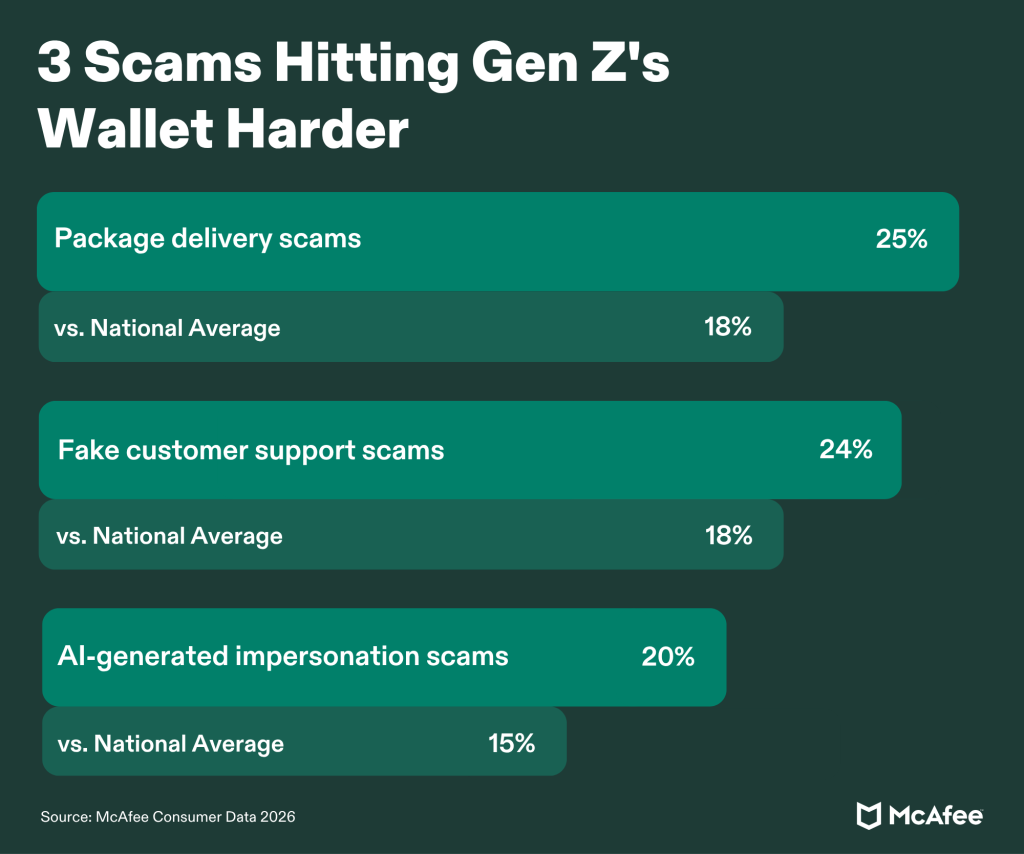
3 Scams Hitting Gen Z’s Wallet Harder
Gen Z Data- Money Scams

Exposure tells us what people are seeing. Financial loss tells another part of the story.

McAfee’s research found Gen Z adults were more likely than Americans overall to report losing money to three particular types of scams:

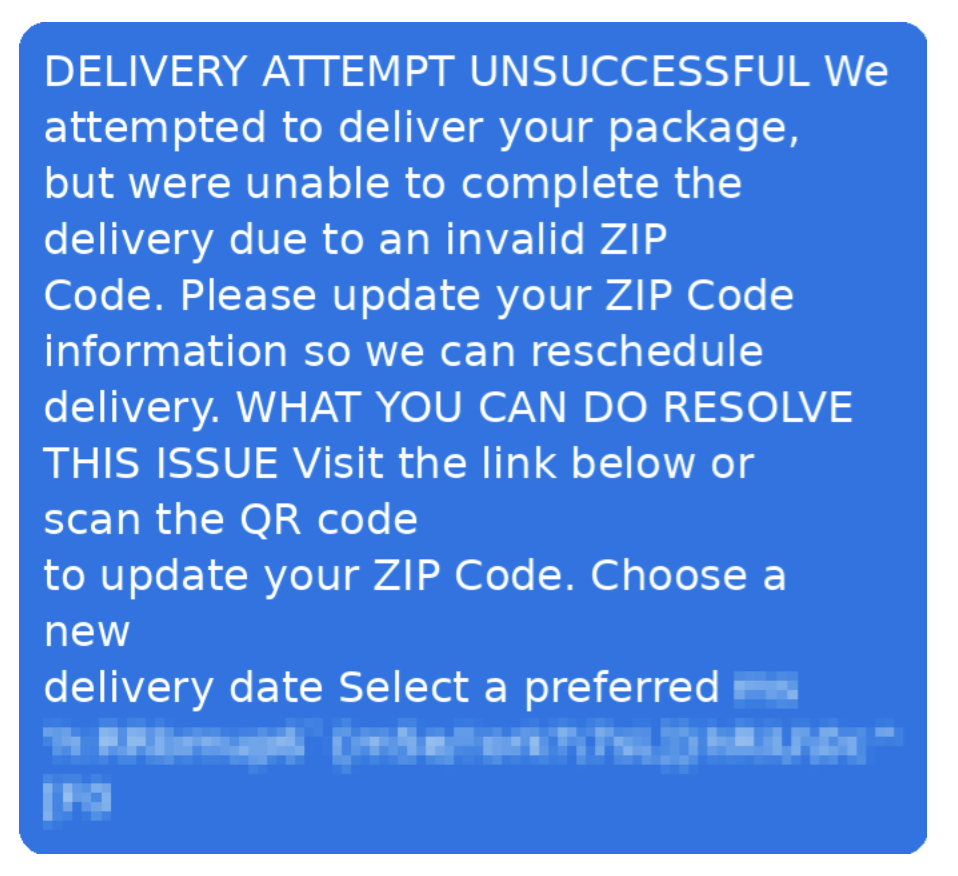
  • Package delivery scams: 25% of Gen Z vs. 18% overall
  • Fake customer support scams: 24% vs. 18%
  • AI-generated impersonation scams: 20% vs. 15%

Each takes advantage of an ordinary digital interaction.

Abhishek’s key takeaway: “Scams can work by fitting naturally into what someone is already doing online, making verification increasingly important before clicking a link, sending money or sharing sensitive information.”

3 Ways Job Scams Are Shaking Gen Z’s Confidence
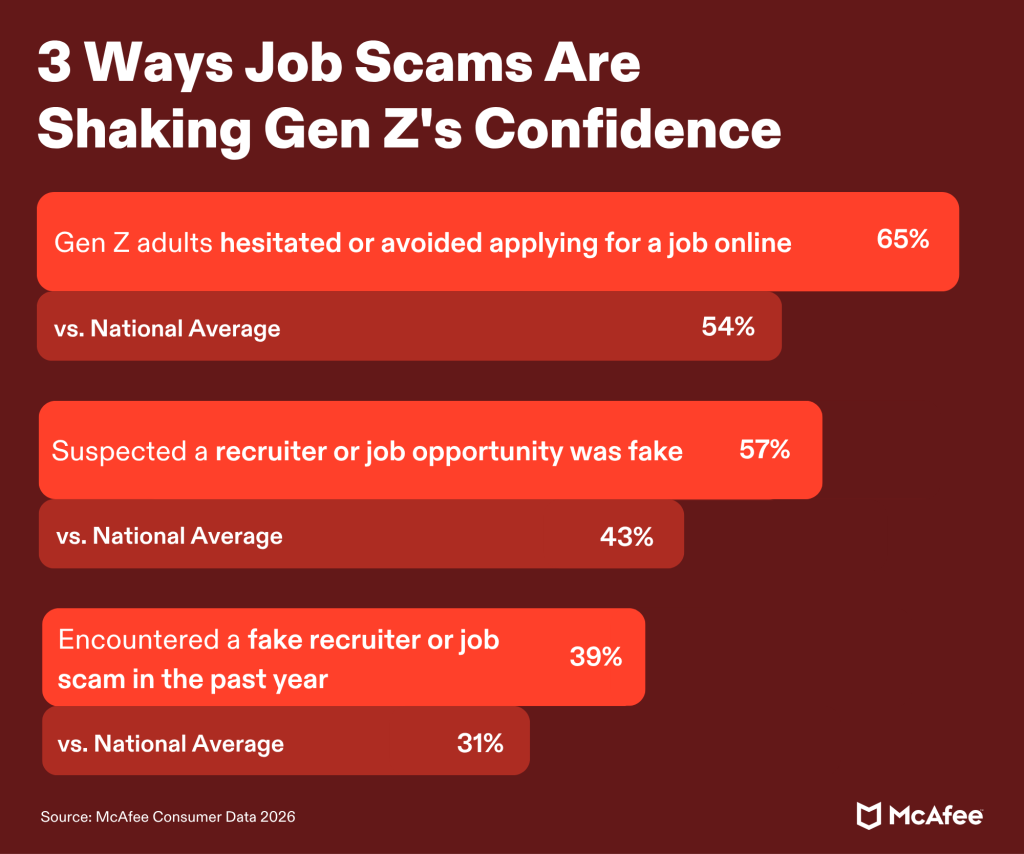
Gen Z Data- Job Scams

The job market provides one of the clearest examples of how scam concerns can affect people even when they never lose money.

McAfee found:

  • 65% of Gen Z adults say scam concerns have made them hesitate or avoid applying for a job online, compared with 54% of Americans overall.
  • 57% have suspected a recruiter or job opportunity was fake, compared with 43% overall.
  • 39% encountered a fake recruiter or job scam in the past year, compared with 31% overall.

For young adults building careers, that uncertainty can carry a real cost. A legitimate recruiter and a scammer may contact someone through the same platforms and use many of the same professional conventions.

Abhishek’s key takeaway: “Verification can help. Search for the position on the company’s official careers page, check the recruiter independently and contact the company through information you find yourself when something feels questionable.”

The Broader Scam Reality Across the U.S.
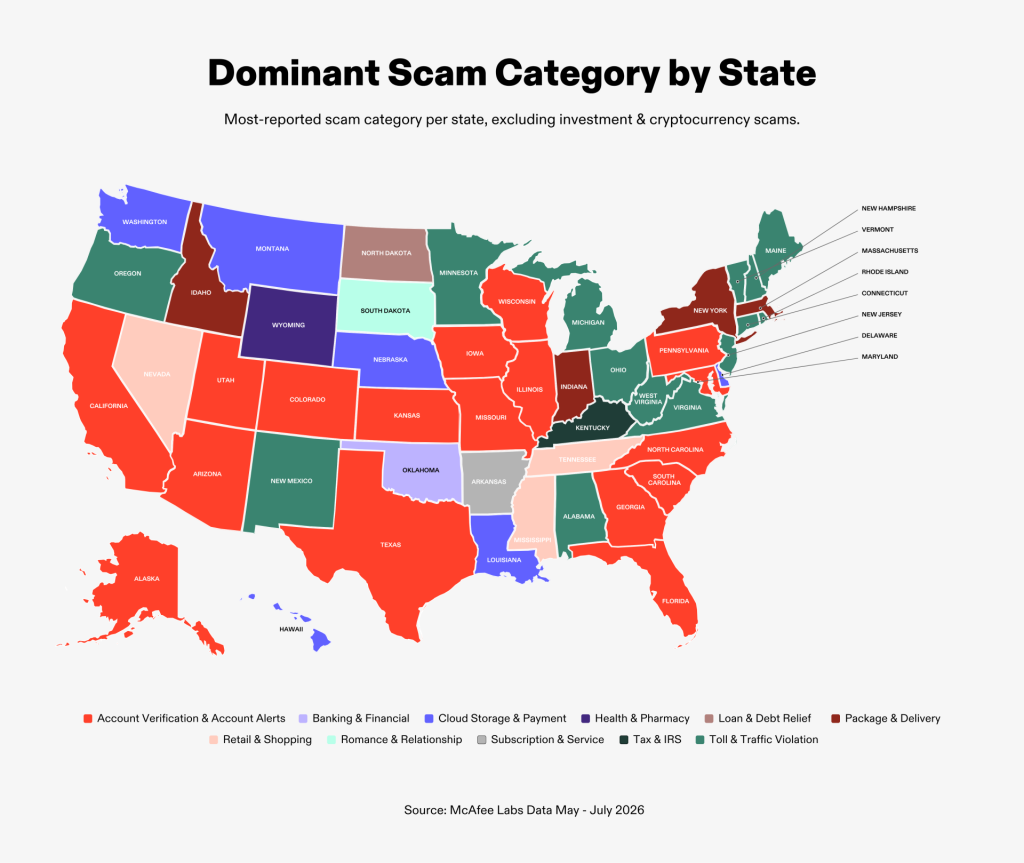
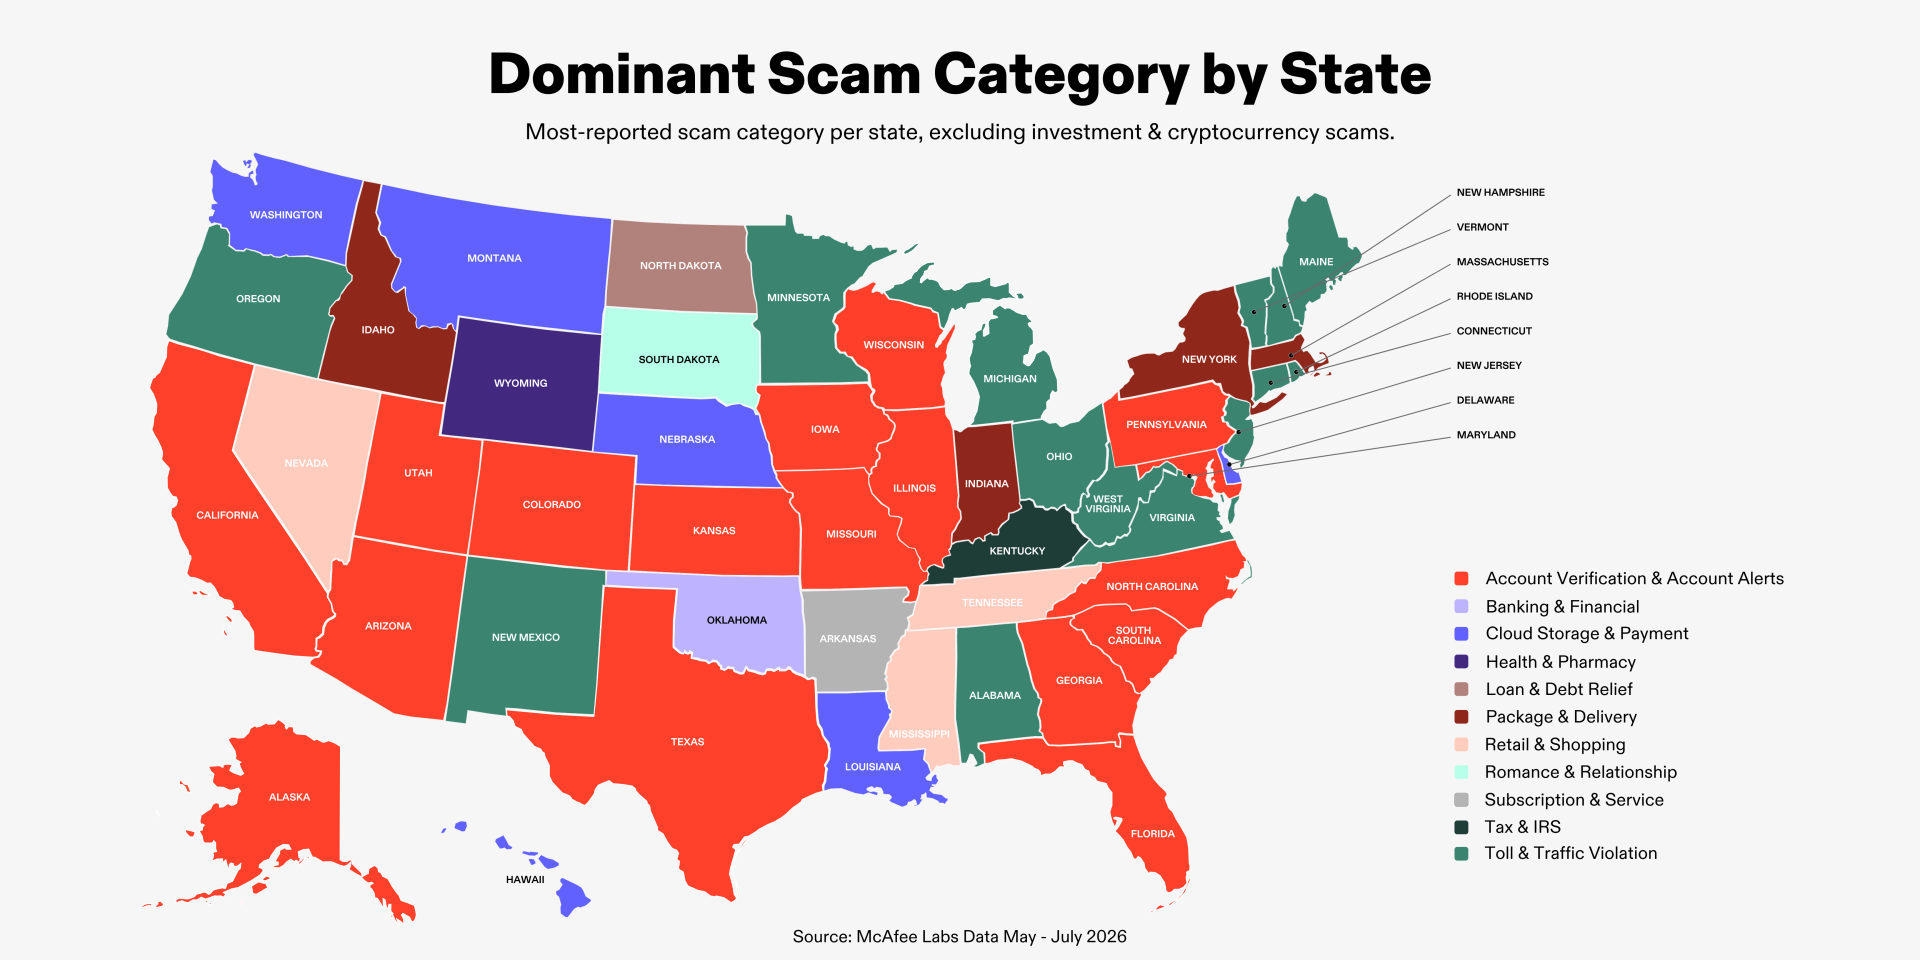
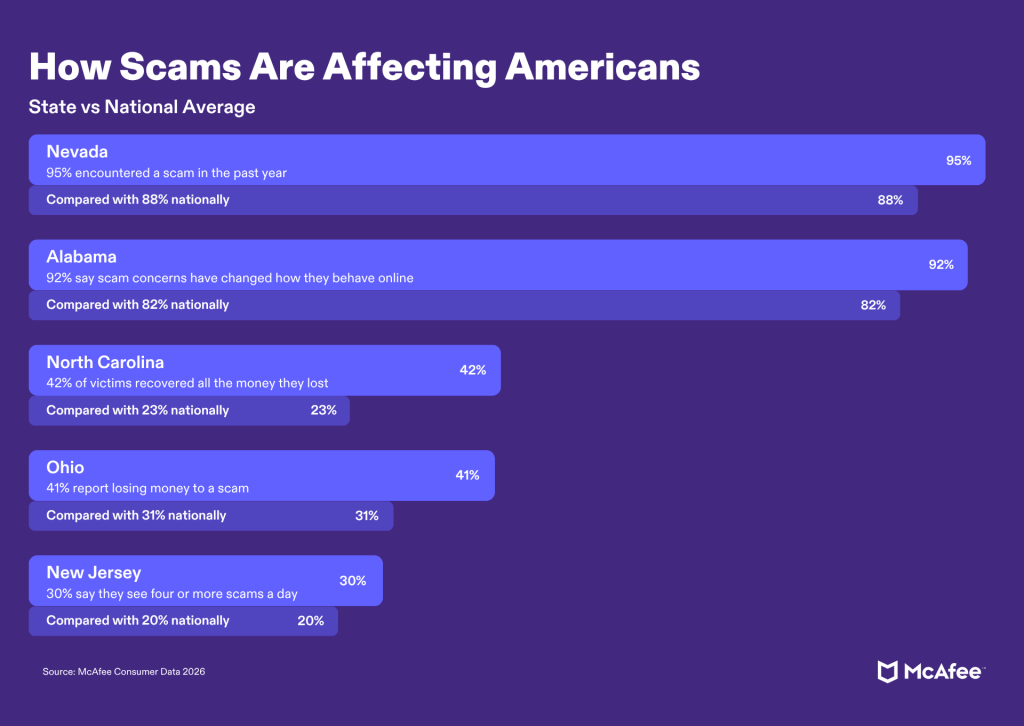
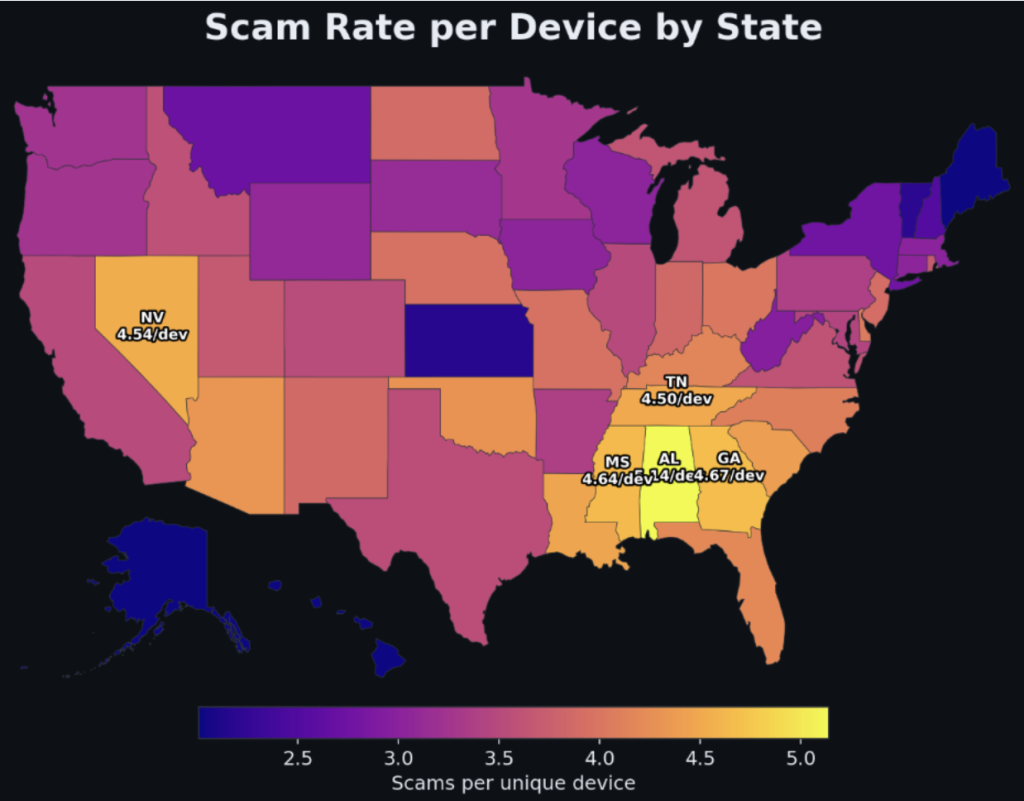
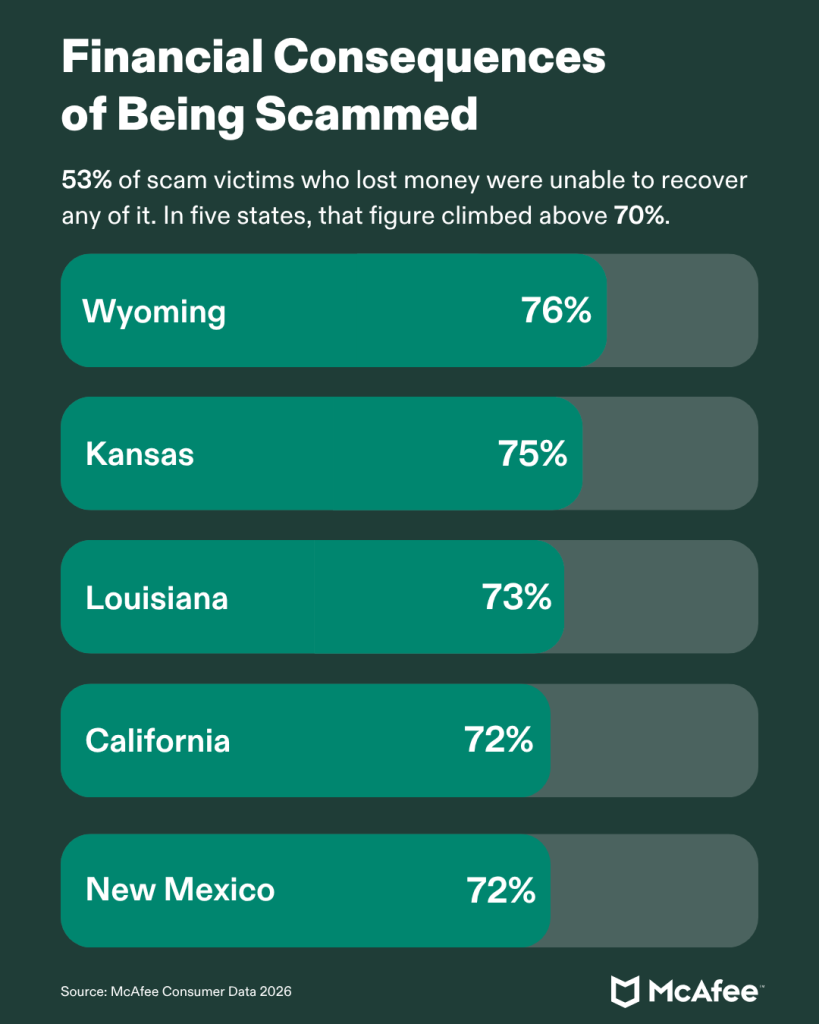
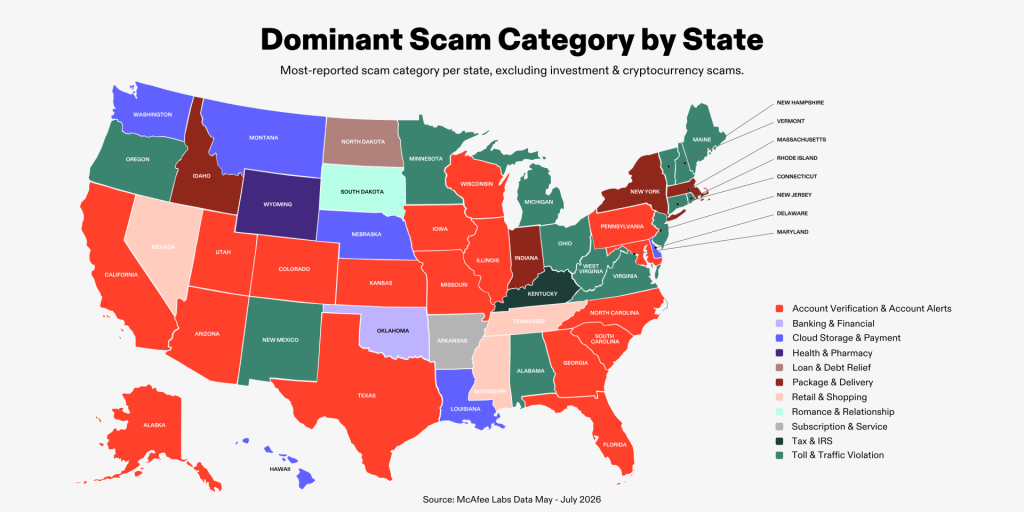
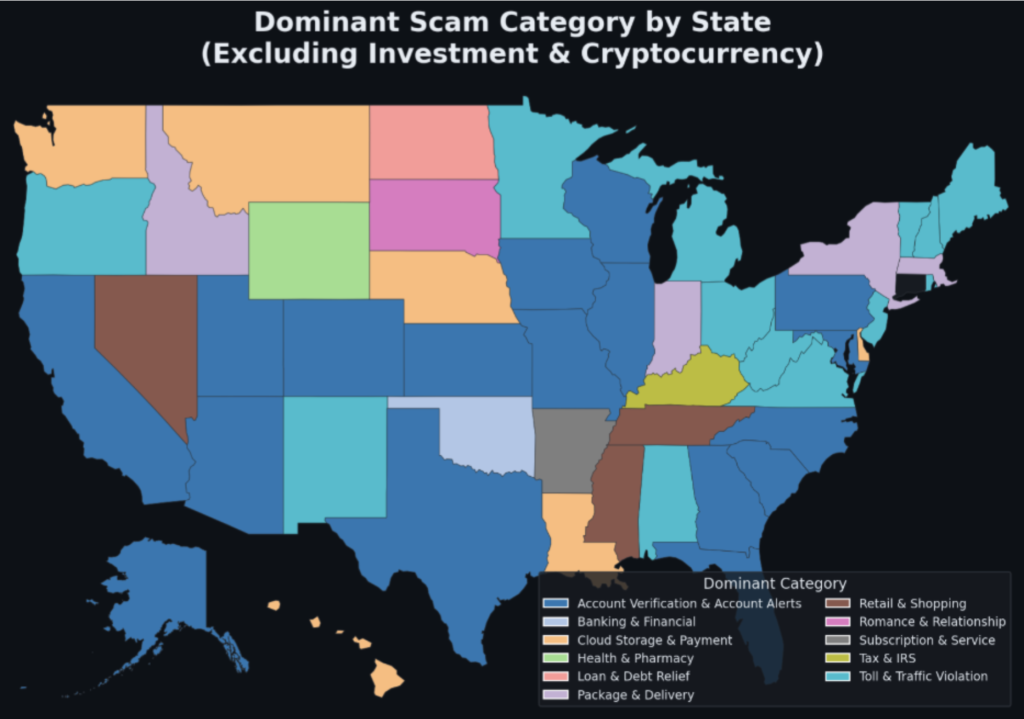
State by state breakdown infographic

Gen Z’s experience sits inside a much bigger shift in how Americans navigate life online.

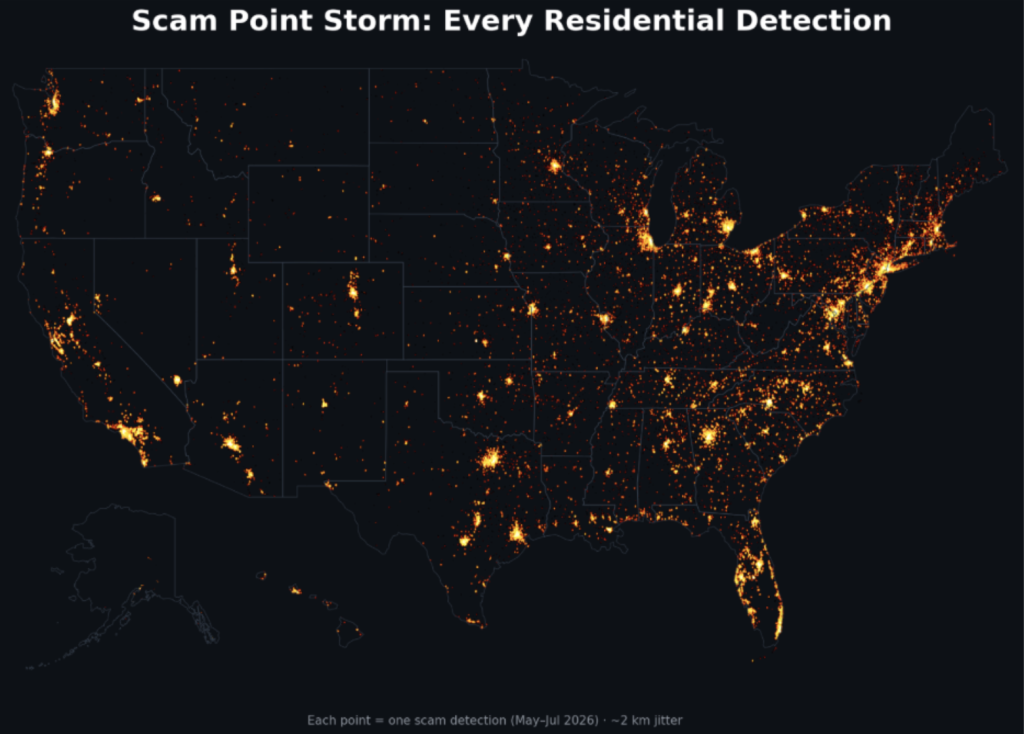
McAfee’s newest research, which combines a nationally representative survey of 5,000 U.S. adults with McAfee Labs analysis of text-based scam activity, found that 88% of Americans encountered at least one type of scam in the past year. Nearly one-third, 31%, reported losing money to one.

The effects extend beyond financial losses.

Nearly three-quarters of Americans, 74%, say they feel the need to double-check most things online before trusting them. Sixty-two percent say figuring out what is real takes more mental energy than it did a year ago. And 82% say concerns about scams have changed something they do online.

That can mean avoiding an unfamiliar retailer, ignoring a legitimate message or deciding against clicking a real link.

AI adds another layer to that uncertainty because convincing content can now be produced faster and at greater scale. As synthetic content becomes part of everyday digital life, spotting scams cannot depend entirely on whether something simply “looks fake.”

For Gen Z, the findings suggest that challenge is already especially visible. They are encountering some forms of manipulated and fraudulent content more frequently while also navigating important parts of early adult life, from finding work to shopping and managing money, online.

Safety Tips From McAfee Experts

A few habits can help reduce the risk without requiring you to investigate everything you encounter online.

Here’s what our threat researchers want you to know:

  • Verify through a second channel. If a friend, recruiter, company or customer support representative contacts you unexpectedly, confirm the request somewhere else. Open the company’s official app, visit its website yourself or contact the person using a number you already trust.
  • Slow down when someone creates urgency. Scammers frequently want a decision before you have time to investigate. Unexpected requests involving money, account credentials, verification codes or personal information deserve an extra check.
  • Investigate the source, not just the content. AI-generated images, video and audio are becoming increasingly convincing. Check who posted something, where an offer originated and whether another reliable source confirms it.
  • Avoid sending money to unlock money. Be especially cautious if a job, prize, investment or refund requires you to pay a fee, purchase equipment or transfer money first.

How McAfee Is Changing to Meet This Moment

As AI changes how people create, communicate and connect, consumer protection needs to evolve with it.

McAfee has been protecting people for decades, and for many people, our name is still synonymous with antivirus. Today’s digital lives extend far beyond a single device, and the risks people encounter do too.

The new McAfee experience is designed to help protect the things people rely on every day, including their personal information, connections, devices and accounts, while making it clearer what’s safe, what needs attention and what McAfee can handle for them.
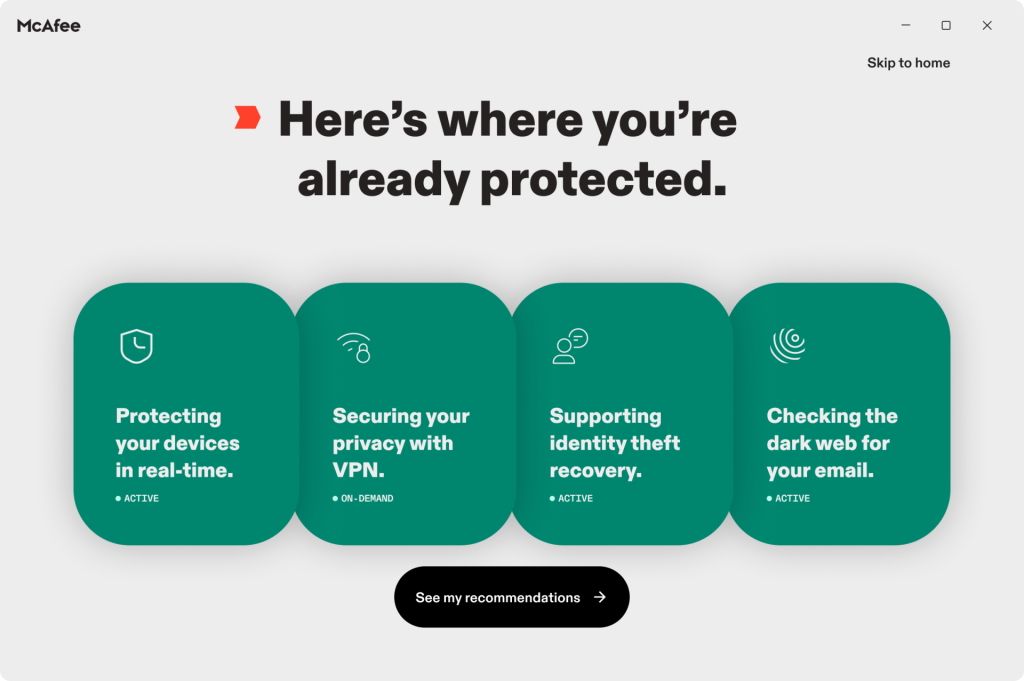
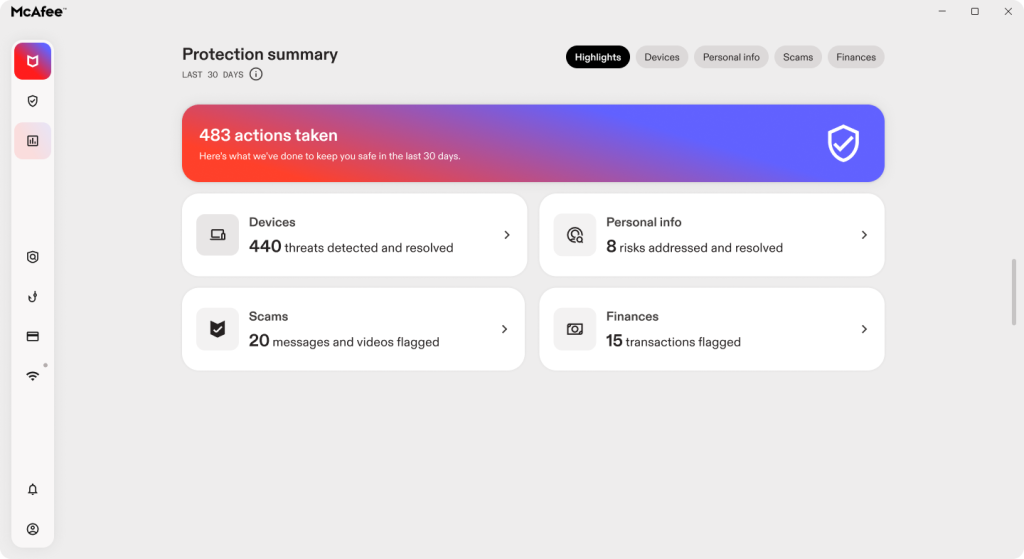
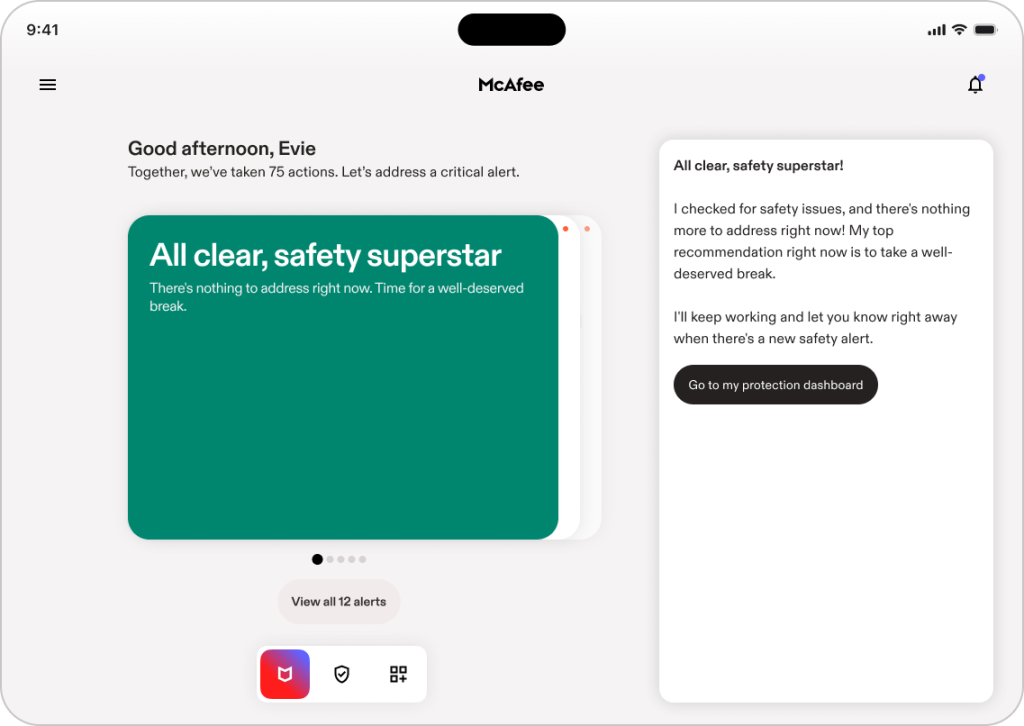
An example of McAfee's new experience and recommendations

That includes helping identify suspicious messages, links and websites, alerting people when personal information appears in a data breach, monitoring for exposed personal information, helping protect connections on risky Wi-Fi and keeping devices and accounts safer.

The experience is built around three principles:

  • Simple and easy. McAfee does more of the work so people don’t need to understand complex threats, security terminology or which setting they need to find.
  • Personalized and proactive. McAfee surfaces timely alerts when information or devices may be at risk, with guided actions that explain what is happening and what to do next in plain language.
  • Always-on and unified. Protection for personal information, connections and devices comes together in one connected experience across devices, helping people stay protected wherever their digital lives take them.

The goal is to help identify risk earlier and give people clearer guidance in the moment, reducing how much of the burden they have to carry themselves.

Navigating the New Scam Reality

Gen Z’s digital fluency has developed alongside the internet itself. Now the internet is changing again.

AI is lowering the barrier to creating realistic fake content, while many of the interactions young adults depend on, including friendships, job searches, shopping, banking and entertainment, happen online.

The answer cannot be expecting people to become experts at identifying every new AI trick.

Let McAfee do that for you.

The post The Top 5 Scams Hitting Gen Z Harder Than the Rest of America appeared first on McAfee Blog.
  •  

Pentagon Data Breach Impacts 3.05 Million: How Military Personnel Can Protect Themselves

A security breach at the Pentagon’s Defense Manpower Data Center (DMDC) exposed unencrypted personal and military records for approximately 3.05 million individuals between October 2025 and July 2026. First reported by Military Times on September 24, 2026, the intrusion compromised sensitive files, including Social Security numbers, belonging to active-duty personnel, veterans, and deceased service members.

With official notification letters dated September 18, 2026, now arriving in physical mailboxes, affected individuals can determine their exposure and enroll in 12 months of free credit monitoring and identity restoration services provided by the Department of Defense through IDX. Understanding the full scope of the incident, confirming whether your records were involved, and establishing immediate account and credit safeguards are essential steps to shielding military benefits and personal finances from targeted exploitation.

How the DMDC Data Breach Happened and What Data Was Compromised

The breach occurred when unauthorized actors exploited a software vulnerability in a DMDC file-sharing system, maintaining access to a server holding unencrypted personnel data for nine months. According to official notification letters mailed by the DMDC on September 18, 2026, unauthorized users accessed personal and military service files between October 2025 and July 2026.

The Pentagon did not issue a public press release prior to dispatching physical mailings. Community members first raised public awareness by sharing letter excerpts on Reddit’s r/Veterans. Pentagon officials confirmed to CNN that the breach compromised records for 2.76 million living individuals and 294,000 deceased service members.

The exposed server contained unencrypted personally identifiable information (PII) belonging to service members, veterans, and military dependents. Compromised records include full names, Social Security numbers, dates of birth, contact information, and administrative military service details.

How to Know If Your Information Was Exposed in the Pentagon Breach

The primary notification method for this incident is a physical letter sent via the United States Postal Service. The DMDC began mailing official breach notification letters dated September 18, 2026, directly to affected personnel, veterans, and surviving family members.

The Pentagon has not released an online lookup database to verify individual exposure. The incident affects individuals whose personnel, manpower, or benefits records were stored on the compromised server during the nine-month exposure window, spanning active-duty military, reserve personnel, National Guard, defense civilians, contractors, veterans, and eligible dependents.

If you have moved recently, your notification letter may be delayed or returned to sender. Log in to milConnect to confirm that your mailing address and contact details are current within the Defense Enrollment Eligibility Reporting System (DEERS). If your records were maintained in DMDC systems between October 2025 and July 2026, take proactive security steps even before a physical letter arrives.

Red Flags That Cybercriminals Are Using Your Military Data

When personal and military records leak, cybercriminals routinely use the data to stage targeted impersonation schemes and financial fraud. Watch for these warning signs:

  • Government impersonation attempts: Unsolicited calls, emails, or text messages claiming to be from the Department of Defense (DOD), Department of Veterans Affairs (VA), or TRICARE requesting verification of personal identifiers.
  • Benefit redirection notices: Unexpected alerts regarding direct deposit changes, login credential updates, or profile modifications across military portals that you did not initiate.
  • Phony breach assistance solicitations: Unofficial communications offering expedited claims, settlements, or data removal services in exchange for an upfront fee or account numbers.
  • Unexplained credit or loan activity: Inquiries on your credit report, new credit card accounts, or collection notices for debt you do not recognize.
  • Unexpected tax or benefit filings: Notifications from the IRS or state tax authorities stating that a tax return or benefit claim has already been filed in your name.

How Military Personnel Can Protect Themselves

Military personnel and service members should take immediate steps to restrict access to their credit profiles and personal accounts:

  1. Enroll in free credit monitoring through the official IDX portal.
    The Defense Department is offering 12 months of free credit monitoring and identity restoration services to affected individuals through IDX. If you received a breach notification letter, use the unique enrollment code included in the mailing to register on the official IDX DMDC response portal or call the support line directly at 1-855-744-4556.
  2. Place a credit freeze with all three credit bureaus.
    Contact Equifax, Experian, and TransUnion to freeze your credit files. A credit freeze blocks prospective lenders from accessing your credit report, stopping identity thieves from opening loans or lines of credit with your Social Security number.
  3. Enable multi-factor authentication on defense portals.
    Log in to MilConnect, VA.gov, and MyPay to update passwords and enforce multi-factor authentication (MFA). Use an authenticator app or hardware security key rather than SMS verification where available.
  4. Verify official contacts independently.
    The DOD, DMDC, and VA do not initiate contact via phone, text, or email to demand immediate payment or confirmation of your Social Security number. Verify any inquiry by navigating directly to official .gov domains.
  5. Inspect TRICARE and medical billing statements.
    Review Explanations of Benefits (EOBs) and medical statements closely. Confirm that all listed provider appointments, diagnostic tests, and prescription orders match care you actually received.

What Military Personnel Should Do If Their Data Was Compromised

If you received an official DMDC notification letter dated September 18, 2026, or notice unauthorized activity on your accounts, execute the following recovery steps:

  • File an identity theft report with the FTC. Submit an official report through the Federal Trade Commission identity theft portal to establish your legal rights and dispute fraudulent accounts with creditors and banks.
  • Obtain an IRS Identity Protection PIN (IP PIN). Prevent fraudulent tax filings using your exposed Social Security number by applying for a six-digit IP PIN through the Internal Revenue Service identity protection page.
  • Place an extended fraud alert on your credit file. If you choose not to freeze your credit entirely, request an extended fraud alert, which requires lenders to verify your identity before approving credit in your name.
  • Notify your financial institutions. Contact the fraud divisions of your bank and credit card issuers to review account statements, replace compromised account numbers, and set up real-time transaction alerts.
  • Retain all breach correspondence. Keep physical copies of your DMDC notification letter, agency complaints, police reports, and dispute logs for ongoing tracking.

How Military Personnel Can Report Fraud and Suspicious Activity

Report security incidents, fraudulent accounts, and impersonation attempts directly through official federal reporting channels:

  • Department of Defense Inspector General: Report military personnel data misuse or military identity impersonation via the Department of Defense Hotline.
  • FBI Internet Crime Complaint Center (IC3): File an online cybercrime complaint regarding credential misuse or unauthorized financial compromise through the FBI Internet Crime Complaint Center.
  • Local Law Enforcement: File a formal police report with your municipal department if an unauthorized party obtains loans, opens accounts, or conducts financial transactions in your name.

Because Social Security numbers and military service records cannot be readily changed, exposure from the DMDC breach presents a persistent risk for active personnel and veterans. Taking proactive security measures now, such as enrolling in the IDX identity monitoring program, locking down credit files, securing military accounts with multi-factor authentication, and reporting suspicious contact immediately, is critical to preventing long-term identity exploitation.

The post Pentagon Data Breach Impacts 3.05 Million: How Military Personnel Can Protect Themselves appeared first on McAfee Blog.
  •  

ASOS Push Notification Hack: Inside the Breach and How to Stay Safe

On October 6, 2026, the ASOS push notification hack sent unauthorized messages to millions of customer devices after cybercriminals accessed a connected third-party platform. ASOS, a British online fashion and cosmetic retailer serving active shoppers worldwide, confirmed that an attacker compromised employee credentials to access external systems. As reported by BBC News, the intrusion exposed customer contact records and personal search histories, although company representatives confirmed that banking and payment information was not accessed.

How the Attack and Social Engineering Breach Worked

The unauthorized messages originated from an extortion ring calling itself the Xuanyewen hacker group. The intruders hijacked the ASOS mobile shopping app interface to broadcast rogue alerts directly to users, claiming they had extracted full customer databases.

The breach did not stem from a software flaw within the ASOS mobile application. Instead, the intruders relied on social engineering, impersonating a trusted contact to deceive an employee into providing valid system credentials.

Those credentials allowed the attackers to sign in to Simon AI, a third-party marketing and personalization platform built on Snowflake Cortex AI that ASOS uses to power customer communications. Once logged in, the threat actors initiated app-wide push alerts and exfiltrated audience data containing customer personal data.

Clarifying the Snowflake Breach Claims

During the intrusion, the hackers claimed they had carried out a direct Snowflake breach to compromise ASOS’s central databases. Official statements from both platforms quickly refuted that claim.

In a corporate statement released through Snowflake’s official statement via Alliance News, a Snowflake spokesperson stated: “We can confirm this issue did not in any way result from a vulnerability, weakness, flaw, or misconfiguration with the Snowflake service… and was not caused by Snowflake.”

Independent reporting and corporate disclosures confirm that the compromise occurred exclusively at the third-party marketing integration layer. Attackers frequently target peripheral marketing tools using stolen credentials because these platforms handle live customer segments without requiring direct access to locked-down corporate networks.

Warning Signs That Your Personal Data Was Compromised

The data accessed during the incident included more than basic contact lists. As documented by BBC’s reporting, data samples provided directly by the threat actors revealed specific customer search histories, including search terms such as “reclaimed vintage.”

In the official ASOS customer breach notification, the retailer stated they did not believe that payment card numbers, banking details, and account passwords were accessed, as those are stored on separate, isolated transactional systems. However, exposed contact information and shopping preferences still present risks for targeted follow-up fraud. Watch for these warning signs that your personal data was exposed:

  • Unsolicited push messages: App notifications prompting you to verify your identity, visit external chat platforms, or click unverified links.
  • Tailored phishing emails: Messages referencing specific clothing brands, recent browsing queries, or recent order details designed to trick you into revealing passwords.
  • Unrequested authentication codes: Password reset messages or multi-factor prompts that you did not initiate.
  • Direct contact from extortionists: Unsolicited communications via email or messaging apps claiming to hold your retail browsing data.

How to Protect Your Personal Data

Taking direct defensive steps helps minimize the risk of identity theft or secondary phishing. Use these best practices to protect your personal data:

  • Avoid clicking unexpected push notification links: If you receive an unexpected alert about an account security issue, dismiss the message and sign in through an official web browser instead.
  • Update your account password: Create a strong, unique password for your ASOS account that is at least 12–16 characters long and not shared across any other platforms.
  • Enable multi-factor authentication (MFA): Set up MFA across your primary email and retail accounts, opting for an authenticator app over SMS codes whenever available.
  • Verify retailer messages independently: If you receive an email regarding an order change or account issue, visit the store’s website directly rather than using embedded links.

What to Do If Your Personal Data Was Compromised

If your personal details were exposed or you interacted with the rogue push alert, take these containment measures:

  • Cease all contact with extortionists: Do not communicate with extortionists or send payments to individuals offering to delete stolen records.
  • Change shared account credentials: If you used your ASOS password on other websites, update those services with unique login combinations immediately.
  • Place a credit freeze: Contact the three major credit reporting agencies—Equifax, Experian, and TransUnion—to freeze your credit files against unauthorized new accounts.
  • Monitor financial statements: Check linked credit card and bank statements for unauthorized charges or low-value test transactions.
  • Create an identity recovery plan: If sensitive contact or identity records were exposed, file a report at the federal government’s IdentityTheft.gov recovery portal to document the incident and receive a recovery plan.
  • Preserve digital evidence: Keep screenshots, message headers, and timestamps of any suspicious texts, emails, or calls you receive.

How to Report Identity Threats and Extortion

Reporting incidents to official oversight agencies helps authorities identify threat infrastructure and take down fraudulent operations:

The ASOS App push notifications incident highlights how cybercriminals bypass central infrastructure by using social engineering to compromise connected third-party tools. Practicing strong credential hygiene, staying alert to targeted phishing messages, and reporting suspicious contact to regulators are your most effective steps for keeping your personal information secure.

The post ASOS Push Notification Hack: Inside the Breach and How to Stay Safe appeared first on McAfee Blog.
  •  

New Adception Campaign Weaponizes Search Ads: How to Stay Safe From Malvertising

A new cyberattack is weaponizing everyday search results to trick users into running malicious code on their devices. The campaign, dubbed “Adception,” was uncovered by Push Security. By buying paid search ads on Google and routing traffic through trusted web services, attackers are placing deceptive links directly in front of people searching for popular software. Then, they use a social engineering framework known as “ClickFix” to trick people into running malicious scripts on their devices.

How the Adception Campaign Works

Search ads appear at the very top of search engine results, making them easy to click and easy to trust. Malvertising (short for malicious advertising) occurs when cybercriminals buy or hijack legitimate ad placements to spread malware or direct users to fraudulent websites. In this campaign, attackers purchase legitimate ad slots but route clicking visitors through a hidden chain of web redirects before loading a fraudulent website. This detour conceals the final destination from automated ad-review crawlers, allowing malicious ads to bypass platform security filters and reach active searchers.

According to Push Security’s research, the threat actors specifically targeted Mac users searching for Anthropic’s Claude AI assistant. To evade automated detection, the attack chain bounces traffic through legitimate Bing click-tracking redirects and a compromised website. Once a visitor lands on the fake software portal, the attackers deploy an evasion technique known as “ClickFix,” using deceptive troubleshooting prompts to trick macOS users into executing base64-encoded malware directly inside the Z shell (zsh).

The campaign executes across five distinct stages:

  1. Sponsored Search Ad Placement: Attackers purchase top-ranked Google search ads that bid on keywords for Anthropic’s Claude desktop app.
  2. Cross-Engine Redirection (Google to Bing): Clicking the Google ad routes the visitor through legitimate Bing click-tracking infrastructure. The attackers use this cross-engine detour because automated Google ad-review crawlers do not expect ad traffic to route through a competitor’s tracking domain, effectively blinding them to the ultimate destination.
  3. Compromised Intermediary Site: The traffic forwards to a compromised WordPress site owned by a South American retailer, which runs two layers of cloaking to weed out automated scanners and non-Mac operating systems.
  4. Deceptive Landing Page: Qualifying visitors land on a counterfeit webpage that closely mimics Anthropic’s official website and branding.
  5. ClickFix Terminal Execution: The landing page displays a fake installation error and activates the “AcSig” ClickFix toolkit, which hijacks the user’s clipboard and instructs them to paste code into the macOS Terminal to “fix” the download.

Warning Signs of Deceptive Search Ads

  • Unfamiliar or shifting URLs: The address displayed on the ad card does not match the real software vendor, or your browser rapidly redirects through multiple unrelated domains before loading.
  • Terminal or command-line prompts: When you arrive at a website through a search ad, it instructs you to open your computer’s terminal, shell, or command prompt to complete a download or resolve an installation error.
  • Clipboard hijack instructions: The webpage asks you to copy code or automatically copies script text containing terms like base64, eval, curl, or zsh into your system clipboard.
  • Fake system repair messages: On-screen pop-ups claim your browser or operating system requires an immediate manual patch to proceed with a standard download.

How to Protect Yourself from Deceptive Search Ads

  • Navigate directly to official vendor sites. Type known web addresses directly into your browser’s address bar rather than searching for download portals.
  • Verify the destination URL before clicking. Inspect the displayed web address on search results to ensure it matches the actual company domain.
  • Use automated web protection tools: Install a secure browsing extension to automatically protect against malware and phishing sites.
  • Never paste unverified code into command-line tools. Legitimate commercial software does not require pasting terminal commands to resolve browser download issues.
  • Use official application stores. Download desktop applications directly through official developer portals, the Mac App Store, or the Microsoft Store.

What to Do If You Interacted with a Malicious Ad

If you clicked a deceptive ad and pasted code into your Mac’s Terminal, assume your device has been compromised. Take these immediate steps to limit the damage:

  1. Disconnect from the internet immediately. Turn off your Wi-Fi from the menu bar at the top of your screen and unplug any network cables. This cuts off communication between your computer and the attacker’s server.
  2. Shut down the Terminal and turn off your Mac. Quit the Terminal app completely. Shut down your computer to stop any background scripts from continuing to run.
  3. Change your passwords from a different device. Using your phone or a separate, clean computer, immediately update passwords for your primary email, online banking, and password manager. When prompted, choose the option to “Log out of all devices.”
  4. Turn on two-factor authentication (2FA). For any critical accounts that don’t already have it, enable two-factor authentication using an authenticator app rather than SMS text messages.
  5. Run a full antivirus scan. Restart your Mac, keep Wi-Fi turned off, and run an offline security scan using reputable antivirus software to detect and quarantine any installed files.
  6. Avoid sensitive logins and seek professional help if uncertain. Do not sign into online banking, email, or password accounts on the affected computer. If your security scan cannot confirm the threat is gone or you feel unsure, take the device to an Apple Store or certified technician to safely wipe and reinstall the operating system.

How to Report Deceptive Ads

  • Report rogue ads to Google: Submit an abuse report via the Google Ads Complaints Form to flag fraudulent ad links and advertiser accounts.
  • Report redirect abuse to Microsoft: Submit details on hijacked redirect links directly through the Microsoft Security Response Center.
  • File an official fraud report: Report deceptive advertising to the Federal Trade Commission.
  • Contact cybercrime authorities: File formal reports regarding malware delivery or financial loss with the FBI’s Internet Crime Complaint Center.
  • Notify the impersonated vendor: Alert the affected brand’s support team to inform them of active trademark abuse and domain spoofing.

Deceptive search ads succeed by exploiting everyday browsing habits and the assumption that top-ranked search results are safe. Taking a moment to verify destination URLs and reporting suspicious sponsored listings helps platforms dismantle malicious infrastructure and keeps the broader online community safer. 

The post New Adception Campaign Weaponizes Search Ads: How to Stay Safe From Malvertising appeared first on McAfee Blog.
  •  

CloudSyncD macOS Malware Hidden in Fake Zoom Installer: How to Avoid Malicious Installers

Security researchers at Jamf Threat Labs issued a September 2026 threat report warning Mac users about a newly discovered malware program called “CloudSyncD.” Disguised as a Zoom installer on unverified download sites, this malicious software tricks users into entering their administrator password, allowing attackers to secretly take remote control of the computer. The campaign targets individuals looking to install or update the popular video conferencing software.

How the CloudSyncD Malware Works

For a detailed technical breakdown of how the malware operates, you can read the full Jamf Threat Labs report. In simple terms, when someone downloads and opens the fake Zoom installer, the malware enacts a process to take control of the Mac:

  • Fake System Prompt: The installer opens a pop-up window asking for your computer password, designed to look like an official macOS prompt.
  • Hidden Credentials: Once typed, the malware saves your password in a disguised file, hiding the text with invisible characters to bypass standard checks.
  • Silent Setup: Using administrative privileges, the malware quietly installs a hidden background program on your system.
  • Remote Access: The background program connects your Mac to an attacker’s server, granting hackers full remote access to run commands, steal files, or install additional software.

Malicious Installer Warning Signs and Red Flags

Recognizing a suspicious installer before opening it prevents system compromise:

  • Unofficial Download Sources: The file originates from a sponsored search link, file-sharing site, or third-party portal rather than the software’s official web page or the official Mac App Store.
  • Immediate Password Requests: A system password prompt appears right when opening a disk image before any setup wizard begins.
  • System Security Warnings: macOS Gatekeeper or XProtect displays an alert stating the software is untrusted or lacks a recognized developer signature.
  • Unfamiliar Background Processes: Unknown applications or scripts execute with administrative privileges in macOS Activity Monitor.

How to Protect Your Mac From CloudSyncD and Other Malware

Adopting safe download practices reduces the risk of installing malicious macOS software:

  • Download exclusively from official sources: Always obtain applications directly from the developer’s official website or the Mac App Store.
  • Verify unexpected password prompts: Cancel any password request that appears unexpectedly when opening a newly downloaded file.
  • Keep macOS security features active: Ensure built-in protections like macOS Gatekeeper and XProtect remain turned on to flag unverified software.
  • Check app signatures before opening: Inspect installer details and developer certificate signatures before approving setup.

What to Do If You’ve Already Used a Fake Zoom Installer

If you downloaded a fraudulent Zoom installer or entered credentials into a suspicious prompt, execute these recovery steps immediately:

  • Disconnect from the Internet: Turn off Wi-Fi and unplug Ethernet cables right away to break active communication between your Mac and remote servers.
  • Change Account Passwords: Using a separate, secure device, update your Mac administrator password and any account credentials accessed from that computer.
  • Turn On Multi-Factor Authentication: Enable multi-factor authentication (MFA) across your financial, email, and personal accounts.
  • Isolate and Remove Malicious Artifacts: Run a full system scan or work with a technical professional to locate and delete unauthorized background files.
  • Place a Credit Freeze: If personal or financial data was stored on the computer, place a credit freeze with Equifax, Experian, and TransUnion.

Report Fraudulent Installers and Secure Your Mac

Reporting malicious downloads helps threat intelligence researchers and federal agencies track active campaigns. Submit reports regarding fraudulent software installers to the FBI Internet Crime Complaint Center or the Federal Trade Commission. Notifying the official security team of the impersonated service provider also assists in taking down fake download domains.

Because CloudSyncD installs persistent background files, completely removing every component is essential to restoring system security. Simply deleting the downloaded installer disk image does not eliminate the threat. Ensure all hidden binaries and configuration files are thoroughly purged from your system to revoke remote access and protect your data.

The post CloudSyncD macOS Malware Hidden in Fake Zoom Installer: How to Avoid Malicious Installers appeared first on McAfee Blog.
  •  

Microsoft X Account Hacked in Crypto Scam: How to Spot Hijacked Accounts Promoting Scams

On October 2, 2026, attackers hijacked Microsoft’s official X account (which reaches over 13 million followers) to execute a cryptocurrency pump-and-dump scheme, as reported by The Verge. The unauthorized access allowed attackers to replace Microsoft’s profile image with its retro mascot Clippy and promote a fraudulent token called $Clippy before the posts were removed. An official statement on Microsoft’s X account confirmed the account was secured, the unauthorized posts were deleted, and an internal investigation into the breach is ongoing.

How the $Clippy Crypto Scam Worked

When cybercriminals gain control of a verified corporate account, they leverage its built-in credibility to trick followers into fake financial investments.

Unauthorized actors gained access to @Microsoft on October 1, 2026. The attackers changed the account’s profile picture to image assets of Clippy, Microsoft’s legacy virtual assistant, and retweeted promotional posts from an impersonator handle, @clippymsftcto.

The malicious posts directed users to external sites promoting a fraudulent $Clippy cryptocurrency token. To confuse followers and delay remediation, the attackers also published a fake apology tweet from @Microsoft claiming control had been restored while continuing to promote the scam. Account access was eventually restored, and X suspended the associated impersonator accounts.

Warning Signs That an Account Has Been Compromised for a Crypto Pump-and-Dump

  • Uncharacteristic financial endorsements: Verified corporate accounts suddenly promoting unannounced meme coins, cryptocurrency presales, or Web3 projects.
  • Sudden profile changes: Abrupt alterations to official branding, logos, bios, or handles accompanying high-yield investment offers.
  • High-pressure purchasing tactics: Posts creating artificial urgency by urging followers to buy unlisted tokens or connect wallets before a deadline.
  • External wallet connection links: Unfamiliar links directing users to third-party decentralized finance platforms or signature-draining websites.
  • Contradictory apology posts: False status updates or fake “all-clear” statements published during an active breach that still include external links or contract addresses.

How to Protect Yourself from Social Media Crypto Scams

Protecting your assets from social media crypto schemes requires careful verification and strict wallet safety practices.

  • Cross-reference announcements on official newsrooms: Confirm product or financial launches on a company’s main website before trusting social media posts.
  • Avoid clicking direct links for token sales: Never interact with link shorteners or unfamiliar domains asking you to connect a digital wallet.
  • Audit token contracts independently: Use reputable blockchain analytics tools to check liquidity, developer wallet allocations, and contract safety before buying new tokens.
  • Remember that verified badges do not guarantee immunity: Blue checkmarks confirm identity verification, but they do not prevent credential theft, session hijacking, or account takeovers.

What to Do If You Have Already Been Targeted

  • Disconnect wallet permissions immediately: Use security tools to cancel active smart contract allowances granted to suspicious sites.
  • Transfer remaining assets: Move funds to a newly generated, secure wallet if you suspect your private keys or seed phrases were compromised.
  • Contact your financial institutions: Notify your bank, credit card company, or crypto exchange immediately if fiat currency or linked accounts were involved.
  • Change passwords and enable multi-factor authentication (MFA): Update credentials across all sensitive accounts using an authenticator app rather than SMS.
  • Document transaction evidence: Save wallet addresses, transaction hashes, screenshots of fraudulent posts, and web links for formal reports.
  • Report identity exposure: If you shared personal identity or banking details on a phishing site, submit a report to the FTC and get a recovery plan.

How to Report Social Media Crypto Scams

If you encounter or fall victim to a social media crypto scam, report cyber fraud directly to the FBI Internet Crime Complaint Center and deceptive financial schemes to the Federal Trade Commission. You can also flag hijacked profiles or scam links using on-platform reporting tools directly on X, or contact local law enforcement if you suffered significant financial losses.

High-profile corporate account hijacks demonstrate how quickly bad actors can exploit trusted brands to promote fraudulent schemes. Verifying financial news across primary corporate websites, auditing token contracts, and recognizing red flags remain critical steps to keeping your digital assets secure.

The post Microsoft X Account Hacked in Crypto Scam: How to Spot Hijacked Accounts Promoting Scams appeared first on McAfee Blog.
  •  

Android/RewaFake: Uncovering a Large-Scale Fake Apps Adware Campaign on Google Play

Authored By: Fernando Ruiz

McAfee’s Mobile Research Team identified more than 1,900 unique applications associated with the campaign across over 500,000 devices in more than 190 countries. Based on publication patterns, we estimate that the operators were releasing approximately 20 to 25 new applications per day, each leveraging different themes, brands, and impersonation targets. The highest concentrations of affected devices were observed in India, Russia, and the United States.

Most of these apps were published on the official android platform impersonating well-known products such as CapCut, Roblox, Zelle, PayPal, Netflix, Xbox Game Pass, Siri, iMessage, etc. under different developer accounts, they shared a common codebase, repeated the same deceptive behaviors, and contacted the same remote server, which told each app where to send its users. That destination was an advertising funnel and in our testing the ads it served led to third-party subscription-fraud pages billing as much as $49.99 per month

McAfee identified the malicious apps, conducted technical analysis, and reported its findings to Google through responsible disclosure channels. Following McAfee’s report, Google removed all of the identified apps from Google Play. McAfee is a member of the App Defense Alliance, which supports collaboration across the mobile ecosystem to improve user protection. McAfee Mobile Security detects these apps as a Medium-Risk Threat. For more information, and to get fully protected, visit McAfee Mobile Security.

The Global Impact

This fake app campaign reached consumers around the world, with McAfee researchers identifying more than 1,900 unique apps across over 500,000 devices in more than 190 countries.

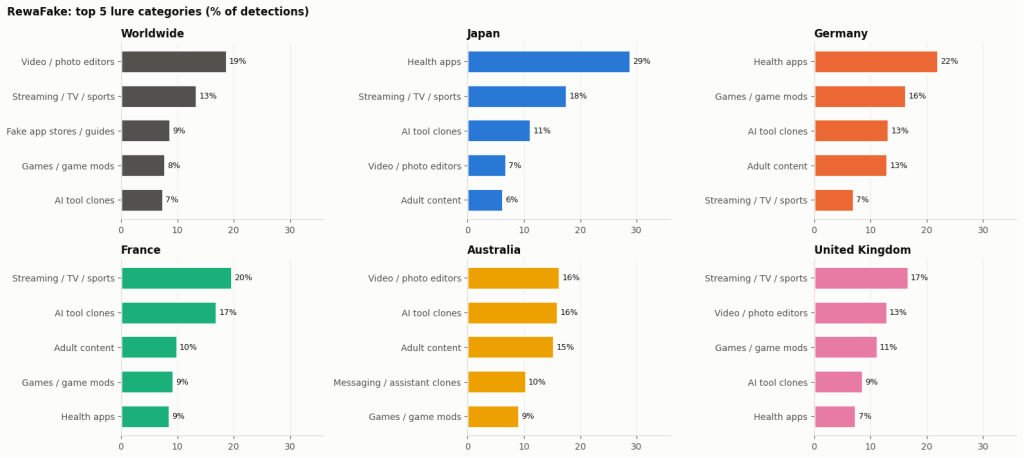
McAfee’s detection data shows how the campaign appeared across key markets. In the United Kingdom, McAfee recorded 11,862 detections, in Germany (5,016 detections), France (4,288), Australia (1,434), and Japan (944).

Market  Devices protected  Global rank  Share of global  Fake apps seen  Top 3 lures 
United Kingdom  10,582  #8 of 207  1.98%  970  Streaming/TV/sports (17%), video editors (13%), games (11%) 
Germany  4,465  #16  0.84%  444  Health apps (22%), games (16%), AI tools (13%) 
France  3,882  #19  0.72%  450  Streaming/TV/sports (20%), AI tools (17%), adult content (10%) 
Australia  1,293  #42  0.24%  306  Video editors (16%), AI tools (16%), adult content (15%) 
Japan  843  #55  0.16%  229  Health apps (29%), streaming/TV (18%), AI tools (11%) 

These figures represent fake app encounters identified by McAfee, not total infections. It reflects where McAfee detected these apps rather than the overall infection rate in each country.

Different Regions, Different Fake App Lures

While the campaign used the same underlying tactics worldwide, the types of apps detected varied by region. Globally, fake video and photo editors accounted for 19% of detections, followed by streaming, TV, and sports apps (13%).

A closer look at individual markets reveals some notable differences:

  • United Kingdom: Streaming, TV, and sports apps led at 17% of detections, followed by video and photo editors at 13%.
  • Germany: Fake health apps accounted for 22% of detections, followed by games and game modifications at 16%.
  • France: Streaming, TV, and sports apps were the most common at 20%, followed by AI tool clones at 17%.
  • Australia: Video and photo editors and AI tool clones were nearly tied, each accounting for approximately 16% of detections.
  • Japan: Fake health apps stood out at 29% of detections, followed by streaming, TV, and sports apps at 18%.

These findings highlight how the same fake app campaign can appear in very different forms depending on what consumers are looking for. Whether it’s a health app, an AI assistant, a streaming service, or a popular game, familiar names and recognizable branding can make a fraudulent app appear trustworthy.

The risk isn’t limited to one country or one type of app. It’s the same underlying deception: an app that promises a familiar service but delivers something entirely different.

The Financial Impersonators

We identified fake apps impersonating Zelle, PayPal, Apple Pay, Mir Pay, Binance and several banks. One fake PayPal app had been downloaded 10,000+ times.

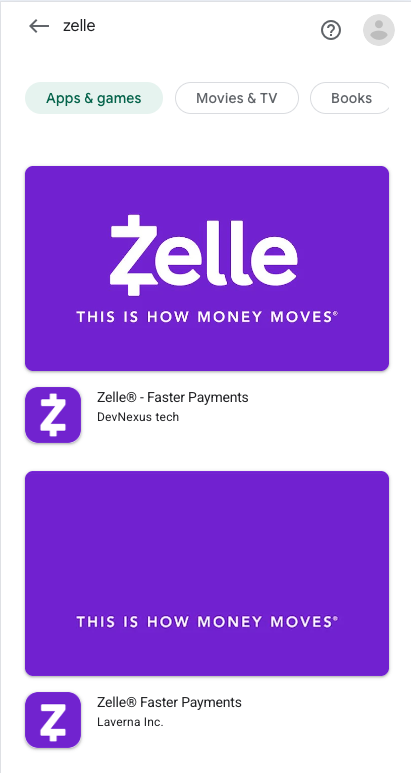
Zelle has no standalone consumer app: it lives inside your bank’s app so anyone searching Google Play for “Zelle” is already confused. And Apple Pay has no Android app at all, so users searching for it cannot find a legitimate result. Both are searches with no correct answer, which makes them ideal traffic to intercept.

Figure 1: Firsts result on Google Play of ‘Zelle’ search are Fake Applications

Figure 1: Firsts result on Google Play of ‘Zelle’ search are Fake Applications

Combine that with an in-app browser whose address bar is hidden and whose destination the operator controls remotely, and the risk profile of a fake banking app is simply not the same as a fake video editor even when both currently do nothing worse than show ads.

From the user’s perspective the current risk is straightforward: they search Google Play for “Zelle”, the first results include fake apps, and installing it delivers not a banking guide but a stream of full-screen ads. Tapping one leads to a page requesting their credit card details for a “free” trial that then bills them monthly.

What Users Actually Got: Gambling Inventory, on an “Everyone” Rating

In multiple cases we observed a gambling-style quiz funnel: “Win Mega Jackpot,” “50,000 COINS DAILY,” “PLAY FOOTBALL QUIZ,” “Play Now.”

Now consider who was looking at those store pages: Among the apps still available for measurement at the time of our analysis, the ones impersonating children’s and teenagers’ brands had been downloaded more than 86,000 times:

Downloads App title Package Name
50,000+ Roblox com.sitaram.robloxgame1
10,000+ Roblox com.sitaram.robloxgame3
10,000+ Netflix Game Controller netflixgamecontroller.uzair1
10,000+ Netflix Game Controller: Play netflixgamecontroller.uzair2
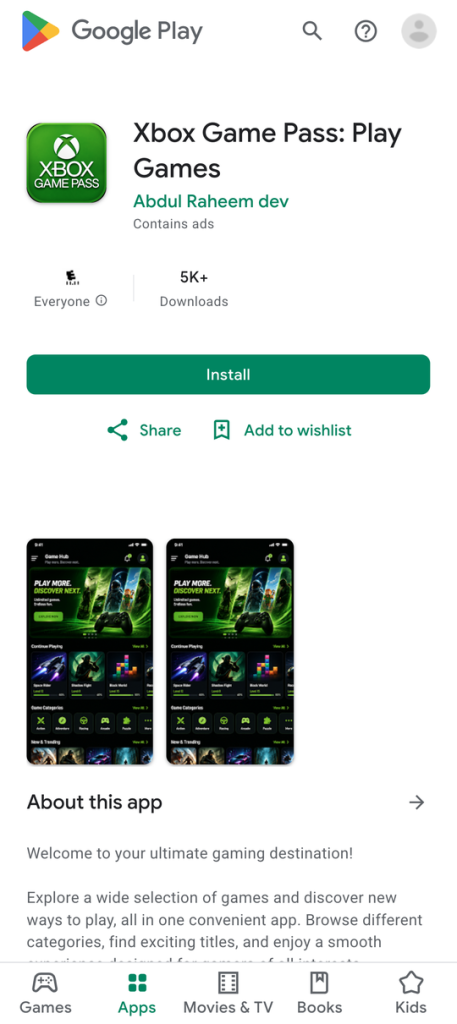
5,000+ Xbox Game Pass: Play Games xboxgame.abdul2
1,000+ Fall Guys for Mobile com.react.fallguysgame1

Across the full campaign we identified 37 apps impersonating games and services aimed at young players: Roblox, Minecraft, Fall Guys, Brawl Stars, Clash of Clans, Deltarune, Xbox Game Pass even GTA VI.

Figure 2: Fake Xbox App with over 5,000 installations

Figure 2: Fake Xbox App with over 5,000 installations

Every one of these listings carried an “Everyone” content rating.

So, the chain runs: a child searches Google Play for Roblox, installs an app called Roblox with the Roblox logo, rated suitable for everyone — and is funneled into gambling-style prize inventory that the operator can redirect at will. No exploit, no permission prompt, no warning.

The Searches With No Correct Answer

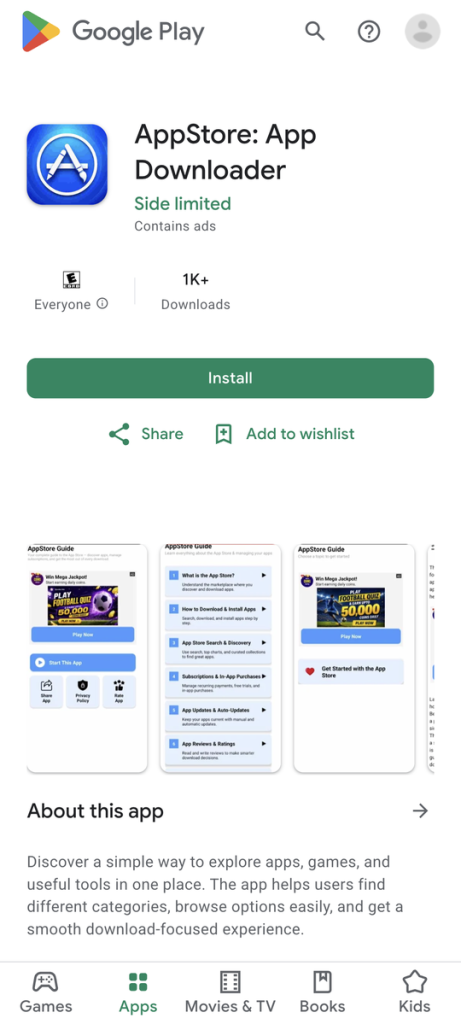
One application captured this strategy particularly well: Published as “AppStore: App Downloader,” the application used a legacy Appstore icon and presented itself as an Android version of Apple’s official software marketplace.

Figure 3: Fake AppStore on Google Play with over 1K Downloads

Figure 3: Fake AppStore on Google Play with over 1K Downloads

A legitimate Apple App Store cannot exist on Android because Apple operates the App Store exclusively for its own platforms, and the iOS applications it distributes are not compatible with Android’s operating system or application format. Any Android app claiming to be Apple’s App Store is therefore impersonating the service rather than providing the official marketplace.

“AppStore: App Downloader” was not an alternative marketplace but an advertising funnel disguised with Apple’s branding, rated for all users, and distributed through Google Play.

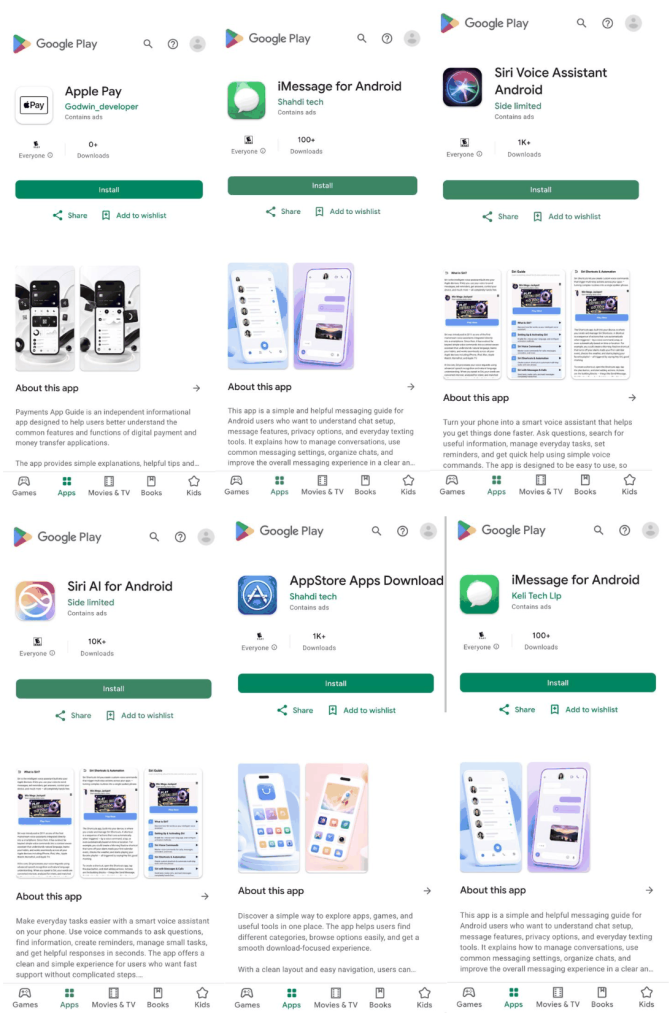
There is no App Store, Siri, iMessage, FaceTime nor Apple Pay app for Android. Zelle has no standalone consumer app, it lives inside your bank app. Every one of those is a search people perform on Google Play every day, and every one of them is a search with no legitimate result.

Figure 4: Multiple fake apps that does not officially exist on Android

Figure 4: Multiple fake apps that does not officially exist on Android

The user’s own intent is the vulnerability: they want the thing, they cannot have the thing, and something appears that looks exactly like the thing. No security control mediates that moment. It is not a technical failure at all: it is a person trusting a logo, which is precisely what logos are for.

How Are the Ads Displayed?

Each app is a shell. It wears the branding of something people search for — CapCut, Roblox, Zelle, PayPal, Netflix, Huawei Health, Xbox Game Pass, Siri, iMessage — and behind that branding it contains no real product. What it contains is a redirector.

On launch, the app contacts a server controlled by the operator:

`hxxps://rewadevelopments[.]online/data/.json`

The server replies with a small configuration block. One field in that block, `qureka_url`, holds a web address. The app takes that address and opens it in an in-app browser window, a Chrome Custom Tab, configured with the URL bar hidden.

In every case we observed, the address served was a gambling-style quiz site promising daily coin rewards. Users did not get a CapCut tutorial or a Zelle guide. They got an endless funnel of ad and quiz pages, monetized by the operator.

The mechanism matters more than today’s payload. Because the destination is fetched from the server at every launch, the operator can change where these apps send users at any moment, for any single app, without shipping an update and without passing store review again. An app wearing a bank’s logo, opening a browser window with the address bar hidden, pointed wherever the operator chooses, is a capability that can be used for phishing and credential exfiltration.

Figure 5: Ads severed from the website loaded in full screen that funnel to subscription fraud.

Figure 5: Ads severed from the website loaded in full screen that funnel to subscription fraud.

The full-screen ads users encounter are not served by the app. Its own ad slots are configured with Google’s public test IDs, which generate no revenue — so the app earns nothing from advertising itself. The ads come from the website the app opens: the destination supplied in the remote JSON configuration. That page’s ad inventory is filled with deceptive offers which, when tapped, lead to credit-card forms tied to subscription-fraud billing.

What Makes These Apps Interesting Is What They Do Not Do

There is no exploit, privilege escalation, rooting attempt, dynamic code loading, obfuscation, encrypted payload, or dropper chain. The applications request no dangerous Android permissions. From the perspective of conventional static analysis, their code presents few of the indicators typically associated with Android malware.

This campaign avoids many of those controls because its primary deception occurs outside the application code. Rather than exploiting a software vulnerability, the operators exploit the user’s trust in an official app store and in recognizable brands.

The post-installation behavior can remain technically simple, as it does here with advertising redirection, because persuading the user to install the application is the most critical stage of the operation.

The affected users did not need to follow a malicious link or sideload an APK from an unofficial forum. They searched an official application store for a product they recognized, and the search results presented an application with the expected name, logo, and visual identity.

How to protect yourself

  • Install financial apps only from your bank’s own website or a verified link. If you are searching for an app store for a payment brand, you are in the exact position this campaign targets.
  • Be suspicious of “guide,” “tutorial,” “helper” and “tips” apps for products you already use.
  • Legitimate services do not need a third party to explain them.
  • Check the developer’s name, not just the app name and icon. A real brand’s app is published by that brand.
  • If a product doesn’t exist on your platform, no app can provide it. There is no Apple Pay, Siri, or iMessage for Android.
  • Ignore install counts as a trust signal. Several of these apps had tens of thousands of downloads.
  • Run mobile security software. McAfee Mobile Security detects this family.

Conclusion

Mobile security has genuinely improved. Permissions are narrower, sandboxing is stronger, exploit mitigations are routine, store review catches more than it used to, and AI now finds obfuscated payloads at a scale no human team could match. Every one of those defenses works but none of them was tested here.

Attackers move to one part of the system that cannot be patched: the judgment of the person holding the phone. And they apply pressure exactly where that judgment is weakest — a familiar logo, an official store, a name that matches what you searched for.

These apps are adware or a medium risk threat rather than malware because the fraudulent content is not theirs. The app opens a web page chosen by its operator; that page’s advertising slots are filled by open programmatic ad exchanges, which sell to whichever advertiser bids. The subscription-fraud pages belong to those advertisers.

As threat actors continue to exploit trust rather than software vulnerabilities, McAfee remains committed to protecting users, raising awareness, and collaborating across the industry to ensure that seemingly harmless applications do not evolve into large-scale fraud operations.

 IOC

Prevalent Apps

App title Package Play downloads SHA-256 (primary build)
Roblox com.sitaram.robloxgame1 50,000+ 4f7b36963518e701276c77c1cad88d16fe64e8025c5223141c9af0eeb954ea63
Roblox com.sitaram.robloxgame3 10,000+ c56d49a2f323ca0333778964fd58a7399aa60c8136a6a178adc1f222747b353f
Netflix Game Controller netflixgamecontroller.uzair1 10,000+ 2bdbd5c78a9d08b69983b965ae466210329b09eb26e5b491acdae9b822c729ab
Netflix Game Controller: Play netflixgamecontroller.uzair2 10,000+ 8cf714e0dab975c12cb5ac16837d7d2748a7f1672a3210a0e8e247dc405f8c68
Xbox Game Pass: Play Games xboxgame.abdul2 5,000+ 37539a20f07bd29e9285e7266ab29015c5467241bea43eee48f77769c42bbc7e
Fall Guys for Mobile com.react.fallguysgame1 1,000+ d9ae6d844bf9269bee7d1f67f2f3d9e1d932974733068639c7204c2c92c391b1
Capkut – Video Editor com.flintos.capcut2 50,000+ ba7a00fd597c04b7aa2efb59da853b1fcf34ba3bb63e7fbef2b9d9ef1a497641
Capcut Video Editor 2026 com.capcut.capvideoeditorapp58 10,000+ 9b9e08b176d12c5e388b33c3e1fcdf2ba52b94cc6b310b56e3596eb783c26569
Siri Voice Assistant Android com.shahdi.siri2 10,000+ b015de54db5073758909e5f3eaa90e73d7ff6f923195569d22395808b99a5557
Siri for Android com.shahdi.siri1 5,000+ 9a0881a67a7c35592216e0896e184d1ed960ef5c2280a6dafcfcbc0dcb29c099
Siri for Android com.keli.siriapp1 1,000+ 30a9f7461a0c11061b9349004f3dcd39ec763ec8bf1520ce655653fca67e183e
iMessage for Android com.keli.imessage3 100+ ac46add9b7bb09779ab0a51924601e649431153c40d95c2ecc995e614ff2b89d
iMessage Android App com.shahdi.imessage2 100+ 83a95ceb22e24d5486f997d3ab7a8fa336cbf52c6489bfd20b285ccb16237f8e
Apple Health for Android com.godwin.applehealth2 1+ 5d2c823acf6e719553688626a113e79842d186de7d3203c011b032eb2f87adca
Huawei Health huwaei.health1 10,000+ 695eca22217b60b6218fbef51bcf660e569f7ce36c1d73a4646494d5489ae352
Casino Plus PH casinoplus.pindo3 10,000+ 3a50fa0ee7be36cbb1052254fbfdc0602abd7f52d69d7dc32d5c9ea6148ed16c
Aviator Game com.aviator.aviatorgamejamantech2 1,000+ 18af2b9a1e9db5f85c789252dbb0048a244e0a181f88b31c0969e6789b9657b8
GTA VI com.react.gta6game1 N/A 78a098470a7926dc0bd36c625032fd421587aea88200fdbb877dbc655110c5f5


Financial Impersonators

App title Package Play downloads SHA-256 (primary build)
PayPal – Fast Payments com.paypal.wallawalled11 10,000+ 601639168ac739e08fd267e86ba7eae440116e5b295fe01c00098bc2d9845405
Zelle® Easy Secure Payments com.premkumar.zelleapp5 100,000+ 8a943f50417c53fd9d8f522fdb69d76c96ca386c2416a43d20f9181350282bd1
Zelle® Faster Payments com.premkumar.zelleapp2 50,000+ 84fac9f350cd9d627392125cd3b06bac62321a2a36954605bd4680383ee86ae2
Zelle® – Faster Payments com.zelleapp.devnexus2 10,000+ 99122b355ba17d6fa55625414f9a48f8755f4a438374ce85c73c751e9f4fe6b6
Zelle® – Online Payments com.mhd.zelleapp2 N/A 0022360894f15199c5f2fda5b5d8be3d26045d12ad50d80d02a23741601345af
Apple Pay com.godwin.applepay3 N/A aa6883d64438a4374a5f44b5180d8ff12ca3d0c9423946df092420291007fdaf

The post Android/RewaFake: Uncovering a Large-Scale Fake Apps Adware Campaign on Google Play appeared first on McAfee Blog.
  •  

How to Shop Safely During Amazon’s October Prime Big Deal Days Shopping Event

Every time a big Amazon sales event takes place, shoppers flock to the deals. And scammers know it.

This year, Amazon has added a new Prime Day event Oct 6-7 called Amazon’s Prime Big Deal Days event. And in preparation, we’re breaking down the ways scammers use AI-driven manipulation to create fake Amazon websites, send delivery scam texts, impersonate customer support agents, and make scams look more convincing than ever. 

Recent McAfee research suggests shoppers may be especially vulnerable in 2026. Forty percent of consumers say they would trust a lower-priced deal without verifying it first, while 29% admit they would skip researching a seller if the price looked good enough.

That combination of urgency, discounts, and increasingly sophisticated scams creates the perfect environment for fraud. 

“Anyone who has ever fallen for a scam thought they would recognize one first,” McAfee’s Head of Threat Research Abhishek Karnik reminds shoppers.  

“That confidence is part of what scammers count on,” he says. “Tools like McAfee exist precisely for those moments, flagging suspicious links, messages, and offers in real time, before a split-second decision becomes a costly one.”  

Here are the most common Amazon Prime Day scams to watch for in 2026 and the warning signs that can help you avoid them. 

Scam Type  How It Works  Red Flags 
Fake shopping websites  Fraudulent websites mimic real retailers and disappear after collecting payments  Prices far below competitors, little company information, newly created websites 
Fake social media ads  Ads promote products that never arrive or are counterfeit  Too-good-to-be-true discounts, limited reviews, unfamiliar brands 
Delivery notification scams  Fake package alerts claim there is an issue with your shipment  Unexpected texts, suspicious links, requests for payment 
Retailer impersonation scams  Messages claim there is a problem with your account or order  Urgent language, login requests, unfamiliar sender addresses 
QR code scams  QR codes redirect shoppers to fraudulent websites  Codes placed on flyers, posters, packages, or public locations 
Brushing scams  Unsolicited packages arrive at your home  Items you never ordered, requests to scan codes or leave reviews 
Fake recall scams  Messages claim a recent purchase has been recalled  Requests for payment, account credentials, or personal information 

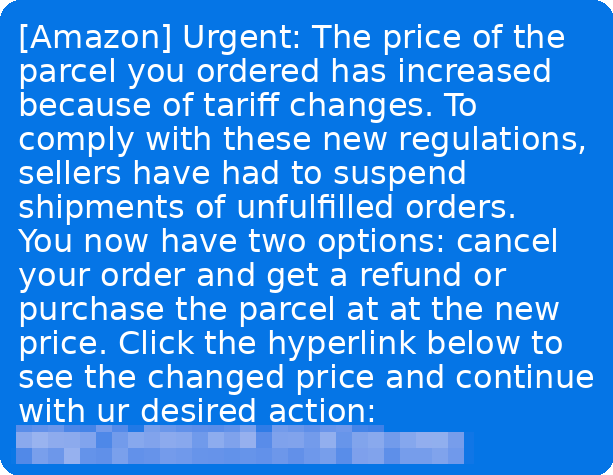
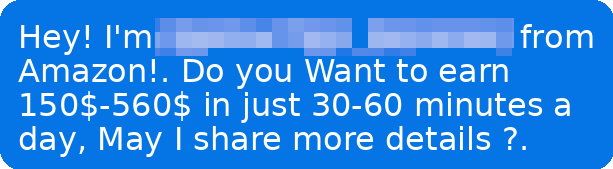
Here are examples of Amazon-related scam texts our team came across near Prime day last year, McAfee’s Scam Detector helped detect and stop these messages:


Figure 1. Examples of Amazon tariff and job scams


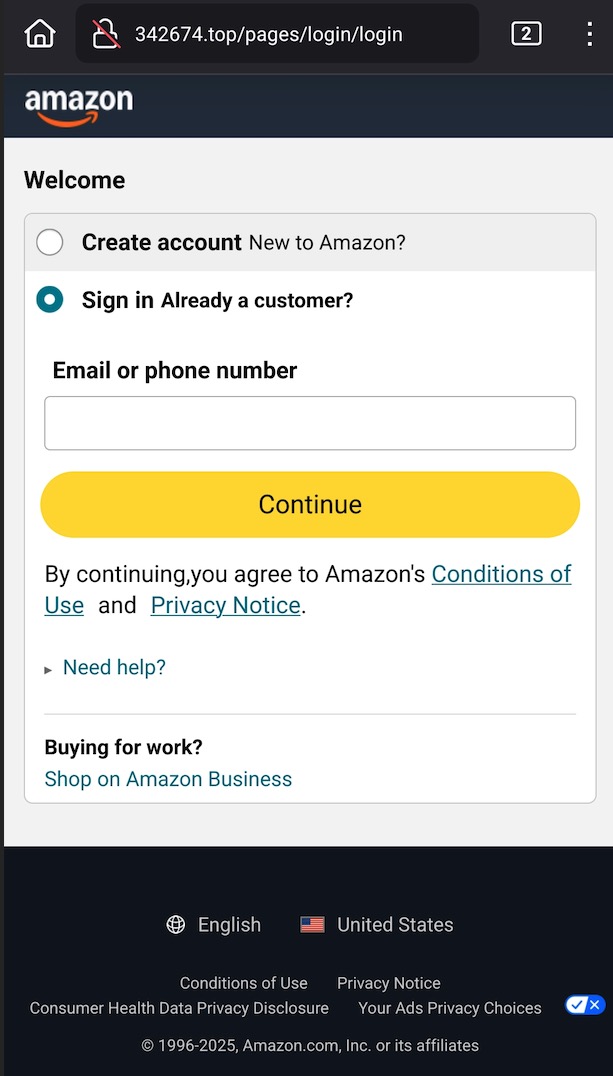
Figure 2. An example of a fake Amazon sign-in page.


Figure 3. Examples of Amazon phishing scams


Why Prime Day Scams Work 

Major shopping events create the exact conditions scammers rely on: urgency, distraction, and the promise of savings. 

McAfee research found: 

  • 82% of consumers prioritize finding the cheapest deal when shopping online  
  • 55% spend more time hunting for discounts  
  • 40% would trust a lower-priced deal without verifying it  
  • 29% would skip researching a seller if the deal looked especially good  
  • 23% feel pressure to act quickly before a deal disappears  

“What the data reflects is that economic pressure has effectively done some of the scammer’s work for them,” says Abhishek Karnik, Head of Threat Research at McAfee. “When consumers are already primed to move quickly and prioritize price over authenticity, it takes far less effort to push them toward a bad click or a fraudulent purchase.”  

How to Protect Yourself This Prime Day 

The good news? These scams are preventable if you know what to watch for and take the right precautions. Here’s your defense playbook: 

Verify Before You Trust 

  • Amazon will never call you about suspicious account activity or unauthorized purchases 
  • Always log into your Amazon account directly through amazon.com to check for real issues 
  • Use Amazon’s Message Center – all legitimate communications from Amazon appear there 
  • Never give personal information, passwords, or payment details over the phone 

Watch for Red Flags 

  • Urgent language demanding immediate action (“Your account will be closed in 24 hours!”) 
  • Requests for payment via gift cards, wire transfers, or cash 
  • Claims that you need to “verify” or “legalize” your money 
  • Transfers to “government agencies” during the same call 
  • Pressure to keep the call secret or not hang up 

How to Protect Your Shopping Experience 

  • Enable two-factor authentication on your Amazon account 
  • Only shop on secure websites (look for “https://” and the padlock icon) 
  • Monitor your bank and credit card statements regularly 
  • Never click links in suspicious emails – go directly to the retailer’s website instead. 
  • Use reputable online protection like McAfee to keep you safer from online shopping scams 
  • Trust your gut – if it feels too urgent or too good to be true, it probably is 

Together, these protections are designed to address the broader range of online risks people face every day. 

Check out the McAfee our latest offer this Amazon Prime Big Deal Days Event here.

The post How to Shop Safely During Amazon’s October Prime Big Deal Days Shopping Event appeared first on McAfee Blog.
  •  

Frontline Education Data Breach: What Happened and How K–12 Staff can Stay Safe

On October 2, 2026, BleepingComputer reported that ed-tech software provider Frontline Education suffered a data breach exposing personal information of K-12 school district employees, including Social Security numbers, email addresses, and physical addresses.

Frontline internally identified unauthorized access on August 14, 2026, stemming from a security flaw in a third-party application, and began notifying impacted school administrators via Cyberscout on October 1, 2026. Because Frontline provides administrative and workforce management tools to over 80,000 schools across the country, the exposure directly impacts teachers, administrators, and educational staff whose employee records were managed through the platform.

How the Frontline Education Data Breach Occurred

According to reporting by BleepingComputer and discussions among IT administrators from multiple school districts in the r/k12sysadmin Reddit community, attackers exploited a vulnerability in a third-party software application integrated with Frontline Education’s systems. This vulnerability enabled unauthorized access to internal databases containing administrative and workforce management records.

Frontline discovered the intrusion on August 14, 2026. Rather than issuing an immediate public statement on its corporate website, Frontline partnered with Cyberscout to dispatch private notification emails directly to superintendents, business managers, and IT personnel starting October 1, 2026. The exposed data includes critical personally identifiable information:

  • Full names and physical street addresses
  • Direct email addresses associated with district employment
  • Social Security numbers (SSNs)

Warning Signs That Your Personal Information was Compromised in a Data Breach

Because compromised Social Security numbers and contact details enable identity theft and targeted phishing, school district employees should watch for these specific warning indicators:

  • Unsolicited verification requests: Emails or calls claiming to represent Frontline Education, Cyberscout, or district HR asking you to confirm personal details or login credentials.
  • Targeted phishing (spear phishing): Messages addressing you by name and referencing your specific school district, job title, or administrative role.
  • Unfamiliar credit inquiries: Alerts from credit monitoring services showing credit checks or new account applications that you did not initiate.
  • Tax filing irregularities: Communications from the IRS or state tax authorities indicating that a tax return has already been filed using your Social Security number.

How School Employees can Stay Safe

If you are a K-12 school employee whose district utilizes Frontline Education software, take these immediate actions to secure your personal information:

  • Place a fraud alert or credit freeze with all three bureaus. Contact Equifax, Experian, and TransUnion to lock your credit files. A credit freeze prevents lenders from accessing your credit report, stopping bad actors from opening unauthorized accounts in your name.
  • Verify notification communications. Confirm with your district’s IT or HR department whether your district was impacted before clicking links in breach notification emails. You can also visit Frontline’s dedicated identity protection portal directly.
  • Enable multi-factor authentication (MFA). Turn on MFA across all personal email accounts, financial portals, and school district access systems to prevent unauthorized sign-ins.
  • Monitor credit reports at the source. Request free annual credit reports through the official annual credit report website to review active accounts and financial inquiries.

What to Do If You Have Already Been Targeted

If your Social Security number or personal financial details have already been misused, complete the following recovery steps immediately:

  • Stop contact with suspicious senders. Do not reply to unverified emails, texts, or phone calls requesting additional personal information.
  • Notify your financial institutions. Contact your bank, credit card issuers, and payment providers to alert them of potential identity theft and place fraud holds on compromised accounts.
  • Report identity theft to the federal government. File an official identity theft report at the FTC identity theft portal to receive a recovery plan and official documentation for disputing fraudulent accounts.
  • Freeze your credit. If you have not yet frozen your credit, do so immediately with Equifax, Experian, and TransUnion.
  • Change affected account credentials. Update passwords for primary email accounts and school portal logins. Use complex, unique passwords for every service.
  • File a report with local law enforcement. If you incur financial losses or discover fraudulent accounts opened in your name, submit a police report and request a copy for your dispute records.
  • Maintain detailed documentation. Retain copies of notification letters, email headers, police reports, and fraudulent transaction statements.

How to Report the Threat and Next Steps

To report suspicious activity or document fraudulent use of your information resulting from this incident, use official reporting channels:

Data breaches often have a long tail, as compromised details can resurface months or years after the initial breach. Long-term protection relies on strong password hygiene, routine credit checks, and ongoing caution with unexpected communications. Automated monitoring tools can alert you if exposed credentials surface online, while consistent security habits and swift action remain your primary defense.

The post Frontline Education Data Breach: What Happened and How K–12 Staff can Stay Safe appeared first on McAfee Blog.
  •  

Cybersecurity Awareness Month 2026: 4 Simple Ways to Stay Safer Online

Cybersecurity used to be easier to picture. It was antivirus software protecting the family computer. A suspicious email you knew not to open. A password you were reminded to make a little harder to guess.

Today, our digital lives don’t fit neatly inside a computer. And neither do the risks.

A scam text can follow you into a purchase. Personal information scattered online can fuel unwanted calls and messages. An account you haven’t thought about in 10 years can still hold information about you. And every ordinary interaction, from following a delivery link to shopping at a new store, can require a moment of calculation: Is this real? Is this safe?

McAfee’s latest research shows how much work that’s becoming. Nearly three-quarters of Americans (74%) say they feel the need to double-check most things online before trusting them, while 62% say figuring out what’s real takes more mental energy than it did a year ago.

That’s why this Cybersecurity Awareness Month, we’re thinking about cybersecurity a little differently.

What is Cybersecurity Awareness Month?

Every October, Cybersecurity Awareness Month encourages people and organizations to build better habits for staying safe online.

For 2026, the Cybersecurity and Infrastructure Security Agency (CISA) is marking the month with the theme “Securing the Next 250.“ CISA points to technologies such as artificial intelligence that are accelerating how quickly attackers can identify and take advantage of weaknesses in computer systems.

For individuals and families, CISA recommends four basic actions:

  • Avoid and report phishing scams.
  • Use strong passwords.
  • Use multifactor authentication and a password manager.
  • Keep software updated.

They’re good fundamentals. Use unique passwords and multifactor authentication when they’re available. Install security updates instead of putting them off indefinitely. And treat unexpected requests for money or information with caution.

But good cybersecurity today also means looking beyond the traditional security checklist.

McAfee’s Cybersecurity Awareness Month Tips: 4 Quick Fixes

1. Make yourself harder for scammers to find

If your phone constantly rings with unknown callers or your inbox is overflowing with unwanted messages, consider looking at how much information about you is available online.

Your name, phone number, email address, home address, and other personal details can appear on data broker and people-search sites. That information can contribute to the pool of data available to marketers, and potentially provide useful ingredients for scammers trying to make a message more convincing.

You can’t make yourself invisible online. But you can reduce unnecessary exposure.

Personal Data Cleanup scans data broker sites for your personal information and can help with its removal, depending on your plan. Think of it as reducing some of the information about you that’s unnecessarily floating around online.

It’s a useful shift in mindset: don’t just get better at dealing with unwanted contact. Look for opportunities to reduce your exposure in the first place.

 2. Close the accounts you forgot you had

Remember Myspace?

What about that Tumblr you haven’t touched in a decade? The shopping site you ordered from once? An old forum account? Or one of the dozens of apps and services you tried, abandoned, and promptly forgot existed?

Our digital footprints are full of these little leftovers.

And your digital footprint isn’t only what you post publicly. It’s also the accounts you’ve created and the companies you’ve entrusted with pieces of your information over the years.

An abandoned account may still contain an email address, old login information, purchase history, personal details, or other data. If a service you no longer use experiences a breach someday, that’s one more place where information associated with you could potentially be exposed.

A good, simple rule: If you don’t use it and don’t need it, consider deleting it.

McAfee’s Online Account Cleanup can help find accounts associated with your email and help you identify ones you may want to remove. We’ve also updated the experience to help prioritize higher-risk accounts, so you can focus your attention where it matters.

This Cybersecurity Awareness Month, see how many pieces of your old internet life you can finally retire.

 3. Keep your public browsing safe

Airport Wi-Fi. Hotel Wi-Fi. Coffee-shop Wi-Fi.

Using a network you don’t control doesn’t need to become a cybersecurity event every time you leave the house.

A VPN, or virtual private network, encrypts the internet traffic traveling between your device and the VPN service. That adds privacy to your connection, particularly when you’re using unfamiliar or unsecured networks.

The important part isn’t remembering to become extra vigilant every time you sit down at a coffee shop. It’s making protection easier to use consistently.

With Secure VPN, you can add protection to your internet connection when you’re away from networks you know and trust.

That’s the kind of cybersecurity we like: something working quietly in the background while you get on with whatever you actually opened your laptop to do.

McAfee will let let you know if you have weak internet security.

McAfee will let let you know if you have weak internet security.

4. Check the destination before you trust the invitation

Think about how many times a day something online asks you to go somewhere else.

A text sends you to track a package. An email asks you to sign in. A search result takes you to a new website. An ad introduces you to a store you’ve never heard of.

Scammers rely on those transitions.

McAfee Labs’ 2026 analysis of text scams found schemes impersonating or referencing everything from deliveries and bank accounts to jobs, tolls, shopping, subscriptions, investments, and utilities. Many are designed to get the recipient to click, respond, or move the conversation somewhere else.

You can inspect every URL yourself. But that puts the work right back on you.

McAfee’s Scam Detector can help warn you about risky websites and links before an everyday click becomes a bigger problem.

It’s a small example of a larger principle at McAfee: You shouldn’t have to be the cybersecurity expert. That’s our job.

While You’re At It: Give Your Browser a 5-Minute Cleanup

If you have another five minutes this Cybersecurity Awareness Month, open your browser settings.

Start with your extensions.

Browser extensions can be genuinely useful, but some require significant permissions to function. If you have extensions you don’t recognize or haven’t used in years, remove them. The fewer unnecessary tools you give access to your browsing, the fewer things you’re relying on to behave responsibly.

Next, check which websites have permission to send you notifications. Remove ones you don’t recognize or no longer want. Unwanted browser notifications can sometimes imitate security alerts or use other alarming messages to get your attention.

Finally, check for browser updates, or simply turn on automatic updates if your browser supports them.

You don’t have to become an expert on browser security. You’re just cleaning out things you no longer need.

A New McAfee Experience To Do More of The Work For You

This Cybersecurity Awareness Month also comes just as we’re rolling out an updated McAfee experience.

The idea behind it connects directly to what our research is telling us.

Seventy-four percent of Americans feel the need to double-check most things online before trusting them. Sixty-two percent say deciding what’s real takes more mental energy than it did a year ago.

Good protection shouldn’t add another set of things to check.

The new McAfee experience brings protection for personal information, connections, and devices into one connected experience across PC, Mac, mobile, and tablet. It’s designed to make it easier to understand what’s protected, what needs your attention, and what McAfee can help handle. That can mean alerting you to suspicious messages and links, helping identify risky websites, monitoring for exposed personal information, protecting your connection, finding forgotten accounts, or helping remove personal information from data broker sites.

We’ve also updated tools including Online Account Cleanup to help people prioritize higher-risk accounts and Personal Data Cleanup to make it easier to understand what personal information is being found and removed on their behalf.

The philosophy behind those changes is simple: Good protection shouldn’t create another job for you.

New McAfee Experience - iPhone Mockup

One Key Takeaway

Our digital lives are simply our lives now.

We shop, date, bank, work, travel, talk to family, look for jobs, manage our health, and discover new things online. And the risks can move just as easily between those digital and physical worlds.

So this Cybersecurity Awareness Month, don’t worry about becoming a cybersecurity expert.

Reduce what you expose. Close what you don’t use. Protect the connections you rely on. And let technology help you decide what’s safe.

The post Cybersecurity Awareness Month 2026: 4 Simple Ways to Stay Safer Online appeared first on McAfee Blog.
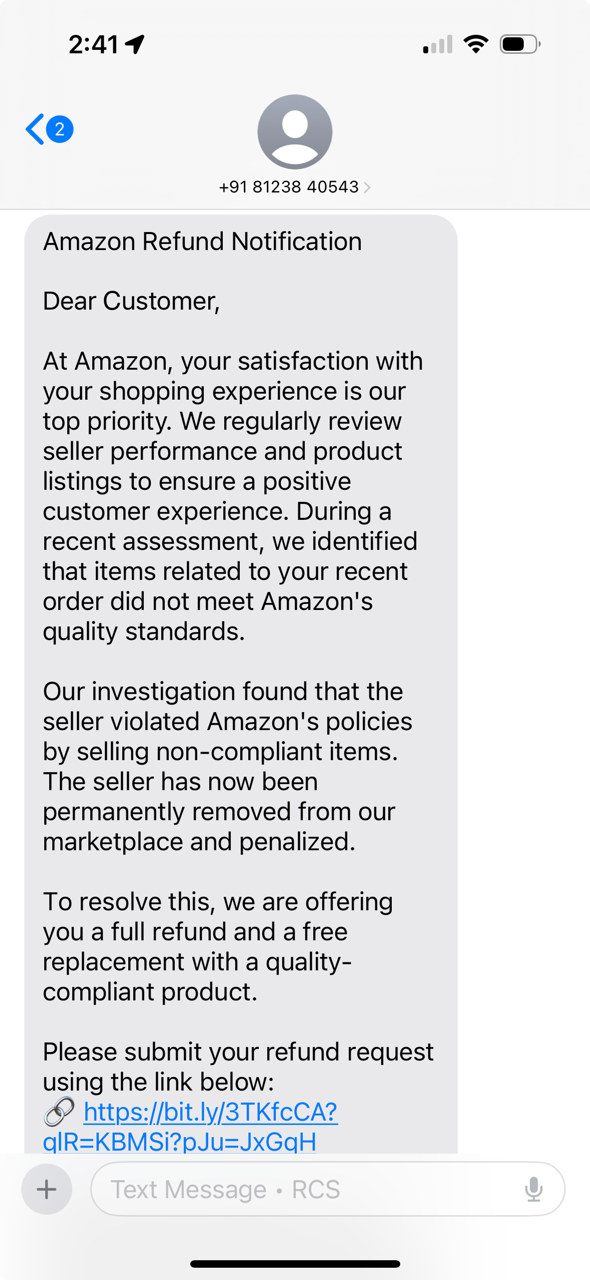
  •  

BigCommerce Ribon App Breach: What It Is and How to Protect Yourself

Customer names, email addresses, phone numbers, and shipping addresses were exposed across multiple e-commerce storefronts when attackers breached two third-party shopping applications. The cyberattack was confirmed when UK online spirits retailer Master of Malt notified its customers on September 18, 2026 of the risk to their personally identifiable information (PII). The following day, they informed customers that Master of Malt was not the target of the attack and that “The attack was against Ribon, which was installed on hundreds of BigCommerce stores.”

In a September 2026 statement reported by BleepingComputer, e-commerce platform BigCommerce alerted merchants that unauthorized actors accessed shopper records between September 13 and September 17, 2026. BigCommerce confirmed its core platform remained uncompromised and uninstalled the affected software on September 17, 2026, to block cybercriminals from further access.

How the BigCommerce Ribon App Breach Worked

According to BigCommerce’s comments to BleepingComputer, the data breach originated from a system compromise at Fastr, the parent company of third-party app developer “Be A Part Of.” Attackers obtained API application keys for the Ribon and Ribon 1.5 e-commerce apps, which merchants integrate into BigCommerce storefronts to manage customer features.

Because e-commerce integrations grant application keys permission to read store data, holding valid credentials allowed attackers to generate legitimate platform API requests. From September 13 to September 17, 2026, the unauthorized actor extracted customer records across affected stores and injected malicious scripts into a small number of storefronts. BigCommerce uninstalled the applications on September 17, 2026, and notified impacted merchants directly.

Warning Signs That Your Personal Data May Have Been Exposed

Exposed contact details often serve as the foundation for follow-up phishing attempts and impersonation scams. Watch for these specific indicators:

  • Unsolicited credential or payment requests: Watch for unexpected emails, texts, or phone calls claiming to be from affected retailers that ask for account passwords, PINs, or financial details.
  • Urgent payment or store verification messages: Be skeptical of communications demanding payment confirmation or immediate money transfers due to an alleged processing error or security update.
  • Suspicious login and verification links: Avoid clicking links in text messages or emails that direct you to non-official login portals or request personal information.
  • Requests for non-standard payment methods: Treat any demand for wire transfers, prepaid gift cards, or cryptocurrency as a major scam indicator.

 How to Protect Yourself After a Data Breach

Protecting your personal accounts after news of a data breach requires proactive credential management and exercising caution with calls and emails. Take these actions to help protect yourself:

  • Verify sender identity before responding. Legitimate retailers will not contact you unexpectedly to ask for sensitive credentials or payment information over phone or email.
  • Inspect email header details and website URLs. Ensure links lead directly to official domain names rather than lookalike URLs.
  • Use unique passwords across online accounts. Ensure passwords used on e-commerce sites are not reused on email or banking portals.
  • Enable multi-factor authentication (MFA). Turn on MFA across primary email and shopping accounts to add a verification layer beyond passwords.

What to Do If You Have Already Been Targeted

If your data was exposed or you received a breach notification from an affected BigCommerce merchant, take these immediate steps to secure your identity and finances:

  • Stop contact and do not send money. Discontinue communication with any sender requesting credentials or payments related to recent purchases.
  • Contact your bank, card issuer, or payment app immediately. Report potential fraud or stop suspicious transactions if payment details were compromised.
  • Update exposed passwords. Change login credentials and turn on multi-factor authentication for affected merchant accounts and any accounts where you reused passwords.
  • Freeze your credit reports. Consider a credit freeze with Equifax, Experian, and TransUnion if you suspect broader personal identity data exposure.
  • Document all suspicious interactions. Keep records of suspicious activity, including phone numbers, message transcripts, email headers, and receipts.

Next Steps After the BigCommerce Data Breach News

If you encounter phishing attempts or fraudulent activity linked to this breach, report the incident directly to official regulatory and law enforcement channels. You can submit details to the FBI Internet Crime Complaint Center, report deceptive or suspicious messages through the Federal Trade Commission, or notify the impacted retailer directly through the customer support portal on its primary website.

The BigCommerce Ribon app incident demonstrates how compromised third-party application permissions can expose customer records even when core e-commerce platform infrastructure remains secure. Verifying sender credentials and maintaining separate passwords across online accounts helps mitigate personal risk when supply-chain breaches occur.

The post BigCommerce Ribon App Breach: What It Is and How to Protect Yourself appeared first on McAfee Blog.
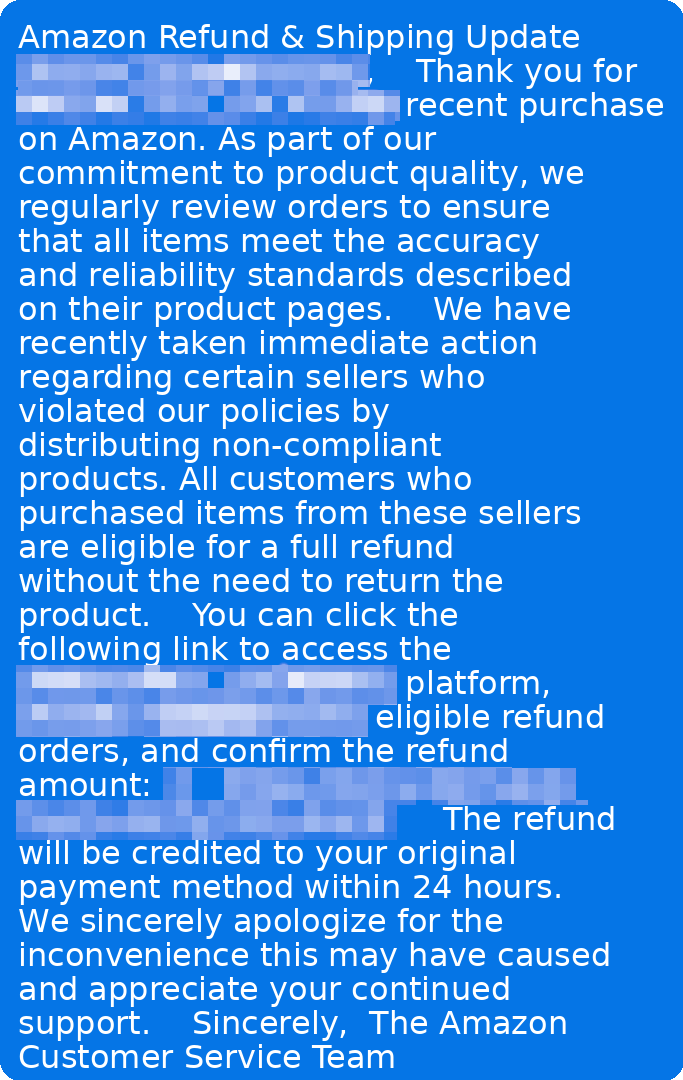
  •  

There’s Safe. And There’s Safer With McAfee: Transformational Protection

For a long time, being safe online came with a relatively familiar set of rules.

“Don’t click suspicious links.”
“Keep your software updated.”
“Be careful about what you share.”

But today, AI is everywhere. And it’s rapidly evolving and drastically changing what it means to trust what we see and hear online. It can make scams more convincing and easier to create at scale, while personal information available online can make those scams feel remarkably specific to us.

As AI reshapes nearly everything we consume and do, our daily interactions all come with an added mental burden: the feeling that you have to question everything.

Our research found that nearly three-quarters of Americans (74%) feel the need to double-check most things online before trusting them.

That finding stuck with me because it captures something bigger than concern about any one cyberthreat: Trust itself is becoming time-consuming work.

In a world where normal, everyday interactions put people at risk, consumers need protection that keeps them safe in every moment, feels simple, and works quickly and proactively.

Meet the new McAfee: a completely transformational safety solution that protects you when you know you need it, and when you don’t.

Always On. Simple and Easy. Personalized and Proactive.

This marks a shift from reactive security to proactive safety that helps you identify risks and take action before any damage is done.

I experienced a great example of it recently. I was getting on a plane and connected to the public Wi-Fi. McAfee let me know that my VPN had automatically turned on to help protect my connection.

I didn’t have to remember to take a security step. I didn’t have to search for a setting or wonder whether I had done the right thing. I didn’t have to know that I should be securing my connection on public Wi-Fi. And I didn’t have to know what a “VPN” is (virtual private network for those who are wondering!) The protection was simply there when I needed it. Always on. Simple and easy. Personalized and proactive.

That small moment captured something much bigger about the experience we want to create.

Scammers will start taking it personally

McAfee has been protecting people for decades, and for many, our name is still synonymous with antivirus. But in a world of accelerating AI, people’s digital lives no longer fit neatly inside a single device, and neither do the risks they encounter.

That’s why the new McAfee experience is designed to do much more than protect individual devices. It helps protect the things people rely on every day, including their personal information, connections, devices, and accounts, while making it clearer what’s safe, what needs attention, and what McAfee can handle for them.

McAfee’s new product experience seamlessly protects your personal info, finances, connections and devices so you can shop, text, bank and browse with confidence, delivering advanced and comprehensive protection at every moment.

This is merely an evolution of what McAfee has always been here to do: keep people safe- from today’s threats and tomorrow’s.

McAfee. Safer Than Safe.

Our new brand is an expression of that same evolution.

Safe is reacting. Safer is preventing.

Safe is worrying about tomorrow. Safer is enjoying today.

Those contrasts capture what Safer Than Safe means to us. It’s about giving consumers greater confidence instead of building on decades of fear associated with scams, malware, risks, alerts, and the protection industry broadly.

With the growing concern over AI and the speed at which it’s evolving, there has never been a more important moment to provide critical safety solutions proactively and simply. And that’s the moment we’re meeting.

That thinking shaped a McAfee brand that is brighter, simpler, and more human. The experience of being protected shouldn’t be defined by warnings and complexity, and neither should the brand behind it.

McAfee’s “Safer Than Safe” brand promise, the new experience simplifies security into one holistic safety solution:

  • Simple & Easy – McAfee’s new experience does the hard work for you. Consumers no longer need to understand complex threats, technical language or how and where to find tools or settings to turn on the protections they need.
  • Personalized, Proactive Assistance – Designed to help consumers stay a step ahead with proactive notifications, clear guidance and easy steps. McAfee surfaces timely and personalized alerts when your information or devices are at risk, with guided actions that explain what is happening and what to do next in plain, easy-to-understand language.
  • Always-On, Unified Product – McAfee protects you everywhere you are and whatever you’re doing. The new experience brings data, identity and threat protection together into one connected experience across all your devices, so staying safe is seamless and easy.

AI will continue to change how we create, communicate, and connect. It will bring extraordinary possibilities and new risks. We cannot expect people to study every development closely enough to recognize every new way their trust might be tested.

Consumers shouldn’t be security experts. That’s our job.

McAfee. Safer Than Safe.

The post There’s Safe. And There’s Safer With McAfee: Transformational Protection appeared first on McAfee Blog.
  •  

What Scams Look Like in Your State: A 50-State Breakdown

No matter where you live in the U.S., AI-driven scams and deceptive content are increasingly filling our feeds, alerts, and inboxes with moments that make us stop and ask: “Is this real?”

But the scams and threats Americans encounter aren’t the same everywhere. Where you live can shape the types of scams reaching your devices, how often you encounter them, and even how those experiences affect the way you behave online.

This 50-state breakdown combines McAfee consumer research with McAfee Labs data to show how Americans are experiencing scams, how those experiences are affecting trust and behavior online, and which text-based scams are reaching devices across the country.

The consumer findings come from a nationally representative survey of 5,000 U.S. adults, with 100 respondents in each state. The survey explores people’s exposure to scams, financial losses, changing online behaviors, concerns about AI and the mental effort involved in deciding what to trust online.

Alongside those findings, McAfee Labs analyzed text-based scam activity across the U.S. from May through July 2026. That data provides a view into the volume, concentration and types of scam texts McAfee observed in each state during the three-month analysis period.

Together, the two datasets offer different views of the same problem: what people say they are experiencing and how it affects them, alongside the scam activity McAfee is seeing in the wild.

Infographic - USA Map Dominant Scam Category by State

Alabama

Key takeaway: Alabama had the highest scam-text rate per device in McAfee’s analysis, while scam concerns are also changing how residents behave online.

  • 66% say figuring out what’s real online takes more mental energy than it did a year ago.
  • 60% check whether something online is legitimate at least weekly.
  • 19% say they do that checking several times a day.
  • 45% have encountered an AI-generated image presented as real.
  • 83% are concerned AI is making scams harder to recognize.
  • 64% have avoided an unfamiliar retailer because of scam concerns.
  • 42% have ignored a legitimate call, text or email because they feared a scam.
  • 41% have avoided trying a new app, website or service.
  • 39% have avoided clicking a legitimate message or link.
  • Investment and cryptocurrency scams were the leading text-scam category detected in Alabama.

McAfee detected 5.14 scam texts per device, the highest rate in the country.

Alaska

Key takeaway: Alaska has one of the widest gaps between rising trust fatigue and active checking: 54% report more mental effort, but only 44% verify online content at least weekly.

  • 54% say figuring out what’s real online takes more mental energy than a year ago.
  • 44% check online legitimacy at least weekly.
  • 13% say they check several times a day.
  • 44% have encountered an AI-generated image presented as real.
  • 82% are concerned AI is making scams harder to recognize.
  • 48% have avoided an unfamiliar retailer.
  • 39% have ignored a legitimate call, text or email.
  • 40% have avoided trying a new app, website or service.
  • 34% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams were the leading text-scam category detected in Alaska.

Arizona

Key takeaway: Arizonans are feeling a pronounced trust burden, with 65% saying it now takes more mental energy to decide what’s real online.

  • 65% report greater mental effort figuring out what’s real online.
  • 60% check online legitimacy at least weekly.
  • 17% check several times a day.
  • 41% have encountered an AI-generated image presented as real.
  • 81% are concerned AI is making scams harder to recognize.
  • 43% have avoided unfamiliar retailers.
  • 44% have ignored a legitimate call, text or email.
  • 31% have avoided trying a new app, website or service.
  • 39% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Arizona’s text-scam volume.

Arkansas

Key takeaway: Arkansas residents are relatively active verifiers: 64% check online legitimacy at least weekly even though only about half report greater mental strain.

  • 51% say figuring out what’s real online takes more mental energy.
  • 64% verify online content at least weekly.
  • 22% check several times a day.
  • 38% have encountered an AI-generated image presented as real.
  • 77% are concerned AI is making scams harder to recognize.
  • 46% have avoided unfamiliar retailers.
  • 42% have ignored a legitimate call, text or email.
  • 32% have avoided trying a new app, website or service.
  • 32% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Arkansas text-scam volume.

California

Key takeaway: California has one of the heaviest trust burdens in the survey: 72% say figuring out what’s real online now takes more mental energy.

  • 72% report greater mental effort deciding what’s real online.
  • 58% verify online content at least weekly.
  • 20% check several times a day.
  • 41% have encountered an AI-generated image presented as real.
  • 83% are concerned AI is making scams harder to recognize.
  • 49% have avoided unfamiliar retailers.
  • 43% have ignored a legitimate call, text or email.
  • 32% have avoided trying a new app, website or service.
  • 38% have avoided clicking a legitimate message or link.
  • Among Californians surveyed who lost money to scams, 72% recovered none of it.

Investment and cryptocurrency scams led California’s  text-scam volume. 

Colorado

Key takeaway: Colorado’s clearest signal is concern about AI-enabled scams, shared by 85% of residents surveyed.

  • 59% report greater mental effort figuring out what’s real online.
  • 56% verify online content at least weekly.
  • 15% check several times a day.
  • 38% have encountered an AI-generated image presented as real.
  • 85% are concerned AI is making scams harder to recognize.
  • 42% have avoided unfamiliar retailers.
  • 45% have ignored a legitimate call, text or email.
  • 35% have avoided trying a new app, website or service.
  • 34% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Colorado’s text-scam volume.

Connecticut

Key takeaway: Connecticut residents report rising trust fatigue, yet fewer than half say they verify online content every week.

  • 57% say figuring out what’s real takes more mental energy.
  • 47% verify online content at least weekly.
  • 18% check several times a day.
  • 35% have encountered an AI-generated image presented as real.
  • 79% are concerned AI is making scams harder to recognize.
  • 33% have avoided unfamiliar retailers.
  • 36% have ignored a legitimate call, text or email.
  • 26% have avoided a new app, website or service.
  • 24% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Connecticut’s text-scam volume.

Delaware

Key takeaway: Delaware stands out for exposure to synthetic imagery, with 46% encountering an AI-generated image presented as real.

  • 53% report greater mental effort figuring out what’s real online.
  • 53% verify online content at least weekly.
  • 8% check several times a day.
  • 46% have encountered an AI-generated image presented as real.
  • 80% are concerned AI is making scams harder to recognize.
  • 47% have avoided unfamiliar retailers.
  • 34% have ignored a legitimate call, text or email.
  • 30% have avoided a new app, website or service.
  • 33% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Delaware’s text-scam volume.

Florida

Key takeaway: Floridians are active online reality-checkers, with 63% verifying messages, offers, websites or people at least weekly.

  • 56% report greater mental effort figuring out what’s real online.
  • 63% verify online content at least weekly.
  • 18% check several times a day.
  • 43% have encountered an AI-generated image presented as real.
  • 85% are concerned AI is making scams harder to recognize.
  • 43% have avoided unfamiliar retailers.
  • 37% have ignored a legitimate call, text or email.
  • 42% have avoided a new app, website or service.
  • 27% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Florida text-scam volume.

From our McAfee Labs Research: This shows approximate location of all the scams received

Georgia

Key takeaway: Georgia had the second-highest scam-text-per-device rate highlighted by McAfee, at 4.67.

  • 59% report greater mental effort figuring out what’s real online.
  • 60% verify online content at least weekly.
  • 25% check several times a day.
  • 33% have encountered an AI-generated image presented as real.
  • 80% are concerned AI is making scams harder to recognize.
  • 40% have avoided unfamiliar retailers.
  • 37% have ignored a legitimate call, text or email.
  • 27% have avoided a new app, website or service.
  • 35% have avoided clicking a legitimate message or link.
  • McAfee detected an average of 4.67 scam texts per device.

Investment and cryptocurrency scams led Georgia’s text-scam volume. 

Hawaii

Key takeaway: Hawaii had the country’s highest scam intensity among affected devices: those receiving at least one scam text averaged 8.45 over three months.

  • 56% report greater mental effort figuring out what’s real online.
  • 54% verify online content at least weekly.
  • 13% check several times a day.
  • 38% have encountered an AI-generated image presented as real.
  • 81% are concerned AI is making scams harder to recognize.
  • 47% have avoided unfamiliar retailers.
  • 38% have ignored a legitimate call, text or email.
  • 37% have avoided a new app, website or service.
  • 37% have avoided clicking a legitimate message or link.
  • Affected devices averaged 8.45 scam texts, the highest figure nationally.

Investment and cryptocurrency scams led Hawaii’s text-scam volume. 

Idaho

Key takeaway: Idaho shows a sizeable trust gap: 62% report greater mental effort deciding what’s real, while 49% verify online content weekly.

  • 62% report more mental effort figuring out what’s real online.
  • 49% verify online content at least weekly.
  • 13% check several times a day.
  • 43% have encountered an AI-generated image presented as real.
  • 82% are concerned AI is making scams harder to recognize.
  • 48% have avoided unfamiliar retailers.
  • 35% have ignored a legitimate call, text or email.
  • 40% have avoided a new app, website or service.
  • 38% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Idaho’s text-scam volume.

Illinois

Key takeaway: Two-thirds of Illinois residents say deciding what’s real online is taking more mental energy than a year ago.

  • 66% report more mental effort figuring out what’s real online.
  • 59% verify online content at least weekly.
  • 18% check several times a day.
  • 39% have encountered an AI-generated image presented as real.
  • 75% are concerned AI is making scams harder to recognize.
  • 40% have avoided unfamiliar retailers.
  • 26% have ignored a legitimate call, text or email.
  • 32% have avoided a new app, website or service.
  • 24% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Illinois text-scam volume.

Indiana

Key takeaway: Indiana’s scam anxiety is translating into caution: 81% are concerned about AI making scams harder to recognize and 60% verify online content weekly.

  • 62% report more mental effort figuring out what’s real online.
  • 60% verify online content at least weekly.
  • 18% check several times a day.
  • 46% have encountered an AI-generated image presented as real.
  • 81% are concerned AI is making scams harder to recognize.
  • 38% have avoided unfamiliar retailers.
  • 41% have ignored a legitimate call, text or email.
  • 35% have avoided a new app, website or service.
  • 35% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Indiana text-scam volume.

Iowa

Key takeaway: Iowa residents report relatively restrained checking behavior: 47% verify online content at least weekly despite 55% reporting greater mental effort.

  • 55% report more mental effort figuring out what’s real online.
  • 47% verify online content at least weekly.
  • 17% check several times a day.
  • 33% have encountered an AI-generated image presented as real.
  • 81% are concerned AI is making scams harder to recognize.
  • 43% have avoided unfamiliar retailers.
  • 32% have ignored a legitimate call, text or email.
  • 33% have avoided a new app, website or service.
  • 34% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Iowa text-scam volume.

Kansas

Key takeaway: Kansas has one of the bleakest recovery pictures in the survey: 75% of scam victims who lost money recovered none of it.

  • 61% report more mental effort figuring out what’s real online.
  • 51% verify online content at least weekly.
  • 10% check several times a day.
  • 40% have encountered an AI-generated image presented as real.
  • 80% are concerned AI is making scams harder to recognize.
  • 42% have avoided unfamiliar retailers.
  • 39% have ignored a legitimate call, text or email.
  • 40% have avoided a new app, website or service.
  • 32% have avoided clicking a legitimate message or link.
  • 75% of victims who lost money said they recovered none of it.

Investment and cryptocurrency scams led Kansas text-scam volume.

Kentucky

Key takeaway: Kentucky is the standout verification state: 76% say they check whether online content is legitimate at least weekly.

  • 62% report more mental effort figuring out what’s real online.
  • 76% verify online content at least weekly.
  • 19% check several times a day.
  • 41% have encountered an AI-generated image presented as real.
  • 83% are concerned AI is making scams harder to recognize.
  • 46% have avoided unfamiliar retailers.
  • 30% have ignored a legitimate call, text or email.
  • 39% have avoided a new app, website or service.
  • 25% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Kentucky text-scam volume.

Louisiana

Key takeaway: Louisiana combines comparatively low trust fatigue with severe financial consequences: 73% of victims who lost money recovered none of it.

  • 45% report more mental effort figuring out what’s real online.
  • 54% verify online content at least weekly.
  • 13% check several times a day.
  • 35% have encountered an AI-generated image presented as real.
  • 75% are concerned AI is making scams harder to recognize.
  • 43% have avoided unfamiliar retailers.
  • 37% have ignored a legitimate call, text or email.
  • 32% have avoided a new app, website or service.
  • 30% have avoided clicking a legitimate message or link.
  • 73% of victims who lost money said they recovered none of it.

Investment and cryptocurrency scams led Louisiana text-scam volume.

Maine

Key takeaway: Maine is one of only two states where toll and traffic scams, rather than investment and crypto scams, ranked first in McAfee’s text telemetry.

  • 64% report more mental effort figuring out what’s real online.
  • 59% verify online content at least weekly.
  • 13% check several times a day.
  • 39% have encountered an AI-generated image presented as real.
  • 81% are concerned AI is making scams harder to recognize.
  • 46% have avoided unfamiliar retailers.
  • 34% have ignored a legitimate call, text or email.
  • 34% have avoided a new app, website or service.
  • 30% have avoided clicking a legitimate message or link.

Toll and traffic violation scams were Maine’s leading text-scam category.

Maryland

Key takeaway: Marylanders show particularly high concern about AI-enabled fraud, with 86% saying AI is making scams harder to recognize.

  • 65% report more mental effort figuring out what’s real online.
  • 60% verify online content at least weekly.
  • 25% check several times a day.
  • 45% have encountered an AI-generated image presented as real.
  • 86% are concerned AI is making scams harder to recognize.
  • 46% have avoided unfamiliar retailers.
  • 45% have ignored a legitimate call, text or email.
  • 37% have avoided a new app, website or service.
  • 44% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Maryland text-scam volume.

Infographic - How Scams Are Affecting Americans 2

Massachusetts

Key takeaway: Massachusetts has a striking trust gap: 65% report more mental effort deciding what’s real, but only 48% verify online content at least weekly.

  • 65% report more mental effort figuring out what’s real online.
  • 48% verify online content at least weekly.
  • 15% check several times a day.
  • 46% have encountered an AI-generated image presented as real.
  • 86% are concerned AI is making scams harder to recognize.
  • 47% have avoided unfamiliar retailers.
  • 35% have ignored a legitimate call, text or email.
  • 37% have avoided a new app, website or service.
  • 38% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Massachusetts text-scam volume.

Michigan

Key takeaway: Michigan joins Maine as the only state where toll and traffic scams outranked investment and cryptocurrency scams.

  • 71% report more mental effort figuring out what’s real online.
  • 52% verify online content at least weekly.
  • 21% check several times a day.
  • 43% have encountered an AI-generated image presented as real.
  • 71% are concerned AI is making scams harder to recognize.
  • 40% have avoided unfamiliar retailers.
  • 35% have ignored a legitimate call, text or email.
  • 34% have avoided a new app, website or service.
  • 32% have avoided clicking a legitimate message or link.

Toll and traffic violation scams were Michigan’s leading text-scam category.

Minnesota

Key takeaway: Minnesota records the highest AI-scam concern in the state crosstabs, at 91%.

  • 60% report more mental effort figuring out what’s real online.
  • 59% verify online content at least weekly.
  • 10% check several times a day.
  • 47% have encountered an AI-generated image presented as real.
  • 91% are concerned AI is making scams harder to recognize.
  • 44% have avoided unfamiliar retailers.
  • 44% have ignored a legitimate call, text or email.
  • 38% have avoided a new app, website or service.
  • 34% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Minnesota text-scam volume.

Mississippi

Key takeaway: Mississippi had one of the heaviest scam-text loads in McAfee’s analysis, averaging roughly 4.64 scam texts per device.

  • 55% report more mental effort figuring out what’s real online.
  • 54% verify online content at least weekly.
  • 17% check several times a day.
  • 32% have encountered an AI-generated image presented as real.
  • 82% are concerned AI is making scams harder to recognize.
  • 43% have avoided unfamiliar retailers.
  • 34% have ignored a legitimate call, text or email.
  • 34% have avoided a new app, website or service.
  • 35% have avoided clicking a legitimate message or link.
  • McAfee detected roughly 4.64 scam texts per device.

Investment and cryptocurrency scams led Mississippi text-scam volume.

Missouri

Key takeaway: Missouri residents show a confidence problem around AI scams: 13% said they were not at all confident spotting AI-created or AI-enhanced fraud.

  • 63% report more mental effort figuring out what’s real online.
  • 60% verify online content at least weekly.
  • 16% check several times a day.
  • 41% have encountered an AI-generated image presented as real.
  • 85% are concerned AI is making scams harder to recognize.
  • 43% have avoided unfamiliar retailers.
  • 40% have ignored a legitimate call, text or email.
  • 39% have avoided a new app, website or service.
  • 35% have avoided clicking a legitimate message or link.
  • 13% said they’re not at all confident they could spot a scam enhanced by AI

Investment and cryptocurrency scams led Missouri text-scam volume.

Montana

Key takeaway: Montana has the highest reported exposure to AI-generated images presented as real, at 51%.

  • 63% report more mental effort figuring out what’s real online.
  • 49% verify online content at least weekly.
  • 11% check several times a day.
  • 51% have encountered an AI-generated image presented as real.
  • 84% are concerned AI is making scams harder to recognize.
  • 47% have avoided unfamiliar retailers.
  • 44% have ignored a legitimate call, text or email.
  • 43% have avoided a new app, website or service.
  • 37% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Montana text-scam volume.

Nebraska

Key takeaway: Nebraska’s strongest signal is AI concern: 87% say AI is making online scams harder to recognize.

  • 56% report more mental effort figuring out what’s real online.
  • 50% verify online content at least weekly.
  • 8% check several times a day.
  • 43% have encountered an AI-generated image presented as real.
  • 87% are concerned AI is making scams harder to recognize.
  • 41% have avoided unfamiliar retailers.
  • 35% have ignored a legitimate call, text or email.
  • 40% have avoided a new app, website or service.
  • 29% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Nebraska text-scam volume.

Nevada

Key takeaway: Nevada has the broadest reported scam exposure in the survey, with 95% encountering at least one type of scam in the past year.

  • 60% report more mental effort figuring out what’s real online.
  • 66% verify online content at least weekly.
  • 18% check several times a day.
  • 43% have encountered an AI-generated image presented as real.
  • 82% are concerned AI is making scams harder to recognize.
  • 45% have avoided unfamiliar retailers.
  • 33% have ignored a legitimate call, text or email.
  • 32% have avoided a new app, website or service.
  • 33% have avoided clicking a legitimate message or link.
  • 95% encountered at least one type of scam in the past year.

Investment and cryptocurrency scams led Nevada text-scam volume.

New Hampshire

Key takeaway: New Hampshire shows another trust gap: 59% report more mental effort figuring out what’s real, while 46% verify online content weekly.

  • 59% report more mental effort figuring out what’s real online.
  • 46% verify online content at least weekly.
  • 10% check several times a day.
  • 48% have encountered an AI-generated image presented as real.
  • 85% are concerned AI is making scams harder to recognize.
  • 50% have avoided unfamiliar retailers.
  • 34% have ignored a legitimate call, text or email.
  • 37% have avoided a new app, website or service.
  • 33% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led New Hampshire text-scam volume.

New Jersey

Key takeaway: New Jersey residents report unusually frequent scam exposure, with 30% saying they encounter four or more scam attempts on a typical day.

  • 61% report more mental effort figuring out what’s real online.
  • 61% verify online content at least weekly.
  • 18% check several times a day.
  • 43% have encountered an AI-generated image presented as real.
  • 82% are concerned AI is making scams harder to recognize.
  • 49% have avoided unfamiliar retailers.
  • 34% have ignored a legitimate call, text or email.
  • 37% have avoided a new app, website or service.
  • 36% have avoided clicking a legitimate message or link.
  • 30% report encountering at least four scam attempts on a typical day.

Investment and cryptocurrency scams led New Jersey text-scam volume.

New Mexico

Key takeaway: New Mexico has one of the toughest scam-recovery pictures: 72% of victims who lost money recovered none of it.

  • 65% report more mental effort figuring out what’s real online.
  • 59% verify online content at least weekly.
  • 16% check several times a day.
  • 39% have encountered an AI-generated image presented as real.
  • 79% are concerned AI is making scams harder to recognize.
  • 42% have avoided unfamiliar retailers.
  • 48% have ignored a legitimate call, text or email.
  • 38% have avoided a new app, website or service.
  • 44% have avoided clicking a legitimate message or link.
  • 72% of victims who lost money said they recovered none of it.

Investment and cryptocurrency scams led New Mexico text-scam volume.

New York

Key takeaway: New York’s most striking behavioral signal is comparatively low retailer avoidance: 33% have stayed away from unfamiliar sellers because of scam concerns.

  • 59% report more mental effort figuring out what’s real online.
  • 58% verify online content at least weekly.
  • 19% check several times a day.
  • 41% have encountered an AI-generated image presented as real.
  • 78% are concerned AI is making scams harder to recognize.
  • 33% have avoided unfamiliar retailers.
  • 37% have ignored a legitimate call, text or email.
  • 27% have avoided a new app, website or service.
  • 27% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led New York text-scam volume.

Displays the number of scams seen per unique device

North Carolina

Key takeaway: North Carolina stands out on recovery: 42% of scam victims who lost money said they recovered all of it.

  • 53% report more mental effort figuring out what’s real online.
  • 65% verify online content at least weekly.
  • 17% check several times a day.
  • 33% have encountered an AI-generated image presented as real.
  • 69% are concerned AI is making scams harder to recognize.
  • 38% have avoided unfamiliar retailers.
  • 38% have ignored a legitimate call, text or email.
  • 29% have avoided a new app, website or service.
  • 29% have avoided clicking a legitimate message or link.
  • 42% of victims who lost money reported recovering all of it.

Investment and cryptocurrency scams led North Carolina text-scam volume.

North Dakota

Key takeaway: North Dakota had the country’s highest concentration of scams in analyzed text traffic, at 2.8%.

  • 61% report more mental effort figuring out what’s real online.
  • 55% verify online content at least weekly.
  • 13% check several times a day.
  • 46% have encountered an AI-generated image presented as real.
  • 83% are concerned AI is making scams harder to recognize.
  • 48% have avoided unfamiliar retailers.
  • 40% have ignored a legitimate call, text or email.
  • 40% have avoided a new app, website or service.
  • 37% have avoided clicking a legitimate message or link.
  • 2.8% of analyzed text traffic was classified as scams, the highest share nationally.

Investment and cryptocurrency scams led North Dakota text-scam volume.

Ohio

Key takeaway: Ohio stands out for financial harm: 41% of respondents say they lost money to an online scam in the past year.

  • 59% report more mental effort figuring out what’s real online.
  • 63% verify online content at least weekly.
  • 20% check several times a day.
  • 46% have encountered an AI-generated image presented as real.
  • 73% are concerned AI is making scams harder to recognize.
  • 44% have avoided unfamiliar retailers.
  • 33% have ignored a legitimate call, text or email.
  • 33% have avoided a new app, website or service.
  • 30% have avoided clicking a legitimate message or link.
  • 41% report losing money to an online scam in the past year.

Investment and cryptocurrency scams led Ohio text-scam volume.

Oklahoma

Key takeaway: Oklahoma consumers are feeling the mental load of navigating AI-powered scams: 85% are concerned AI is making scams harder to recognize, while half say figuring out what’s real online requires more mental effort.

  • 56% verify online content at least weekly.
  • 19% check several times a day.
  • 47% have encountered an AI-generated image presented as real.
  • 85% are concerned AI is making scams harder to recognize.
  • 50% have avoided unfamiliar retailers.
  • 46% have ignored a legitimate call, text or email.
  • 39% have avoided a new app, website or service.
  • 43% have avoided clicking a legitimate message or link.
  • 10% say they never spend time checking whether online content is legitimate.

Investment and cryptocurrency scams led Oklahoma text-scam volume.

Oregon

Key takeaway: Oregon scam concerns are spilling into ordinary digital life, with 45% avoiding new apps, websites or services.

  • 57% report more mental effort figuring out what’s real online.
  • 49% verify online content at least weekly.
  • 17% check several times a day.
  • 41% have encountered an AI-generated image presented as real.
  • 85% are concerned AI is making scams harder to recognize.
  • 52% have avoided unfamiliar retailers.
  • 45% have ignored a legitimate call, text or email.
  • 45% have avoided a new app, website or service.
  • 39% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Oregon text-scam volume.

Pennsylvania

Key takeaway: Pennsylvania has one of the heavier trust burdens in the survey, with 67% saying figuring out what’s real takes more mental energy.

  • 67% report more mental effort figuring out what’s real online.
  • 54% verify online content at least weekly.
  • 14% check several times a day.
  • 39% have encountered an AI-generated image presented as real.
  • 85% are concerned AI is making scams harder to recognize.
  • 48% have avoided unfamiliar retailers.
  • 38% have ignored a legitimate call, text or email.
  • 37% have avoided a new app, website or service.
  • 31% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Pennsylvania text-scam volume.

Rhode Island

Key takeaway: Rhode Island scam concerns are affecting legitimate online behavior: 42% have avoided clicking a real message or link.

  • 58% report more mental effort figuring out what’s real online.
  • 57% verify online content at least weekly.
  • 11% check several times a day.
  • 45% have encountered an AI-generated image presented as real.
  • 84% are concerned AI is making scams harder to recognize.
  • 40% have avoided unfamiliar retailers.
  • 37% have ignored a legitimate call, text or email.
  • 36% have avoided a new app, website or service.
  • 42% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Rhode Island text-scam volume.

South Carolina

Key takeaway: South Carolina has a confidence problem around AI scams: 13% say they are not at all confident identifying AI-created or AI-enhanced fraud.

  • 57% report more mental effort figuring out what’s real online.
  • 47% verify online content at least weekly.
  • 12% check several times a day.
  • 44% have encountered an AI-generated image presented as real.
  • 79% are concerned AI is making scams harder to recognize.
  • 43% have avoided unfamiliar retailers.
  • 42% have ignored a legitimate call, text or email.
  • 38% have avoided a new app, website or service.
  • 39% have avoided clicking a legitimate message or link.
  • 13% say they are not at all confident identifying AI-created or AI-enhanced fraud.

Investment and cryptocurrency scams led South Carolina text-scam volume.

South Dakota

Key takeaway: South Dakota’s scam response is relatively restrained compared with many states, with 35% avoiding unfamiliar retailers and 29% avoiding legitimate links.

  • 55% report more mental effort figuring out what’s real online.
  • 52% verify online content at least weekly.
  • 11% check several times a day.
  • 41% have encountered an AI-generated image presented as real.
  • 78% are concerned AI is making scams harder to recognize.
  • 35% have avoided unfamiliar retailers.
  • 37% have ignored a legitimate call, text or email.
  • 38% have avoided a new app, website or service.
  • 29% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led South Dakota text-scam volume.

Tennessee

Key takeaway: Tennessee residents report rising trust fatigue without matching verification habits: 59% feel more mental strain, but 48% verify weekly.

  • 59% report more mental effort figuring out what’s real online.
  • 48% verify online content at least weekly.
  • 15% check several times a day.
  • 40% have encountered an AI-generated image presented as real.
  • 80% are concerned AI is making scams harder to recognize.
  • 48% have avoided unfamiliar retailers.
  • 33% have ignored a legitimate call, text or email.
  • 35% have avoided a new app, website or service.
  • 37% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Tennessee text-scam volume.

Texas

Key takeaway: Texas is one of the more active verification states, with 62% checking online legitimacy at least weekly.

  • 61% report more mental effort figuring out what’s real online.
  • 62% verify online content at least weekly.
  • 22% check several times a day.
  • 46% have encountered an AI-generated image presented as real.
  • 81% are concerned AI is making scams harder to recognize.
  • 41% have avoided unfamiliar retailers.
  • 30% have ignored a legitimate call, text or email.
  • 32% have avoided a new app, website or service.
  • 30% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Texas text-scam volume.

Infographic describing state-by-state threat data

Utah

Key takeaway: Utah has one of the highest levels of exposure to AI-generated imagery, with 49% seeing an AI image presented as real.

  • 58% report more mental effort figuring out what’s real online.
  • 50% verify online content at least weekly.
  • 8% check several times a day.
  • 49% have encountered an AI-generated image presented as real.
  • 85% are concerned AI is making scams harder to recognize.
  • 43% have avoided unfamiliar retailers.
  • 40% have ignored a legitimate call, text or email.
  • 43% have avoided a new app, website or service.
  • 32% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Utah text-scam volume.

Vermont

Key takeaway: Vermont has a sizeable trust-versus-action gap: 58% report more mental effort online while 47% verify content weekly.

  • 58% report more mental effort figuring out what’s real online.
  • 47% verify online content at least weekly.
  • 12% check several times a day.
  • 45% have encountered an AI-generated image presented as real.
  • 79% are concerned AI is making scams harder to recognize.
  • 47% have avoided unfamiliar retailers.
  • 28% have ignored a legitimate call, text or email.
  • 32% have avoided a new app, website or service.
  • 30% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Vermont text-scam volume.

Virginia

Key takeaway: Virginia reports comparatively low exposure to AI-generated images presented as real, at 34%, even as concern about AI scams remains high.

  • 58% report more mental effort figuring out what’s real online.
  • 54% verify online content at least weekly.
  • 15% check several times a day.
  • 34% have encountered an AI-generated image presented as real.
  • 83% are concerned AI is making scams harder to recognize.
  • 40% have avoided unfamiliar retailers.
  • 33% have ignored a legitimate call, text or email.
  • 39% have avoided a new app, website or service.
  • 30% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Virginia text-scam volume.

Washington

Key takeaway: Washington has one of the highest levels of AI-scam concern in the survey, at 86%.

  • 62% report more mental effort figuring out what’s real online.
  • 55% verify online content at least weekly.
  • 15% check several times a day.
  • 40% have encountered an AI-generated image presented as real.
  • 86% are concerned AI is making scams harder to recognize.
  • 50% have avoided unfamiliar retailers.
  • 36% have ignored a legitimate call, text or email.
  • 34% have avoided a new app, website or service.
  • 36% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Washington text-scam volume.

West Virginia

Key takeaway: West Virginia has one of the lower weekly verification rates in the survey, at 45%, despite a majority reporting greater trust fatigue.

  • 55% report more mental effort figuring out what’s real online.
  • 45% verify online content at least weekly.
  • 12% check several times a day.
  • 43% have encountered an AI-generated image presented as real.
  • 81% are concerned AI is making scams harder to recognize.
  • 41% have avoided unfamiliar retailers.
  • 25% have ignored a legitimate call, text or email.
  • 29% have avoided a new app, website or service.
  • 31% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led West Virginia text-scam volume.

Wisconsin

Key takeaway: Wisconsin shows relatively high exposure to synthetic imagery: 46% have encountered an AI-generated image presented as real.

  • 56% report more mental effort figuring out what’s real online.
  • 49% verify online content at least weekly.
  • 15% check several times a day.
  • 46% have encountered an AI-generated image presented as real.
  • 85% are concerned AI is making scams harder to recognize.
  • 39% have avoided unfamiliar retailers.
  • 35% have ignored a legitimate call, text or email.
  • 26% have avoided a new app, website or service.
  • 26% have avoided clicking a legitimate message or link.

Investment and cryptocurrency scams led Wisconsin text-scam volume.

Wyoming

Key takeaway: Wyoming has the most distressing scam-loss recovery story in the survey: 76% of victims who lost money recovered none of it.

  • 64% report more mental effort figuring out what’s real online.
  • 52% verify online content at least weekly.
  • 11% check several times a day.
  • 49% have encountered an AI-generated image presented as real.
  • 78% are concerned AI is making scams harder to recognize.
  • 44% have avoided unfamiliar retailers.
  • 41% have ignored a legitimate call, text or email.
  • 43% have avoided a new app, website or service.
  • 31% have avoided clicking a legitimate message or link.
  • 76% of victims who lost money said they recovered none of it.

Investment and cryptocurrency scams led Wyoming text-scam volume.

The post What Scams Look Like in Your State: A 50-State Breakdown appeared first on McAfee Blog.
  •  

Your State’s Scam Reality: What New Research Reveals Across All 50 States

There is a small tax many of us pay in our everyday interactions without even realizing it.

A package notification arrives, and we stop to check whether we actually ordered something. A recruiter reaches out about a job, but before replying, we research the person and the company. A bank alert appears, and instead of tapping the link, we open the banking app ourselves.

These are sensible habits. But McAfee’s latest research suggests the effort behind them is increasing the average American’s every day mental load.

Nearly three-quarters of Americans (74%) say they feel the need to double-check most things online before trusting them. Sixty-two percent say figuring out what is real takes more mental energy than it did a year ago.

That growing burden is one reason McAfee is introducing a new brand and product experience built around a broader idea of what protection should do. Good security shouldn’t demand more of people’s attention. It should help give some of it back.

That’s why the new McAfee experience is designed to do more than protect individual devices. It helps protect the things people rely on every day, their personal information, connections, devices, and accounts, all while making it clearer what’s safe, what needs attention, and what McAfee can handle for them.

New McAfee Experience - iPhone Mockup

Get quick alerts and easily update protections in McAfee’s app

That matters at a moment when attention is already stretched thin. AI is everywhere, and it has made it easier to produce convincing content at an enormous scale, adding to an already crowded attention economy. Increasingly, ordinary moments come with an extra question: Is this real?

And those questions have consequences. Our research found that 82% of Americans have changed how they behave online because of scams. Some have stopped buying from unfamiliar retailers. Others have ignored communications that turned out to be legitimate. Eighteen percent say scam concerns have even caused them to avoid responding to a job opportunity.

“I’ve accused my doctor’s office of being an AI,” says McAfee Threat Researcher Charles McFarland, recounting a time when even he thought something legitimate was fraudulent. “I had to apologize.”

Financial losses remain a serious part of the picture. Nearly one-third of Americans (31%) reported losing money to a scam in the past year. But measuring scams only in dollars misses something important. Scams are also making trust more expensive.

This report examines that growing cost: the attention Americans are spending figuring out what to trust, how the scam experience differs across all 50 states, and what protection should look like when staying safe increasingly competes for the same limited time and attention as everything else we do online.

Infographic - USA Map Dominant Scam Category by State

Key Findings

McAfee’s research combines a nationally representative survey of 5,000 U.S. adults, with 100 respondents in every state, and McAfee Labs analysis of text-based scam activity across the U.S.

Together, the findings show how scams are affecting not only Americans’ wallets, but also their attention, trust and behavior online.

Scams are placing a growing burden on Americans’ attention. Nearly three-quarters (74%) say they feel the need to double-check most things online before trusting them, while 62% say figuring out what is real takes more mental energy than it did a year ago. (Survey)

That uncertainty is changing legitimate online behavior. Eighty-two percent say scam concerns have changed something they do online. Forty-four percent have avoided buying from an unfamiliar retailer, 37% have ignored a legitimate call, text or email, 34% have avoided a new app, website or service, 33% have avoided a legitimate link and 25% have abandoned an online purchase. (Survey)

Scams can make real opportunities harder to trust. Twenty-seven percent encountered a fake recruiter or job opportunity in the past year. At the same time, 18% say scam concerns have caused them to avoid responding to a job opportunity. (Survey)

Financial losses are widespread, and getting money back can be difficult. Nearly one-third of Americans (31%) report losing money to a scam in the past year. Among those who lost money, 53% recovered none. In Wyoming, Kansas, Louisiana, California and New Mexico, more than 70% of victims who lost money recovered nothing. (Survey)

Investment and cryptocurrency scams dominate text-based scam activity. McAfee Labs found them to be the leading scam-text category by volume in 47 of 50 states from May through July 2026. Maine, North Dakota and Michigan were the exceptions. In Maine and North Dakota, toll and traffic scams ranked first. Meanwhile, in North Dakota, loan and investment scams ranked first. (McAfee Labs)

The volume and intensity of scam texts varies considerably by state. Alabama averaged 5.14 scam texts per device, the highest in McAfee’s analysis. In North Dakota, scams represented 2.8% of analyzed text traffic, the highest concentration nationally. In Hawaii, devices receiving at least one scam text averaged 8.45 scam messages during the three-month analysis period. (McAfee Labs)

Some states experience especially high exposure or financial consequences. Ninety-five percent of Nevada respondents encountered at least one type of scam in the past year. In Ohio, 41% reported losing money to a scam. Thirty percent of New Jersey respondents say they encounter four or more scam attempts on a typical day. North Carolina stood out in the other direction: 42% of victims who lost money said they recovered all of it. (Survey)

Many scam texts are designed to begin a conversation rather than complete the scam immediately. Joining or clicking through to a WhatsApp group was the most common requested action in the scam texts McAfee analyzed, driven largely by investment and cryptocurrency schemes. The initial message may be only the first step in a longer attempt to build trust before asking for money. (McAfee Labs)

Displays the number of scams seen per unique device

Displays the number of scams seen per unique device

The New Scam Landscape

Scams no longer occupy some separate, obviously suspicious corner of the internet. Increasingly, they imitate the ordinary business of being online.

In its analysis of U.S. text-based scams from May through July 2026, McAfee Labs identified 49 leading scam topics across 23 broader categories. They touched nearly every part of daily life: package deliveries and bank accounts, job offers and investments, shopping and subscriptions, health and utilities, relationships and family emergencies.

Example of one of the many types of delivery text scams consumers face Example of one of the many types of delivery text scams consumers face

The full list spans Cloud Storage & Payment; Package & Delivery; Banking & Financial; Toll & Traffic Violation; Tax & IRS; Legal Threat & Law Enforcement; Government Impersonation; Tech Support & Security; Prize & Lottery; Romance & Relationship; Employment & Job Offer; Subscription & Service; Account Verification & Account Alerts; Investment & Cryptocurrency; Charity & Donation; Utility & Bill Payment; Health & Pharmacy; Family & Friend Emergency; Retail & Shopping; Loan & Debt Relief; Buying Property & Real Estate; Context-Free Links & Phone Numbers; and Other.

That breadth matters. The more scams resemble the normal messages people receive every day, the more ordinary life requires verification.

One category nevertheless dominated. Investment and cryptocurrency scams were the largest text-scam category by volume in 47 of 50 states. Only Maine, North Dakota and Michigan broke the pattern, with toll and traffic violation scams as well as loan and investments ranking first.

The prevalence of investment scams is important because many are not trying to steal money with a single text. They are trying to start a relationship.

The most common action requested in the scam texts analyzed by McAfee was clicking or joining a WhatsApp group, driven heavily by investment and cryptocurrency schemes. A message might promote an investing community or offer access to financial advice.

Example of a scam text attempting to move users to WhatsApp Example of a scam text attempting to move users to WhatsApp

Moving the recipient into a group or private conversation gives the scammer more time to establish credibility before money enters the picture. Plus, for many of us, social apps feel more personal and we more easily let our guard down when we move a conversation to these messaging platforms.

That helps explain why an unsolicited text that looks relatively harmless can still be the beginning of a much longer scam.

Other prominent scams rely on a different tactic: urgency. Fake account alerts can suggest that something needs immediate attention. Toll and traffic scams warn of an unpaid charge or violation. McAfee Labs also saw scammers impersonating T-Mobile with fake reward offers among the largest individual scam topics.

Example of a scam text attempting to move users to WhatsApp Example of scammers exploiting trusted brands like T-Mobile to dupe customers

The stories change, but the underlying objective is often the same. Scammers want people to act before they have time to question what they are seeing. And there is a lot to question.

Across the United States

McAfee’s analysis found meaningful differences in the amount of scam traffic reaching consumers around the country during the three month analysis period. Alabama recorded an average of 5.14 scam texts per device, the highest in the analysis. Georgia followed at 4.67, with Mississippi close behind at 4.64.

North Dakota stood out in a different way. There, scams represented 2.8% of all text traffic McAfee analyzed, the highest concentration in the country. Hawaii showed another pattern: among devices that received at least one scam text, the average was 8.45 scam messages during the three-month period. That was about 15% higher than Alabama, which ranked second at 7.35 scam texts per exposed device.

Rank  State  Scams per device  State  Scams per device scammed 
1  Alabama  5.14  Hawaii  8.45 
2  Georgia  4.67  Alabama  7.35 
3  Mississippi  4.64  Ohio  7.29 
4  Nevada  4.54  Florida  7.29 
5  Tennessee  4.50  North Dakota  7.28 

A third measure shows how concentrated scam traffic was within people’s overall text messages. North Dakota had the highest concentration in the country, with scams accounting for 2.8% of all text traffic McAfee analyzed.

These measures capture different dimensions of the same problem. The all-device average shows how many scam texts reached devices across a state overall. The exposed-device average shows how persistent scam activity was for devices that received at least one scam. And the share of total text traffic shows how prominent scam messages were within the broader messaging environment.

This shows each states top scam category by volume if Investments & Cryptocurrency scams are ignored. Notice these colors don’t necessarily match the colors from the previous graph.

This shows each states top scam category by volume if Investments & Cryptocurrency scams are ignored. Notice these colors don’t necessarily match the colors from the previous graph.

For consumers, those distinctions may be invisible. What they experience is repetition: another message asking for attention and another decision about whether it deserves it.

AI raises the stakes further. It can make convincing scam content cheaper and faster to produce, while people are simultaneously encountering more AI-generated material in everyday online life. The result is an environment where the old advice to simply “look for something suspicious” becomes harder to apply reliably. Sometimes the suspicious thing looks perfectly ordinary.

That is why the next phase of consumer protection cannot depend on people becoming infinitely better at scrutinizing everything themselves.

America’s Scam Reality

McAfee’s consumer research shows what happens when that scam environment meets everyday life.

Most Americans are encountering scams regularly. Eighty-eight percent say they experienced at least one type of scam in the past year, and one in five say they typically encounter four or more scam attempts in a single day.

Yet frequency tells only part of the story. The more consequential finding may be what people are doing in response.

Eighty-two percent say scam concerns have changed their online behavior. Forty-four percent have avoided an unfamiliar retailer. Thirty-seven percent have ignored a legitimate call, text or email because they suspected a scam. Thirty-three percent have avoided clicking a legitimate message or link.

These are not examples of people falling for scams. They are examples of people trying not to.

Job scams make that tradeoff particularly tangible. Twenty-seven percent of Americans say they encountered a fake recruiter or job opportunity in the past year. Eighteen percent say concerns about scams have caused them to avoid responding to a job opportunity.

The financial consequences remain substantial when a scam does succeed. Nearly one-third of Americans (31%) report losing money to a scam in the past year. Among those victims, 53% recovered none of what they lost.

From our McAfee Labs Research: This shows approximate location of all the scams received

From our McAfee Labs Research: This shows approximate location of all the scams received

But a national average can obscure how differently people experience the problem.

Our full 50-state scam breakdown examines the data state by state, combining McAfee’s consumer survey with Labs telemetry to show where scam exposure is highest, where financial recovery is hardest, how concerns affect behavior, and which types of text scams McAfee is seeing across the country.

Across those differences, one finding remains remarkably consistent: Americans are adapting. They are checking more carefully and approaching unfamiliar interactions with greater caution, or even avoiding them altogether.

Those behaviors can help keep people safe. But that puts the mental load on back onto the everyday user. There is a limit to how much vigilance we should expect people to supply on their own.

The better question is how technology can take on more of that work for them. And that is the thinking behind McAfee’s new brand and product experience, beginning its rollout in the U.S. today.

How McAfee is Changing to Meet the Moment

McAfee’s new consumer experience is designed to make protection simpler to understand and easier to act on, while helping people navigate the moments where scams and other threats increasingly create uncertainty.

We’ll let you know if something seems suspicious and could put you at risk.

The experience is built to spot risks earlier, guide people clearly, and act when protection can be handled automatically. That means flagging suspicious messages, links, sites, exposed data, or unsafe connections; explaining what matters in plain language; and helping people take the right next step without requiring them to become security experts.

McAfee can alert you when your information appears in a data breach, help identify suspicious messages and links, protect your connection on risky Wi-Fi, monitor for exposed personal information, and help keep your devices and accounts safer.

Just as importantly, we’ve worked to make those protections understandable.

Instead of expecting people to know cybersecurity terminology or hunt through settings, the experience is designed to surface what matters and help people understand what to do next.

Because good protection shouldn’t create another job for you.

The refreshed McAfee experience makes it easier to see what needs your attention and how you’re protected.

The refreshed McAfee experience makes it easier to see what needs your attention and how you’re protected.

What We’re Unveiling

That idea, making protection do more of the work, is built into the new McAfee experience we’re unveiling today.

We’ve brought protection for personal information, connections, and devices into one connected experience across PC, Mac, mobile, and tablet. Instead of asking people to piece together what’s protected or search for what needs attention, McAfee makes it easier to see both in one place.

The experience is also more personal. McAfee can alert you when your information or devices may be at risk and provide guided actions, that explain what needs your attention in plain language. The goal is not to give people more security information. It’s to help them understand what matters to them and what they can do about it.

And over time, the experience is designed to become more personal and relevant to each person, proactively identifying risks, alerting in the moment, and guiding when action is needed for the protections that matter most based on their digital life.

We’ve also made improvements to privacy tools like Online Account Cleanup, which now helps people prioritize higher-risk accounts, and Personal Data Cleanup, which makes it easier to see the personal information being found and removed on their behalf.

Taken together, these changes reflect where we believe consumer safety needs to go: less hunting through settings, less deciphering security alerts, and less relying on people to spot every threat themselves.

More protection that understands what matters, explains what needs attention, and works proactively in the background.

Here to give you peace of mind and lighten the mental load of life online.

Here to give you peace of mind and lighten the mental load of life online.

Conclusion

The findings in this report suggest that the impact of scams extends beyond exposure and financial loss.

Every scam adds another small decision to an already crowded digital day: Is this message real? Is this link safe? Is this person who they say they are? As those decisions multiply, staying safe online becomes not just a security challenge, but a growing mental burden.

As people encounter more attempts to imitate legitimate messages, businesses and opportunities, the effort required to establish trust becomes a consequence in its own right.

That makes reducing the burden of verification an increasingly important part of consumer protection. People should not have to devote more of their limited attention to staying safe simply because scams are becoming harder to distinguish from everyday life online. That’s where McAfee comes in.

The post Your State’s Scam Reality: What New Research Reveals Across All 50 States appeared first on McAfee Blog.
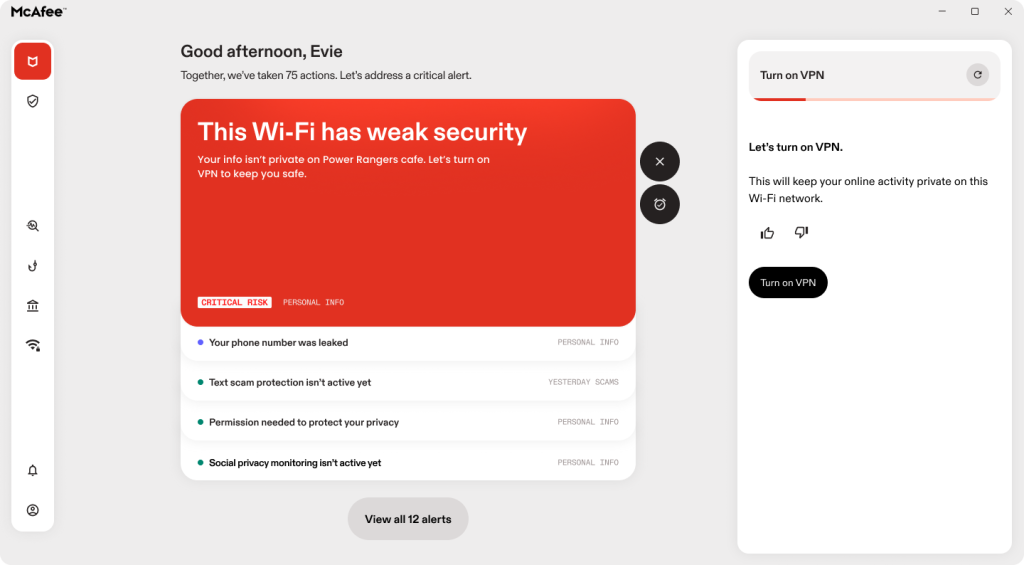
  •  

Card Skimmers Expose 600k Cards: What They Are and How to Protect Yourself

Cybercriminals are deploying autonomous AI agent frameworks to target online retailers and steal payment card details at scale, according to research from cybersecurity firm Gambit Security. Their analysis reveals that the ongoing campaign has compromised at least 119 websites—including a Fortune 500 hospitality company, a major U.S. airline, and an online fashion retailer—exfiltrating over 600,000 valid credit card records. These automated systems allow threat actors to scan, exploit, and infect target sites at a remarkably low operational cost, lowering the technical and financial barriers to large-scale cybercrime.

How the AI Credit Card Skimming Attack Works

In simple terms, a digital credit card skimmer acts like a hidden recording device inside an online checkout counter. Instead of physically tampering with a card reader, scammers use automated software tools to breach an e-commerce website’s backend servers.

Once inside, the software places invisible lines of malicious code directly on the payment page. When you enter your credit card number, expiration date, and security code to make a purchase, the hidden code silently copies your financial information and sends it to the attacker. Your order processes normally without any visible interruption.

Behind this campaign, threat actors use three specialized open-source AI frameworks to manage the intrusion without needing constant human oversight:

  • Strix: Automatically scans websites to search for unpatched security vulnerabilities or unprotected doors into backend servers. Across an eight-day window, Strix logged 633 scanning hours across 138 website hosts.
  • Cairn: Takes the security flaws discovered by Strix and uses them automatically to break through website defenses, giving the scammer administrative access.
  • Hermes: Serves as an orchestration agent for the operation. Powered by advanced AI (Claude Opus 4.6), it makes real-time tactical decisions, directs the attack steps, installs the skimmers, and manages 121 operational skills.

The Low Cost and High Impact of AI-Driven Attacks

According to data published by Gambit Security, the attacker ran 105 distinct attack waves in a five-day span using brief instructions like “get to work.” The total infrastructure cost ranged between $12,000 and $18,000, averaging just $25.46 per targeted company. By driving the average cost down to tens of dollars per target, AI automation slashes the financial and technical barriers to cybercrime. Threat actors can now execute high-volume enterprise breaches at scale that previously required costly manual operations and dedicated technical teams.

Once inside, the AI agents inject malicious JavaScript skimmers into checkout forms, Google tag blocks, content delivery networks (CDNs), or server caches. The Hermes agent was also instructed to execute cleanup routines that wiped stolen payment fields directly from merchant databases, causing server errors and data loss for affected retailers. While this particular campaign compromised e-commerce websites, automated scripts can also target payment data directly on client devices, such as the browser-level threats highlighted in McAfee Labs research on wallet-swapping extension malware.

Warning Signs and Red Flags

Digital skimmers operate quietly within legitimate checkout pages, but technical anomalies can indicate a compromised payment form:

  • Checkout latency or page crashes: The payment form freezes, stutters, or throws an error message while processing your transaction.
  • Repeated payment prompts: The website requests that you re-enter your payment card details immediately after you submit them.
  • Visual formatting errors: Payment entry fields display misaligned input boxes, mismatched fonts, or unexpected design changes compared to the rest of the site.
  • Immediate transaction notifications: Your bank flags an unfamiliar charge or location seconds after you complete a purchase.

How to Protect Yourself From Digital Credit Card Skimmers

  • Pay with third-party digital wallets. Complete purchases using Apple Pay, Google Pay, or PayPal. These payment services use encrypted tokenization, ensuring your actual credit card number is never transmitted to or stored on the merchant’s payment form.
  • Use virtual credit cards. Generate temporary, single-use, or merchant-locked virtual card numbers through your bank or card issuer to prevent stolen card details from being reused elsewhere.
  • Avoid saving payment information in merchant accounts. Input payment details manually for individual transactions rather than storing card numbers inside store customer profiles or retailer databases.
  • Enable real-time transaction alerts. Turn on immediate push notifications or SMS alerts in your banking app for every account charge so you can identify unauthorized activity immediately.

What to Do If You’ve Already Been Targeted

If you suspect your credit card information was stolen or compromised in a digital skimming attack:

  • Contact your bank or card issuer immediately. Report the compromised card, request an immediate cancellation, and dispute any unauthorized charges.
  • Update your account credentials. Change passwords and turn on multi-factor authentication (MFA) across all financial accounts and shopping portals where you used the same login information.
  • Place a credit freeze. Contact Equifax, Experian, and TransUnion to freeze your credit files, preventing unauthorized accounts from being opened in your name.
  • Maintain transaction records. Retain bank statements, order confirmation emails, receipts, and the web URL of the merchant site where the purchase occurred.
  • Create an official recovery plan. If personal identifying information (such as your Social Security number or date of birth) was exposed alongside financial details, submit a report to the FTC to get a recovery plan.

Reporting Credit Card Skimming and Staying Safe

Reporting stolen payment data helps law enforcement track malicious server infrastructure and disrupt automated threat networks. If you suspect your financial data was exposed on a compromised site, report the incident through official channels:

  • FBI Internet Crime Complaint Center: Submit a formal incident report with ic3.
  • Federal Trade Commission: Report payment fraud and scam activity to the FTC.
  • Local Police Department: File a police report if required by your bank or insurance provider for fraud reimbursement claims.
  • The Affected Merchant: Contact the retailer’s customer support or security team directly through their official domain.

While AI skimming attacks can be difficult to detect on the front end of retail websites, taking immediate action after a suspected exposure limits potential financial damage. By utilizing encrypted digital wallets, avoiding stored payment methods, and reviewing account statements regularly, you significantly reduce your exposure to AI-driven cybercrime.

The post Card Skimmers Expose 600k Cards: What They Are and How to Protect Yourself appeared first on McAfee Blog.
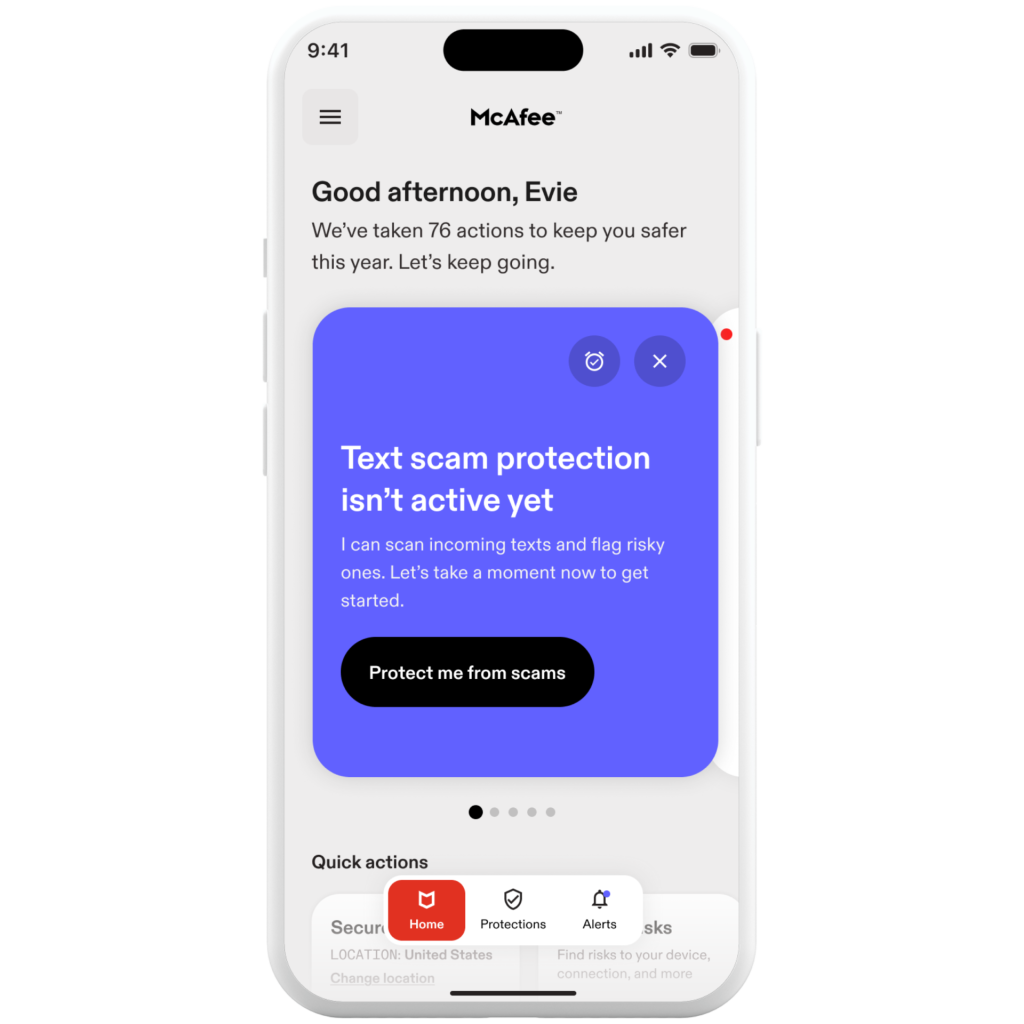
  •  

FBI Job Portal Hack Claimed by ShinyHunters: What Happened and How to Protect Yourself

An agent walks by the FBI seal at headquarters.

The FBI is investigating a major data breach after learning the federal agency’s job application portal was compromised, according to a September 2026 report by 404 Media. The cyberattack on FBIJobs.gov may have exposed the personal records of thousands of job applicants alongside current and former FBI personnel.

On September 23, the FBI shared in a statement that they were “aggressively investigating this matter,” and on September 29, shared a video on X reporting that Dutch authorities had arrested an alleged leader of ShinyHunters, the global cybercrime group known who took responsibility for the FBI data breach. In the video, Brett Leatherman, Assistant Director of the FBI’s Cyber Division, warned remaining members of ShinyHunters that the FBI knew where to find them and suggested they reach out to the FBI first while they still have the choice.

Inside the FBI Jobs Portal Cyberattack

The intrusion targeted the FBI Candidate Gateway, where the hacker group claims to have extracted sensitive personally identifiable information (PII). According to the group and media reviews of leaked sample data, this compromised dataset contains the PII of federal job applicants, prospective candidates, active special agents, and former FBI employees. Exposed records allegedly include full legal names, home addresses, phone numbers, email addresses, spousal information, job titles, and Social Security numbers.

In a statement circulated on the dark-web by ShinyHunters, the group attempted to use the stolen database to extort the agency, giving officials one week to retract a public advisory that had identified ShinyHunters as a criminal syndicate. After the deadline passed and the advisory remained live, the group claimed they would not publish the database publicly. However, breached records frequently wind up circulating in cybercriminal forums.

How Breach Data Creates Additional Threats

When news breaks that sensitive personnel data from a high-profile agency has been exposed, the risks extend beyond immediate identity theft. Cybercriminals can leverage this stolen data to launch two categories of attacks:

  • Internal Spear-Phishing and System Infiltration: Hackers could use stolen internal personnel registries, agent titles, and applicant profiles to target current FBI staff. By citing real colleague names, internal job postings, or specific department codes, bad actors can craft hyper-targeted phishing emails to trick employees into surrendering internal network credentials. The goal of this attack would be to gain access to restricted databases, confidential files, and sensitive intelligence networks.
  • External Impersonation and Consumer Fraud: Scammers could also exploit stolen agent credentials to trick the general public. By matching leaked names with real public offices, fraudsters could contact civilians claiming to be active federal agents conducting official investigations, pressuring targets into paying fake fines or forfeiting financial credentials.

Watch for Warning Signs of FBI Impersonation Scams

Because this breach may have exposed real personnel details, impersonation attempts carry heightened risk. Scammers could pair verified agent names, genuine department titles, and realistic internal background details with fake caller ID tags, making fraudulent outreach appear legitimate. Be extra vigilant for these red flags that you may be dealing with an impersonation scam:

  • Demands for immediate payment. Federal agencies will never call to demand immediate payment, and do not accept payment via gift cards, cryptocurrency, wire transfers, or cash couriers.
  • Threats of arrest or legal action. Impersonators use high-pressure tactics, claiming you face active arrest warrants or federal lawsuits if you do not pay or comply on the spot.
  • Pressure to remain on the line. Scammers try to prevent you from independently verifying their identity. Legitimate law enforcement officers will allow you to hang up and call official public agency numbers.
  • Spoofed caller ID and credentials. Scammers manipulate caller ID displays to mirror official FBI field office phone numbers or send emails containing legitimate bureau logos.

How to Protect Yourself from Impersonation Scams

Protect against impersonation schemes by verifying all unexpected contacts independently.

  • Hang up and verify directly. If you receive a call claiming to be from the FBI or another federal agency, hang up immediately. Search for the official phone number of your local FBI field office on fbi.gov and call them directly to confirm if the inquiry is legitimate.
  • Do not trust caller ID. Phone numbers displayed on caller ID can be spoofed to match real government offices.
  • Avoid clicking links in unsolicited messages. If you receive an email or text message regarding an FBI application or investigation, do not click embedded links. Type the official URL ending in .gov directly into your browser.

What to Do If Your PII Was Compromised or You’ve Been Targeted by Scammers

If you shared personal details or sent funds to a scammer, or if you previously submitted job applications or personal information through federal career sites, take immediate action to secure your identity and accounts:

  • Stop contact with scammers and cease payments. Block all phone numbers, email addresses, and messaging channels used by the scammer immediately. Do not transfer additional money.
  • Notify your financial institutions. If you’ve initiated payment with a suspected scammer or notice charges that you did not approve, contact your bank, credit card issuer, or payment app provider right away to report fraudulent transactions and request charge reversals or account holds.
  • Update passwords and activate multi-factor authentication (MFA). Change login passwords across all online accounts, starting with primary email and financial logins, and enable MFA using an authenticator app.
  • Freeze your credit. Contact Equifax, Experian, and TransUnion to freeze your credit files, preventing attackers from opening loans or credit lines in your name.
  • File an identity theft report. If your Social Security number or identity details were exposed, visit IdentityTheft.gov to submit a report and receive a personalized recovery plan.
  • Preserve evidence. Save phone logs, text messages, emails, wire receipts, and digital wallet addresses associated with the scam.

Report Cybercrime to Help Make a Safer Internet

Reporting cybercrime and impersonation attempts helps law enforcement trace criminal networks like the ShinyHunters hacker group and shut down active fraud operations. Submit reports through these official channels:

  • FBI Internet Crime Complaint Center (IC3): Submit a complaint regarding cyber breaches and online scams through the IC3 reporting portal.
  • Federal Trade Commission (FTC): Rport fraud, impersonation, and identity theft directly to the FTC fraud reporting page.
  • Federal Communications Commission (FCC): File complaints about illegal robocalls and caller ID spoofing via the FCC consumer complaint portal.
  • Local Police Department: Contact local law enforcement if you experienced monetary loss or direct extortion threats.
  • The FBI: Report direct agent impersonation through the official FBI contact page.

Prompt reporting provides law enforcement with vital intelligence to track threat actors and protect others from emerging scams.

The post FBI Job Portal Hack Claimed by ShinyHunters: What Happened and How to Protect Yourself appeared first on McAfee Blog.
  •  

FBI Warns of Law Enforcement Impersonation Scams: What They Are + How to Protect Yourself

The FBI Internet Crime Complaint Center (IC3) issued a September 2026 public service announcement warning of a rise in government and law enforcement impersonation scams. These scams feature individuals posing as law enforcement agents leveraging threats to acquire money or personal information.

Between January 2025 and July 2026, the IC3 received nearly 61,000 complaints regarding fraudsters posing as local police, federal agents, or court officials, with reported losses exceeding $1.6 billion. Imposters use caller ID spoofing and legal threats to extract immediate payments and sensitive personal information from their targets.

How Law Enforcement Impersonation Scams Work

Law enforcement impersonation scams rely on scammers projecting authority and manufacturing urgency. Their goal is to drive you to act before you can verify the caller’s identity.

According to the IC3, fraudsters use caller ID spoofing technology to make your phone screen display the legitimate name and telephone number of a law enforcement agency or court. They build credibility by providing fake badge numbers, official-sounding department names, and fictitious case file numbers.

During these law enforcement imposter scams, callers may claim that you missed jury duty, owe outstanding court fines, face an active arrest warrant, or have a suspended driver’s license or passport. The fraudster insists that you resolve the issue immediately over the phone or online. They demand payment via non-traditional methods, including prepaid gift cards, cryptocurrency, wire transfers, or physical cash couriers. Scammers frequently follow up with text messages or emails containing links to fake government portals designed to capture payment details and login credentials.

Impersonation Scam Warning Signs and Red Flags

If you receive a call from police, local courts, or federal agencies, watch for these warning signs that you could be dealing with a scam:

  • Demands for immediate payment over the phone: Legitimate law enforcement officers and court clerks will not call demanding instant payment to clear a warrant or missed jury duty summons.
  • Requirements for non-standard payment methods: Requests for payment via prepaid gift cards, cryptocurrency, bank wire transfers, or physical cash couriers indicate a scam.
  • Threats of immediate arrest or legal action: Imposters use aggressive tones to force rapid payment before you can verify their credentials through official sources.
  • Unsolicited links in text messages or emails: Follow-up messages directing you to online payment or verification portals are designed to capture personal credentials or payment details.
  • Requests for sensitive personal identifiers: Scammers ask for Social Security numbers, banking details, or account passwords under the pretense of “verifying” your record.

How to Protect Yourself From Impersonation Scams

  1. Hang up and verify through official channels. Immediately disconnect if you receive a suspicious call from police or court officials. Look up the agency’s official telephone number on a public .gov website and call directly to verify claims.
  2. Recognize how legitimate agencies operate. Real law enforcement officers, courts, and government agencies do not demand payment over the phone, nor do they accept gift cards, cryptocurrency, wire transfers, or cash couriers.
  3. Avoid clicking links in unexpected messages. Do not click unsolicited links or download attachments in emails or text messages claiming to come from court or police portals. Type official website addresses directly into your web browser.
  4. Limit public personal information. Fraudsters collect names, home addresses, and family details from social media and data broker websites to make fake scripts sound authentic. Adjust your privacy settings and submit removal requests to public data broker directories.

What to Do If You’ve Already Been Targeted

  • Stop all communication immediately: Cease interacting with the scammer immediately and do not send additional money.
  • Contact financial institutions: Call your bank, credit card issuer, or payment app provider right away to report the fraud and request a payment reversal or wire recall.
  • Secure online accounts: Change passwords and enable multi-factor authentication on all financial and email accounts that may have been exposed.
  • Freeze your credit: Contact Equifax, Experian, and TransUnion to freeze your credit files and prevent unauthorized accounts from being opened in your name.
  • Report identity theft: If you shared sensitive identifiers like your Social Security number, submit a report to the FTC to get a recovery plan.
  • Maintain evidence: Retain all call logs, text messages, emails, payment receipts, and cryptocurrency transaction details.

Reporting Law Enforcement Impersonation Scams

Reporting an impersonation incident promptly helps authorities track fraudulent networks and protects others from falling victim. If you encounter a fake call from police or a fraudulent court notice, submit an official report through the FBI Internet Crime Complaint Center. You should also contact your local police department to file a report, particularly if you experienced financial loss or received direct threats. Finally, inform the specific agency or court that was impersonated by calling the official directory number listed on its .gov website, allowing their security officials to issue public advisories.

The post FBI Warns of Law Enforcement Impersonation Scams: What They Are + How to Protect Yourself appeared first on McAfee Blog.
  •  

8 Steps to Protect Your Child From Identity Theft

The best ways to protect your child from identity theft include freezing their credit, limiting exposure of personal information, monitoring for suspicious activity, securing family devices, and teaching safe online habits. Because children often don’t discover identity theft for years, taking preventive action early can help protect their credit, finances, and future opportunities.

Child identity theft is one of the fastest-growing forms of fraud, and many families don’t discover it until years after the damage is done. But child identity theft has surged in recent years, with 38% of U.S. survey participants reporting that a child or family member’s child had been victimized in 2025, jumping from 23% the year prior.

This guide explains how child identity theft happens, what warning signs to watch for, and the eight most effective ways to protect your child’s future.

Key Takeaways

  • Children are prime targets because their Social Security numbers or national ID equivalents are a blank slate, allowing fraud to go undetected for years.
  • Data breaches, phishing scams, social media oversharing, and AI-powered fraud are making child identity theft more common and harder to detect.
  • In 2025, the FTC received 22,782 identity theft reports involving people 19 and under in the United States.
  • AI-driven scams are making it faster and cheaper to target families and steal children’s data at scale.
  • Freezing your child’s credit, monitoring for suspicious activity, and teaching safe online habits are among the most effective protective measures parents can take.

What is Child Identity Theft?

Child identity theft is a crime in which someone steals a minor’s personal information, most commonly the minor’s name, date of birth, and Social Security number (SSN) or equivalent national identifier, to commit fraud. The thief might open credit card accounts, take out loans, rent housing, file fraudulent tax returns, or claim government benefits, all in the child’s name. A 2021 Javelin Strategy study found that this crime affects one in every 50 children and costs U.S. families nearly $1 billion annually.

Why Child Identity Theft Is So Dangerous

The crime is made uniquely dangerous by the silence. Because children typically do not start applying for credit until they are 16 to 18, a thief can have more than a decade of undetected activity. As a result, by the time the victim becomes an adult, they may face:

  • Damaged credit scores
  • Debt collection notices
  • Loan denials
  • Difficulties renting housing

The crime is not confined to the United States, either. One documentary tells the story of Renata Furst Galvão, a native of Brazil, whose identity was stolen at age six and used to amass more than $400,000 in debt.

How Criminals Get Access to Children’s Information

To protect your child effectively, it helps to understand exactly who is targeting them, how they are getting in, and why the threat is accelerating. Even the most security-conscious household can be exposed through no fault of its own. In reality, information is often exposed through organizations that collect and store children’s data.

Common sources include:

  1. Data breaches at retailers, healthcare providers, schools, and financial institutions could expose children’s information alongside adults’.
  2. Social-engineering scams and phishing attacks may target parents directly to extract children’s details.
  3. Social media profiles are prime targets for identity thieves to monitor, which is why a child posting their birthday, school name, and city in separate posts creates genuine risks. Minimize the personal details shared online and in photos.
  4. Online games and apps that over-collect data, including a child’s full name, birthdate, and town, create additional opportunities for personal data exposure.

New Risks: AI Scams and Synthetic Identities

A December 2025 survey found that reports of ID theft rose from 43% in 2024 to 78% in 2025, a single-year spike that reflects how AI-powered tools have made it faster and cheaper for criminals to generate convincing phishing messages and fake identities at scale.

Synthetic identity fraud is particularly dangerous for children. It pairs a real Social Security number belonging to a minor unlikely to use it anytime soon with a fictitious name and address. The resulting fake identity can then build a credit history, take out loans, and disappear before anyone connects the dots.

Warning Signs Your Child’s Identity May Be Stolen

Catching this crime early makes the recovery process far less painful. Knowing what to look for means you will not dismiss the very clues that trigger a fast response.

Unexpected Mail, Bills and Collection Calls

The most common early indicators arrive in your mailbox or by phone, including:

  • Pre-approved credit card offers in your child’s name
  • Collection agencies calling to speak with your child
  • Court notices or bills for accounts your child never opened

Any business mail addressed to a young child should trigger an immediate investigation.

Rejected Applications, Benefit Denials, Suspicious Debt

Many families first discover the theft during pivotal life moments. Examples include:

  • A teen may be denied a learner’s permit due to fraudulent driving violations.
  • A young adult may be denied an apartment because of unpaid debt on their credit report.
  • Stolen Social Security numbers can interfere with access to government benefits.

Unexplained Credit Activity

Children typically should not have a credit history, so potential warning signs of identity theft include:

  • A credit report exists under your child’s name
  • Credit accounts appear that your family never opened
  • Loan applications are associated with your child’s Social Security number
  • Debt appears on your child’s credit file

If your child has a credit record before they are old enough to use credit, it may indicate identity theft.

The 8-Step Protection Plan for Parents

You can follow these steps while seeking guidance from financial educators, credit authorities, and consumer protection experts. Start small by choosing two or three today, then build from there.

Step 1: Check and Freeze Your Child’s Credit

A credit freeze is one of the most effective ways to protect your child from identity theft. If your child is under 16, request a free credit freeze from Equifax, Experian, and TransUnion. This prevents anyone from opening new financial accounts in your child’s name without your authorization. Once in place, the freeze remains active until you ask the credit bureau to temporarily lift or remove it.

Because minors typically don’t have established credit files, the process for placing a freeze differs from that for adults. Each of the three major credit bureaus provides specific instructions for parents and guardians. Follow the guidance from Experian, Equifax, and TransUnion to place a freeze on your child’s credit file.

Step 2: Enable Fraud Alerts and Social Security Reports

In addition to a credit freeze, it’s smart to watch for signs that someone is using your child’s identity. Ensure that you:

  • File a fraud alert with each credit bureau to prompt verification checks if someone attempts to open an account in your child’s name.
  • Request an earnings report from the Social Security Administration to confirm whether wages are being reported under your child’s SSN.
  • Once your child is old enough to have a legitimate credit file, teach them to stagger their use of free credit reports from the AnnualCreditReport website, checking one bureau every four months.

Step 3: Educate Your Kids about Identity Theft & Private Information

In an honest, age-appropriate conversation, explain to them that personal information is the master key to their financial future and should not be shared with online strangers. Role-playing helps: ask your child what they would do if someone they met in a game asked for their full name and home address. Empowered kids are less likely to overshare and more likely to alert you when something feels off.

Step 4: Get Fierce about Protecting Your Child’s Data

Draw a very thick line around your child’s details. Reiterate that sharing them should be limited only when truly necessary, such as school enrollment or medical forms, and only with verified institutions. Ask why it is needed, how it will be stored, and if an alternative identifier is acceptable. Keep important documents in a locked safe and shred papers with your child’s information before disposal.

Step 5: Lock Down Devices, Accounts, and Online Habits

Talk with your kids about safe internet habits. Instruct them to stay skeptical of quizzes, free offers or apps, and unbelievable promos that request personal details. Set their social media accounts to private and limit follower or friend lists to people they know in real life. Use strong, unique passwords for family accounts and enable multifactor authentication on email, school portals, and social media apps used by older children.

Step 6: Monitor for Early Warning Signs

Regularly check your household mail for notices addressed to your child. If you spot anything suspicious, contact the company directly using the contact details on its official website. Do not call the number printed on the suspicious document, as it could redirect you to the thief who sent it. Consider using an identity monitoring service that scans for your child’s data in data breaches or on the dark web and alerts you when their information surfaces.

Step 7: Get Full-Device and Network Security

Many identity theft incidents start with a compromised family device. To reduce this risk, keep operating systems, browsers, and apps fully updated. Secure your home Wi-Fi with a strong password and WPA3 encryption to prevent data interception. Comprehensive security software, such as McAfee+ Family Plans, can help you block malware, keyloggers, and phishing sites that harvest personal data from every device in your home, including the tablets and phones your children use most.

Step 8: Act Quickly If Theft Happens

If you discover or suspect your child’s identity has been stolen, immediately contact the company where the fraudulent account was opened, close the account, and request written confirmation that your child bears no liability. Report the theft to IdentityTheft.gov, follow the personalized recovery plan, and file a police report to create an official record that will help resolve disputes with creditors.

Next, contact each credit bureau to cancel fraudulent accounts, inquiries, and collection notices linked to your child’s SSN. Keep detailed records of every call, letter, and case number throughout the process. Reporting the incident to the authorities helps your family recover and supports broader enforcement efforts that protect other families.

Final Thoughts

Child identity theft is a fast-growing, serious threat worldwide, but it is also one of the more preventable forms of fraud when families take proactive steps early. Start this week by spending 10 minutes to safely lock away your child’s physical documents, then call the major credit bureaus to request a freeze on your child’s credit. Build toward the full eight-step plan over the next month to close every door that leads to potential harm.

Beyond the 8-step sprint, add a recurring data safety day to your family calendar each year to recheck credit freezes and fraud alerts, review your children’s online accounts and platform settings, update devices and passwords, and discuss emerging threats. A family that combines strong protective habits with smart security tools is a much harder target for any kind of cybercrime.

The post 8 Steps to Protect Your Child From Identity Theft appeared first on McAfee Blog.
  •  

A Parent’s Guide to YouTube Safety for Children

It’s 10 p.m. on a school night, but your child is still watching YouTube Shorts, one after another, and the feed never ends. YouTube is one of the most widely used video platforms among children. A 2025 Pew Research Center study found that about 85% of parents allow their children to watch videos on YouTube, including 51% who permit daily use.

If your children are among the millions using YouTube, this article will help you balance your child’s screen time on the platform, filter out inappropriate content, and keep their data safe.

Key Takeaways

  • Even kid-friendly content on YouTube can include inappropriate themes, aggressive marketing, or low-quality videos designed solely for engagement, not learning.
  • Choosing the right YouTube experience for your child’s age is essential. Select from YouTube Kids, supervised accounts on the main YouTube, or regular YouTube.
  • In January 2026, YouTube introduced new parental controls for Shorts, allowing parents to set time limits or block short-form videos entirely for supervised accounts.
  • The most effective approach combines smart tool settings, including content filters, time limits, and Restricted mode, with co-viewing and open conversations within families.

Is YouTube Safe for Kids?

YouTube can be safe for kids, but it isn’t automatically safe. While the platform offers educational videos, creative content, and entertainment for children of all ages, kids can still encounter inappropriate videos, cyberbullying, misleading content, and excessive screen time if parental controls aren’t enabled. For most families, YouTube Kids, supervised accounts, parental filters for YouTube, and regular monitoring provide the safest experience.

What Parents Need to Know about YouTube

YouTube has become a primary platform where children spend hours each week being entertained, getting help with their homework, and following social trends such as challenges and Shorts. They shift seamlessly between devices: first watching on the TV in the living room, then switching to a tablet in their bedroom, and then pulling it up on a phone in the car.

Unfortunately, some parents underestimate how quickly YouTube’s recommendation algorithm can steer kids from age-appropriate content to more intense, commercial, or borderline inappropriate videos. Recommendation algorithms are primarily designed to maximize engagement and viewing time, which may not always align with age-appropriate content. One minute, your child is watching an educational science video. Three autoplay cycles later, they’re watching an unboxing channel where an adult screams at toys for 20 minutes straight.

What Are the Biggest YouTube Safety Risks for Kids?

While YouTube offers everything from educational content to entertaining videos for kids, no video-sharing platform is completely risk-free. YouTube carries risks that many parents don’t fully understand until problems arise at home. Understanding these challenges is the first step toward helping children build more balanced digital habits.

Inappropriate and Low-Quality Content

Automated filters aren’t perfect. Despite explicit policies banning deceptive, sensational, and clickbait content on YouTube Kids, inappropriate content can slip through. You might find cartoon violence, endless unboxing videos dressed up with science or learning keywords, or content that promotes unrealistic body images. In addition, many videos aimed at children encourage risky physical challenges, harmful pranking, and consumerism.

If your child is gravitating toward such content, use it as a teaching moment. Watch a few videos together and ask your child what they like about them. Then gently guide them toward higher-quality alternatives.

Child development experts warn that this type of content, when consumed in large doses, can crowd out creative play, may contribute to a lack of focus, and reduce time spent on activities that foster creativity and critical thinking.

YouTube Shorts and Excessive Screen Time

Short-form vertical video like YouTube Shorts has become a particular source of concern for parents, educators, and mental health professionals. The format’s infinite scroll and rapid-fire delivery make it engaging for young viewers, but researchers and child safety advocates have raised concerns that endless-scroll feeds may cause sleep disruption and compulsive viewing habits.

In addition, pediatric health organizations, including the American Academy of Pediatrics, are concerned that excessive screen time can mean fewer hours spent reading, playing outdoors, having face-to-face conversations, or engaging in imaginative play.

Cyberbullying and Unsafe Interactions

Children using standard YouTube accounts may encounter toxic comments, harassment, or cyberbullying. While younger children are less likely to engage with comments, older kids and teens often participate in online discussions that can expose them to negative interactions.

If your child experiences online harassment:

  • Encourage them not to respond to aggressive comments
  • Teach them how to report online bullying
  • Use YouTube’s reporting tools to block abusive users
  • Save evidence of serious threats or harassment

Learning how to stop a cyberbully starts with open communication and making sure children know they can come to a trusted adult when something online feels wrong.

Data, Privacy, and Advertising

YouTube Kids collects data about your child’s viewing habits and device, including IP addresses, to power recommendations and serve ads. Although regulations such as the Children’s Online Privacy Protection Act (COPPA) in the U.S. limit personalized advertising for children, many parents remain uneasy about the amount of data collected.

Recommendation algorithms can also narrow what kids see, showing them endless variations of the same content type. A child who watches one slime video might end up in a loop of nothing but slime videos. This creates a repetitive, passive viewing experience that doesn’t expose children to diverse ideas or interests.

Red Flags or Warning Signs Parents Should Watch For

A child doesn’t need to view harmful content to develop unhealthy YouTube habits. Consider reviewing your family’s YouTube settings if you notice:

Behavioral Changes

Consider reviewing your family’s YouTube settings, screen time limits, and online safety practices if you notice any of the following:

  • Meltdowns, arguments, or persistent bargaining for “just one more video” when it’s time to stop watching
  • Sleep disruption, including difficulty falling asleep, waking up tired, or sneaking devices at night to watch videos
  • Declining interest in offline activities, such as sports, reading, hobbies, or time with friends and family
  • Secretive behavior, such as hiding screens, clearing watch history, or becoming defensive when asked what they’re watching
  • Slipping grades or incomplete homework due to excessive time spent watching videos or YouTube Shorts
  • Appearing unusually anxious, upset, or withdrawn after spending time on YouTube
  • Receiving mean comments, harassment, or unwanted attention on their uploaded videos
  • Becoming overly attached to content creators and speaking about them as if they are personal friends
  • Reluctance to discuss online interactions, comments, or messages from other users

These behaviors don’t necessarily mean your child is watching harmful content. However, they may indicate that YouTube is displacing other important activities, that screen time has become excessive, or that your child is experiencing uncomfortable online interactions.

For older children and teens, changes in mood, secrecy around devices, or sudden reluctance to use YouTube may also be signs of cyberbullying. Creating a judgment-free environment can make it easier for children to discuss negative online experiences and seek help when needed.

If you notice several of these warning signs at once, it may be time to reassess screen time limits, review the watch history together, and discuss how to interact safely with others online.

Choose the Right Experience for Your Children

YouTube offers three distinct experiences for families, and choosing the right one for each child matters more than any other setting you’ll configure:

YouTube Kids

YouTube Kids is a standalone app designed specifically for children. It offers three age-based profiles designed to pull up appropriate content for young viewers:

  • Preschool (4 and under): This is the most restrictive mode, featuring videos that promote creativity, playfulness, learning, and exploration.
  • Younger (5-8): This mode expands to include songs, cartoons, crafts, and content for early elementary-aged children.
  • Older (9-12): In this mode, the app features music videos, gaming content, science videos, and vlogs appropriate for tweens.

Within each profile, parents can choose between Curated mode and All of YouTube Kids mode. Curated mode includes only channels verified by YouTube’s human reviewers, making it the safest option for younger children. All of YouTube Kids mode includes more videos approved by automated filters, increasing the chance that inappropriate videos may slip through.

Disabling the search function in YouTube Kids limits your child to content on the home screen, which is an excellent option for very young children who don’t yet need the breadth of YouTube’s catalog. You can also block specific channels and review your child’s watch history to monitor what they’re watching. Overall, the app offers additional protections compared with the standard YouTube experience.

Supervised Accounts on Main YouTube

Supervised accounts on the main YouTube platform serve as a middle ground for kids who’ve outgrown YouTube Kids’ toddler aesthetic but aren’t ready for the unfiltered internet. These accounts, managed through Google Family Link, let parents:

  • Choose from three content settings: Explore for ages 9+, Explore More for ages 13+, and Most of YouTube for ages 18+
  • Enable or disable the search function
  • Manage which features the child can access, including comments, live streams, and community posts
  • Benefit from stricter community guidelines and protections for users under 18

After receiving feedback from parents and experts, the platform introduced controls to block Shorts or to set daily time limits for supervised accounts. The new controls also let parents:

  • Customize Bedtime reminders that prevent access during late hours when screens should be off
  • Enable Take a Break reminders, which prompt the child to pause after extended viewing sessions

These controls apply across all devices where the child is signed in and are designed to prevent children from disabling them without parental approval. In addition, the streamlined sign-up process makes it easier for parents to create a supervised account and switch between their own and their child’s account within the mobile app.

Regular YouTube

Regular YouTube is the full, unrestricted platform. If your child has an adult account, you’re relying entirely on their judgment and whatever settings they choose to enable. For younger teens, this can be risky without clear family agreements and monitoring.

Understanding YouTube Age Verification

YouTube uses account information and age-verification systems to determine whether a user should be treated as a child, teenager, or adult. Age verification determines what content users can access, what ads they see, and which safety features YouTube automatically applies.

How Does YouTube Age Verification Work?

When someone creates a Google account, they provide a birthdate that YouTube uses to determine age. In some regions, YouTube may also use account signals to estimate whether the user is under 18.

If YouTube determines that a user is under 18, the platform may:

  • Restrict age-restricted videos
  • Limit personalized advertising
  • Provide additional recommendation safeguards
  • Enable reminders to take breaks
  • Apply additional teen safety protections

What Happens If YouTube Thinks You’re Under 18?

If YouTube identifies a user as under 18, additional protections may automatically apply. These may include restrictions on mature content, changes to recommendations, reduced ad personalization, and digital well-being features designed for younger users.

How to Set Parental Controls on YouTube

YouTube offers several parental control options to help families manage content, screen time, privacy, and interactions. Most of these controls can be configured through Google Family Link, YouTube Kids, or YouTube’s built-in safety settings.

Parents who want to enable parental controls on YouTube, add a parental lock to the YouTube app, or create a more age-appropriate experience can explore the following options:

Parental Control

What It Does

Supervised Accounts

Allows parents to select age-appropriate content settings and manage certain YouTube features.

YouTube Kids

Provides a child-focused experience with age-based content settings and additional parental controls.

Search Controls

Lets parents limit or disable search to reduce exposure to unintended content.

Channel and Video Blocking

Allows families to block specific channels or videos they don’t want children to access.

Restricted Mode

Helps filter potentially mature content from search results and recommendations.

YouTube Shorts Controls

Lets parents manage access to Shorts and set viewing limits on supervised accounts.

Screen Time and Bedtime Controls

Allows families to set YouTube time limits, bedtime reminders, and viewing schedules.

Comment and Community Features

Gives parents greater control over interactions with other users.

For younger children, families may choose YouTube Kids with Search disabled to provide a more curated content experience. Older children and teens may benefit from supervised accounts that offer greater independence while still giving parents visibility and control.

Google regularly updates its parental control tools and settings. For the latest information on available options and setup guidance, visit Google’s Family Help Center.

Building a Safer YouTube Setup at Home

After choosing the right experience for your child, you can start configuring YouTube’s settings for added security.

For YouTube Kids

  1. Choose the correct age profile and content mode during the app setup.
  2. Disable search if you want to limit viewing to home screen recommendations only.
  3. Block specific channels if you notice your child repeatedly watching low-quality or overly commercial content.
  4. Turn off autoplay to prevent endless video chains.
  5. Review your child’s watch history weekly to spot any concerning patterns.

For Supervised Accounts

  1. Open Google Family Link and set up a supervised YouTube account for your child.
  2. Choose the appropriate content level, starting conservatively. You can always grant more access later.
  3. Set time limits for Shorts or block them if your child struggles with self-regulation.
  4. Configure Bedtime reminders to enforce screen-free hours, especially before sleep.
  5. Enable Take a Break reminders to interrupt binge-watching sessions.
  6. Keep search disabled initially, and enable it only when your child demonstrates good judgment.
  7. Review and adjust settings every few months as your child matures.

Any YouTube Account Your Child Might Access

  1. Turn on Restricted Mode, which uses community feedback, metadata, and other signals to hide videos that may contain mature content. To lock this mode so that your child can’t disable it, go to the Google Family Link.
  2. Disable autoplay and turn off notifications to reduce passive consumption.
  3. Review the privacy settings to make sure that your child’s uploads, if allowed, aren’t publicly visible.

Co-Viewing and Conversations

Settings and filters are necessary, but they’re not sufficient. Research on children’s media use consistently shows that the best outcomes result from combining tools with active parental engagement. This means:

  • Co-viewing: Sit with your child regularly and watch their favorite channels together. Ask what they like about the content and use it as an entry point for conversations about advertising, authenticity, and what’s real versus staged.
  • Talking about what they see: If your child watches gaming videos, talk about the difference between games and reality. If they watch beauty influencers, discuss how lighting, makeup, and editing can create unrealistic expectations.
  • Modeling good habits: Children learn by watching you. If you’re constantly on your phone or scrolling through videos during family time, they’ll internalize that as normal. Set family screen-free zones and times that apply to everyone, including adults.
  • Creating a media plan: Sit down together and agree on daily or weekly screen time limits, acceptable content types, and what to do if they encounter something that makes them uncomfortable. Tools like the American Academy of Pediatrics media plan can help structure this conversation.

Final Thoughts

Recent years have brought improvements to YouTube as an engagement tool for children. Short-form video time limits, supervised accounts with meaningful controls, and growing awareness among parents and educators of the stakes mean we are better positioned to create safer, more balanced digital experiences.

Combine these efforts with another layer of comprehensive protection tools, such as McAfee+, to help reduce exposure to threats that may bypass platform-level filters. Together, these measures support a more thoughtful and safer online experience for children.

The post A Parent’s Guide to YouTube Safety for Children appeared first on McAfee Blog.
  •  
❌