OpenAI has launched two new security products, one for penetration testing and another for defense, and warned organizations that their businesses are only safe if they use tools like these. “We're now at a point where companies will be secure only to the extent of the frontier model that they use to defend themselves and how well they utilize that,” OpenAI President Greg Brockman said during a Thursday keynote address. The co-founder of the company that broke security did admit that security “fundamentals are important, and not to be discounted.” However, “you need to really reorient your security practice around what these models can do,” Brockman said, with zero irony, and presumably talking about using AI models for defense - not for hacking other organizations. “Also very important is product.” This product, of course, should come from OpenAI, and, to that end, the company rolled out Daybreak Red Team and Daybreak Defense Factory, which are both part of OpenAI’s Daybreak security platform. Red Team, which is available in early access, uses OpenAI models to test companies’ web applications for vulnerabilities. Nancy Wang, who leads cyber-applied AI, described it as “superhuman pen-test at the scale of automated continuous scanning,” with a fleet of agents using source code and app context to investigate and test attack paths. It also helps security teams validate reported vulnerabilities - from code scanners, bug bounty programs, and disclosure reports - and then test the patches for these flaws. The second product, Daybreak Defense Factory, automates the “defensive loop” by “finding, validating, and fixing vulnerabilities at scale.” This one also uses agents built on OpenAI’s latest cyber models - currently, that’s GPT-6 Cyber. The agents scan organizations’ codebases, hunting for vulnerabilities and developing patches. Engineers review and approve the proposed fixes before they go into production. “This way engineers get a merge-ready pull request with the patch and a test that shows that it works,” Wang said. Meanwhile, as OpenAI execs touted the new security products, a coalition of nonprofits filed a lawsuit in San Francisco Superior Court asking a judge to stop OpenAI, Anthropic, Google, Meta, and SpaceX's AI businesses from developing or deploying AI systems more capable than their most advanced existing models. The lawsuit, filed by Irreplaceable Education Fund, Public Citizen, Heat Initiative, and The Alliance for Secure AI, cites incidents involving OpenAI agents accessing Hugging Face, gaining unauthorized access to an Australian government portal containing Medicare statistics, and other AI-related cybersecurity incidents. “Defendants tell us that the AI technology they are developing poses catastrophic risks to the public, including by enabling AI-driven cyberattacks and bioweapons,” the court documents allege, adding that the AI companies “are not wrong.” ®
Lego-owned marketplace BrickLink has been offline for almost a week after identifying "unusual activity on the platform," leaving fans unable to buy and sell spare bricks and minifigures. The company initially described the outage as "necessary work" and said the site would return on November 9. That deadline has come and gone. Visiting BrickLink's domain automatically serves the platform's maintenance page, which was last updated on November 11. "We took BrickLink offline after identifying unusual activity on the platform," the website states. "Our immediate priority was to secure the site, protect our members and ensure the integrity of BrickLink. "Before bringing the site back online, we need to fully understand what has happened. That means containing the issue, investigating how it happened and checking for related issues. "This work is still ongoing and we appreciate your patience while we work to get things back online as soon as possible." The references to security, containment, and investigation suggest something beyond routine maintenance, although BrickLink has not confirmed whether it suffered a cyberattack. The Register asked Lego for more information, but it did not immediately respond. Some adult fans of Lego (AFOL) have criticized the lack of information since the outage began on Friday, November 6. "Imagine how much better this would have been received if they were transparent from day one instead of pretending they have control over something they clearly don't," said one disgruntled Legohead via Reddit. "They don't even need to say what went wrong," said another. "Just an email acknowledging the issue would be appropriate. The entire site is down, and has been for days. That warrants more than a splash page." BrickLink was launched by Dan Jezek in June 2000 as an independent marketplace for enthusiasts to buy and sell Lego sets and individual pieces, including discontinued parts and rare minifigures. The Lego Group acquired BrickLink and Sohobricks from investment outfit NXMH in 2019 for an undisclosed sum. NXMH had bought BrickLink in 2013 and also owned Sohobricks, a South Korean manufacturer of unofficial but Lego-compatible bricks. Lego shuttered Sohobricks in 2020. At the time of Lego's acquisition, BrickLink had more than 10,000 storefronts on its marketplace selling Lego sets, parts, and minifigures. The AFOL community was initially concerned about Big Brick's intention with the acquisition, fearing that it would lead to high prices closer to those on Lego's own Pick a Brick parts-ordering service. For now, buyers and sellers would probably settle for a marketplace that's actually online. ® Updated to add on November 13: Lego said on Friday that BrickLink is back online after acknowledging the "confusion and uncertainty" the downtime caused among Lego fans. A statement made via the BrickLink website confirmed that "some" usernames and IP addresses were accessed, as were "a very small number" of email addresses. "We have already emailed members whose BrickLink usernames or emails were accessed with further information," it said. "Based on our investigation, passwords and payment information were not accessed. You do not need to take any action at this time. We have addressed the issue identified through our investigation and will continue to monitor the platform closely." The site is back online, although its Studio Forum remains down, and the company said it will provide more information on this front "over the coming days." BrickLink will also waive sellers' fees for November and December as a token of appreciation for putting up with the downtime and disruption.
eMudhra's private key exposure has been a security disaster, but it also means that you can block those annoying ads on smart TVs if you’re so inclined. Luckily for those with some know-how and a hatred of smart TV ads, Czech software developer Daniel Vrátil has done the work for you and published his project on GitHub for anyone who wants to take a stab at it - and do the legwork to add support for their own ad-riddled television. Vrátil said he’d been blocking ads on his Samsung smart TV using a Pi-hole (DNS-based ad-blocking software that can run on a Raspberry Pi, for those unfamiliar), but right around the time the eMudhra certificate leak mess unfolded, he had messed something up while tinkering with his home lab and the ads were back. First, here's a bit of background on the eMudhra mess. The company, based in India, operated a publicly trusted HTTPS certificate authority and says it has issued more than 60 million digital certificates. As we learned last month, eMudhra wasn't doing its best to keep its cryptographic keys safe: Eight intermediate CA private keys were found to be absurdly weak, with one being the number four and the others consisting of two- or three-digit numbers that could be guessed with little effort. eMudhra has since left the CA racket, saying that it wasn’t a big deal to it since issuing certs was a small part of its business. The company has blamed a bad software script put in place to generate keys that its hardware couldn’t handle as the root of the issue. What all that means, in a practical sense, is that anyone could forge an eMudhra certificate to spoof a website and do something malicious. It also means that security researchers who were able to get their hands on devices that still trust eMudhra certificates could have a field day learning how their communications work, which is exactly what Vrátil took advantage of. eMudhra private keys were added to the open source mitmproxy service - a fully interactive HTTPS proxy that can be used for good or bad - shortly after they were exposed. Pair that with a 2022 Samsung smart TV that still trusts the compromised eMudhra certificates, and you have a way to inspect its HTTPS traffic and redirect selected requests to a server of your choosing. By Vrátil’s account, swapping out annoying ads for pictures of his family on his TV’s main screen was a pretty simple task. “Luckily for me, Samsung did not yet release an update for my TV that would revoke the certificate,” Vrátil explained in his writeup. “This allowed me to route all traffic from the TV through mitmproxy and get a list of all the domains and endpoints that my TV talks to, but also see the structure of the requests and response payloads.” The advertising traffic flow was pretty basic, it turns out: Activity on the TV is relayed to an ad server, which serves up ads on the home screen based on a JSON response. By generating a certificate for Samsung's advertising domains using a compromised eMudhra signing key, and configuring his router to direct requests for those domains to a server on his home network, Vrátil was able to replace ads with family photos served from his NAS. He also added code that tosses other requests to those advertising domains, including tracking data, into a black hole rather than forwarding them to Samsung's servers. As mentioned above, it’s on GitHub for those who want to trick their TV, if it still supports eMudhra certificates, but you’ll have to do the legwork to dissect how your device is getting ads and tweak the code to work. “It's not exactly a one-click setup,” Vrátil told The Register in an email. He’s invited people to try it out, but no one has bothered to submit a pull request to add support for their own device to his public repo. It’s also worth noting that this is only going to work as long as vulnerable devices keep trusting eMudhra certificates, which hopefully means you need to act fast. That said, smart TVs that are out of support may never receive such an update, leaving them exposed to the certificate weakness even if their owners block the ads. “The compromised eMudhra certificates open up a lot of opportunities for understanding and spoofing network requests from embedded devices, especially those that no longer receive security updates,” Vrátil told us. “And while replacing ads on a TV's home screen with pictures of my family is fun, there are also countless much more sinister applications of this vulnerability.” As for Vrátil, he’s still trying to figure out how to block the firmware update that may eventually render his method obsolete, even though that, as he points out, is a security risk in and of itself. “I want to run the traffic through a proxy that would validate the connection against an up-to-date trust store to at least mitigate anyone intercepting traffic from my TV, or spoofing responses, like I do with my little project here, but it won't protect me from other potential security risks, so there's a trade-off,” he explained. We suppose at this point you can take your pick of abuse. You can use a vulnerability to block ads and some tracking while leaving your TV exposed to potential interception, or let the manufacturer serve up ads and collect data about your viewing habits. There are safer ways to block ads than relying on a TV to keep trusting a compromised CA. ®
Microsoft has warned customers still clinging to Exchange Server 2016 and 2019 to consider the software "permanently vulnerable" as November's security fixes arrive for Subscription Edition (SE) alone. The warning appears in the release documentation for November's Exchange Server SE security update. Looking for Exchange 2016 and 2019 information? Tough. Microsoft stated: "Exchange Server 2016 and 2019 are no longer tested for vulnerabilities and there are no updates released. If you are using those versions of Exchange, you should consider them permanently vulnerable [Microsoft's emphasis] and should upgrade your organization immediately." You have been warned. Support for Exchange Server 2016 and 2019 ended on October 14, 2025, but the company announced an Extended Security Updates (ESU) program in July 2025. The plan was that this program would end on April 14, 2026, by which time customers would surely have made the jump to a later or online version, right? The company said: "This period will not be extended past April 2026 (you do not need to ask)." And... of course it was. As April 2026 rolled around, and it became clear that some customers were still stubbornly sticking with the old versions, Microsoft did the equivalent of heaving an exasperated sigh and offered another six months of paid security updates. Those final weeks also brought a separate treat: a Windows Server update breaking Exchange Server. This time it was serious. Microsoft released the final Exchange Server 2016 and 2019 security updates on October 13. No more patches, no more vulnerability testing, and apparently no more reprieves. According to Microsoft's Security Update Guide, the November update fixed nine vulnerabilities in Exchange Server SE, including a critical remote code execution flaw, CVE-2026-118207. Microsoft isn't testing earlier versions of Exchange for the vulnerabilities. ®
Hackers have used a dodgy third-party ScreenConnect extension to push malware onto at least 288 machines across 48 organizations, prompting ConnectWise to disable a handful of plugins in hundreds of customer environments. Security outfit Huntress first raised the alarm in a Reddit post on Wednesday, warning of an active campaign targeting cloud-hosted ScreenConnect instances. At the time, its security operations center was tracking six compromised managed service providers (MSPs) and more than 286 affected endpoints, with the numbers still climbing. ConnectWise acquired popular remote supporttool ScreenConnect in February, 2015. Huntress spotted the attacks at around 1747 UTC, when someone began using ScreenConnect's remote command feature to install rogue clients on machines managed by multiple IT service providers. All 288 endpoints were hit within 90 minutes, with roughly a third compromised in the first ten minutes. Huntress suspects more MSPs may have been compromised, as the attackers appeared to be numbering their victims sequentially, with the numbers suggesting earlier attacks that it hadn't detected. The attackers deployed a 16-file malware toolkit dubbed SCKit, which installs a separate ScreenConnect client to maintain remote access even if the legitimate connection is shut down. It also contains code designed to spread the infection to IT technicians and potentially other customers under their control. Huntress has since traced the activity to a possible authentication weakness in RMM+, a third-party extension that lets other management tools issue commands through ScreenConnect without technicians using its console. Versions 1.0.31 and 1.0.32 of the extension contain a flaw that means installations without a configured access key will accept a blank one. Because RMM+ operates independently of ScreenConnect's normal user accounts and authentication controls, an attacker could potentially execute commands without defeating MFA. Huntress said the findings matched what its investigators saw during the attacks, with commands reaching machines across several ScreenConnect installations despite no corresponding login activity. The researchers also confirmed that the attacks affected ScreenConnect versions 26.6.6.9747 and 26.7.6.9783, meaning administrators running the latest releases weren't necessarily safe. ConnectWise has acknowledged that third-party extensions may have been involved but has stopped short of confirming how the attackers initially gained access. In a security advisory, the company said it was investigating unauthorized access to certain partner environments and had identified approximately 400 installations containing at least one extension from the RMM+ family. It has disabled five extensions, including RMM+, RMM Plus, and Labtech Plus, wherever it can do so remotely, and urged customers running their own ScreenConnect servers to follow suit. ConnectWise stressed that the 400 environments were identified because they had the extensions installed, not because they were necessarily compromised. The company said: "At this time, we have found no evidence of a compromise of ConnectWise infrastructure or a vulnerability in ScreenConnect itself." There's another nasty trick buried in SCKit. According to Huntress, the malware is designed to turn an infected computer into a trap for the technician sent to investigate it. If the technician connects through ScreenConnect, the toolkit attempts to transfer malware back to their workstation, steal authentication cookies, and use their access to infect other machines. That could give attackers a route from one compromised customer into others managed by the same IT provider. However, Huntress says it has yet to see that part of the attack succeed. "We have not observed that method to spread work successfully. The console-takeover attempt failed in every recovered host log we have checked so far," the researchers wrote. Huntress also suspects that some of the malware's C# code was generated using an LLM, pointing to unusually detailed comments explaining what the code is supposed to do. Apparently, even malware authors appreciate a little help with their homework. Both Huntress and ConnectWise are urging administrators not to investigate suspected infections by remotely connecting through ScreenConnect, since doing so could put the technician's own machine at risk. Administrators are being advised to use other security tools to investigate affected machines, look for rogue ScreenConnect clients, and check what commands have been run. Any malware left behind will also need to be removed before the machines are brought back online. Huntress warned on Reddit that some machines were becoming reinfected within minutes of being taken out of isolation because the malware had not been properly removed. Simply disabling the vulnerable extensions won't necessarily undo the damage, either. As ConnectWise warns, "Disabling extensions and resetting credentials alone may not remove unauthorized software, persistence mechanisms, or access already established on endpoints." And with the attackers already able to install their own remote access software, kicking them out could prove considerably harder than closing the door they came through. ®
European tech buyers are increasingly choosing cybersecurity vendors from their own continent in a bid to reduce their reliance on American technology. Digital sovereignty isn't only prompting enterprise customers to question their clouds of choice, it is also reshaping other parts of the industry too, and the shift is marked. According to sales figures compiled by Context, distributor sales in EMEA of cybersecurity products from EU-headquartered vendors jumped 35 percent in the two years to calendar Q3 2026. Total cybersecurity sales grew up 10 percent over the same period, and sales by US-run companies went up just 8 percent. That growth is from a relatively small base, though EU vendors gained nearly three percentage points to reach 15 percent of tracked sales by value. There is still a long way to go as US-headquartered vendors accounted for 62 percent. The trend coincides with a loss of trust in the Trump administration among customers outside of America, after it cosied up to autocratic rulers while criticizing and punishing allies with tariffs and more. Context stopped short of assigning blame. It said organizations are reviewing their reliance on third-party tech in light of EU compliance regimes: the NIS2 Directive and Digital Operational Resilience Act (DORA). NIS2, transposed into national law in October 2024, requires organizations in the bloc to raise their common level of security in the face of digital threats and risks to critical infrastructure. DORA, introduced in January last year, is designed to strengthen cyber security in the financial sector. "Digital sovereignty is becoming a buying decision. As customers and resellers get clearer about what it means in practice, they're asking who holds the encryption keys, who can access sensitive logs and where that data is stored," said Context veep of research Joe Turner. "We're seeing a measurable shift in the EMEA channel. EU vendors gained nearly three points of sales share in two years. An organization can keep its existing identity platform and still choose a European supplier to manage its security logs. That's the kind of decision that gives European vendors an opening." The stats indicate that EU-HQd vendors comprised 92 percent of tracked sales in security awareness training, 82 percent in vulnerability management, and 52 percent for SIEM and log management. US-headquartered companies held into 74 percent of identity and access management sales and 54 percent of cloud security sales. The Reg has asked Context for UK-specific figures to see whether British customers are also voting with their wallets for European alternatives. That certainly isn’t the case for tech purchases in the British public sector, despite Prime Minister Andy Burnham’s professed desire to buy British. Data released yesterday by the Institute for Public Policy Research showed just £1 in every £6 spent by government with the biggest technology suppliers goes to Brit businesses. Still, Burnham only came to power in July so there is time yet for him to put his money where his mouth is. Sovereign AI is another area of concern for enterprise customers. Analyst Omdia said last month that despite the marketing adjective meaning "local assets," almost a third AI providers disclose no proof of sovereignty, and some "expect enterprise to pay for audits to verify their claims." Omdia also found that 80 percent of contracts say network resilience is "out of providers control or responsibility," and "US-headquartered AI providers offer better service transparency and contract terms than a majority of local sovereign AI providers, with providers in India a notable exception." Sovereign services in Omdia's classification include data residency, operational autonomy, jurisdictional sovereignty, and technological autonomy. "Local hosting is not sovereignty. Serious providers must demonstrate their credibility through transparent operations, fair contracts and proof of competence. That includes the network, because data in transit must be sovereign too," said Camille Mendler, research director for telco B2B at Omdia. Someone should tell Microsoft and Anthropic. ®
Welcome, once again, to PWNED, where all the victims are self-owned. This week, we welcome you to a London hotel where you could check out its admin credentials for a booking website just by walking past the front desk. Our story comes courtesy of Neycho Tepavicharov, co-founder of Flashcloud, a Delaware-based web hosting company. He was staying at a hotel in London when he noticed a shocking breach of basic security protocols by management, who were a little too hospitable with their credentials. As he was passing through the lobby, Tepavicharov noticed that the door behind the front desk was open and, inside that back room, there was a whiteboard. On the whiteboard, written in plain English, were the hotel’s Booking.com administrative username and password. Anyone near the desk could clearly see the login information, and if they didn’t have time to write it down, they could have snapped a picture for later use. As Tepavicharov explains, there’s plenty of mischief you could perform with these credentials. “With that login, someone could change or cancel reservations, see guests’ names and contact details, or message guests pretending to be the hotel,” he said. “Fake 'please confirm your payment' messages sent from compromised hotel accounts are a well-known scam.” An attacker could potentially exploit that access to disrupt hotel operations or target guests with convincing scams. Whether the exposed credentials alone would have been enough to access the account would depend on its security settings. Tepavicharov decided to play the role of good samaritan and warn the hotel’s manager that the business was endangering itself by showing everyone its password. “I asked to speak with the manager and showed him what I’d seen. He was mortified and very grateful,” Tepavicharov said. “Nobody on staff had thought of it as a risk. It was just the easiest way for the whole team to share one login.” After Tepavicharov talked to the manager, not only did the hotel change its ways, but it also moved its website to his hosting service, Flashcloud. Tepavicharov notes that there are plenty of takeaways from this incident. Most important: give each user dedicated credentials with their own separate login, and use multi-factor authentication. “The lesson is an old one, but it keeps happening,” he said. “Shared logins end up written somewhere convenient. Give each staff member their own login, turn on two-factor authentication, and keep passwords in a password manager, not on the wall.” ®
Former certification authority eMudhra has claimed a buggy Python script is the main reason it issued laughably insecure digital certificates. The company posted its account of the matter on Bugzilla where a user with the handle “Naveen Kumar ML” wrote “During a single key‑generation ceremony on 30 April 2025, sixteen subordinate (issuing) CA key pairs in eMudhra’s ‘B’ and ‘C’ series were generated correctly on a hardware security module and then processed through an approved wrap/unwrap round‑trip using a custom python key‑handling script.” eMudhra aimed to create eight ECDSA P-384 private keys which should have been 48 bytes long. But the script contained what Kumar described as “a bug/defect in the import code [which] resulted in a read‑back from the unwrapped object that truncated the private value, so the certified public keys correspond to private scalars below the expected range and are recoverable from public information.” The truncation is the key problem here, because it appears that eMudhra ignored 47 of the 48 bytes, producing its infamously insecure single-byte keys such as the number four. Whatever the nature of the bug, Kumar asserts it was “a custom script run only on an isolated ceremony host and was not a function of the emCA software.” eMudhra needed that script because “global supply chain constraints” meant it couldn’t acquire the hardware security modules (HSMs), devices that generate and store cryptographic keys, that it wanted to use when creating a set of certificates for use in the USA. It therefore used HSMs made by a company called Utimaco to generate keys and planned to transfer the keys it produced to a different set of HSMs from a company called Crypto4A. Kumar explained that eMudhra decided on that move, which is unusual, because changes to policy about provenance of certificates meant it had to generate new certs by the end of May. The plan went sour when the company didn’t notice the errors in its script and didn’t test the keys it created. The rest is history: a Mozilla team member noticed that the company’s keys were woefully weak and pointed out that attackers could therefore issue fraudulent certificates that allowed them to impersonate servers, observe traffic, or even modify data in transit. Browser-makers quickly tweaked their software so it would not recognize certs from eMudhra. The Indian business then quit the SSL/TLS certification business, which it said was never a major source of revenue but had suddenly become a severe source of embarrassment. Kumar’s new post lists three steps eMudhra will take to wind up its certification business, one of which will see the company “Put in place improvements motivated by findings of [an] independent review to strengthen our general PKI operations.” Sounds like a plan. ®
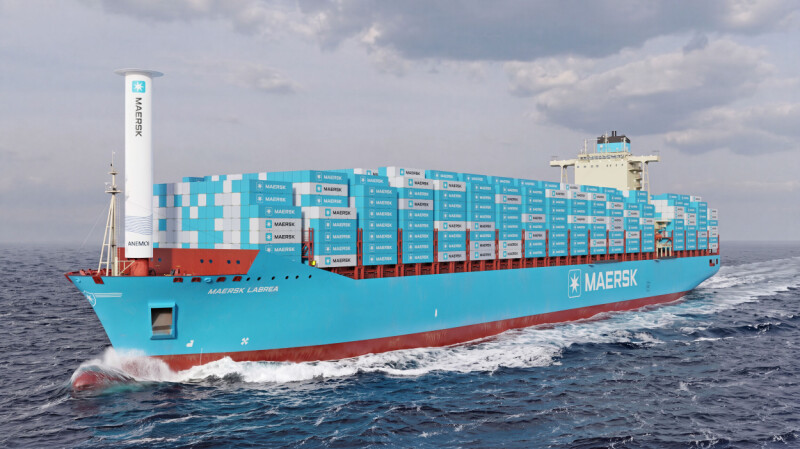
Shipping behemoth A.P. Moller-Maersk says it is investigating "an IT security incident" involving the potential theft of data from a legacy system. In a statement issued on Wednesday, the Denmark-based shipping, cargo, and logistics giant confirmed it immediately launched an investigation into the attack and the affected system was secured. "Our findings so far strongly suggest no sensitive data has been disclosed," the company said. "The incident is isolated to a local system, and we have found no indication that there has been any impact on other Maersk systems or customer and partner systems that connect to Maersk through integrations such as APIs and EDI." Maersk described the legacy local system as one "from a previous acquisition," and said it does not expect the attack to have an effect on operations. Customers were reassured that they can continue to use Maersk platforms to manage their shipments as usual, and to expect updates from the company as and when they're available. "Cybersecurity remains a constant, ongoing priority for Maersk," it added. "We have rigorous processes in place to identify and prevent incidents and minimize customer impact. "As always, please treat any unexpected communications claiming to relate to this matter with caution and verify them through your usual Maersk contact. "Thank you for your patience as we continue to investigate the incident." Fortunately for those who immediately feel uneasy after hearing "Maersk" and "IT security" mentioned in the same breath, the wording of the shipping giant's disclosure suggests this intrusion won't be as calamitous as the NotPetya disaster in 2017. Mimicking the Petya ransomware strain, NotPetya was an infamous destructive wiper malware strain that wormed its way across the global economy. Western intelligence agencies attributed the malware to Russia's Sandworm group, an outfit believed to be part of the country's military intelligence service (GRU). Maersk said at the time that it expected the attack to result in a circa $300 million bill, owing to remediation and rebuild costs. Offering a sense of scale, Jim Hagemann Snabe, then chair of Maersk, told World Economic Forum delegates in 2018 that the company's rebuild encompassed 4,000 new servers, 45,000 new PCs, and 2,500 applications – which he said had been completed over just ten days. In 2020, as exclusively revealed by The Register, Maersk went on to lay off around 150 staffers from its command and control center in Maidenhead, England. The staffers who lost their jobs had played key roles in the recovery. ®

 Login