The October 2026 Windows security update may break networking for some customers who are still clinging to long-deprecated NTLMv1 security. A seemingly minor change in the update could have major implications for administrators and enterprises that haven't fully moved away from the legacy technology. Before the October 2026 update, Windows permitted NTLMv1-derived credentials for Single Sign-On and generated warning events. After the update, requests to use NTLMv1-derived credentials are blocked. It comes down to the BlockNtlmSSO registry value. If it hasn't been set, Windows will now use Enforce mode (1) instead of Audit mode (0), thus blocking requests and potentially impacting Wi-Fi, Ethernet, and VPN authentication, and therefore connections. The update does not set the value of BlockNtlmSSO, and administrators can set it to 0 to temporarily allow NTLMv1-derived Single Sign-On credentials. However, Microsoft noted, "Using Audit mode reduces the protection provided by Enforce mode and should only be considered as a scoped, temporary security exception." To be clear, this is not a bug and is by design. The addition of NTLM to the deprecation list occurred in 2024, and Microsoft added audit logs for NTLMv1 usage in late August 2025. The Windows giant has made no secret of its desire to ditch the legacy technology, stating in 2023, "Our end goal is eliminating the need to use NTLM at all." The problem is NTLM's longevity. It appeared in 1993 with Windows NT 3.1, and removing it from enterprise environments has proven tricky, even though it is somewhat insecure by modern standards. Microsoft removed it from Windows 11 24H2 and Windows Server 2025, but some remnants can still be found, notably when using MS-CHAPv2-based connections, including PEAP-MSCHAPv2, and EAP-MSCHAPv2, in a domain-joined environment. Hence the introduction of the audit mode in 2025, to help administrators spot where the technology was still being used. It is now 2026, and Microsoft has taken the next step. If Credential Guard is not enabled and BlockNtlmSSO is not set to Audit mode (0), the use of NTLMv1-derived credentials will be blocked as Microsoft works "to finalize the disablement of NTLMv1." There is no indication of how long the BlockNtlmSSO workaround (setting the value to Audit mode) will work - most likely until the next major Windows release. In September, Microsoft said, "In-market versions of Windows client and Windows Server will continue to support NTLM." However, it also stated, "Our long-term objective is a Windows platform that doesn't need NTLM at all." As such, if the message wasn't already clear, the move to enforce it by default makes it impossible to miss. The technology still exists in the operating system, but it is on its way out and will be removed in a future Windows release. Problems with networking after the October 2026 Windows security update could therefore signal that migration plans are not as far along, or as complete, as administrators might have thought. ®
The US' bankruptcy courts are currently down owing to what officials are calling a “cybersecurity incident.” The Administrative Office of the US Courts said the websites and systems that support the Bankruptcy Noticing Center (BNC), which manages electronic comms related to bankruptcy cases, were pulled offline while the vendor investigates. BAE Systems runs the affected systems and websites on behalf of the Federal Judiciary, and is “working to restore operations,” according to an announcement by the US Courts on Thursday. “As a result of the incident, all access to the BNC systems and websites that BAE operates on behalf of the judiciary and the related bankruptcy noticing process are unavailable at this time, including bnc.uscourts.gov, bankruptcynotices.uscourts.gov, notices.uscourts.gov, and the National Creditor Registration Service," it said. “The incident has also halted the BNC’s production and distribution of bankruptcy notices for bankruptcy courts.” While the public notice was published on Thursday, the issues affecting the BNC systems began a few days earlier, on October 9, according to the Bankruptcy Court of the Eastern District of Texas. Alongside its own announcement, the same court published a general order indicating that for any case filed on or after September 14 with an active motion to stay, that delay would be extended by an additional 30 days. The court said it will continue to accept filings, open cases, and process documents, but said there may be a delay in the entry and service of notices and orders until the issues are resolved. The courts' ability to process electronic and paper bankruptcy notices is affected, and it applies to federal bankruptcy courts across the country. A spokesperson at BAE told The Register: "BAE Systems, Inc. operates the Bankruptcy Noticing Center (BNC) on behalf of the Administrative Office of the U.S. Courts (AOUSC). We are aware of a security incident that is isolated to the BNC system and have taken immediate steps to address it. We are coordinating closely with AOUSC on the response." The disruption comes at a difficult time for the US public sector, which has struggled with multiple recent cyberattacks. ShinyHunters' attack on the FBI in September is doubtless the most high-profile of these, although the Arizona Judicial Branch confirmed an attack on the state’s court systems at around the same time. Officials said the “criminal hackers or their bots” were responsible for stealing personal data and backup court files. The US Courts also said in August 2025 that it was stepping up its cybersecurity measures in response to increased targeting of its case management system. ®
An old-fashioned smash-and-grab job on a photographer’s vehicle threatens the security of pupils’ data as a UK secondary school says it faces a potential data protection pickle. Jon Curtis-Brignell, headteacher at Priory School in Lewes, said in an email this week that a company the school hired to take pupils’ annual school photos has alerted it to a data theft case after a vehicle was broken into. “Pret-a-Portrait has informed us that, overnight between 6 and 7 October, one of its vehicles was broken into and a camera bag containing SD memory cards was stolen,” Curtis-Brignell wrote. “Some of these cards may have contained photographs taken at Priory School, together with images of the QR code cards used for school photographs, which show pupils’ names and class names.” The headteacher said that the same equipment used to take the photos at Priory School was also used for three additional photography jobs after Pret-a-Portrait visited the school on October 1. Pret-a-Portrait, which has offices in the UK, Qatar, and the UAE, told the school that it believes “most, if not all” of the files containing pupils’ data will have been overwritten as a result, but it cannot be certain. Curtis-Brignell said that the potentially affected information included photographs, pupils’ names, and their “class information associated with the photography process.” Other types of data, such as addresses, contact details, financial information, medical information, and safeguarding records stored in the school’s own systems remain untouched. Nick Kerr, owner of Pret-a-Portrait, told The Register that no physical, printed photos were stored in the vehicle at the time of the break-in, and that it was not possible to determine the potential scope of the data protection violation. “As the email from Priory School explains, it is likely to be somewhere between a small subset of their pictures and none of them,” said Kerr. On a positive note, he said that there is nothing to suggest the files have been improperly accessed. “Our analysis reveals that no improper access to pictures from this job occurred in between the time of the theft and the pictures being taken offline.” Per the headteacher’s email, Pret-a-Portrait confirmed that it took a number of steps to mitigate the potential damage, including taking all school photos offline, changing the IDs used to access them, and changing its procedures so that all SD cards are wiped at the end of each commission. The company also “reviewed and strengthened its procedures following the incident,” and reported the matter to both the police and the ICO. “I appreciate that receiving an email of this nature may understandably cause concern,” Curtis-Brignell added. “We have worked closely with our Data Protection Officer and Pret-a-Portrait to understand what happened, establish the potential risk and ensure that appropriate action has been taken. “We wanted to be open with families about what has happened, while also reassuring you that there is currently no evidence that the information has been accessed or misused and that a number of steps have now been taken to prevent access to the affected photographs and reduce the risk of a similar incident occurring again.” ®
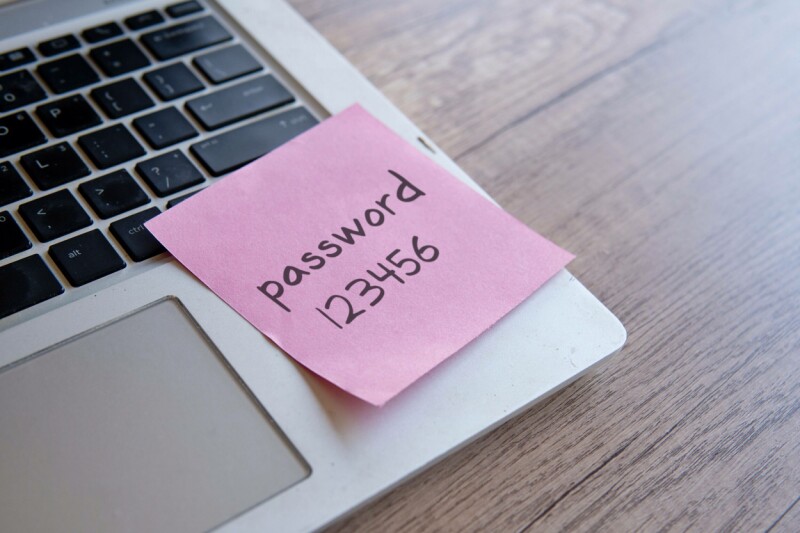
Change is constant, but The Register likes to keep some things the same – such as using Friday mornings to bring you a new installment of On Call, the reader-contributed column that shares your tech support stories. This week, meet a reader we'll Regomize as "Daniel" who told us that in 2020 he was hired to replace a two-person IT department at a UK school. "The IT manager had left amid some 'accounting irregularities,' mainly involving high-end gaming PCs being purchased using school funds but never making it onto the school site," Daniel told On Call. "His deputy stepped up just in time to have to deal with a ransomware attack that took the school's entire network offline for three months." The school eventually hired external contractors to rebuild the network and restore from the only available backup, which was months old. The deputy IT manager then quit without serving their notice period. Daniel took the vacant job and in his first week the school principal asked him to audit the network and deliver a report explaining how to get things up to scratch. "I found a few quick wins, including the password policy which at the time was set to six letters. Just that, no complexity, no expiry," Daniel told On Call. "And users hadn't been forced to change them since before the ransomware attack. Or, indeed, ever." The principal approved Daniel's proposed password policy and a requirement for everyone to change their password immediately. "I was not prepared for the backlash this would create," Daniel wrote. The school's data manager proudly said she had used the same password since 1998 and justified keeping it on the grounds that everyone on staff knew it. "She said, 'If I'm not in, they can log in as me and run the reports.'" It gets worse: the password was "letmein" and the data manager had written it on a piece of paper and taped it to her desk. As Daniel rolled out the new password policy, more complaints rolled in. The school principal eventually told Daniel to direct all enquiries regarding the password changes to him. "Within two days, he came into my office, sighed, put his head in his hands, and ordered me to revert the change and to remove the requirement for everyone to change their password," Daniel wrote. "I resisted, I really did," he wrote. "But it was his school. I got him to put the request in writing." The principal left three months later, and a nonprofit took over the school. Daniel's new bosses agreed with his stance and reinstated his password policy. The data manager again fought the change. "After a meeting with me and the nonprofit's IT director, she decided to take early retirement, so she wouldn't have to learn the new systems – or change her beloved password." Have management or users rejected your advice? Click here to tell us what happened, and your story could appear in a future edition of On Call. ®
Security researchers warned about exploitable vulnerabilities in refrigeration controllers months - and in one case, more than a year - before cyberattacks disrupted hundreds of French supermarkets. Late Sunday night, unknown criminals hacked thousands of controllers, cranking the heat as high as 122°F (50°C), spoiling food and sparking fires across nearly 700 of the country’s supermarkets. France's national cybersecurity agency ANSSI on Monday warned of widespread compromises involving Danfoss refrigeration controllers, and a day later added affected systems from Copeland and its Dixell brand. The compromised devices were accessible over the internet, with many reportedly no longer receiving software or security updates and others running outdated firmware. Danfoss did not immediately respond to The Register’s request for comment. Copeland emailed us the following statement: “We acknowledge the vulnerability identified in a discontinued, end-of-life generation of controllers. Protecting our customers’ operations has always been a top priority. We are currently working with impacted customers to mitigate the risk. We will continue to support customers in strengthening cybersecurity through supported products, current software and industry-recommended practices.” Operational technology (OT) security firm Claroty’s Team82 sounded the alarm on these buggy devices in August, warning that hackers could “freeze the controller” and “defrost the food.” At the time, the researchers published details of dozens of vulnerabilities, including authentication bypass and operating-system command execution flaws, affecting Danfoss AK-SM 800A and Copeland XWEB controllers. Even earlier, the US Cybersecurity and Infrastructure Security Agency (CISA) published advisories about security flaws in both brands’ controllers. In February, CISA said nearly two dozen CVEs in Copeland XWEB and XWEB Pro could be exploited to “allow an attacker to bypass authentication, cause a denial-of-service condition, cause memory corruption, and execute arbitrary code.” In a May 2025 advisory, updated in August 2025, CISA published a similar warning about buggy Danfoss AK-SM 8xxA series devices. “What makes this incident particularly striking is the timeline,” Tiago Henriques, chief underwriting officer at cyber insurance provider Coalition, told The Register. He noted that the French supermarket hacks happened two months after Team82 published its research, and Danfoss released a firmware update (R4.3.1) to mitigate the flaws. 'Critical exposure' continues “Yet, despite the availability of these patches, Coalition’s scanning identified critical exposure to these threats continuing well into the fall,” Henriques said. Between September 7 and October 6, Coalition’s sensors identified 1,506 unique IP addresses still publicly exposing a Danfoss StoreView web-accessible admin panel, and 820 of these - 54 percent - were associated with French networks. “Our scans counted at least 2,624 refrigeration controllers from the named brands with a login page open to the internet: 1,506 Danfoss StoreView and 1,119 XWEB,” he added, noting that one IP runs both types of controllers. To be clear: this doesn’t mean all of these controllers were vulnerable, but rather they were exposed to the open internet. Even after the cyberattacks - as of Thursday - 618 Danfoss devices remain connected to the internet, according to the insurance provider’s count. Of these, 206 are connected to French networks, while 50 are in the US, and two in the UK. “An unpatched device featuring a web-accessible admin panel can act as a major entry point” for digital attackers, Henriques said. “The takeaway is clear: digital risk extends far beyond workstations and email servers.” Criminals are targeting OT and other industrial devices that are connected to the internet, too. “Identifying these exposed access points before they are targeted can directly contribute to preserving business continuity,” Henriques said. OT cyber leaders call for CISA directive In America, a group of OT cybersecurity and technology providers doubled down on their call for stronger food and agriculture protections in the US. The French cyberattacks “are another stark reminder of the importance of implementing baseline cybersecurity measures to enhance operational technology cybersecurity,” the Operational Technology Cybersecurity Coalition (OTCC) said in a Wednesday statement. Earlier this month, the group, whose members include Claroty, Forescout, Honeywell, and Schneider Electric, called on CISA to issue a Binding Operational Directive to improve OT cybersecurity within the federal government. The OTCC repeated this demand on Wednesday and suggested that the US Department of Agriculture could encourage organizations in the food and agriculture sector to implement cybersecurity best practices. “While no incidents have been reported in the United States, malicious actors are undoubtedly viewing this incident as a potential attack vector to perform here,” the statement said. “We cannot wait for that to happen.”®
The online advertising industry has found a new way to make itself even more unpopular, with one adtech outfit accused of helping spyware vendors infect people's phones without them even clicking an ad. Researchers at Citizen Lab say they've uncovered the first publicly confirmed case of a zero-click mercenary spyware attack being delivered through targeted online ads, with devices at Al Jazeera among those infected. The technique, dubbed "AdFection," turns advertising networks into a spyware delivery system. Simply opening a website or app can be enough to trigger the attack, with no suspicious links or downloads involved. Israeli adtech firm Discover-Tech is allegedly behind the operation, according to researchers at Citizen Lab, which says the company acts as a middleman between the online advertising industry and multiple spyware and hacking vendors. "We present technical evidence that the Israel-based company Discover-Tech, while purporting to be a legitimate advertising company, appears to be a front for large-scale ad espionage abuse," the researchers wrote. “In fact, it appears that serving as this bridge is Discover-Tech’s primary purpose." Discover-Tech’s Controlium platform exploits the real-time bidding system that decides which ads appear on websites and apps. Every time someone loads a page, advertisers compete for available ad space and, in the process, receive information about the user's device and location. Discover-Tech allegedly used that data to identify specific targets and serve them malicious ads. One spyware vendor linked to the operation is Candiru, the Israeli developer now known as Integrity Labs. Citizen Lab traced attacks against at least 45 devices at Al Jazeera in 2024 and 2025 to Candiru spyware delivered through ads from Discover-Tech. Discover-Tech didn't have to sneak into the advertising system, as Google and IAB Europe had listed the company as an approved vendor since 2020, apparently unaware of what it was Citizen Lab claims it was doing with that access. Citizen Lab sifted through nearly four billion ad-bidding records and found Discover-Tech ads on more than 70,000 mobile apps and 120,000 websites between March and June 2026. Some reached networks belonging to government agencies, defense organizations, and NATO. Researchers found no evidence that those organizations were infected, but they say the ads could have been used to profile devices on those networks. The researchers said the operation also covertly directed millions of devices toward servers associated with Candiru, although those connections don't necessarily indicate spyware infections. Google has since terminated Discover-Tech's access to its advertising exchanges and removed it from its approved vendor lists. IAB Europe followed suit, while Beeswax, Vungle and Eskimi also took action. Discover-Tech and Candiru did not respond to Citizen Lab's requests for comment, nor ours. The researchers argue that the findings expose serious failings in an advertising industry that allowed a company with links to commercial surveillance operators to operate inside its supposedly vetted ecosystem for years. “Discover-Tech’s mass abuse, privacy invasion, and facilitation for mercenary spyware attacks illustrates structural flaws with the online advertising system, which failed to detect or prevent the abuse documented in this report,” Citizen Lab said. For years, the worst thing about targeted advertising was that it knew far too much about you. Turns out some advertisers were interested in much more than your shopping habits. ®

 Login