❌

Reading view

CISA Urges Immediate Ivanti Connect Secure Updates as Honeypots Log 105 Exploit Attempts

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday urged organizations to take steps to immediately update their Ivanti Connect Secure (ICS) appliances and deployments to the latest version following the disclosure of an actively exploited vulnerability. The security flaw, tracked as CVE-2026-104935 (CVSS score: 8.6), is a case of authentication bypass impacting ICS

  •  

curl Patches HTTP/2 Upload Flaw After PoC Demonstrates Client-Side Code Execution

A flaw in how curl handles HTTP/2 uploads lets a malicious server receiving an upload corrupt the client's memory, and the researcher who reported it turned that into code execution on the uploading machine. The curl project fixed it on October 14 in curl 8.23.0. Taking over a client needs exact knowledge of its build and memory layout, and curl expects a real attack to end in a crash

  •  

How to Run a Deepfake Readiness Drill Before a Cloned Voice Calls Your Team

Cloned voices and synthetic video calls now show up in payment fraud, help desk resets, and access requests. A structured drill shows security teams exactly where verification breaks down, while nothing is at stake. The call comes in at 4:40 on a Friday. It's the CFO, or it sounds exactly like her, asking the controller to push a supplier payment out before the weekend because a deal closes

  •  

Researchers Used a Public OpenAI Model to Build a $250,000 Chrome Full-Chain Exploit in Six Days

A team at security firm XBOW chained three then-unknown Google Chrome bugs into a single attack that runs code on a Windows computer when the user only loads a web page, the company said. Its researchers built the attack in six days by directing AI agents running OpenAI's publicly available GPT-5.6 Sol model. Google has since confirmed all three bugs, fixed them, and paid XBOW its top $

  •  

Hirudo Android Trojan Uses Patched Banking Apps to Bypass Their Built-In Security Checks

Cybersecurity researchers have disclosed details of a new Android banking trojan called Hirudo that works by replacing legitimate banking apps with purpose-built patched versions designed to bypass security checks from inside the app itself, marking a new escalation in financial fraud.  Dutch mobile security company ThreatFabric said it identified replacements for eight Indonesian banking

  •  

An AI Agent Found a Critical OTP Bypass in Production. The Attack Was the Easy Part.

The bug was simple: the login let you choose where your sign-in code went. Proving it on a live website was the hard part. TL;DR During an authorized assessment, an AI pentesting agent found a critical authentication bypass on a major insurer's production website, on its own. One login request let the user choose where the one-time passcode went. The attack was the easy part. Proving it

  •  

OpenAI engineer charged after boardroom bug found wrapped in toilet paper

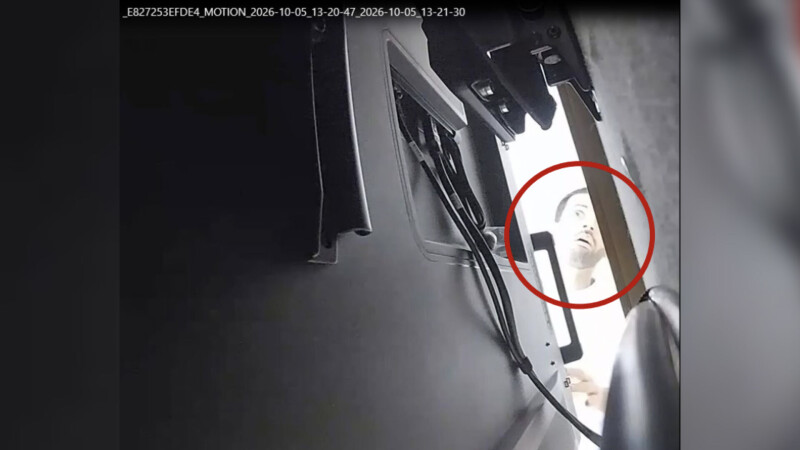
The Department of Justice has charged an OpenAI engineer with attempting to intercept oral communications after allegedly planting a recording device in an exec conference room. Investigators claim company security staff found a second device in his bag. Saudi national Abdulrahman Alfozan, 35, is described in court documents as an engineer at OpenAI who had worked there since July 2025, and has held permanent residency in the US since September 2020. He was arrested on October 9 and made his initial federal court appearance on October 13. He is accused of installing, on or around September 28, 2026, a Seeed XIAO ESP32-S3 Sense recording device via a USB port in a TV located in OpenAI's executive conference room. According to the complaint, staff discovered the device concealed in toilet paper on September 30. OpenAI said it used its models to analyze the device. According to the complaint, it may have been modified to prevent data transfer between the recorder and the TV. The contents of the bug's microSD card may also have been encrypted, as the company could not retrieve any of the data stored on the card after making a forensic image of it. CCTV footage placed him near the room on several dates, although prosecutors say Alfozan had no authority to access or participate in meetings held in the executive conference room, which is often reserved for the highest-level discussions. Officials did not state whether the device was able to capture anything of importance, but said the room typically plays host to non-public and secret technical meetings, as well as those with government representatives. OpenAI did not have CCTV covering the executive conference room at the time when the secret device was planted, but the company subsequently installed a camera. Court documents [PDF] include an image taken on October 5 from a camera situated behind the TV into which the DoJ claims the recording device was installed, allegedly showing Alfozan checking on it. Investigators examined Alfozan's devices, according to the complaint, which alleges that between around August 17 and September 16, 2026, Alfozan used a productivity agent to inquire about company building addresses, meeting rooms, room capacities and calendars, and external-partner meeting venues. The complaint also describes an AI chatbot account associated with his spouse that shared installation identifiers, logged IP usage, and user-path references with Alfozan's account. Between September 24 and 30, it submitted prompts about building and modifying an audio-recording device. The prompts allegedly included questions related to recording reliability, how to add browser access and controls, how to develop a second unit with speech-triggered recording, and more. On October 5, the day Alfozan was allegedly recorded looking behind the executive conference room TV, company representatives say he left a bag unattended in the office's printer room. Security staff inspected the bag, finding a wallet, an ID card, and a second Seeed-manufactured recording device, before Alfozan reported the bag missing, according to the DoJ. He collected the bag the following day from the company's Lost and Found, and later claimed in a written report that several items were missing, including a credit card, around $500 in cash, two AirPods, one set of headphones, sunglasses, and a power bank. Alfozan was charged with an attempt to intercept oral communications, an offense that carries a maximum sentence of five years in prison and a $250,000 fine. "According to the complaint unsealed today, Abdulrahman Alfozan allegedly concealed a covert recording device inside his employer's executive conference room to secretly capture sensitive communications about the company's super intelligence technology," said FBI director Kash Patel. "Protecting American SI innovation is essential to safeguarding our nation's economic strength and national security, and the FBI views that mission as one of our highest counterintelligence priorities." "At this time, we have no indications of this individual inappropriately accessing or exfiltrating model weights, source code, or customer data," OpenAI said in a statement. "The employee was terminated." "We take protecting our technology, data, and people seriously, and as a matter of national importance. Our security program is designed to protect against a wide range of threat actors, from insider risks to cybercriminals to nation states, and this case is an example of how AI can help address these sophisticated security threats." ®

  •  

AI-Found Linux Kernel Flaw Gives Local Users Root, and Can Break a Guest Out to the Host

A flaw in Linux's vhost subsystem lets a local user read and write kernel memory at will and become root across nearly a decade of kernel versions. In one virtualization setup, it lets an untrusted virtual machine write to the host's memory and hijack the program that runs the virtual machine. The bug is tracked as CVE-2026-74580 and named Vghost. Tencent Zhuque Lab, which found the

  •  

Four-Byte Write and Timing Bug Let Researchers Run Code in Windows SmartScreen Enclave

Security researchers ran their own code inside a protected part of Windows that is meant to stay sealed off even when the rest of the computer is taken over. The protected area is a VBS enclave, an isolated slice of memory the operating system uses to guard secrets, and the one they broke into handles passwords for a Windows anti-phishing feature. The work was done in a lab as a proof of

  •  

Ransomware gets personal: 'We-know-where-you-are kind of stuff'

Tim Beasley, a senior incident response consultant at Semperis, was investigating a cyberattack involving Russia’s Midnight Blizzard when a package containing nesting dolls and other regional gifts showed up on his doorstep. At the time, Beasley served as the lead investigator for Microsoft’s Detection and Response Team (DART). He assumed it was from the group, which has been linked to the Kremlin’s Foreign Intelligence Service (SVR), although the sender didn’t leave a note. “Just little souvenirs and gift basket stuff from that area of the world,” he told The Register. “We-know-where-you-are kind of stuff. It’s a real eye-opener when you get that type of thing.” While digital intrusions having physical consequences is nothing new, cybercriminals in recent years have turned to real-life harm and mental and physical trauma to force victims into paying extortion demands. Some groups even use cybercrime as a gateway drug to real-life violence. Over the summer, Europol and its partners' investigators flagged 4,340 “horrific” URLs for removal as part of an ongoing crackdown on The Com (short for community), a loosely knit network of online groups whose young members participate in a range of illicit activities including hacking, swatting, digital extortion, real-life shootings, and other physical violence. “We’ve seen violence as a service get used,” Beasley said. He’s also investigated ransomware attacks where C-suite executives receive pictures of their kids’ schools directly from the cybercriminals in an attempt to apply psychological pressure to pay the extortion fee. “I've seen threats involving people's families, from social media reconnaissance, and in our world you more and more come to expect it, which is unfortunate,” Beasley said. This type of psychological intimidation and harm against victim companies’ employees has seen an uptick in the last several years to the point where it's almost common. Thirty-seven percent of ransomware attacks involved psychological or physical threats against staff, according to Semperis’ annual ransomware risk report. The global study of 1,200 post-ransomware organizations conducted over the first half of the year found attackers threatening psychological intimidation (23 percent) and physical threats (17 percent), to force payment. They are not only targeting executives and staff, but also families of their victims. A quarter of these victims experienced doxxing – posting individuals' personal details, such as names, home and work addresses, and phone numbers online – while another 25 percent had to seek psychological and/or medical treatment in response to ransomware infections. Nearly the same number (24 percent) hired personal security teams, while 23 percent experienced swatting calls – that's when attackers phone emergency services and report a bogus incident like a bomb or active-shooter threat to trigger an armed response. Additionally, more than half (53 percent) of respondents reported that ransomware attackers carried through on threats in the past year. Some of these threats reported by ransomed organizations’ employees include: threatening texts, letters, or packages: 57 percent threats against family or friends: 37 percent physical intrusion: 19 percent abduction: 17 percent bodily harm: 13 percent stalking: 6 percent. “It's the more well-known groups,” using psychological and physical threats to force payments, Beasley said. “I've seen Scattered Spider, I've seen ShinyHunters, I've seen Lapsus$.” For what it's worth, ShinyHunters claimed in an exclusive interview with The Register that they “don't attack human beings.” They did, however, admit that “there are times in the work we do sometimes we have to push the corporate to the absolute limit to get them on the table.” The takeaway for defenders and executives from this report is to “stand your ground,” Beasley said. “Don’t buckle under the pressure, and just know that you know it's going to be okay. If you feel like you're under duress, then by all means get law enforcement involved. Don't be afraid to call the cops. Don't be afraid to get the FBI involved, sooner rather than later. And don’t pay them.” This last piece of advice is important, as once you pay, they're going to come back for more. Semperis’ report found that 69 percent of surveyed ransomware victims were targeted multiple times within the past 12 months, and 31 percent made multiple payments to attackers. “Don’t pay anything,” Beasley said. “Never pay them.”®

  •  

Microsoft Patches Record 1,413 Flaws, Including Exploited Windows Shell Bug

Microsoft on Tuesday shattered its own Patch Tuesday record by shipping patches for a whopping 1,413 vulnerabilities, including one that it said has come under active exploitation. These include 1,102 flaws in Windows, 134 in Office, 61 in Developer Tools, 36 in SharePoint Server, and 22 in SQL Server. Of these, more than 670 relate to privilege escalation, followed by over 300 remote code

  •  

OpenAI Employee Arrested for Allegedly Planting Hidden Recorder in Executive Conference Room

A Saudi national and employee of OpenAI has been arrested for allegedly planting a hidden recording device in an executive conference room at the company's San Francisco offices to covertly record sensitive conversations. Abdulrahman Alfozan, 35, has been charged with using or endeavoring to use an electronic, mechanical, or other device to intercept oral communications. He was arrested by

  •  

Microsoft Patches More Than 1,400 Security Flaws

Microsoft today issued updates to fix more than 1,400 security vulnerabilities in its Windows operating systems and other software. Today’s epic patch batch dwarfs September’s record of nearly 1,000 fixes, which was already about ten times the normal monthly patch load from Redmond.

Just one of the weaknesses patched this week is considered a “zero day,” or already exploited in the wild. CVE-2026-96951 is a security feature bypass in the Windows Shell that affects Windows 10 and 11 systems, as well as some Server versions.

Windows 10 users might be wondering if they can still expect security updates after this month. Microsoft had been slated to stop shipping updates for Windows 10 systems in October 2025, but ended up adding another year of free updates after considerable pushback. A few months ago, Microsoft quietly extended that support for another year (until October 2027).

At least 78 of the flaws fixed this month are rated “critical,” meaning they could be exploited with little or no action by the user, and most of those critical bugs allow an attacker to execute code of their choice on the vulnerable system.

While Microsoft said there are no signs anyone is exploiting it yet, a security feature bypass in the .NET Framework (CVE-2026-108398) was publicly disclosed prior to today, potentially giving attackers advance time to work out how to exploit the bug.

Satnam Narang at Tenable said the number of flaws fixed this month far surpasses the previous record-setting year 2020, when Microsoft patched 1,261 CVEs.

“We’ve now crossed the 4,000 CVE mark with two months left to go,” he said.

Microsoft credits large language models for the high volume of bug discovery, and presumably AI gets credit for many of the patches used to fix these flaw. Meanwhile, security experts have been warning that these unusually large patch volleys from Microsoft are placing extra strain on corporate security teams, which often have to test individual updates before deploying them across a network to ensure the fixes don’t cause problems for other software.

Tyler Reguly, associate director of security research and development at Fortra, notes that just 26 Microsoft vulnerabilities appeared in the “Known Exploited Vulnerabilities” (KEV) catalog maintained by the U.S. Cybersecurity & Infrastructure Security Agency (CISA) so far this year, and security teams would do well to prioritize patching those 26 vulnerabilities first.

“Security leaders should focus on exploitable risk, and ask whether their teams have the clarity, capacity and support to act,” Reguly said.

Which vulnerabilities deserve the most scrutiny in your organization? The folks at Cisco Talos have a useful roundup of the more noteworthy flaws that Microsoft fixed today, and of course the SANS Internet Storm Center has a reliable roundup that indexes vulnerabilities by severity, CVE number and affected software.

  •  
❌