 Login

Sender spoofing in Proton Mail via display-name homograph
Proton Mail confirmed and paid for an email-spoofing bug, then left it unfixed for 16 months
[link] [comments]

Proton Mail confirmed and paid for an email-spoofing bug, then left it unfixed for 16 months


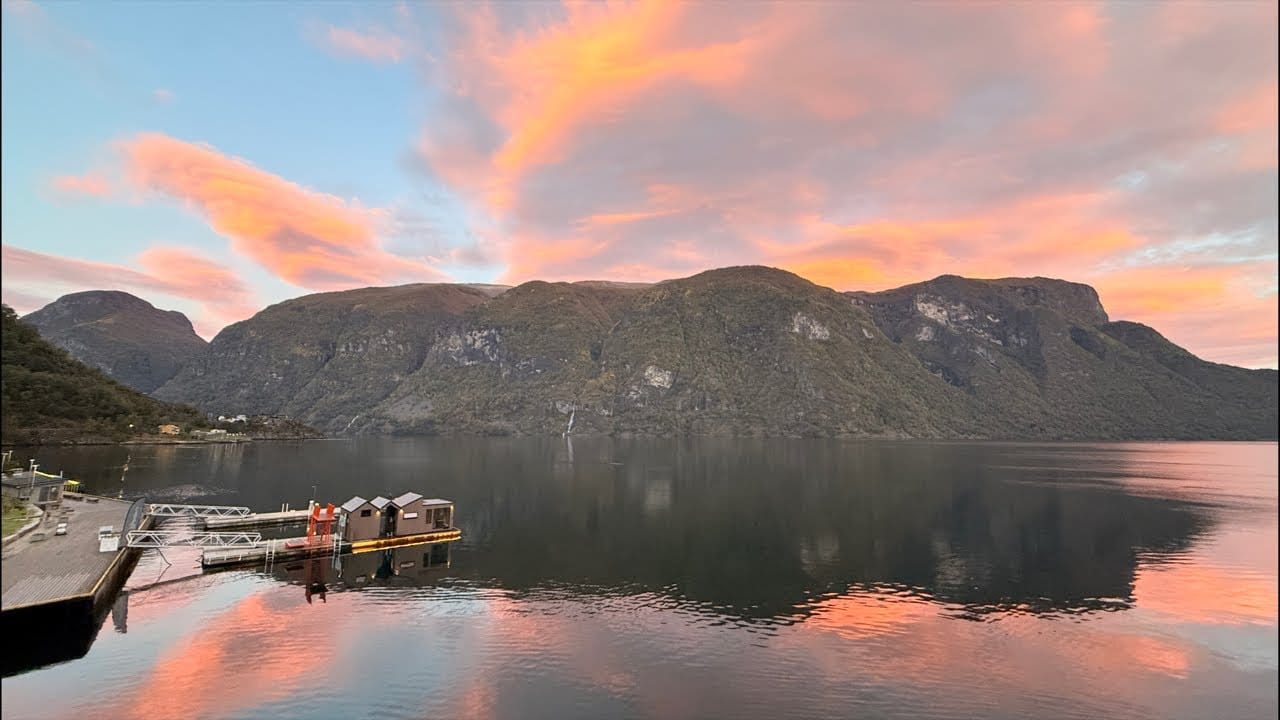
How's that view?! With NDC Oslo now done, it's a little bit of sightseeing before heading to Denmark for GOTO in Copenhagen for Scott's and my "Cyber-broken" talk. In the meantime, this week is mostly about the ShinyHunters trajectory targeting both Cl0p and the FBI, which does feel a little like a crescendo in their activities. Time will tell, but poking the feds in this way doesn't seem great for your longevity.
In my disorganised travel state, I also forgot to touch on a brand new sponsor for this week and the weeks to come: Origin. They build tooling to monitor what your AI agents are doing, which is obviously pretty timely given the current climate. They're running a free CISO briefing on 1 Oct, so go check that out if you think maybe your agents might need some oversight.



Unlike traditional approaches, console named-pipe injection does not use VirtualAllocEx and WriteProcessMemory. Instead, it takes advantage of read and write operations through a named pipe, along with the way console programs store interactive commands in memory.
GET-only egress to full code execution: chaining a URL mirror and a screenshot service
A technical audit evaluating the security defaults of 15 official Helm charts used for AI serving, vector databases, and Model Context Protocol (MCP) agents (including KubeRay, vLLM, LiteLLM, Qdrant, Weaviate, and Flux159 MCP).
Key findings from static manifest analysis and live single-pod lateral movement probes on a test cluster:
The paper documents reproducible test commands, network capture logs, and remediation Helm snippets. Scrubbed raw probe logs and results tables are available on GitHub: https://github.com/Sorami-Consulting-AU/ai-kubernetes-helm-chart-security
We scanned 7,040 randomly sampled U.S. local-business directory listings and graded the response headers against a published rubric. Of the 4,688 live sites, 49.7% met none of seven header criteria, and 8 sites (0.17%) passed a strict header-only script-CSP rule. Rubric, parser rules, code and de-identified data are all on the page.


