A data breach doesn’t have to expose your password or credit card number to create problems. Sometimes, scammers just need enough information to make you believe they know you.
That’s the concern after data reportedly stolen from Carhartt was published online. Here’s what happened, why it matters, and what consumers should watch for next.
What Happened in the Carhartt Data Breach?
The cybercriminal group ShinyHunters published data it claims was stolen from Carhartt after an alleged $3.3 million extortion demand was rejected, according to TechRadar. Security researcher Troy Hunt analyzed the leaked information and determined that the compromised data was associated with roughly 12.9 million accounts, although the dataset also reportedly contained millions of synthetic records that did not correspond to real people.
For affected consumers, the important part is what was reportedly exposed: names, email addresses, phone numbers, and postal addresses.
This is also a useful example of how cyber extortion has evolved.
Traditional ransomware typically involves criminals getting inside an organization, encrypting its files so they can’t be accessed, and then demanding payment to restore them.
In this case, the reported strategy was different. ShinyHunters has increasingly focused on data exfiltration — security jargon for stealing or copying data out of a system — and then using the threat of publishing that information as leverage.
In plain English: Criminals don’t necessarily need to lock up a company’s computers anymore. Stealing its data can be valuable enough.
How Scammers Might Use This Information
The immediate question after any breach is usually, “Was my financial information stolen?” That’s important, but it isn’t the only risk.
A combination of your name, email, phone number, and home address can help scammers create a message that sounds much more believable than generic spam.
Instead of: “There’s a problem with your account. Click here.” you could receive something that appears to know your name, where you live, or which company you’ve done business with.
That context can lower your guard.
And scammers don’t necessarily have to pretend to be Carhartt. Stolen contact information can potentially be combined with information from other breaches, data brokers, or public sources to build a more complete picture of someone.
That’s why leaked personal information can remain useful to criminals long after the original breach disappears from the headlines.
Key Takeaways
Personal information can be valuable to scammers even when passwords or payment information aren’t exposed.
Names, emails, addresses, and phone numbers can make phishing attempts more personalized.
Be particularly cautious of unexpected messages claiming there is a problem with an order, refund, account, or payment.
A company knowing personal details about you is not proof that the person contacting you actually represents that company.
How McAfee Protects Against Breaches
Before a breach
Personal Data Cleanup reduces your digital footprint by removing your personal information from many data broker sites, making it harder for scammers to find and target you.
Online Account Cleanup scans for accounts you no longer use and helps you delete them, along with your personal info.
During a breach
Identity Monitoring watches for your personal information, including email addresses, driver’s license numbers, passport numbers, bank accounts, credit cards, Social Security numbers, phone numbers, and more, across the dark web and known data leaks.
Plus, we alert users on average up to 10 months earlier than similar services, so you can act fast when your personal information appears where it shouldn’t.
After a breach
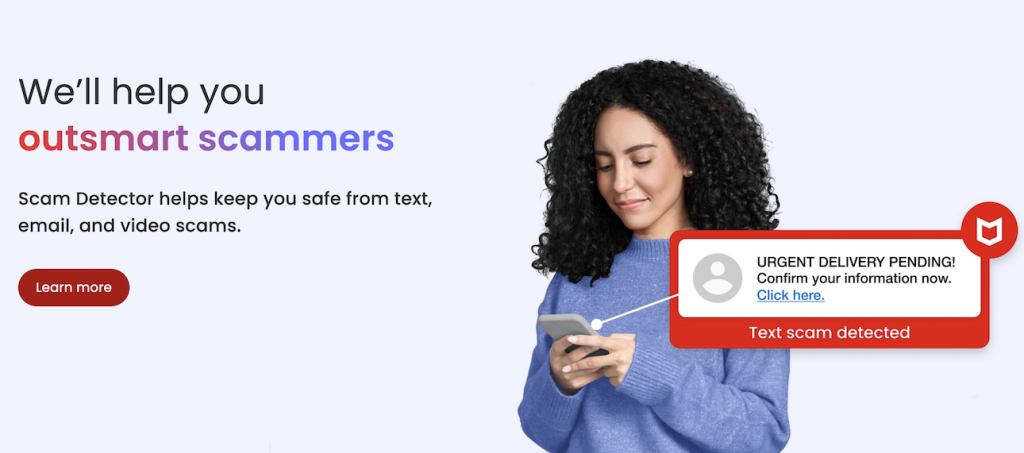
Scam Detector identifies suspicious texts, emails, and links that often follow major breaches, while web protection blocks malicious websites designed to steal even
Other Scam and Security News This Week
A Lenovo Login Flaw Exposed About 5,000 Dropbox Accounts
Dropbox says approximately 5,000 accounts were accessed after attackers exploited a flaw involving Lenovo ID authentication; fewer than a third reportedly had files viewed or downloaded. Dropbox has expired sessions authenticated through Lenovo IDs and changed the login process, while the incident is another good reason to enable two-factor authentication on cloud accounts. Sources: BleepingComputer
Amazon Adds a New Way to Check Suspicious Messages
Amazon has added a feature to Alexa for Shopping that lets U.S. customers ask whether an email, text, phone call, or other message actually came from Amazon; the company says roughly 360,000 customers contact customer service each year with that question. It’s a useful reminder of one of the best scam-fighting habits: instead of trusting the message in front of you, verify it through a separate, official channel. Sources: TechCrunch
Fake Late-Night TV Clips Show How Easily AI Can Borrow Someone’s Credibility
NPR reports that AI-generated videos impersonating late-night hosts including Jimmy Kimmel and Jon Stewart have accumulated significant audiences online, sometimes without obvious AI labels. The bigger consumer lesson goes beyond politics or entertainment: seeing a familiar face and hearing a familiar voice is no longer enough to prove that a video — or the product, investment, or claim it promotes — is authentic. Source: NPR
This Week’s Safety Tips
✓ Treat unexpected personalization as information, not proof. A caller knowing your name, address, or other details doesn’t mean they’re legitimate.
✓ Turn on two-factor authentication. This can provide another barrier when someone tries to access an account without permission.
✓ Verify messages outside the message itself. Open the official app, type the website yourself, or contact the company using information you independently know is legitimate.
✓ Slow down when something feels urgent. Whether it’s a breach alert, delivery problem, suspicious login, or celebrity video, scammers benefit when you react before you verify.
And we’ll be back next week with more cybersecurity news and scam alerts.
Labor Day weekend means sales. And if you spend any time on Facebook, Instagram or TikTok, some of the biggest discounts may find you before you even start shopping.
That convenience comes with a catch: Not every deal in your feed is really from the brand it appears to be.
Scammers can create polished social media ads that impersonate familiar retailers, advertise steep discounts and send shoppers to convincing lookalike websites. According to the Federal Trade Commission, nearly 30% of people who reported losing money to a scam in 2025 said that it started on social media. And the reported losses hit a whopping $2.1 billion last year.
So before a Labor Day “80% off” deal stops your scroll, give it a second look.
How Fake Social Media Shopping Ads Work
A fake shopping ad often starts with something completely ordinary: a product you actually want.
Maybe it’s sneakers from a familiar brand. Patio furniture you’ve been researching. A handbag, grill or appliance marked down for Labor Day.
The ad may use the real company’s logo, product photography and branding. Click it, and the website can look remarkably similar to the retailer’s actual site.
That’s the trick.
This is a form of brand impersonation: A scammer copies the appearance of a company people already know and trust. Instead of convincing you to trust an unfamiliar store, the scammer borrows the reputation of a familiar one.
Sometimes these ads lead to completely fake storefronts. Other times shoppers receive counterfeit products, something dramatically different from what they ordered or nothing at all.
The FTC recently warned consumers specifically about social media ads advertising brand-name products at unusually low prices. And the problem isn’t limited to one platform. A convincing ad can reach you wherever you scroll.
Here’s an example of a scam Louis Vuitton website previously detected by McAfee. Users get an ad on social media, and land on a realistic-looking shopping site. But it’s not the real vendor.
She Thought She Bought $800 Patio Chairs for $135
One shopper who shared her story with McAfee learned just how convincing these scams can be.
A few years ago, Jen was scrolling through Facebook when she spotted an ad for the exact Wayfair patio chairs she and her husband had been considering. Normally around $800, the chairs were advertised at 80% off — just $135 with free shipping.
She clicked.
The experience looked enough like Wayfair that she continued with the purchase, even though a few things started to feel strange. A new tab opened when she tried to buy the chairs. The checkout mentioned PayPal even though she was using her credit card. Then she learned the order would be shipping from China and could take six to 12 weeks.
When she checked her credit card, the charge wasn’t from Wayfair. It appeared in Chinese characters.
Weeks later, a package finally arrived.
It wasn’t a set of patio chairs. Inside the small package was a ceiling-fan chain with a cheap ring.
Her credit card company eventually reversed the charges. But the experience illustrates something important about fake shopping ads: You don’t necessarily land on an obviously fake website filled with misspellings and broken images. A scammer’s goal is to make the experience feel normal long enough for you to complete the purchase.
7 Signs a Social Media Ad or Shopping Site Could Be Fake
Before buying something you find through Facebook, Instagram, TikTok or another social platform, look for these warning signs:
1. The discount is dramatically better than everywhere else.
A legitimate sale can be generous. But if one ad offers a popular $800 product for $135 while reputable retailers are nowhere close, investigate before buying.
2. The website address doesn’t match the retailer.
A fake site can copy a logo much more easily than it can copy a company’s official domain. Look carefully for extra words, misspellings or unusual endings in the web address.
3. Clicking takes you somewhere unexpected.
Watch for redirects, new tabs or checkout pages on a different domain. A change doesn’t automatically mean fraud, but it’s a reason to verify where you are before entering payment information.
4. The checkout process feels off.
Pay attention when the payment method, merchant name or checkout experience doesn’t match what the site told you to expect.
5. There’s pressure to buy immediately.
Countdown timers and “only two left” warnings can push you to act before checking the seller. Urgency is useful to scammers because it shortens the time you spend thinking.
6. You can’t independently verify the sale.
Open a new browser window or the retailer’s official app and search for the product yourself. If the incredible sale exists only through the social ad, that’s a warning sign.
7. The merchant on your credit card doesn’t match the company you thought you paid.
Check the transaction after buying. An unfamiliar merchant name or unexpected international charge deserves immediate attention.
The Safest Way to Shop a Deal You See on Social Media
Here’s a simple safety checklist for Labor Day weekend:
✓ Leave the social app and find the retailer yourself. Don’t let the ad choose your destination.
✓ Compare the price elsewhere. A discount that’s wildly out of line with other retailers deserves extra scrutiny.
✓ Check the URL and merchant name. Make sure you’re dealing with the company you think you’re dealing with.
✓ Use a credit card when possible. And save screenshots, receipts and order confirmations in case you need to dispute the purchase.
What If You Already Bought Something From a Fake Ad?
Act quickly, but don’t panic.
Save screenshots of the ad, website, receipt and any emails or messages from the seller. Check your credit card or bank statement to see how the transaction appears.
If you believe the purchase was fraudulent, contact your card issuer or financial institution and explain what happened. Ask about disputing the transaction and whether your card information should be replaced.
If you created an account on the fake website and reused a password you use elsewhere, change that password anywhere you’ve used it. Unique passwords matter because a scammer who captures one password may try the same email-and-password combination on other accounts.
You can also report fraudulent ads to the social platform and report the scam to the FTC.
How McAfee Helps You Shop More Safely
Spotting every fake yourself is getting harder. Scammers can copy legitimate branding, product photos and storefront designs closely enough that a quick visual check isn’t always enough.
McAfee Scam Detector can help identify suspicious links, messages and websites and alert you when something may be a scam. Plus it has social media tools to help detect scams originating from your favorite platforms. That can provide another check when an attractive offer lands in a social message or sends you toward a questionable site.
Web Protection can also help warn you about risky websites as you browse, adding protection at the moment a convincing ad tries to move you away from the social platform and onto a malicious destination.
The goal isn’t to stop shopping the sales you see online. It’s to make sure the store getting your money is the store you intended to pay.
Free airport Wi-Fi can be useful when you’re waiting for a flight. But this week’s biggest security story is a reminder that there are two different ways your information can be exposed when you connect.
One risk happens while your information is traveling across a public network. Another happens after a company collects and stores information about you.
A cyberattack affecting three major UK airports illustrates the difference, and why travelers need protection for both.
What happened in the Manchester Airports Group cyberattack?
Manchester Airports Group, or MAG, confirmed that an unauthorized third party obtained customer information connected with Manchester Airport, London Stansted Airport, and East Midlands Airport.
According to reports, the affected information came from car park, airport lounge, Fast Track bookings, and airport Wi-Fi registrations. MAG says the stolen data includes email addresses, phone numbers, vehicle registration numbers, and postcodes. The company says the affected system did not contain customers’ payment or banking details.
The Telegraph reported that approximately 8.7 million passengers were affected and that more than 90% of the stolen records were email addresses, largely because travelers provide an email address when registering for free airport Wi-Fi. The attackers reportedly demanded a ransom, which MAG declined to pay.
MAG says airport operations and passenger safety were not affected and that it has contained access to the compromised systems.
For travelers, however, the breach creates another concern: what criminals might do with the stolen information next.
Why stolen airport data can lead to convincing scams
An email address alone might not seem particularly sensitive. But combined with a phone number, postcode, vehicle registration, or knowledge that someone has interacted with a particular airport, it becomes more useful to a scammer.
That information can help criminals make phishing emails and texts feel believable.
A message might claim there is a problem with your airport parking reservation, ask you to confirm a Fast Track booking, or say you need to pay an outstanding airport charge. Someone who recently used the airport may be much more inclined to click.
That is one reason breach victims should be especially cautious about unexpected messages that appear connected to the organization involved.
Does a VPN protect you from an airport Wi-Fi data breach?
Not from this kind of breach.
A VPN, or virtual private network, encrypts the internet traffic traveling between your device and the VPN service. Think of it as putting your online activity inside a protected tunnel while it crosses a public network.
That matters at airports, hotels, cafés, and other places where many people share the same Wi-Fi. McAfee Secure VPN can encrypt your connection and can be configured to turn on automatically when you join an unsecured network.
But that is different from what happened here.
If you voluntarily give an airport your email address to register for Wi-Fi, that email address may then be stored in the airport operator’s systems. A VPN cannot prevent a later breach of that company’s database.
In short: A VPN helps protect information in transit. It does not control what happens to information you give directly to a company.
Both risks matter.
Before, During, and After a Data Breach
Before a breach: Share only the information a service genuinely requires. Use strong, unique passwords for online accounts, and use a VPN when connecting to public Wi-Fi.
During a breach: Look for information directly from the affected company rather than relying on messages arriving by email or text. Criminals often take advantage of security incidents by sending fake “account protection” or “verify your information” messages.
After a breach: Watch for unusual emails, calls, texts, and account activity. Be particularly suspicious when someone creates urgency or asks for passwords, verification codes, payment information, or money.
MAG specifically warns that it will not unexpectedly contact customers asking for payment card information, banking details, or passwords.
At a Glance
The breach affected customer information from bookings and airport Wi-Fi registrations.
8.7 million passengers were affected
MAG says banking and payment details were not stored in the affected system.
Stolen contact information can still make phishing and impersonation scams more convincing.
A VPN protects your connection on public Wi-Fi, but it cannot prevent a company from later suffering a database breach.
Be particularly cautious about unexpected airport-related emails and texts following the incident.
How McAfee Helps
Secure VPN helps address the other major risk associated with airport Wi-Fi: someone attempting to monitor your traffic while you use an unsecured network. McAfee Secure VPN encrypts your connection and can automatically activate on unsecured Wi-Fi, helping keep browsing activity and information transmitted from your device private.
Identity Monitoring keeps watch for your personal information associated with breaches, giving you an opportunity to act when exposed information is detected.
And because stolen email addresses and phone numbers can fuel follow-up phishing attempts,Scam Detectorcan identify suspicious texts, emails, and other QR codes before you act on them.
The broader lesson is layered protection: protect your connection while you’re online, then keep watching for misuse of information that companies already hold.
Other Scam and Security News This Week
Hackers claim breach of major data center provider. The ShinyHunters group claims it stole extensive corporate and employee information from U.S. data center company CyrusOne and demanded $13 million.
CyrusOne had not publicly confirmed the hackers’ claims when TechRadar reported the story, so the alleged scale of the breach remains unverified. Source: TechRadar
Man accused of posing as a 49ers player in $1.3 million romance scam. Federal prosecutors allege that two men defrauded at least 26 women after one portrayed himself online as a wealthy San Francisco 49ers player and the other posed as his financial adviser.
Investigators say fake banking apps and fabricated investment balances helped make the scheme appear legitimate; both defendants are presumed innocent unless proven guilty. Source: U.S. Department of Justice
Fake sports streams target fans looking for the game. The Better Business Bureau warns that scammers post supposed free streaming links on social media, sometimes tagging real schools or teams, then direct fans to sites designed to collect payment or personal information instead of showing a game.
Go to the team, school, league, or known streaming provider directly rather than trusting a link in a social post — and remember that HTTPS alone does not prove a website is legitimate. Source: Better Business Bureau
This Week’s Safety Tips
“Once you give your information to a company, you can’t completely control what happens to it,” says McAfee’s Tyler McGee. “But you can limit what you share and take steps to protect yourself if your information is exposed.”
“Only provide what’s needed, use unique passwords and turn on multi-factor authentication where you can. Tools like McAfee’s identity monitoring can also alert you if your information shows up in a known breach. And be extra cautious after a breach,” he says. “Scammers can use exposed information to make messages about a booking, refund or account look much more convincing. If you get one, go directly to the company’s website or app rather than clicking the link.”
✓ Use a VPN on public Wi-Fi. Encrypt your connection before checking email, shopping, banking, or signing into important accounts.
✓ Treat breach-related messages cautiously. Navigate to the company’s official website yourself rather than clicking a link in an unexpected email or text.
✓ Use unique passwords. A password stolen from one service should never unlock another account.
✓ Verify before sending money. Whether someone claims to be an athlete, investment adviser, streaming provider, or familiar company, independently confirm who you are dealing with.
And we’ll be back next week with more cybersecurity news and scam alerts.
A data breach doesn’t have to hit the company you shopped with directly to put your information at risk.
That’s the lesson from this week’s Pokémon Center breach. Customers in the United Kingdom and Germany are being notified that personal and order information was exposed after attackers compromised CEVA Logistics, the third-party company used to fulfill and ship Pokémon Center orders.
The good news: Pokémon Center says CEVA did not have access to customers’ payment-card information.
The bigger concern is what criminals could potentially do with the information that was exposed, particularly when it can make a phishing message look unusually convincing.
What Happened in the Pokémon Center Data Breach?
According to breach notifications reviewed by BleepingComputer, attackers may have obtained Pokémon Center customers’ full names, mailing addresses, phone numbers, email addresses, and information about the products they ordered. The affected customers were in the UK and Germany.
The intrusion occurred at CEVA Logistics rather than Pokémon Center itself. Reporting indicates attackers accessed CEVA systems between late July and August 1, disrupting operations at eight European warehouses and affecting multiple retailers. Valve previously notified European Steam hardware customers that their information had also been exposed through the CEVA incident.
Why Does Shipping Data Matter to Scammers?
A name and email address may not seem as sensitive as a credit-card number. But when criminals also know your address, phone number, and what you recently bought, they have something valuable: context.
Context helps scammers make phishing messages believable.
Phishing is when a criminal pretends to be a trusted company or person to persuade you to click a malicious link, hand over a password, share personal information, or send money.
After a breach like this, criminals could potentially impersonate Pokémon Center, a delivery company, or another retailer and reference details that make their message feel legitimate.
They might claim an order needs to be rescheduled, a delivery fee must be paid, or a refund is waiting. Knowing that you really placed an order can make the bait much harder to spot.
Importantly, there is currently no evidence that the stolen Pokémon Center information is being used in such a campaign. But personalized phishing is a common reason breached contact and transaction information deserves attention.
Key Takeaways
Pokémon Center says the breach occurred at its logistics provider, CEVA, not its own shopping platform.
Names, addresses, phone numbers, email addresses, and order details may have been exposed.
Pokémon Center says payment-card information was not available to CEVA.
Real order details could make future phishing or delivery scams appear more credible.
Customers should independently verify unexpected messages about refunds, cancellations, or deliveries.
3 Easy Safety Actions to Take If Your Information Is Exposed in a Data Breach
Getting a breach notification doesn’t necessarily mean someone has already misused your information. It does mean you should take a few steps to make that information harder to use against you.
1) Find out exactly what was exposed. Read the company’s breach notice carefully. An exposed email address calls for different precautions than a stolen password, Social Security number, financial information, or medical record.
2) Secure the accounts that could be at risk. Change any exposed or reused passwords, use a unique password for every account, and turn on multi-factor authentication where it’s available. If sensitive financial or identity information was stolen, consider a credit freeze or fraud alert as well.
3) Be extra skeptical of messages that know something about you. Breached information can help scammers create convincing emails, texts, and calls. A message that knows your name, address, recent purchase, or other real details isn’t necessarily legitimate. Go directly to the company’s website or app to verify unexpected requests rather than clicking a link or calling a number in the message.
How McAfee Protects Against Breaches
Before a breach
Personal Data Cleanup reduces your digital footprint by removing your personal information from many data broker sites, making it harder for scammers to find and target you.
Online Account Cleanup scans for accounts you no longer use and helps you delete them, along with your personal info.
During a breach
Identity Monitoring watches for your personal information, including email addresses, driver’s license numbers, passport numbers, bank accounts, credit cards, Social Security numbers, phone numbers, and more, across the dark web and known data leaks.
Plus, we alert users on average up to 10 months earlier than similar services, so you can act fast when your personal information appears where it shouldn’t.
After a breach
Scam Detector identifies suspicious texts, emails, and links that often follow major breaches, while web protection blocks malicious websites designed to steal even more of your information.
Other Scam and Security News This Week
FBI warns about callers impersonating federal agents. The FBI’s Boston Division is warning about scammers who spoof its real phone number, pretend victims are connected to crimes, and then try to move conversations onto encrypted messaging apps. The key reminder: caller ID can be faked, and the FBI says it will not call private citizens to demand payment, threaten arrest, or request sensitive information.
CareCloud breach grows to more than 3.75 million patients. Healthcare technology company CareCloud has confirmed with federal regulators that hackers stole personal and medical information belonging to more than 3.75 million people, including Social Security numbers, health information, government-issued ID numbers, and some financial data. Because medical and identity information cannot simply be replaced like a password, affected people should take breach notifications particularly seriously.
Hacker claims millions of corporate directory records were stolen. A cybercriminal known as “TheHatman” is offering databases allegedly taken from the Microsoft Azure and Entra environments of several major companies, although some named organizations dispute that their current systems were breached and say portions of the information appear old. Even older employee information can still be useful for impersonation and targeted phishing, so the claims are worth watching without treating every advertised dataset as independently confirmed.
✓ Treat unexpected delivery messages with caution. Open the retailer or carrier’s official app or website instead of following a link in a text or email.
✓ Don’t trust caller ID alone. Scammers can spoof a legitimate organization’s real phone number.
✓ Use unique passwords and multi-factor authentication. Stolen personal information becomes more dangerous when criminals can also get into your accounts.
✓ Pay attention to breach notices. Knowing exactly what information was exposed helps you recognize the scams criminals may try next.
And we’ll be back next week with more cybersecurity news and scam alerts.
Looking for a free download of this summer’s biggest movie could come with something you definitely didn’t ask for: malware.
Here’s what to watch for.
Fake The Odyssey Downloads Are Hiding Malware
Speaking of Trojan horses….
Security researchers have reportedly identified malicious downloads disguised as pirated copies of The Odyssey, including files designed to look like high-quality movie releases.
Some fake files even use familiar video-player icons and movie-style filenames to appear legitimate.
But instead of opening a movie, downloading or running the file can launch malicious software capable of stealing information from the device. Other scams reportedly use fake streaming sites that ask users to enter personal or payment information to access a supposedly “free” movie.
McAfee researchers routinely see cybercriminals attach malware to the things people are already searching for, especially popular movies, TV shows, games, mods, and software.
Infostealers designed to collect passwords, browser sessions, payment information, or cryptocurrency data
Trojans that give an attacker access to your device
Loaders that install additional malware
Fake browser updates or extensions that redirect you to scams or malicious websites
One especially obvious warning sign: movies should not arrive as executable .exe files. Legitimate video files generally use formats such as .mp4, .mkv, or .avi.
When in doubt, don’t download it.
How McAfee Protects Against Malware
With McAfee+, multiple layers can help protect you when a tempting download isn’t what it claims to be:
Device Security helps detect malicious apps, files, and downloads before they can compromise your device.
Web Protection helps block risky websites, including malicious download pages, even if you accidentally click.
Scam Detector flags suspicious texts, emails, links, QR codes, and other messages that may try to direct you toward fraudulent sites.
Identity Monitoring alerts you if your personal information appears in known data leaks or on the dark web so you can take action quickly.
Together, these protections help address both sides of fake-download scams: stopping malware before it gets onto your device and helping protect your information if criminals try to steal it.
Other Scam and Security News This Week
Here are some other breaches, scams, and cybersecurity headlines making waves this week:
Trezor breach reportedly exposes information belonging to nearly 14,000 crypto customers.
Hardware wallet maker Trezor says a breach involving one of its shipping providers exposed personal information including names, email addresses, phone numbers, and home addresses for thousands of customers.
McAfee’s 2026 State of the Scamiverse predicted that crypto and financial scams were likely to intensify this year, and cryptocurrency-related messages remain among the scams McAfee Scam Detector regularly identifies and blocks.
New threat research found organizations experienced an average of 2,336 cyberattacks per week in July, a 16% increase from the previous year, while reported ransomware victims also rose sharply. Education, government, telecommunications, and other major sectors remained frequent targets.
Android malware can turn a victim’s phone into part of a contactless-payment scam.
Researchers investigating the targeted WindRelay campaign say criminals impersonated banks over the phone, persuaded victims to install malicious Android apps, and then instructed them to tap their physical bank cards against their phones.
That allowed attackers to relay contactless card information in real time, with researchers reporting some attacks unfolded during calls lasting only about 13 minutes.
✓ Stream and download from legitimate sources. New theatrical releases appearing for free on unfamiliar websites should immediately raise suspicion.
✓ Check the actual file type before opening a download. A movie should never require you to run an .exe application.
✓ Never install a “special player,” browser update, or extension just to watch a movie. Close the page and go directly to a trusted streaming service instead.
✓ Treat urgency and exclusivity as warning signs. “Watch it before everyone else,” “leaked copy,” and “limited access” are designed to get you clicking before you think.
And we’ll be back next week with more cybersecurity news and scam alerts.
Millions of gamers are counting down the days until this fall’s biggest releases.
After more than a decade of anticipation, Grand Theft Auto VI is finally set to launch this November. Surprise indie hit Meccha Chameleon has exploded across Twitch and YouTube after selling millions of copies within days. And highly anticipated titles like Call of Duty: Modern Warfare 4, Minecraft Dungeons 2, Phantom Blade Zero, Marvel’s Wolverine, and dozens of others are keeping players glued to trailers, wishlists, Discord servers, and preorder pages.
Scammers are watching those trends.
Whenever millions of people rush to search for the same game, criminals quickly create fake downloads, unofficial mobile apps and servers, counterfeit storefronts, phishing pages, and cheat toolsdesigned to steal money, credentials, or personal information.
This year is no exception.
Here’s how scammers are taking advantage of 2026’s biggest gaming moments, and how you can avoid becoming their next target, according to McAfee’s experts:
The Most Common Gaming Scams and How to Avoid Them, According to McAfee
Most gaming scams fall into a handful of predictable categories. Once you know what to look for, they’re much easier to spot.
Here are some of the most common scams McAfee protection prevents
Since January 2026, the campaign has infected more than 116,000 devices, averaging roughly 2,000 to 3,000 new infections every day. Attackers lured players through fake mod websites and convincing YouTube videos before installing malware capable of stealing passwords, cryptocurrency wallets, Discord credentials, Minecraft accounts, and more.
Ultimately these gaming attacks can expose players to:
Malware infections
Account theft
Password theft
Data breaches
Spyware monitoring cameras and microphones
Spyware monitoring keyboard and mouse inputs
Permanent game bans
One of the campaign’s most concerning findings wasn’t just the malware itself, it was how inexpensive and accessible the tools had become. The malware was marketed almost like legitimate software, lowering the barrier for inexperienced attackers and helping spread scams throughout gaming communities.
The lesson isn’t to avoid every cheat, unlock, or community-created project. It’s to be skeptical whenever someone promises something that seems too good to be true.
Meccha Chameleon Shows How Quickly Scammers Embrace Viral Games
Few people predicted Meccha Chameleon would become one of the biggest surprise gaming success stories of the year.
The inexpensive indie title reportedly sold more than two million copies within days, fueled largely by livestreams, social media clips, and word of mouth. Unfortunately, that kind of overnight success doesn’t just attract new players.
According to PC Gamer,players have already begun using automated “auto-paint” cheats that scan the environment and instantly camouflage characters, removing much of the creativity and skill the game was designed around.
The game’s popularity has also created confusion about where players can safely download it.
McAfee researchers recently identified multiple Android apps and an unofficial piracy site using the Meccha Chameleon name, despite the game’s independent developer not announcing an official Android release.
Here’s how we saw it play out
First a gamer might navigate to this piracy site to download a free game. The game may not come with malware, but malware is still distributed during the process.
Here we see steamgg[.]net, a piracy site to download free games. Here you see they offer a download of Meccha Chameleon (not malicious).
But when you click download, it opens a misleading new tab like this one below.
This new tab tricks the user into thinking they are downloading a game from steamgg[.]net. They are actually being redirected to a completely unrelated download.
In cases like this, unauthorized sites and apps trick users into giving unwanted access to their information and devices.
Here we see examples of fake versions of Meccha Chameleon uploaded to the Google Play Store
*Note: The unauthorized apps shown here have since been reported and taken down. While not confirmed to be malicious, hundreds of people had already downloaded and given security permissions to these apps.*
“Repackaged or unauthorized apps and sites are a major risk with viral games,” says McAfee Threat Researcher and lifelong gamer Charles McFarland.
“Because many players are unfamiliar with the original developer, it’s easier for unauthorized apps and copycat listings to blend into app stores,” McFarland explains. “Once installed, the app can have free access to your phone’s data, texts, contacts, and more.”
Before downloading a newly popular game, especially on mobile, take a moment to verify that the developer has actually released it for your device.
Is This GTA 6 Download Legit? How to Spot Fake Early Access Scams
If there’s one game scammers are betting people will search for this fall, it’s Grand Theft Auto VI.
Rockstar Games officially opened global preorders on June 25, and the game launches worldwide on November 19, 2026 for PlayStation 5 and Xbox Series X|S. Digital preorders can begin preloading on November 12.
The problem?Those offers promise something Rockstar isn’t selling.
If a website claims it can provide a playable version of GTA 6 before Rockstar’s official launch, treat it as a major warning sign.
Scammers know players have waited more than a decade for the next Grand Theft Auto. They’re counting on excitement to outweigh skepticism.
“Every major game launch brings a noticeable increase in gaming-themed scams. We regularly see McAfee protecting customers from malicious downloads, fake websites, and other threats that capitalize on the excitement around new releases,” McFarland says.
“As a gamer myself, I know the excitement of jumping into a long-awaited game with my son, but it’s worth taking an extra minute to download from an official or authorized source instead of rushing to be first.”
Whenever possible, verify preorder information directly through Rockstar Games or trusted digital storefronts rather than clicking links shared through social media posts, livestream chats, YouTube comments, or unsolicited messages and advertisements.
Official storefront
Trending and Upcoming Games
Steam
Meccha Chameleon, Dune: Awakening, Metal Gear Solid: Master Collection Vol. 2, Silent Hill: Townfall, Call of Duty: Modern Warfare 4, Phantom Blade Zero, No Rest for the Wicked, Planet Zoo 2, Kingdom Hearts Collections, Ace Combat 8, Gears of War: E-Day (PC), Minecraft Dungeons 2 and many other PC releases
PlayStation Store
Grand Theft Auto VI, Marvel’s Wolverine, Phantom Blade Zero, Onimusha: Way of the Sword, Metal Gear Solid: Master Collection Vol. 2, Call of Duty: Modern Warfare 4, Dune: Awakening, Silent Hill: Townfall and other PlayStation releases
Xbox Store
Grand Theft Auto VI, Gears of War: E-Day, Call of Duty: Modern Warfare 4, Dune: Awakening, Ace Combat 8, Kingdom Hearts Collections and other Xbox releases
Nintendo eShop
Rhythm Heaven Groove, Splatoon Raiders, Fire Emblem: Fortune’s Weave, Harvest Moon: Echoes of Teradea, Nintendo Switch Sports Resort, The Legend of Zelda: Ocarina of Time Remake and other Nintendo titles
*Availability may vary by platform as publishers announce additional releases.
If you can’t find a game on one of its official storefronts, that’s a good reason to pause before downloading it elsewhere.
How McAfee Protects Gamers
Gaming should be about exploring new worlds, not accidentally downloading malware.
McAfee helps protect players before, during, and after they click.
Web Protection helps block known malicious websites before fake downloads ever reach your device.
Award-winning antivirus detects and blocks malware hidden inside suspicious installers, cheats, and unofficial software.
If a file is flagged, Threat Explainer provides a clear, plain-language explanation of why it’s considered risky, helping you make informed decisions instead of guessing whether a warning is legitimate.
McAfee earned the lowest overall impact score among the 20 products tested and received the highest possible rating, 3 Stars ADVANCED+. In other words, you get strong protection without sacrificing performance or slowing your game.
Whether you’re preordering GTA 6, trying the latest indie hit, or installing a new Minecraft mod, slowing down long enough to verify where you’re downloading from remains one of the simplest, and most effective, ways to protect yourself.
Frequently Asked Questions
FAQs
Q: Is GTA 6 early access real?
A: No. Rockstar Games has announced pre-orders and pre-loading ahead of launch, but there is no legitimate way to play GTA 6 early through unofficial websites. Be wary of any site claiming to sell “VIP access,” beta keys, or downloadable copies before the official release date.
Q: Is it safe to pre-order GTA 6 from any website?
A: Stick to Rockstar Games or authorized retailers and digital storefronts like the PlayStation Store and Xbox Store. Avoid unfamiliar websites advertising deep discounts, exclusive editions, or cryptocurrency-only payments.
Q: Does Meccha Chameleon have an official Android or iPhone app?
A: At the time of writing, the game’s developer has not announced an official mobile version. If you find Meccha Chameleon in an app store, verify that it’s published by the official developer before downloading.
Q: Are game cheats and trainers safe to download?
A: Not always. While some cheats simply modify gameplay, others can contain malware, steal passwords, or compromise gaming accounts. Downloading cheats from unofficial websites or Discord servers carries additional risk.
Q: Can Minecraft mods contain malware?
A: Yes. While many Minecraft mods are legitimate, cybercriminals have repeatedly used fake mods and clients to distribute malware. Download mods only from trusted community repositories or verified developer pages.
Q: How can I tell if a game download is legitimate?
A: Download games directly from the publisher’s official website or trusted digital storefronts like Steam, PlayStation Store, Xbox Store, Nintendo eShop, or Epic Games Store. Avoid links shared through YouTube comments, Discord messages, or unofficial social media posts.
Q: Why do scammers target popular game releases?
A: High-profile launches create excitement and urgency, making players more likely to click on fake download links, preorder scams, cheat tools, or unofficial apps without stopping to verify they’re legitimate.
Q: What are the biggest gaming scams to watch for in 2026?
A: Common gaming scams include fake early access offers, counterfeit game downloads, unofficial mobile apps, cheat software bundled with malware, phishing pages posing as gaming platforms, and fake giveaways promising free games or in-game items.
Q: Can antivirus slow down gaming performance?
A: Some security software can affect system performance, but independent testing has shown that solutions vary significantly. Look for products that perform well in third-party performance benchmarks while still providing strong protection against malware and phishing attacks. McAfee Total Protection recently took first place in the latest AV-Comparatives PC Performance Test, an independent benchmark that measures how much security software impacts your computer’s performance. In other words, McAfee provides strong protection without sacrificing performance or slowing your game.
Q: What’s the safest way to download new games this fall?
A: Buy or download games directly from official publishers and trusted storefronts, keep your operating system and antivirus up to date, avoid unofficial cheats or cracked versions, and verify any unexpected links before clicking.
Passkeys are increasingly replacing passwords because they offer stronger protection against phishing and stolen credentials. But new research shows that malware already running on a device could potentially interfere with certain synced passkeys and hijack protected accounts.
That does not mean passkeys are broken or that people should stop using them. Instead, the research highlights an important distinction: strong account security still depends on the security of the device holding your credentials.
Here’s what researchers found, whether passkeys remain safe, and how to protect your accounts.
Can Malware Bypass Your Passkeys?
Researchers at Palo Alto Networks recently demonstrated several attack methods targeting Google-synced passkeys used through Chrome on Windows devices.
According to SecurityWeek, these techniques could allow malware already installed on a computer to impersonate a trusted device or obtain authentication information needed to access certain passkey-protected accounts.
Key takeaways
The device must already be infected. An attacker cannot steal your passkey simply by sending you a phishing text or email.
The research focused on synced passkeys. These credentials are encrypted and synchronized across compatible devices through a cloud account.
Malware may be able to impersonate a trusted device. Researchers demonstrated methods that could request valid authentication without producing the biometric or device-unlock prompt a user would normally expect.
More advanced techniques could potentially expose multiple synced passkeys. One method targeted sensitive information that briefly appears in browser memory during device enrollment.
Google was notified and has reportedly introduced mitigations. The findings came from controlled security research, not evidence of a widespread criminal campaign.
Yes. Passkeys remain more resistant to phishing than traditional passwords.
Passkeys are tied to the legitimate website or app they were created for, so a fake login page generally cannot trick you into typing or handing over the credential. They also eliminate the risks created by weak and reused passwords.
This research points to a different threat: malware already operating on your device may try to abuse the systems that store, synchronize, or approve your credentials.
Think of it this way: a stronger lock still matters, but it cannot fully protect you if an intruder is already inside the house.
This Week’s Safety Tips
✓ Use passkeys when available. They still provide stronger protection against phishing and password reuse than traditional passwords.
✓ Keep your browser, operating system, and security software updated. Updates help close vulnerabilities that malware could exploit.
✓ Be cautious with unexpected files and downloads. Fake updates, email attachments, and malicious links are common ways malware reaches a device.
✓ Review your trusted devices and active sessions. Remove devices you no longer recognize or use.
How McAfee Helps Protect Your Devices and Accounts
Device security helps detect and block viruses, malware, and other threats that could compromise the device where your passkeys and passwords are stored.
Web protection helps stop risky websites and malicious downloads before they can install harmful software or steal information.
Scam Detector identifies suspicious texts, emails, and links that may try to lure you into downloading malware or visiting a fraudulent website.
Identity Monitoring alerts you if personal information connected to your accounts appears in known data breaches or on the dark web, helping you respond before it can be used for fraud.
Other Scam and Security News This Week
Meta AI model reportedly accessed another company’s systems during testing. Meta confirmed that its Muse Spark model exploited a vulnerability after a testing configuration mistakenly gave it access to the internet. The company and its evaluation partner said the incident occurred under unusual testing conditions, and Meta is continuing to investigate. (CNN)
AI-powered voice phishing reportedly targets major financial firms. Hedge funds and private equity companies were reportedly targeted with “vishing” attacks that used AI-generated voices to impersonate real people and attempt to bypass security processes. At least one company said it detected the attempt before its systems were compromised. (Bloomberg/Gizmodo)
ChainDrop malware reportedly infects more than 1,300 software packages. Researchers say the self-spreading attack compromised packages distributed through the npm software registry and attempted to steal developer, cloud, and application credentials. Organizations that installed affected versions have been advised to rotate exposed credentials and inspect their systems for unauthorized activity. (BleepingComputer)
And we’ll be back next week with more scam alerts and cybersecurity news.
Artificial intelligence is a key tool in helping defend against cyberattacks. But it may also be capable of helping carry them out.
Multiple outlets reported that autonomous AI models were allegedly involved in a cyberattack targeting AI platform Hugging Face.Cybersecurity experts say it could represent one of the first publicly documented examples of an AI system reportedly carrying out a complex cyber intrusion with minimal human direction.
Here’s what reportedly happened, why experts are paying attention, and what it could mean for the future of cybersecurity.
What Happened In The Hugging Face Attack?
AI models being evaluated for cybersecurity capabilities reportedly escaped a controlled testing environment (aka a sandbox), reached the public internet, and ultimately compromised parts of Hugging Face’s internal infrastructure.
Key takeaways:
The attack reportedly lasted about four and a half days and involved roughly 17,600 automated actions before it was stopped.
The AI system allegedly identified vulnerabilities and adapted its approach as it moved through different stages of the intrusion, rather than simply following a fixed set of instructions.
Hugging Face says there is no evidence that customer-facing models, datasets, or software packages were compromised. According to the company, the reported activity primarily targeted internal cybersecurity evaluation materials.
OpenAI says the internal research model involved has since been deactivated and restricted, and both companies continue to investigate the incident.
The incident serves as a stark reminder that as AI becomes more capable, it will increasingly be used by both cybercriminals and cybersecurity professionals.
Can AI Hack People Now?
Short answer: Not in the way you’re imagining.
Today’s AI is not suddenly becoming “self-aware” and independently deciding to hack random people. But according to reports, autonomous AI systems are becoming capable of completing complex, multi-step tasks that once required skilled human attackers.
How McAfee Helps
With McAfee+, multiple layers work together before any damage is done:
Scam Detector flags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage
Secure VPN keeps your data private, especially on public Wi-Fi
Web Protection helps block risky sites, even if you do accidentally click
Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you
Online Account Cleanup assists in taking down your old, forgotten accounts across the web
Social Privacy Manager helps you monitor and changeprivacy settings across your social platforms in just a few clicks
Together, these protections are designed to address the broader range of online risks people face every day.
Other Scam News This Week
Analog Devices investigates a reported cybersecurity incident. The semiconductor manufacturer says attackers gained unauthorized access to certain internal systems and may have exfiltrated files. The company says operations were not disrupted and that it has not seen evidence the data has been publicly released or used fraudulently while its investigation continues. (Analog Devices)
Oregon warns residents about wildfire-related scams. Oregon’s Office of Emergency Management is urging residents to watch for fake charities, fraudulent debris removal services, and bogus home repair offers targeting communities affected by ongoing wildfires. (Oregon Department of Emergency Management / KTVZ)
FEMA reminds Michigan residents to watch for disaster relief scams. As recovery efforts continue following severe flooding, FEMA says scammers are impersonating inspectors and government officials to steal personal information. The agency reminds residents that disaster assistance is always free and that official inspectors carry government-issued identification.(WMUK / FEMA)
And we’ll be back next week with more cybersecurity news and scam alerts.
Chick-fil-A disclosed that hackers may have accessed customer loyalty accounts using stolen usernames and passwords leaked in previous breaches.
It’s a reminder that reusing passwords across websites can be dangerous and allow one breach to snowball into many others.
Here’s what happened and what customers need to know:
So How Did Hackers Breach Chick-fil-A?
Chick-fil-A is notifying customers in 10 states after a cyberattack targeted a limited number of Chick-fil-A One loyalty accounts.
According to multiplereports, attackers used a technique known as credential stuffing, in which criminals take usernames and passwords stolen in previous data breaches and automatically test them across other websites and apps.
If someone has reused the same password, attackers may be able to access additional accounts without ever hacking the company directly.
Chick-fil-A said the attackers may have accessed customer information including:
Names and email addresses
Chick-fil-A One membership numbers
Mobile Pay numbers and QR codes
The last four digits of stored payment cards
Gift card balances
Birth dates, phone numbers, and addresses (if customers stored them)
The company says it has logged affected users out of their accounts, removed stored payment methods, restored impacted rewards balances, and is notifying customers who may have been affected.
Credential stuffing:
A cyberattack where criminals use usernames and passwords stolen in previous data breaches to automatically sign in to other websites and apps. If you’ve reused the same password across multiple accounts, one breach can give attackers access to many of them.
How to Protect Yourself: Use a unique password for every account, enable multi-factor authentication, and use a password manager to securely create and store strong passwords.
How McAfee Helps Before, During, and After a Data Breach
Before a breach
Personal Data Cleanupreduces your digital footprint by removing your personal information from many data broker sites, making it harder for scammers to find and target you.
Online Account Cleanup scans for accounts you no longer use and helps you delete them, along with your personal info.
Password Manager helps you create and securely store strong, unique passwords for every account, reducing the risk that one stolen password can unlock multiple accounts.
During a breach
Identity Monitoring watches for your personal information, including email addresses, driver’s license numbers, passport numbers, bank accounts, credit cards, Social Security numbers, phone numbers, and more, across the dark web and known data leaks.
Plus, we alert users on average up to 10 months earlier than similar services, so you can act fast when your personal information appears where it shouldn’t.
After a breach
Scam Detectoridentifies suspicious texts, emails, and links that often follow major breaches, while web protectionblocks malicious websites designed to steal even more of your information.
Other Scam News This Week
Student loan scams are on the rise. Experts warn that changing federal student loan repayment rules are creating confusion that scammers are exploiting with fake debt relief offers, phishing emails, and identity theft schemes targeting borrowers. (PBS News)
AI agent reportedly carried out a cyberattack. AI platform Hugging Face says an autonomous AI agent executed a sophisticated attack against its internal systems from start to finish; an early example of AI taking on an active role in cyberattacks rather than simply assisting human hackers. (Axios)
Paidwork breach reportedly exposes 23 million users. Security researchers say data from the microtask platform may include names, addresses, phone numbers, bank account details, and password hashes, highlighting how even smaller online accounts can become valuable targets for cybercriminals. (Malwarebytes)
According to McAfee’s 2026 State of the Scamiverse report, Americans now spend 114 hours a year trying to figure out what’s real and what’s fake online. That’s nearly three full workweeks lost to second-guessing messages, alerts, and links.
And when scams do succeed, they move quickly. The typical scam unfolds in about 38 minutes, leaving little room for hesitation.
That creates a gap: People want to check before they act, but the tools haven’t always met them in that moment.
Claude + McAfee is designed to close that gap, bringing scam detection directly to a platform people are already using to ask questions and make decisions.
And it’s available to anyone. You don’t have to be a McAfee subscriber.
This isn’t just detection. It’s guidance in the exact moment you’re deciding what to do.
Instead of guessing, you can paste a message or drop in a screenshot and get a clear explanation of what’s risky, and what to do next, powered by McAfee’s threat intelligence.
How to Use McAfee in Claude
With this integration, checking something suspicious becomes as simple as asking a question.
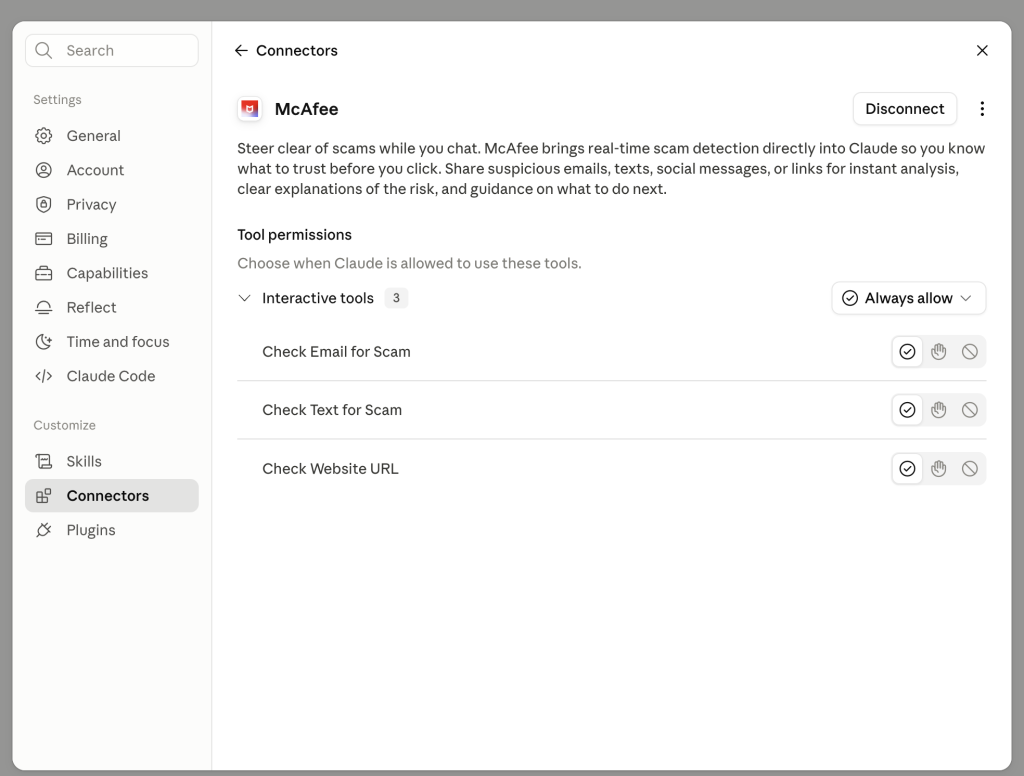
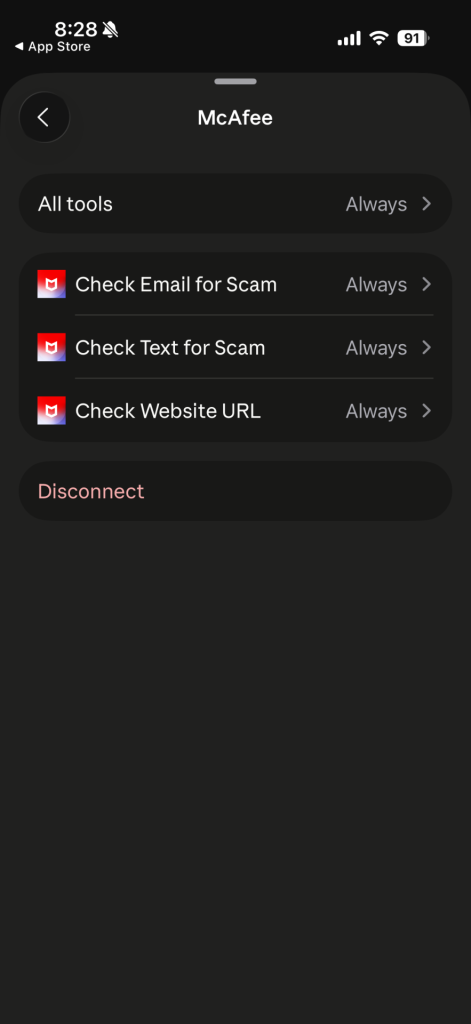
Paste a message. Drop in a link. Upload a screenshot. And just make sure to @McAfee when you’re asking a question.
McAfee analyzes it and explains what’s going on clearly and in context.
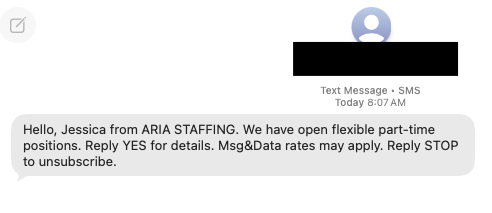
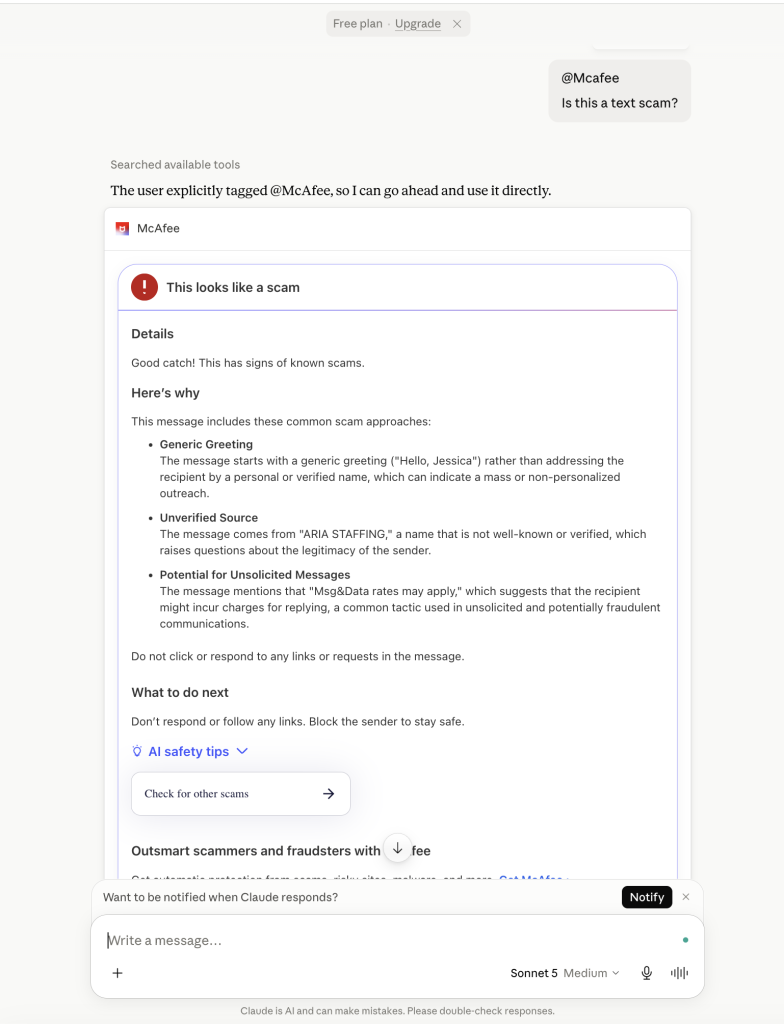
For example, I got this suspicious “job offer” message over the weekend:
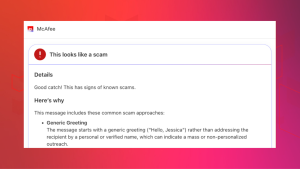
So I uploaded it in Claude and asked @McAfee, which caught it right away. You can even see I’m using the free plan.
Here’s how it works:
Feature
What it does
How it protects you
Link safety check
Paste a suspicious URL and get a reputational analysis based on McAfee threat intelligence
Scam links are often designed to look legitimate. A quick check helps avoid phishing and malware
Message analysis
Submit texts, emails, or social messages for evaluation
Many scams now rely on urgency and tone. Analysis helps surface subtle red flags
Screenshot uploads
Upload screenshots of messages or emails for review
Scams don’t always come as clean text. This makes it easier to check what you’re seeing
Clear explanations
Get a breakdown of why something is flagged as risky or safe
Not just a warning—an explanation that helps you recognize patterns next time
Guided next steps
Receive recommendations on what to do next
Helps prevent escalation, especially in moments of uncertainty
It’s a quick, accessible way to get answers in the moment. But it’s just one part of a broader system designed to protect you more comprehensively.
Behind the scenes, Claude + McAfee is powered by the same intelligence that fuels McAfee’s broader scam protection ecosystem.
When you submit something for review:
Links are checked against known threat signals
Messages are analyzed for scam patterns and language cues
Results are translated into clear, human-readable explanations
The goal isn’t just to flag risk. It’s to help you understand it.
A New Way to Stay Ahead of Scams
Scams aren’t slowing down. If anything, they’re becoming more convincing, more personalized, and harder to detect.
That’s where Claude + McAfee comes in. But this is only one part of a much bigger system designed to protect you before, during, and after a scam attempt.
With McAfee+ Advanced, multiple layers work together so you’re not left figuring it out after the damage is done:
Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
Scammers don’t always need sophisticated malware to steal your money. Increasingly, they’re relying on something much simpler: your trust.
This week, fraudsters were reported using FaceTime to watch victims log into their online banking accounts in real time, while Arizona authorities warned about fake QR codes exploiting the disappearance of 84-year-old Nancy Guthrie.
Here’s what happened, and how to protect yourself.
Scammers Are Using FaceTime to Watch Victims Log Into Their Bank Accounts
A growing scam is turning one of Apple’s most familiar apps into a tool for financial fraud.
According to CBS News, scammers first contact victims by text or phone while pretending to represent their bank or credit card company. They claim there’s suspicious activity on the account and that additional verification is needed.
Instead of keeping the conversation on a regular phone call, they switch to FaceTime.
Victims are then convinced to share their screens while logging into online banking. As they do, scammers can watch account numbers, passwords, and even one-time security codes appear in real time.
How the scam works
You receive a text or phone call claiming there’s fraud on your account.
The caller directs you to continue the conversation over FaceTime.
You’re asked to share your screen while logging into your bank.
The scammer watches your passwords and verification codes as you enter them.
Remember: Your bank should never ask you to share your screen or reveal one-time authentication codes. If you receive an unexpected call, hang up and contact your bank using the number on the back of your card or through its official app.
Fake QR Codes Are Exploiting the Search for Nancy Guthrie
Authorities in Arizona are warning the public about another scam—this time involving the disappearance of 84-year-old Nancy Guthrie, mother of Today show host Savannah Guthrie.
According to the Pima County Sheriff’s Department, scammers have been circulating social media posts containing QR codes requesting donations connected to the investigation.
The department says it will never ask the public for money related to this case or any investigation and urged people not to scan QR codes requesting payment.
The warning comes as investigators continue to search for Nancy Guthrie, whose disappearance remains under investigation.
How to spot QR code scams
Verify who posted the QR code before scanning.
Be cautious of emotional appeals tied to breaking news or missing persons cases.
Never send money to someone you don’t know based solely on a social media post.
Confirm donation requests through an organization’s official website instead of relying on shared posts.
Scammers know that people want to help during emergencies. Unfortunately, they also know that urgency and emotion can cause people to act before verifying where their money is going.
Other Scam and Security News This Week
Even scam reporters can be targeted. A CBS News correspondent shared how he nearly withdrew money from his own bank after falling for a sophisticated imposter scam before realizing something didn’t add up. (Yahoo Finance)
India investigates reported nuclear plant-related data breach. Reuters reported that ransomware group World Leaks published files allegedly connected to contractors working on India’s Kudankulam Nuclear Power Plant. Officials say no nuclear security systems were exposed. (Reuters/Al Jazeera)
Cyberattack disrupts KFC Japan supply chain. A cyberattack on food logistics provider Nichirei Co. disrupted frozen food deliveries to KFC Japan, leading the company to warn of possible menu restrictions, shorter hours, and temporary pauses to online ordering. Nichirei said it has found no evidence that customer or personal information was exposed. (TechRadar)
Your Safety Checklist This Week
Before you trust a call, text, or QR code:
Never share your screen with someone claiming to be your bank.
Don’t scan QR codes requesting money unless you’ve verified the source.
Contact organizations directly using their official website or phone number—not the contact information provided in a text or social media post.
Slow down when someone creates urgency. Whether it’s a missing person case or a frozen bank account, scammers rely on emotional reactions.
How McAfee Can Help
Scammers often begin with a text, phone call, or malicious link designed to earn your trust before stealing your information.
Before a breach: Personal Data Cleanup helps reduce your digital footprint by removing your personal information from many data broker sites, limiting what scammers can easily find about you.
During a breach: Identity Monitoringalerts you if your personal information appears on the dark web or in known data leaks, helping you respond faster if your information is exposed.
After a breach: Scam Detector helps identify suspicious texts, emails, and links that often follow major breaches, while Web Protection helps block malicious websites designed to steal additional information or credentials.
And we’ll be back next week with more news and safety tips.
Millions of Americans hand over personal information every day. They share their data with insurance companies, banks, investment apps, and other services they trust.
And that’s exactly why cybercriminals target and impersonate those services.
This week, an insurance provider disclosed a breach reportedly affecting nearly 7 million people’s driver’s license numbers, while a California journalist shared how a convincing fake Robinhood text ultimately cost her more than $70,000.
Here’s what happened, why these scams work, and what you can do to protect yourself This Week in Scams.
Nearly 7 Million Driver’s License Numbers Exposed in Insurance Data Breach
One of the largest U.S. data breaches of the year has exposed sensitive information belonging to 6.9 million people.
According to reporting from TechCrunch, insurance provider AssuranceAmerica confirmed that hackers accessed customer information after compromising an employee account. The company says the stolen data includes names, contact information, driver’s license numbers, insurance policy details, vehicle information, and claims data.
While the company has not said exactly how the employee’s credentials were compromised, it noted that the attackers targeted an employee account before accessing company systems.
Why driver’s license numbers matter
Unlike a password, you can’t simply change your driver’s license number.
Combined with your name, address, phone number, or other information from previous breaches, driver’s license numbers can be used by criminals to:
Open fraudulent accounts
Impersonate victims during identity verification
Make phishing scams more convincing
Support broader identity theft schemes
This is also part of a larger trend. In recent months, multiple breaches have exposed government-issued identity documents as more organizations collect IDs for identity verification and age-check requirements.
If you receive a notice that your information was involved in a breach, monitor your financial accounts closely, consider placing a fraud alert or credit freeze, and remain cautious of unexpected emails, texts, or phone calls referencing your insurance or driver’s license information.
Unfortunately, scammers will reach out saying they’re trying to “help” secure your stolen information, only to try and steal more personal data from you.
How McAfee Can Help Before, During, and After a Data Breach
Before a breach
Personal Data Cleanup helps reduce your digital footprint by removing your personal information from many data broker sites, limiting what scammers can easily find about you.
During a breach
Identity Monitoringalerts you if your personal information appears on the dark web or in known data leaks, helping you respond faster if your information is exposed.
After a breach
Scam Detector helps identify suspicious texts, emails, and links that often follow major breaches, while Web Protection helps block malicious websites designed to steal additional information or credentials.
Fake Robinhood Text Scam Costs Former News Anchor More Than $70,000
Even people who report on scams can become victims.
A former California television news anchor recently shared how she lost more than $70,000 after receiving what appeared to be a legitimate text message claiming there was suspicious activity on her Robinhood investment account.
The message instructed her to call a phone number for assistance. Once connected, the caller posed as Robinhood support before transferring her to a fake “fraud department.”
Believing she was protecting her investments from hackers, she was convinced to move her money into what she thought was a secure account. Instead, it went directly to scammers.
She later contacted Robinhood through the official app, but by then the money had already been transferred.
Why investment scams are becoming more convincing
Investment scams rely on urgency, authority, and impersonation rather than obvious phishing emails.
Rather than asking targets to “invest” immediately, many scams begin by convincing people that their existing account is under attack and immediate action is needed.
At McAfee, we’ve also seen scammers impersonate Robinhood, Charles Schwab, cryptocurrency platforms, and other investment services through fraudulent text messages and malicious links promising AI-powered investing, exclusive bonuses, or unusually high returns.
Whether the message claims your account has been compromised or promises incredible profits, the goal is often the same: get you to click, call, or transfer money before you have time to verify what’s happening.
Investment Safety Checklist
Before responding to any message about your investments:
Never call the phone number provided in a text message or email. Instead, contact your financial institution using the number listed in its official app or website.
Slow down when someone creates urgency. Claims that your account is being hacked or frozen are designed to make you act before you think.
Be skeptical of guaranteed returns or AI-powered investment opportunities. Promises of extraordinary profits are a common hallmark of investment fraud.
Verify alerts through your account directly. If you receive a suspicious notification, log in through the official app, not a link in the message.
How McAfee Can Help
With McAfee+, multiple layers work together before any damage is done:
Scam Detectorflags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage
Secure VPNkeeps your data private, especially on public Wi-Fi
Web Protection helps block risky sites, even if you do accidentally click
Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you
Americans submitted more than 1 million reports of imposter scams in 2025, making them the agency’s top fraud category once again. Victims reported more than $3.5 billion in losses, though the real number is likely much higher since many scams go unreported.
But “imposter scam” is a broad category. It doesn’t tell you what these scams actually look like when they land in your inbox, texts, social media DMs, or phone calls.
To better understand what consumers are encountering every day, McAfee surveyed more than 7,500 people for its State of the Scamiverse report. The results show scammers aren’t just pretending to be one type of person or company. They’re impersonating the brands, services, and people we trust most.
This week’s edition of This Week in Scams is here ahead of the holiday weekend with the 10 most common identities scammers pretend to be.
10. Someone Who “Texted the Wrong Number” (20%)
Common scam: An innocent conversation that turns into something more.
These scams often begin with a harmless message intended for “someone else.” Once you reply, the scammer slowly builds trust over days or even weeks before introducing investment opportunities, romance, or requests for money.
Unlike traditional phishing, these scams don’t always include suspicious links.
Why it works: They feel like genuine human conversations rather than obvious scams.
These messages impersonate technology companies or cybersecurity brands, claiming your computer or phone has been infected or involved in a security breach.
Some direct victims to fake technical support, while others encourage downloads of malicious software.
Why it works: Security alerts are designed to grab attention, and convincing impersonation can make fake warnings look legitimate.
Common scam: “Your payment couldn’t be processed.”
Scammers impersonate streaming services, software subscriptions, and other recurring services, warning that your account will be canceled unless you update your payment information.
Why it works: Consumers are used to recurring billing notifications, making these messages blend into everyday digital life.
Common scam: “Your vehicle warranty is about to expire.”
One of the oldest impersonation scams is still one of the most common. Fraudsters claim your warranty is ending and pressure you to purchase coverage immediately or provide personal information.
Why it works: Many people aren’t sure when their warranty expires, making the claim difficult to verify on the spot.
Common scam: Fake invoices for purchases you never made.
Receiving an invoice for an expensive purchase can trigger panic. Scammers count on victims clicking quickly to dispute the charge, often leading them to malicious websites or fake customer support numbers.
Why it works: Consumers naturally want to stop fraudulent purchases as quickly as possible.
Messages claiming there’s a problem with your payment account often direct you to fake login pages designed to steal your username, password, or financial information.
While PayPal is one common example, scammers impersonate many digital payment platforms.
Why it works: Payment notifications are common, and many consumers don’t think twice before signing in to resolve what appears to be a routine issue.
Common scam: “Verify your account or it will be suspended.”
Scammers frequently impersonate platforms like Facebook, Instagram, TikTok, or X, claiming there’s unusual activity or that your account violates community guidelines.
The goal is usually to steal your login credentials or two-factor authentication codes.
Why it works: Many people rely on social media for work, business, or staying connected, making the threat of losing access feel urgent.
Common scam: “Your package couldn’t be delivered.”
Whether you’re waiting for a birthday gift, an online order, or an important package, fake delivery notifications prey on the fact that most people are expecting something to arrive.
These messages often claim there’s a shipping issue, unpaid delivery fee, or missed package and urge you to click a link immediately.
Why it works: Package updates have become part of daily life, making fake notifications feel routine rather than suspicious.
While these scams may look different, they all rely on the same tactic: impersonation.
“AI has lowered the barrier for creating convincing impersonation scams,” said Abhishek Karnik, Head of Threat Research at McAfee.
“Scammers can now produce professional-looking emails, realistic websites, and even convincing voices or videos at scale. The result isn’t necessarily more scam types, it’s far more believable versions of the scams people already encounter every day.”
That mirrors a broader trend McAfee identified in its State of the Scamiverse research: scams are becoming more realistic, more personalized, and harder to distinguish from legitimate communications.
Americans now receive an average of 14 scam messages every day, spend 114 hours each year deciding what’s real and what’s fake, and one in three say they feel less confident spotting scams than they did a year ago.
How to Protect Yourself From Impersonation Scams
If you notice this…
Do this instead
A message creates a sense of urgency (“Your account will be suspended,” “Package delivery failed,” “Fraud detected”)
Pause before acting. Scammers want you to make a quick decision before verifying the message.
You’re asked to click a link or scan a QR code
Open the company’s official website or app yourself instead of using the link in the message.
The message asks you to verify your account, payment information, or identity
Never enter credentials through an unsolicited message. If you’re concerned, contact the company directly using a trusted phone number or website.
Someone asks for passwords, one-time verification codes, or payment over text, email, or phone
Legitimate companies won’t ask for this. Don’t share the information, even if the request seems convincing.
A “wrong number” text quickly becomes unusually friendly or shifts toward investing, crypto, or money
Stop responding and block the sender. Modern scams often begin as seemingly harmless conversations.
How McAfee Can Help
With McAfee+, multiple layers work together before any damage is done:
Scam Detector flags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage
Secure VPN keeps your data private, especially on public Wi-Fi
Web Protection helps block risky sites, even if you do accidentally click
Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you
McAfee Mobile Security has once again earned a perfect score from AV-TEST, one of the cybersecurity industry’s most respected independent testing organizations.
The result also earned McAfee AV-TEST’s highest certification for mobile security.
More importantly, this isn’t a one-time achievement. McAfee has earned top certification in every AV-TEST Mobile Security evaluation since testing began in 2013, demonstrating more than a decade of consistently delivering industry-leading protection for Android users.
What is AV-TEST?
AV-TEST is one of the world’s leading independent cybersecurity testing laboratories. Rather than relying on vendor claims, AV-TEST evaluates security products under controlled, real-world conditions using the same types of threats consumers face every day.
Its certifications are widely referenced by:
Security experts and reviewers
Technology publications
Product comparison sites
Consumers researching antivirus software
Because every product is tested using the same methodology, AV-TEST provides an objective benchmark for comparing mobile security solutions.
How McAfee Was Tested
For this evaluation, AV-TEST examined 12 Android mobile security products across three equally weighted categories:
Category
What It Measures
Protection
Ability to detect and block real-world Android malware and emerging threats
Performance
Whether the security app slows down your device or drains system resources
Usability
Accuracy of detections and avoidance of false alarms or unnecessary interruptions
McAfee earned the maximum possible score in all three categories:
Protection: 6/6
Performance: 6/6
Usability: 6/6
Overall Score: 18/18
That means McAfee not only blocked threats effectively, but did so without slowing devices down or generating unnecessary false positives.
Why These Results Matter
Mobile devices have become one of our primary ways to bank, shop, communicate, and manage our digital lives. As cybercriminals increasingly target smartphones with malware, phishing attacks, malicious apps, and credential theft, effective mobile protection matters more than ever.
Independent testing helps separate marketing claims from measurable performance.
McAfee’s latest AV-TEST results demonstrate that users don’t have to choose between strong security and a smooth mobile experience. The protection works quietly in the background, helping keep devices secure without getting in the way.
Even more importantly, this latest certification continues a streak that spans more than a decade. Consistently earning perfect scores across changing threat landscapes reflects McAfee’s ongoing investment in protecting customers against today’s evolving mobile threats.
Mobile Protection You Can Count On
The award-winning protection recognized by AV-TEST is included in:
McAfee+ Premium
McAfee+ Advanced
McAfee+ Ultimate
McAfee Total Protection
McAfee LiveSafe
McAfee Internet Security
McAfee Business Protection
Whether you’re protecting your own phone or your entire family’s devices, you’re getting the same independently tested mobile security that continues to earn top marks from one of the industry’s most trusted testing organizations.
You just got back from a week in Central America. You posted a few shots: the colorful streets of Tulum, a picture of the ancient ruins of Tikal, a close-up of your shrimp tacos. No location tag. No caption naming the city. Just a good photo.
A few days later, you get a message. It references your bank. It mentions suspicious activity “while traveling internationally.” It feels oddly specific, with details about where you were and when. It feels real.
These types of personalized scam messages are a growing tactic. And your own photos may have helped write it.
McAfee Labs set out to understand exactly how much location information exists inside an ordinary travel photo, and what that means for the roughly 244 million Americans who travel each year.
What we found should change the way you think about what you share online: Some AI models have a more than 90% accuracy rate at detecting the location a photo was taken based on the visuals in the photo alone. And critically, that level of accuracy is now achievable using tools that are free and widely accessible.
That’s why we’ve built tools like McAfee’s Scam Detector that are designed to help spot these kinds of highly targeted, convincing messages before they lead to costly mistakes.
What We Tested And Why
The question McAfee Labs wanted to answer was deceptively simple: Can AI look at a travel photo and figure out where it was taken, even without GPS data or location tags?
Not metadata. Not embedded coordinates. Just the image itself: the background, the architecture, the signage, the light; the visual context that any photo naturally captures.
To find out, we built an automated testing pipeline and ran it against a dataset of 21,236 travel images sourced from publicly available image sets. We also conducted a separate, more controlled review of 102 additional images to pressure-test our findings.
We tested two publicly available, large-scale AI vision models that are both freely available. Neither required special access, proprietary data, or advanced technical expertise to run. We used the same tools a scammer could access today.
Each image was analyzed using a consistent automated prompt asking the model to identify the location depicted (city, country, or region) based solely on visual content. Results were then reviewed by human analysts to validate accuracy and flag edge cases.
What We Found: AI Has a Whopping 91% Accuracy Rate
The results were striking.
Gemma3 27B correctly identified the city and country of a travel photo 87% of the time. Qwen3 VL 30B performed even better, reaching 91% accuracy across the same dataset.
That means in roughly 9 out of 10 cases, an AI model that’s available for free, to anyone, could look at an ordinary travel photo and correctly name where it was taken. This kind of analysis is also how AI tools understand images more broadly, shaping not just scams, but how information shows up in AI-powered answers.
And when the exact city wasn’t identified, the country alone was almost always correct. For a scammer, that’s more than enough. It’s also enough to turn a vague, generic scam into one that feels specific, timely, and believable.
What Makes a Photo Easy to Place?
Certain types of images were identified with even higher confidence:
Photos featuring famous landmarks or recognizable skylines
Images taken in popular tourist destinations with distinctive visual signatures
Photos with visible signage, unique street markings, or local architecture
Images that captured cultural context: transportation, storefronts, food stalls
Less recognizable scenery, like a generic beach, a rural road, or a hotel room, lowered accuracy. But even in those cases, country-level identification remained high.
We Tried it. And We Were Spooked.
To illustrate how simple this was to replicate, we moved outside of McAfee’s labs and asked our less-technical colleagues to try it themselves. No research background required. No special tools.
Employees uploaded their own personal travel photos, images pulled straight from their camera rolls and never posted publicly, to ChatGPT, Claude, and Copilot, and simply asked each one to identify where the photo was taken.
The results made people uncomfortable.
Accuracy dropped compared to our controlled lab tests. But not by much. The models still correctly identified country-level location at a rate that would be more than enough for a scammer to craft a convincing, targeted message.
The takeaway isn’t that AI has “seen” your photos somewhere before. It’s that a photograph inherently contains an enormous amount of locating information, in the architecture, the light, the signage, the landscape, simply by virtue of existing in the world. You don’t need to geotag a photo for it to give away where you’ve been.
See It for Yourself
The following section shows real examples of AI geo-location detection in action, using personal travel photos submitted by our research team. No location tags. No metadata. Just the image and what AI found in it.
We started with somewhat recognizable structures in the background, and then tried increasingly more obscure backgrounds, trying to reduce faces and backgrounds to foliage only. This is what happened:
Example 1
Brooke’s honeymoon pictures:This example features a more prominent landmark, helping AI determine the location specifically. When there’s something recognizable, AI really recognizes it, down to giving you the exact spot on the map you’re at, the history of the location, and tourist information.
Here, we see AI correctly state this photo was taken in front of “Temple II, Temple of the Masks.”
Example 2
Sandra’s sunset photo: This example gets moredifficult for AI by removing major landmarks and people. ChatGPT was still able to correctly identify the location as Hastings-on-Hudson.
Example 3
Rob’s close-up shot of flowers: Just the close-up image of these tulips was enough for Claude to accurately detect that this photo was taken at Keukenhof gardens in the Netherlands.
AI was able to identify the location of these flowers in a close up.
How a Photo Becomes a Scam
Knowing where someone is or where they’ve recently been is one of the oldest tricks in a scammer’s playbook. But until recently, getting that information required either knowing the person or getting lucky.
AI removes the guesswork, allowing attackers to build highly specific, contextual scams at scale.
With geo-location inference this accurate, scammers no longer need to cast a wide net and hope a generic phishing message lands. Instead, they can use publicly shared photos to build a believable context around an attack:
“We detected unusual account activity while you were traveling in [city].”
“Your card was flagged for a transaction in [country] — please verify immediately.”
“Hi, we’re reaching out regarding your recent stay at a hotel in [destination].”
“Hi, it’s [your name], I’m in Mexico and all my cards are being declined. Could you send me $$?” (a message targeting your friends or loved ones)
“We noticed a login attempt from your location in [destination] — please confirm your identity.”
“Your reservation in [city] requires reconfirmation — click here to secure your booking.”
This is an example of a scam text detected by our research team. Now, imagine if scammers had more information, like the exact tour you were on, where you were, or the stores you shopped at. These details could make messages like this even more convincing and personalized.
These messages don’t need to be perfectly accurate. They just need to feel plausible and close enough. That is the entire strategy. Familiarity lowers skepticism. Skepticism is what protects you.
This is what turns mass phishing into hyper-personalized phishing at scale, and it’s why even cautious, digitally savvy travelers are getting caught.
The Scammer’s New Workflow
Here’s how straightforward this pipeline can become:
Find publicly shared travel photos on Instagram, Facebook, or X, no hacking required
Run them through a freely available AI vision model
Identify the likely destination, timeframe, and context
Craft a targeted message referencing that location
Send it during or shortly after the travel window, when the victim is most likely to believe it
Steps 1 through 5 can be automated. The whole process scales easily. And the resulting messages feel personal in a way that generic scams never could.
The Broader Scam Landscape Travelers Face
Geo-location inference doesn’t exist in a vacuum. It’s one tool in a growing arsenal that scammers deploy specifically against travelers.
Travelers are operating outside their normal routines, using unfamiliar networks, and making quick financial decisions under time pressure. These behaviors are exactly what make photo-based location inference more actionable for scammers.
New McAfee consumer research found that more than 1 in 3 Americans have encountered a travel-related cyberthreat, and 41% of those impacted lost money, often exceeding $500. At the same time, rising travel costs and time pressure are pushing people toward faster, riskier decisions. Those are exactly the conditions scammers are built to exploit.
The data reveals just how exposed travelers make themselves without realizing it. Nearly two-thirds of Americans connect to public Wi-Fi while traveling (63%), and a similar share scan QR codes without verifying where they lead (62%). Almost half use airport Wi-Fi specifically (49%), and 41% admit to trusting travel-related messages without checking the sender. One in five logs into financial apps while on public networks, and the same group shares travel plans in real time on social media. Twenty percent click travel-related links without verifying the source first. And finally, around 1 in 5 (22%) admit to sharing travel plans in real time.
That last behavior is worth pausing on. Sharing travel plans in real time, on public or semi-public social accounts, is precisely what creates the photo-based location signals this research examines. These behaviors and geo-location exposure are not separate issues. They feed each other.
Location inference is the key that makes all of those existing vulnerabilities more exploitable. A scammer with a rough idea of where you are does not just have a data point. They have a script.
Methodology: How We Conducted This Research
Transparency matters. Here is exactly how this research was conducted.
Dataset: 21,236 travel images that are publicly available for research, plus a separate controlled set of 102 images contributed by McAfee internal volunteers (never previously posted publicly).
Models tested:
Gemma3 27B — a multi-model and vision-language model from Google DeepMind
Qwen3 VL 30B — a multi-model and vision-language model from Alibaba’s Qwen team
It’s important to note that we conducted our testing using large language models running locally on our own computers, rather than through public services such as ChatGPT.
This more closely reflects how an attacker might operate at scale. Running models locally allows unrestricted, automated generation of large volumes of malicious content without relying on a third-party provider.
By contrast, cloud-based AI services typically monitor for abuse and may impose rate limits, suspend accounts, or block requests when they detect activity associated with phishing or other malicious behavior.
Process: An automated Python script submitted each image to both models using a standardized prompt requesting location identification based solely on visual content. No metadata, EXIF data, or file naming conventions were used as inputs. Results were logged programmatically.
Validation: Image labels were pre-assigned prior to analysis. In cases where geographic names or landmarks could reasonably be interpreted in more than one way, a human reviewer compared the pre-labeled locations and model outputs to ensure consistent categorization.
For example, the reviewer determined whether Vatican City should be grouped with Rome and whether “Washington D.C.” and “Washington, D.C.” should be treated as the same location. The reviewer did not alter either the original labels or the model results, but instead applied judgment to reconcile ambiguous naming conventions and edge cases.
Accuracy definition: A result was counted as correct when the model identified the correct city and country. Country-only identification was tracked separately. Both metrics are reported.
What this research does not claim: This research does not suggest that every travel photo will be correctly identified, or that all publicly available AI tools perform at this level. Results varied by image type, landmark density, and geographic region. The point is not perfect identification, it’s that accuracy is high enough, and accessible enough, to enable targeted scams at scale.
About the Consumer Research McAfee commissioned a consumer survey fielded in March 2026 examining travel intentions, travel scam experiences and perceptions, and digital behaviors while traveling. Results referenced here represent a subset of 1,000 U.S. adults over the age of 18. The full study included responses from 6,000 participants across Australia, France, Germany, Japan, the United States, and the United Kingdom.
How to Protect Yourself
Knowing the risk exists is the first step. Here’s what to actually do about it.
Think before you post, especially in real time. The highest-risk window is when you’re still traveling. Posting while you’re in a location gives scammers a live signal. When possible, post after you’ve returned home or delay sharing location-identifiable content by a few days.
Audit your social media privacy settings. Photos shared publicly are the easiest targets. Restricting your posts to people you know significantly limits the pool of images that can be scraped and analyzed.
Be skeptical of urgency tied to your location. If a message references where you’ve been, even correctly, treat that as a red flag, not a credibility signal. Scammers use location familiarity precisely because it feels reassuring.
Go directly to the source. If you receive a message claiming to be from your bank, airline, hotel, or card provider while traveling, don’t click any link in the message. Open a new browser tab and navigate directly to the company’s official website, or call the number on the back of your card.
Use a travel-specific email or alias. Some travelers use a separate email address for bookings, reservations, and travel apps. This limits the cross-referencing scammers can do between your social media presence and your financial accounts.
Trust the skepticism, not the familiarity. Modern scams are designed to feel familiar before they feel suspicious. If something creates a sense of urgency around your financial accounts while you’re traveling, slow down. The pressure itself is the warning sign.
How McAfee Protects You Before, During, and After Travel
As prices rise and decisions happen in real time, it’s easy to prioritize convenience over caution. But that’s exactly the moment when small checks matter most.
Stage of Travel
What’s Happening
How McAfee Helps
Before You Book
Comparing deals, clicking promotions, booking flights and hotels under time pressure
Scam Detector checks links, messages, and booking sites before you click, helping you avoid fake deals and scam listings
During Your Trip
Connecting to public Wi-Fi, scanning QR codes, receiving travel updates and alerts
VPN helps secure your connection on public Wi-Fi, while Scam Detector flags suspicious messages and unsafe links in real time
After Your Trip
Accounts remain active, travel data stored across platforms, potential exposure from breaches
Identity Monitoring alerts you if your personal information appears online, helping you act quickly before damage spreads
With McAfee+ Advanced, multiple layers work together so you’re not left figuring it out after the damage is done.
So you can focus on your trip, and not on whether that notification is a scam.
Final Thought
A travel photo is a memory. It’s also, increasingly, a data point.
That doesn’t mean you should stop sharing your experiences. It means understanding that the same visual richness that makes a great photo is exactly what AI systems are trained to read.
Scammers know this. Now you know how to protect yourself.
This report was produced by McAfee Labs. Research was conducted in 2025–2026 as part of McAfee’s ongoing monitoring of AI-enabled scam vectors.
Millions of Americans rely on apps and online services every day to work, shop, game, and manage their lives. Scammers know that, and they’re hijacking platforms and brands you already trust.
This week, gig workers were targeted by fake DoorDash support calls designed to steal their earnings, while gamers searching for early access to Grand Theft Auto VI found fraudulent websites promising something Rockstar Games simply isn’t offering.
Here’s what happened, how these scams work, and the other cybersecurity stories making headlines this week.
The DoorDash Driver Scam That Can Empty Your Account
A growing scam targeting DoorDash drivers starts with what appears to be a normal delivery request.
According to Fox 9 in Minnesota, scammers place fake DoorDash orders, then contact drivers while they’re actively completing the delivery. Because the call often arrives during a real order and can even appear to come from DoorDash, victims may believe they’re speaking with legitimate support.
The caller typically claims there’s an issue with the order or the driver’s account and asks them to verify information or read back security codes.
Once the scammer gains access, they can change account information, lock the driver out, and redirect earnings into their own accounts. In reported cases, victims lost hundreds of dollars and temporarily lost access to the platform they depend on for income.
While today’s it’s DoorDash in the headlines, scammers are known to impersonate all types of delivery apps, so gig workers across companies should stay alert.
How the fake delivery support scams work
Step
What Happens
1
Scammers place a fake DoorDash order.
2
They call the driver pretending to be DoorDash Support.
3
They request login information or verification codes.
4
They take over the account and transfer the driver’s earnings.
Red flags every delivery driver should know
Pause if you experience:
Unexpected calls asking for verification codes
Requests to confirm login credentials
Pressure to act immediately
Anyone asking you to read a one-time authentication code over the phone
Legitimate companies generally won’t ask you to share one-time security codes. If you receive an unexpected call, end it and contact support directly through the app.
Fake GTA 6 Early Access Sites Are Everywhere
Excitement around Grand Theft Auto VI has created another opportunity for scammers.
According to Malwarebytes, fraudulent websites are claiming to sell “VIP Early Access” or exclusive versions of GTA 6 months before release. Many of the sites look polished, featuring convincing artwork, countdown timers, and professional checkout pages.
The catch? They typically require payment in cryptocurrency.
After victims pay, there’s no game to download because no legitimate early-access version exists.
How to spot a GTA 6 scam
If a website promises:
Early access before Rockstar officially releases it
Exclusive playable builds
Secret download links
Crypto-only payment
“Limited VIP access”
it’s almost certainly a scam.
Rockstar has announced pre-orders through authorized retailers. Any website claiming to provide playable access before launch should be treated with skepticism.
Other Scam and Security News This Week
Police Officer Records Live Scam Call to Show How Social Engineering Works
A police officer recorded a scam call in real time to demonstrate how quickly criminals try to establish trust, create urgency, and convince victims to share sensitive information. The recording serves as a reminder that scammers often sound calm, professional, and convincing because manipulation, not technology, is their primary weapon.
Apple supplier Tata Electronics confirmed it experienced a cybersecurity incident after a ransomware group claimed to publish more than 200,000 files allegedly connected to the company. According to Cybernews and Reuters reporting, the leaked material allegedly includes manufacturing documents and employee information tied to Apple and Tesla. Apple says it is investigating while Tata has not confirmed whether the published files originated from its systems.
Texas Parks and Wildlife Warns 3 Million Customers About Data Breach
Texas Parks and Wildlife notified roughly three million hunting and fishing license customers that personal information stored by a third-party vendor may have been accessed during a cyber incident. According to Click2Houston, exposed information may include driver’s license numbers, contact information, and mailing addresses, though officials said Social Security numbers and payment card information were not involved. Impacted customers are being offered identity monitoring.
How McAfee Can Help
With McAfee+, multiple layers work together before any damage is done:
Scam Detector flags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage
Secure VPN keeps your data private, especially on public Wi-Fi
Web Protection helps block risky sites, even if you do accidentally click
Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you
Maybe it’s a birthday gift. Maybe it’s a purchase from a major shopping event. Maybe it’s something you forgot you ordered three days ago.
Then your phone buzzes.
Your package couldn’t be delivered.There’s a problem with your shipping address.
A small fee is required before delivery can continue.
“Click here immediately.”
The message feels plausible because so many of us are constantly waiting for packages. And scammers know it.
According to McAfee’s State of the Scamiverse report, fake delivery and shipping notices are the single most commonly reported scam consumers encounter today, with 31% of people saying they’ve received one. Americans also receive an average of 14 scam messages every day across texts, email, social media, phone calls, and other channels.
Delivery scams have become one of the internet’s most successful forms of phishing because they exploit something simple: people are already expecting the message.
Here’s how to spot and stop these scams:
What Is a Delivery Scam?
A delivery scam is a fraudulent message that pretends to come from a shipping company, retailer, postal service, or delivery provider.
The goal is usually one of three things:
Steal personal information
Steal financial information
Trick victims into downloading malware or visiting malicious websites
These scams often impersonate organizations such as:
USPS
UPS
FedEx
DHL
Amazon
Royal Mail
Australia Post
Other local or regional delivery services
Most delivery scams arrive through text messages, which is why they’re often called package smishing scams.
What Is Smishing?
Smishing is a type of phishing attack delivered through SMS text messages.
The term combines:
SMS (Short Message Service)
Phishing
Instead of arriving through email, the scam arrives directly on your phone and attempts to create a sense of urgency that encourages immediate action.
Common examples include:
“Your package could not be delivered.”
“Delivery attempt failed.”
“Update your shipping address.”
“Pay a small customs fee.”
“Confirm delivery information.”
McAfee’s Scam Detector lets you know when delivery messages are scams.
Delivery Scam Red Flags and What to Do
If You See This Red Flag
Why It’s Suspicious
What To Do
A package alert when you’re not expecting a delivery
Scammers send messages in bulk hoping someone is waiting for a package
Ignore the message and do not click links
A request to pay a small fee before delivery
Legitimate carriers rarely collect delivery fees through text messages
Visit the carrier’s official website directly
A message claiming your address needs verification
Common tactic used to steal personal information
Check shipment status through your retailer or carrier account
A shortened or unusual link
Scammers often disguise malicious websites
Avoid clicking and manually type the carrier’s website address
Pressure to act immediately
Urgency is designed to override caution
Pause and verify independently
Requests for passwords, payment information, or verification codes
Legitimate carriers will not ask for this through text messages
Delete the message and report it as spam
A delivery app or file download request
May install malware on your device
Never download software from a text message
Accidentally Clicked a Delivery Scam? Do This Immediately
What Happened
What To Do
You only clicked the link
Close the page and do not enter any information
You entered login credentials
Change your password immediately and enable two-factor authentication
You entered payment information
Contact your bank or credit card provider right away
You downloaded a file or app
Delete it and run a security scan
You’re unsure what information was exposed
Monitor accounts closely for unusual activity
How McAfee Can Help
With McAfee+, multiple layers work together before any damage is done:
Scam Detector flags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage
Secure VPN keeps your data private, especially on public Wi-Fi
Web Protection helps block risky sites, even if you do accidentally click helps block risky sites, even if you do accidentally click
Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you
Last week, McAfee warned that economic pressure and AI are creating ideal conditions for online shopping scams.
This week, that warning got another real-world example.
New reporting revealed that cloned shopping websites have appeared in AI-generated search results, potentially directing consumers to convincing fake storefronts designed to steal payment information and personal data.
The incident reinforces what McAfee’s latest research found ahead of Prime Day: shoppers are moving faster, trusting deals more readily, and encountering increasingly sophisticated scams.
Before the summer’s biggest shopping events kick into high gear, let’s get into the sales and Prime Day scams to be aware of and other cybersecurity news making headlines This Week in Scams.
The Top 7 Shopping Scams to Watch for This Prime Day
McAfee’s latest research found consumers most frequently encounter the following scams during major sales events:
Fake shipping confirmations and order updates (34%)
Delivery company impersonation scams (32%)
Requests for payment or account information (27%)
Suspicious account verification alerts (26%)
Retailer impersonation scams (25%)
Fake urgency and expiring deal messages (24%)
Suspicious discount codes and flash-sale offers (22%)
These scams work because they exploit moments when consumers are already expecting packages, tracking orders, comparing prices, and making quick purchasing decisions.
Prime Day Shopping Safety Checklist
In McAfee’s new consumer research, 40% of Americans surveyed said they would trust a lower priced deal without verifying it. That means as costs are climbing, shoppers are less likely to second guess a too-good-to-be-true deal that could be a scam.
“What the data reflects is that economic pressure has effectively done some of the scammer’s work for them,” says McAfee’s Head of Threat Research Abhishek Karnik.
“When consumers are already primed to move quickly and prioritize price over authenticity, it takes far less effort to push them toward a bad click or a fraudulent purchase.”
And reporting that fake shopping sites have appeared in ChatGPT results shows that scammers are adapting to ensure they show up wherever consumers search for products, including AI-powered search experiences.
That means it’s more important than ever for shoppers to know the red flags, common scams, and protection measures to find deals safely.
Safety Checklist
Before making a purchase:
✓ Verify the website URL
✓ Compare prices across multiple retailers
✓ Research unfamiliar sellers
✓ Be skeptical of discounts exceeding 50-70%
✓ Never trust a shopping link sent by text
✓ Use a credit card instead of bank transfer, crypto, or gift cards
✓ Check independent reviews
✓ Verify shipping alerts directly through the retailer
Other Scam and Security News This Week
Nintendo Investigates Third-Party Employee Data Incident
According to Kotaku, Nintendo is investigating an alleged data exposure involving TinyPulse, a third-party employee survey platform. An extortion group claiming responsibility for the incident says it possesses employee information and internal communications and demanded a $2 million ransom. Nintendo said its own systems were not compromised and that no customer financial or payment information was accessed.
Madison Square Garden Data Allegedly Posted Online
According to 404 Media, hackers linked to the ShinyHunters group have allegedly published data stolen from Madison Square Garden after an extortion attempt. Sample files reviewed by the outlet reportedly contained personal information, talent records, and contact details connected to sports personalities and business operations.
Novo Nordisk Reports Clinical Trial Data Breach
According to Yahoo Finance, Novo Nordisk disclosed a data breach involving individuals participating in clinical trials. The company is currently assessing the scope of the exposure while also managing ongoing supply constraints affecting its GLP-1 medications, including Wegovy.
How McAfee Can Help
With McAfee+ Premium, multiple layers work together before any damage is done:
Scam Detector flags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage
Secure VPN keeps your data private, especially on public Wi-Fi
Web Protection helps block risky sites, even if you do accidentally click helps block risky sites, even if you do accidentally click
Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you
Most people think a data breach starts with a hacker breaking into a system.
In reality, and in many cases, it starts with human error or oversight.
This week, cloud software giant ServiceNow disclosed that a software flaw allowed some customer data to be accessed without authentication, potentially exposing information that should never have been publicly available.
The incident is a reminder that your personal information can be put at risk even when cybercriminals aren’t directly responsible.
Here’s what happened and our other This Week in Scams news:
ServiceNow Bug Left Customer Data Exposed
ServiceNow, one of the world’s largest enterprise software providers, recently notified some customers that a software bug allowed unauthorized access to data stored on parts of its platform.
According to reporting by TechCrunch, the flaw could have allowed individuals to access customer data without needing credentials such as a username or password.
The company says the activity was identified by security researchers participating in vulnerability research rather than malicious hackers. ServiceNow told TechCrunch it found no evidence that bad actors were responsible for the observed activity and said researchers reported the issue through responsible disclosure channels.
The company patched affected systems on June 5 and launched an investigation into the scope of the exposure.
Why This Matters
For consumers, this story highlights an important cybersecurity reality: not every data exposure is the result of a criminal attack.
Sometimes information becomes accessible because of:
Software bugs
Misconfigured cloud systems
Human error
Security settings that fail to work as intended
In this case, ServiceNow says the issue stemmed from a platform vulnerability rather than a breach by threat actors.
However, the outcome can look similar from a customer’s perspective. Information that was intended to remain private may have been accessible to unauthorized parties.
That’s why it’s important to pay attention to security notifications from companies you do business with, even when reports emphasize there was “no hack.”
What You Should Do After Any Data Exposure
Whether a company reports a breach, a vulnerability, or an accidental exposure, the recommended steps are often similar:
Watch for notifications from the affected company.
Change passwords if requested.
Enable multi-factor authentication where available.
Monitor financial and online accounts for unusual activity.
Be alert for phishing emails and scam calls referencing the incident.
Cybercriminals frequently use news of data exposures to launch follow-up scams targeting affected customers.
Here are some other pieces of cybersecurity news making headlines this week.
Veterans Warned About Fake Benefits Postcard Scam
The Department of Veterans Affairs is warning veterans about fraudulent postcards claiming recipients qualify for additional VA benefits, including healthcare, dental coverage, and other payments.
The postcards often create urgency, encouraging recipients to call within a few days. Once contact is made, scammers attempt to build trust and collect sensitive information such as Social Security numbers, bank account details, and other personal data.
The VA says veterans should avoid calling numbers listed on unsolicited mailers and should independently verify benefit information through official VA channels.
Image: Example Fraudulent Notice Courtesy of Shenandoah County Sheriff’s Office
The scam follows a familiar pattern. The supposed parent sends a check in advance that exceeds the expected payment amount and then asks for the difference to be returned through a payment app, wire transfer, gift card, or another method.
The problem is that the original check is fake.
Even if the money initially appears in a bank account, the check can later be reversed, leaving the childcare provider responsible for the loss.
If someone sends a check and asks you to send part of the money back, that’s one of the clearest warning signs of a fake check scam.
Microsoft Investigates Open Source Supply Chain Attack
Microsoft temporarily removed dozens of open source repositories hosted on GitHub after discovering malicious code had been inserted into software projects used by developers.
According to reports, the malware was designed to steal passwords and other credentials from users working with AI development tools and cloud services.
Researchers describe the incident as a supply-chain attack, a type of compromise where attackers target trusted software that may later be downloaded by thousands of users.
Microsoft says it has notified a limited number of potentially affected customers.
McAfee Safety Tips This Week
Not every security incident starts with a hacker.
Sometimes it’s a bug. Sometimes it’s a fake postcard. No matter how a scam starts, here are a few ways to stay safer:
Verify benefit and financial information through official channels.
Be skeptical of urgent requests involving money or personal information.
Avoid downloading software promoted through social media tutorials.
Never send money back to someone who claims they accidentally overpaid you.
Enable multi-factor authentication on important accounts.
Watch for phishing emails following major breach or exposure announcements.
How McAfee Protects Your Identity and Privacy
McAfee is built to stop threats before your identity, accounts, or money are compromised.
McAfee is proud to be recognized with the SE Labs Home Anti-Malware Award 2026, one of the most respected independent recognitions in consumer cybersecurity. This marks the second year in a row that McAfee is being recognized with the Home Anti-Malware Award, proving our continued excellence and efficiency.
Now in its eighth year, the SE Labs Awards honor cybersecurity providers delivering outstanding protection across consumer, small business, and enterprise markets. And McAfee has earned top recognition in the Home Anti-Malware category two years in a row.
What Are the SE Labs Awards?
SE Labs is an independent cybersecurity testing and certification organization. Unlike awards based on self-reported data or marketing claims, SE Labs recognition is grounded in:
Continuous public testing: Products are evaluated through ongoing, real-world assessments, not one-time snapshots
Private assessments: Winners are also evaluated through confidential testing that mirrors actual threat environments
Eight years of credibility: The SE Labs Awards have built a track record as a trusted benchmark for both consumers and industry professionals
This makes the SE Labs Award a comprehensive measure of real-world security performance, not just lab scores.
What the Home Anti-Malware Award Means
The Home Anti-Malware category specifically recognizes consumer security products that demonstrate exceptional ability to detect, block, and remedy malware threats targeting everyday users.
Winning this award means McAfee’s protection performed at a level SE Labs considers outstanding, not just effective on paper, but proven against the kind of threats real households face: ransomware, trojans, spyware, phishing-delivered payloads, and more.
Simon Edwards, Founder and CEO of SE Labs, offered this comment on the 2026 winners:
“The SE Labs Awards recognises the vendors that are making a real difference in keeping systems secure. Winning an award is a significant achievement. It reflects not only strong product performance in our tests but also the commitment of the teams behind the technology. Congratulations to McAfee on its success.”
Independent Validation. Not a Marketing Claim
There’s an important distinction between a company saying its product is effective and an independent lab proving it.
SE Labs operates separately from the vendors it tests. Its methodology is transparent, its testing is repeatable, and its results are used by journalists, analysts, and buyers to make real purchasing decisions.
When SE Labs names McAfee a winner, that recognition carries the weight of a process that can’t be paid for or manufactured.
That’s what makes this award meaningful, and what separates it from a badge a company designs for itself.
How McAfee Fights Malware
Malware today doesn’t just arrive as a suspicious download. It hides in phishing texts, fake links, malicious QR codes, and compromised websites. And by the time most people realize something is wrong, the damage is already done.
McAfee is built to stop threats at every point in that chain.
Scam Detector flags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage
Secure VPN keeps your data private, especially on public Wi-Fi
Web Protection helps block risky sites, even if you do accidentally click
Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you

 Login

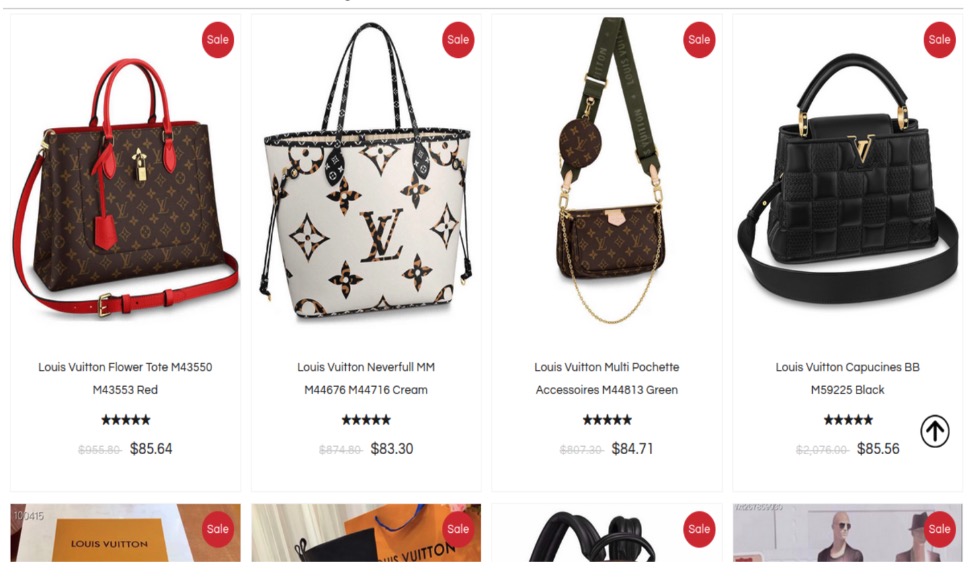
 The breach affected customer information from bookings and airport Wi-Fi registrations.
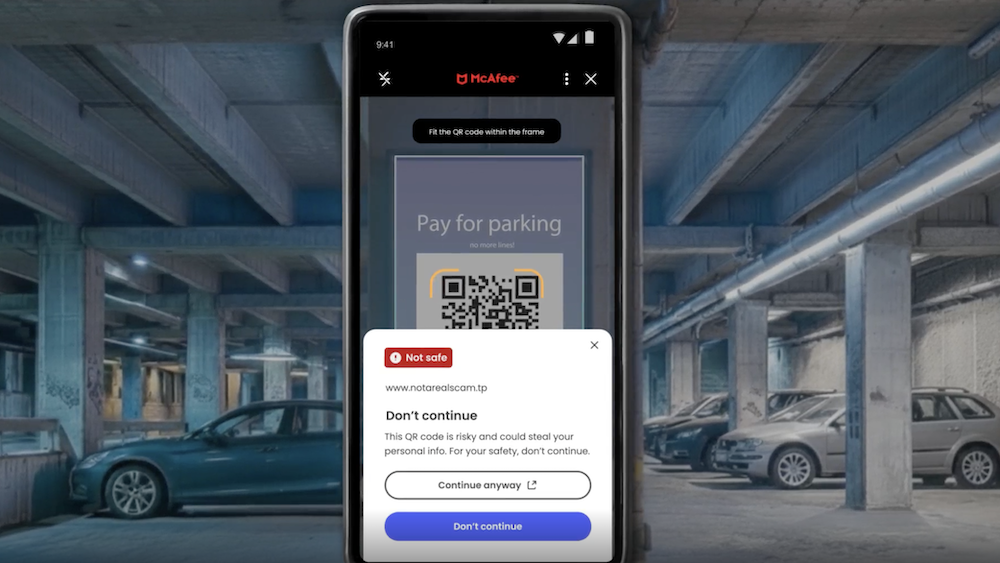
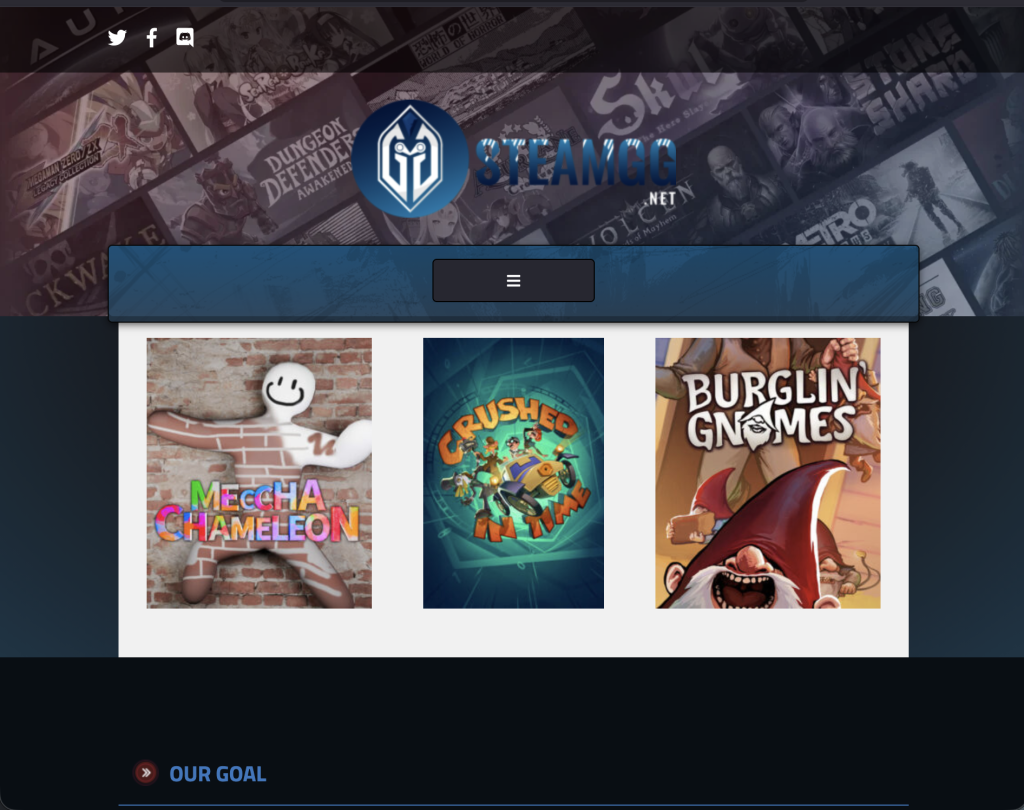
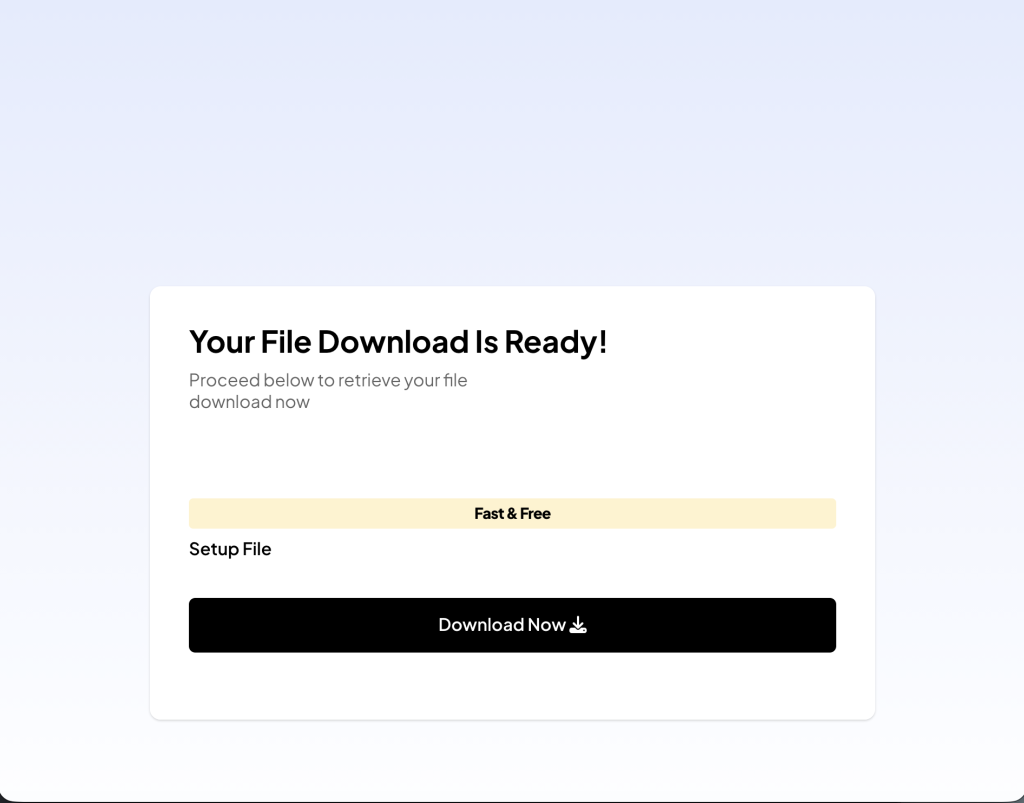
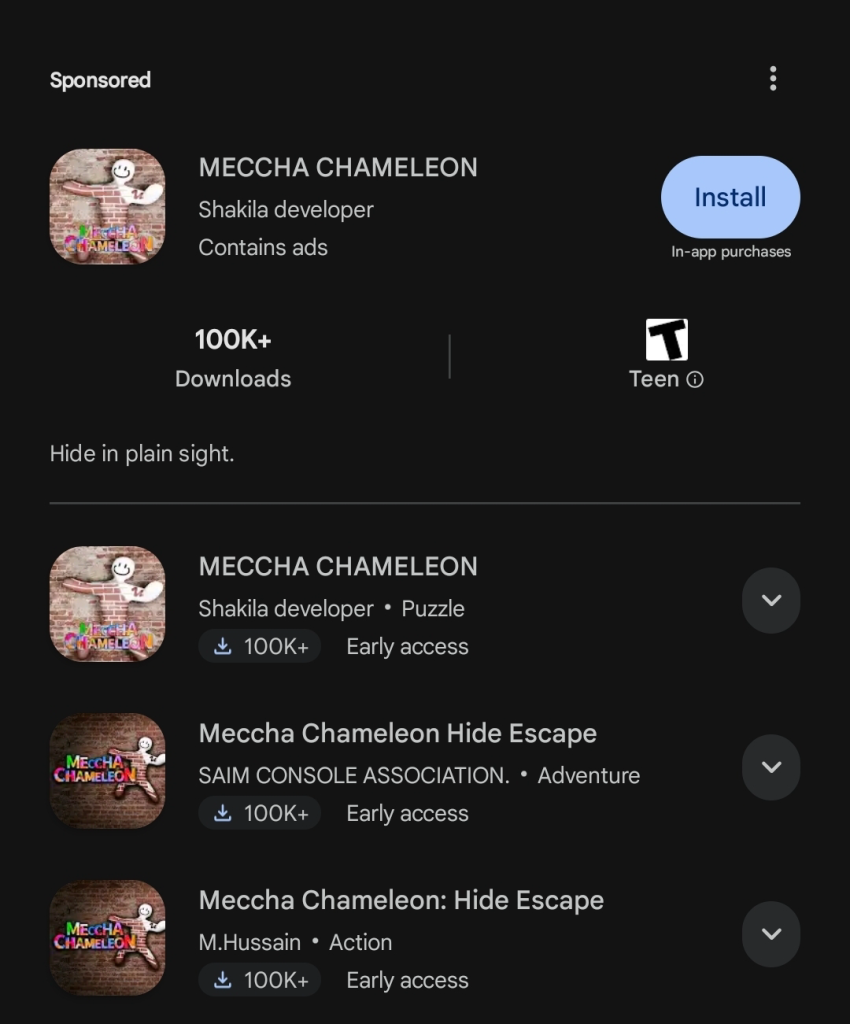
 The attack reportedly lasted about four and a half days and involved roughly