Reading view

Who Runs the Ransomware Group ‘The Gentlemen?’

A cybercrime group known as The Gentlemen has emerged as the second most active ransomware gang by victim count, rapidly attracting a talented pool of hackers through an aggressive recruitment strategy that promises affiliates 90 percent of any ransom paid by victims. This post examines clues pointing to a real life identity for the administrator of The Gentlemen ransomware group.

A graphic created and shared by The Gentlemen ransomware group administrator Hastalamuerte on Breachforums in May 2026. Credit: ke-la.com.

Experts at the security firm Check Point Software have been closely covering exploits of The Gentlemen, a so-called “ransomware-as-a-service” (RaaS) offering that pays affiliates handsomely to help spread the group’s malware.

“A 90/10 affiliate revenue split — compared to the industry standard 80/20 — is accelerating the group’s growth by attracting experienced operators from competing programs,” the researchers wrote in April.

Check Point found The Gentlemen are the second most active ransomware group by victim count so far this year, claiming at least 332 published victims since the group’s inception in mid-2025 and more than 240 in 2026 alone.

According to Check Point, the group targets Internet-facing devices (VPNs, firewalls) as their entry point, and once inside moves quickly to encrypt entire networks within hours.

Check Point says the administrator and primary operator of the ransomware group uses the nickname Zeta88 on the Russian-language cybercrime forums, and that this individual was previously known under the moniker Hastalamuerte. Check Point noted that a breach of the group’s backend infrastructure made it clear that Hastalamuerte/Zeta88 is the person who assembles the locker and RaaS panel, manages payments, and is essentially the administrator of the entire program who receives 10 percent of all ransoms.

WHO IS HASTALAMUERTE?

The cyber intelligence firm Intel 471 shows that the user Hastalamuerte is a Russian and English speaking person who registered on almost a dozen cybercrime forums between 2019 and the present day, including Exploit, Breachforums, Ramp_V2, BHF, Raidforums, and Nulled.

Intel 471 reveals that Hastalamuerte registered on Breachforums in January 2025 from an Internet address in Izhevsk, the capital city of Russia’s Udmurt Republic. Likewise, the user Zeta88 signed up at the English-language cybercrime forum Breached in August 2022 from a different Internet address in Izhevsk.

Intel 471 finds Hastalamuerte registered on Raidforums in 2020 using the email address hastalamuerte1488@protonmail.com (1488 is a common combination of two numeric symbols associated with white supremacy). A lookup on this address at the open source intelligence service Epieos shows it is connected to an account at Apple and to a phone number ending in 04.

Epieos says that Protonmail address is also linked to a GitHub account under the username SantaMuerte. That account is marked private, but a history of this user’s activity shows they are watching and developing a number of malware tools and exploits.

In April 2020, Hastalamuerte said on the crime forum Nulled that they could be contacted at the Telegram instant messenger name @hastalamuerte18, and the threat intelligence company Flashpoint finds this username is assigned the unique Telegram ID number 30907522 [full disclosure: Flashpoint is an advertiser on this blog].

The breach tracking service Constella Intelligence reports that Hastalamuerte’s Telegram ID is connected to another username — “bu4vs” — and to the Russian phone number 79127650004. Pivoting on this phone number in Constella fetches multiple records from hacked Russian government databases showing it is assigned to one Alexander Andreevich Yapaev, a 36-year-old from Izhevsk.

Constella reveals that phone number was used to create an account at the Russian social media platform Pikabu under the name “4apai18,” and shows Mr. Yapaev has signed up at a number of websites using the common surname Ivanov, or else “Chapaev” (the numeral 4 is often used as shorthand for a “ch” sound in Russian).

A search in Intel 471 for cybercrime forum members with the nickname SantaMuerte unearths an account by the same name created in 2020 on the Russian hacking forum Codeby. Intel 471 shows this user originally registered on Codeby with the not-so-subtle nickname Alexandr 4apaev.

Constella finds Mr. Yapaev regularly used the email address bu4vs@mail.ru. Meanwhile, Epieos shows this address is connected to a LinkedIn account for Alexander Yapaev, who lists himself as the head of B2B marketing at the company Uralenergo Udmurtia, one of Russia’s largest suppliers of electrotechnical and lighting products.

Mr. Yapaev did not respond to multiple requests for comment.

Nearly every time we publish one of these Breadcrumbs stories, readers are curious to know why it seems like so many cybercriminals from Russia apparently do little to hide their real life identities. The truth is that — Russian or not — most didn’t exactly set out to be arch criminals, but instead got drawn into the scene gradually over several years as their skills broadened and sharpened.

Another important dynamic is that the Russian government generally either co-opts or ignores cybercriminal activity within its borders so long as the hackers do not steal from or attack Russian businesses and citizens. As a result, successful cybercriminals in Russia are usually insulated from prosecution and arrest by foreign law enforcement agencies provided they occasionally pay off the right people and do not travel abroad. And cybercriminals who intend to strictly adhere to those unwritten rules may (at least initially) be less concerned about covering their tracks online.

But the simplest explanation is that cybercriminals of all nationalities tend to make a number of basic operational security mistakes early in their careers, when they are less savvy and have far less to lose by their carelessness. A review of Hastalamuerte’s early posts on the crime forums (circa 2019-2020) shows a relatively unsophisticated and low-skilled hacker still trying to learn the ropes and earn a positive reputation on these communities.

For example, in June 2020 Hastalamuerte’s Telegram account joined a multi-month training program (@pntst) to learn how to use popular penetration testing tools, and their candid posts to this hacker training camp show Hastalamuerte struggling to use these tools effectively. A Google-translated record of Hastalmuerte’s posts to @pntst is here.

Update, June 11, 10:23 a.m. ET:  The threat research group PRODAFT has released a detailed writeup on the history and current operations of The Gentlemen. PRODAFT said its findings match the same persona with “high confidence,” and found the administrator (Zeta88/Hastalamuerte) supplies affiliates with initial access directly, primarily Fortinet SSL-VPN credentials obtained through brute-force attacks or sourced from the group’s own leak database. They also discovered the administrator is using AI to develop and maintain the ransomware and associated tooling, as well as to assist with post-exploitation activity.

  •  

Weekly Update 507

Weekly Update 507

1,000 breaches is one hell of a milestone. It's not just the process of getting data, verifying it, loading it, sending notifications etc, it's all the other stuff that goes into keeping the whole thing afloat. Legal docs. Trademarks. Accounting. Agreements. The most mind-numbingly boring stuff you can imagine happening in the background so that the stuff you see in the foreground can all work. And then there are those "other things" I had to deal with along the way, but more of that in this week's video. Thanks to everyone who has stuck around to see this thing reach such a milestone 🙏

Weekly Update 507
Weekly Update 507
Weekly Update 507
Weekly Update 507
  •  

A Record-Breaking Patch Tuesday for June 2026

Microsoft today released software updates to plug nearly 200 security holes across its Windows operating systems and supported software, a record number of fixes for the company’s monthly Patch Tuesday cycle. Nearly three dozen of those bugs earned Microsoft’s most dire “critical” rating, and exploit code for at least three of the weaknesses is now publicly available.

The software giant said in a blog post last month that both its engineers and the security community are increasing using artificial intelligence tools to find bugs, meaning this month’s heavy Patch Tuesday may start to become the norm, said Satnam Narang, senior staff research engineer at Tenable.

“Some surveys put AI usage among security professionals generally at 90%, so it’s unsurprising that this volume of patches may be the norm,” Narang said. “Pandora’s proverbial box has been opened, and as more advanced AI models become available, we expect the norm to continue upward across the board, not just for Patch Tuesday.”

June’s zero-day bugs include CVE-2026-49160, a denial of service vulnerability affecting a range of web servers, including Microsoft Internet Information Services (IIS). Microsoft says the flaw was reported by OpenAI’s Codex.

Two of the zero-days addressed this month appear to stem from recent vulnerability disclosures by Nightmare Eclipse, the nickname chosen by a security researcher who has been dropping exploits for various Windows flaws. One of those, dubbed “GreenPlasma,” leverages an elevation of privilege weakness in the Windows Collaborative Translation Framework, the same framework patched today in CVE-2026-45586.

Nightmare Eclipse also last month released “YellowKey,” an exploit for a Windows BitLocker vulnerability that allows an attacker with physical access to view encrypted data, and CVE-2026-50507 is a patch for an elevation of privilege bug in BitLocker.

Microsoft received heavy blowback on social media last month after it said in a blog post that it was considering taking legal action against the security researcher. The company later clarified on Twitter/X that while it has no intention of pursuing legal actions against researchers, it would report them to authorities if they break the law. The advisories for CVE-2026-49160 and CVE-2026-50507 do not credit any researchers in the acknowledgement section, saying only that “Microsoft recognizes the efforts of those in the security community who help us protect customers through coordinated vulnerability disclosure.”

Nightmare Eclipse claims to be a former employee of Microsoft, although Microsoft has not responded to questions about this claim. Rapid7 notes that a recent blog post by Nightmare Eclipse included an image of Albert Wesker, a character from the Resident Evil video game series who formerly worked as a researcher for a technology company before going rogue.

Nightmare Eclipse has pledged to release even more zero-day exploits for Windows in what they called a “bone shattering” drop planned for July 14 (the same day as next month’s Patch Tuesday). Immediately following the release of Microsoft patches today, the researcher published an exploit for what they claimed was a zero-day bug in Windows Defender.

While 200 vulnerabilities may be a record for Patch Tuesday, the actual number of security flaws Microsoft addressed this month is far higher, said Rapid7’s Adam Barnett.

“So far this month, Microsoft has provided patches to address 360 browser vulnerabilities, which is an order of magnitude more than has been typical in any given month over the past few years,” Barnett wrote. “As usual, browser [flaws] are not included in the Patch Tuesday count above. Indeed, the vast, and presumably sustained, uptick in the number of browser vulnerabilities has led to Microsoft no longer enumerating Chromium CVEs in the Security Update Guide.”

Microsoft also patched a zero-day vulnerability in Visual Studio Code that allows attackers to steal GitHub tokens with a single click. The company was forced to push a stopgap fix for the flaw on June 3, after a researcher published instructions showing how to exploit it. The researcher said they opted not to work with Microsoft because of a recent experience wherein Redmond silently patched a flaw they reported without offering credit or recognition.

Microsoft battled its own internal zero-day emergencies last week, after at least 72 of the company’s public code repositories were infected with a variant of the Shai-Hulud worm. Researchers found that all of the affected packages were connected to Microsoft official Azure Durable Task SDK, which got hit by the same Shai-Hulud worm in May.

Other major software makers are also shipping outsized update bundles this month. Adobe has released updates to fix a massive number of critical vulnerabilities across a range of products, including Adobe Experience Manager, Acrobat Reader and Cold Fusion. On June 3, Google resolved a whopping 429 vulnerabilities in its latest Chrome browser update (Chrome automatically downloads updates but installing them usually requires a complete restart of the browser).

As ever, please consider backing up your data before applying operating system updates, and drop a note in the comments if you run into any problems with this month’s patches.

Further reading:

Microsoft’s Security Update Guide

Action1’s Patch Tuesday breakdown

SANS Internet Storm Center notes on Patch Tuesday

  •  

Security in the Post-Mythos Era

Discover how AI-driven vulnerability discovery is reshaping the cybersecurity landscape. Learn why foundational hardening and proactive threat detection are now essential for defending against zero-day threats in the post-AI era.
  •  

New Research: Rising Costs Are Driving Consumers to Ignore Scam Instincts for Better Deals

Most people don’t get scammed because they ignore warning signs. 

They get scammed because they find a reason to explain those warning signs away. 

The website looks a little off, but the deal is incredible. The text message is unexpected, but they’re already waiting for a package. The seller is unfamiliar, but the discount is too good to pass up. 

That’s what makes major shopping events such fertile ground for scammers.  

New McAfee research suggests that economic pressure may be making that problem worse, as 40% of consumers say they would trust a lower priced deal without verifying it. That means as costs are climbing, shoppers are less likely to second guess a too-good-to-be-true deal that could be a scam. 

“Anyone who has ever fallen for a scam thought they would recognize one first,” McAfee’s Head of Threat Research Abhishek Karnik reminds shoppers. 

“That confidence is part of what scammers count on,” he says. “Tools like McAfee exist precisely for those moments, flagging suspicious links, messages, and offers in real time, before a split-second decision becomes a costly one.” 

New McAfee Research Reveals the Cost of Deal Hunting 

While most shoppers believe they can spot a scam, McAfee’s new research suggests many are engaging in behaviors that increase their risk. 

Rising Prices Are Driving Riskier Shopping Decisions 

Economic pressure is changing how people shop online. 

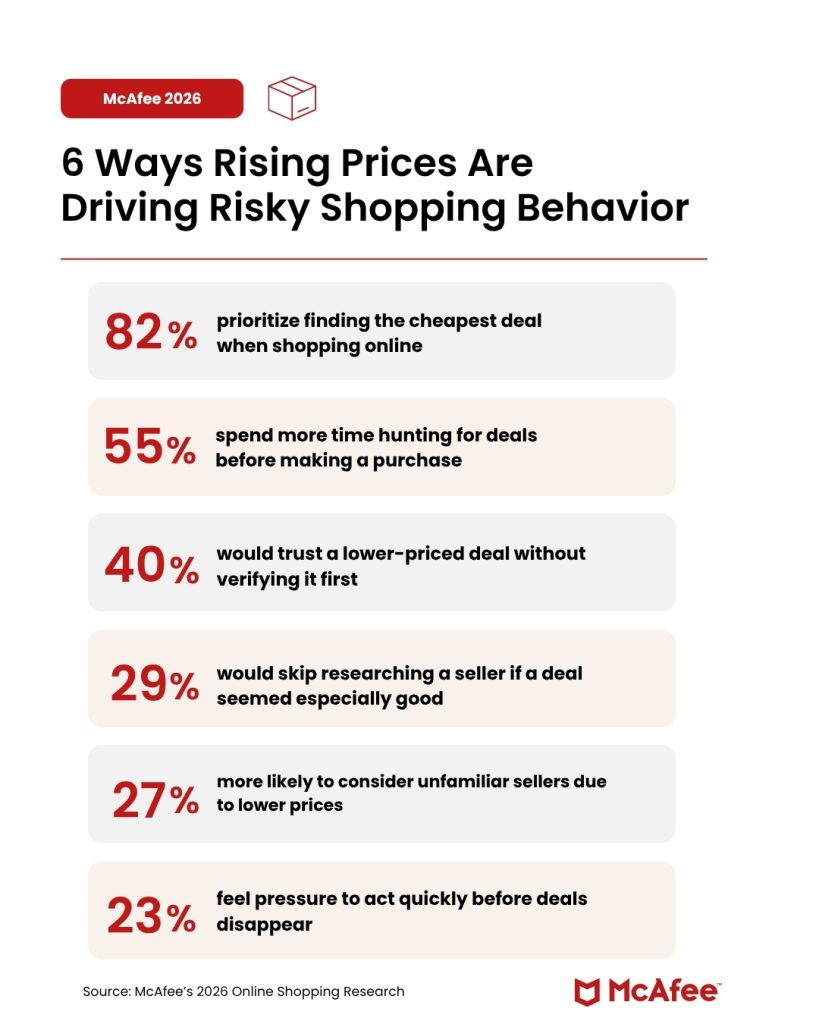
McAfee found: 

  • 82% prioritize finding the cheapest deal when shopping online 
  • 55% spend more time hunting for deals 
  • 40% would trust a lower-priced deal without verifying it first 
  • 29% would skip researching a seller if the deal seemed especially good 
  • 27% are more likely to consider unfamiliar sellers because of lower prices 
  • 23% feel pressure to act quickly before deals disappear 

The same behaviors that help shoppers find bargains can also make them more vulnerable to fraud. 

“What the data reflects is that economic pressure has effectively done some of the scammer’s work for them,” says Karnik. “When consumers are already primed to move quickly and prioritize price over authenticity, it takes far less effort to push them toward a bad click or a fraudulent purchase.” 

Infographic, 6 ways rising prices are driving risky shopping behavior

Shopping Scams Are Already Costing Americans Real Money 

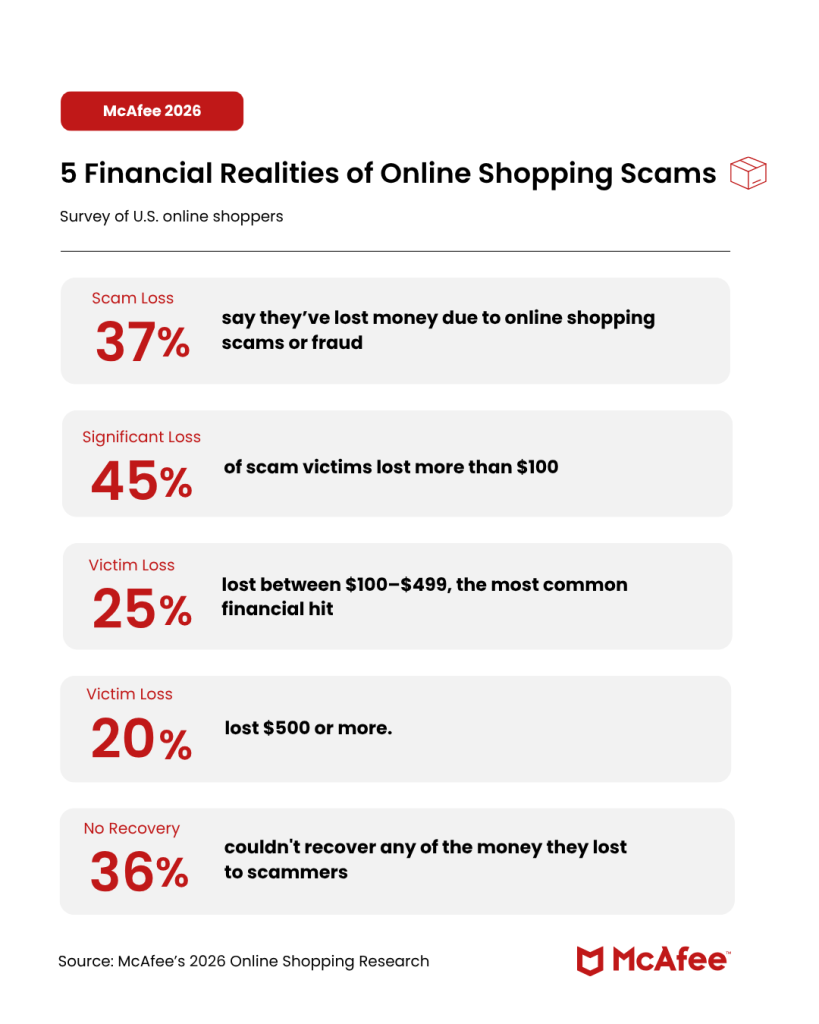
The financial impact is significant: 

  • 37% say they have lost money due to online shopping scams or fraud 
  • 45% of victims lost more than $100 
  • 25% lost between $100 and $499 
  • 20% lost $500 or more 
  • 36% were unable to recover any of their money 
5 financial realities of online shopping scams infographic

AI Is Making Shopping Scams Harder to Spot 

Consumers are increasingly aware that artificial intelligence is changing the scam landscape. 

According to McAfee research: 

  • 70% agree AI-generated content is making shopping scams harder to identify 
  • Nearly three-quarters have encountered shopping content they believed was suspicious or AI-generated 

“The signs people have historically relied on, poor grammar, low-quality images, obviously off branding, are no longer reliable,” advises Karnik. “AI has lowered the production cost of a convincing fake to nearly zero.” 

It’s not just a fake landing page fraudsters are creating.  

“AI is being used to make fake review sections, impersonation messages that look exactly like it came from a major retailer, realistic logos, believable URLS,” Karnik says. “When you’re shopping online, you need to adjust your expectations to match that new AI reality.” 

What Are the Most Common Shopping Scams During Major Sales Events? 

Scammers follow consumer attention. 

Whenever millions of people are searching for deals at the same time, scammers create fake websites, impersonate retailers and delivery companies, and use urgency to pressure shoppers into acting before they think. 

Here are some of the most common shopping scams consumers encounter during major sales events, as well as the red flags consumers can watch for: 

Scam Type  How It Works  Red Flags 
Fake shopping websites  Fraudulent websites mimic real retailers and disappear after collecting payments  Prices far below competitors, little company information, newly created websites 
Fake social media ads  Ads promote products that never arrive or are counterfeit  Too-good-to-be-true discounts, limited reviews, unfamiliar brands 
Delivery notification scams  Fake package alerts claim there is an issue with your shipment  Unexpected texts, suspicious links, requests for payment 
Retailer impersonation scams  Messages claim there is a problem with your account or order  Urgent language, login requests, unfamiliar sender addresses 
QR code scams  QR codes redirect shoppers to fraudulent websites  Codes placed on flyers, posters, packages, or public locations 
Brushing scams  Unsolicited packages arrive at your home  Items you never ordered, requests to scan codes or leave reviews 
Fake recall scams  Messages claim a recent purchase has been recalled  Requests for payment, account credentials, or personal information 

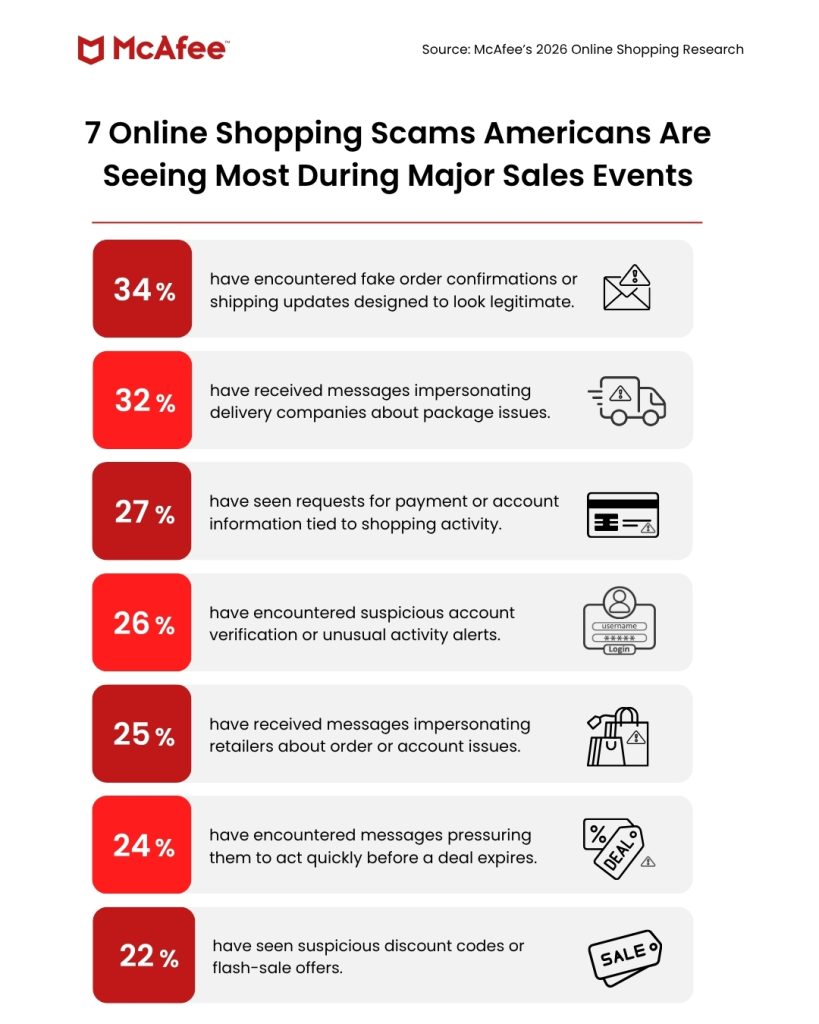
 According to McAfee research, consumers most commonly report encountering fake shipping notifications, delivery scams, retailer impersonation scams, account alerts, and suspicious discount offers during major shopping periods. 

How McAfee Can Help 

With McAfee+ Premium, multiple layers work together before any damage is done:  

  • Scam Detector flags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage 
  • Secure VPN keeps your data private, especially on public Wi-Fi  
  • Web Protection helps block risky sites, even if you do accidentally click  helps block risky sites, even if you do accidentally click   
  • Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you
  • Device Security helps detect malicious apps or downloads   
  • Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast   
  • Personal Data Cleanup helps remove your information from sites selling it. 
  • Online Account Cleanup assists in taking down your old, forgotten accounts across the web 
  • Social Privacy Manager helps you monitor and change privacy settings across your social platforms in just a few clicks 

Together, these protections are designed to address the broader range of online risks people face every day. 

Plus, click here to get McAfee’s limited-time deals on real-time protection this Amazon Prime Day, from June 23 to June 26.

About our consumer research 

McAfee surveyed 1,000 U.S. adults in May 2026 as part of a broader study of 5,000 respondents across the U.S., UK, France, Germany, and Japan, focused on online shopping intentions, scam awareness, and purchase behaviors. 

The post New Research: Rising Costs Are Driving Consumers to Ignore Scam Instincts for Better Deals appeared first on McAfee Blog.

  •  

GTA Cheat Users Exposed in Breach as Minecraft Malware Hits 116,000 Players

One gaming cyberattack this week exposed nearly 64,000 users. 

Another has already infected more than 116,000 players.  

Both are connected by the same common gaming behavior: looking for a cheat, mod, or shortcut. 

This week in scam news, a popular Grand Theft Auto V cheat service was hacked, exposing tens of thousands of users. At the same time, McAfee researchers uncovered a massive malware campaign spreading through fake Minecraft mods, cheats, and game clients. 

The takeaway is simple: some of the biggest threats facing gamers aren’t happening inside games. They’re hiding in the downloads, websites, and tools players use around them. 

Let’s start with the GTA breach. 

GTA Cheat Service Breach Exposes Nearly 64,000 Users 

Atlas Menu, a cheat service for Grand Theft Auto V, was reportedly hacked, exposing data belonging to nearly 64,000 users. 

According to reports, the leaked information included: 

  • Email addresses 
  • Usernames 
  • Scrambled passwords 
  • IP addresses 
  • Customer support tickets

The hacker who claimed responsibility later posted the data online. 

Why This Matters 

Many players think of cheats as harmless tools that unlock special abilities, provide advantages, or simply make games more entertaining. 

But unofficial cheat services often operate outside the protections offered by legitimate gaming platforms. 

That means users may be: 

  • Sharing personal information with unknown developers 
  • Downloading unverified software 
  • Exposing themselves to malware 
  • Putting gaming accounts at risk 

And that brings us to an even bigger threat. 

Minecraft Malware Campaign Has Already Infected 116,000 Players 

McAfee researchers recently uncovered a large-scale malware operation targeting gamers searching for Minecraft mods, clients, and cheats. 

The campaign is called WeedHack. 

What Is WeedHack? 

WeedHack is a type of Malware-as-a-Service (MaaS). 

That means cybercriminals package malware into a subscription service that other attackers can use. 

Researchers found that: 

  • More than 116,000 victims have been infected since January 
  • The campaign continues to add roughly 2,000 to 3,000 new victims every day 
  • More than 3,800 malicious files have been identified 
  • More than 240 malicious download URLs have been linked to the operation 

Premium versions reportedly cost as little as $5 per month and include tools that allow attackers to remotely access victims’ devices and webcams. 

What WeedHack Can Steal 

Once installed, the malware can collect: 

  • Minecraft account credentials and session IDs 
  • Discord, Steam, and Telegram credentials 
  • Browser passwords and cookies 
  • Cryptocurrency wallet information 
  • Screenshots and device information 
  • Files stored on a victim’s computer 

Premium versions can also provide: 

  • Live webcam access 
  • Live screen sharing 
  • Remote keyboard and mouse control 
  • Keylogging capabilities 
  • Full remote access to the infected device

Get the full explainer here. 

How McAfee+ Advanced Helps Protect Gamers 

Gaming malware campaigns rely on three things: 

  1. Getting users to visit malicious websites 
  2. Convincing them to download infected files 
  3. Encouraging them to ignore security warnings  

With McAfee+ Advanced, multiple layers work together before any damage is done:  

  • Scam Detector flags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage 
  • Secure VPN keeps your data private, especially on public Wi-Fi  
  • Web Protection helps block risky sites, even if you do accidentally click  helps block risky sites, even if you do accidentally click   
  • Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you
  • Device Security helps detect malicious apps or downloads   
  • Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast   
  • Personal Data Cleanup helps remove your information from sites selling it. 
  • Online Account Cleanup assists in taking down your old, forgotten accounts across the web 
  • Social Privacy Manager helps you monitor and change privacy settings across your social platforms in just a few clicks 

Together, these protections are designed to address the broader range of online risks people face every day.

Other Scam and Cybersecurity News This Week 

Here are some other important headlines to be aware of: 

Carnival Data Breach Impacts Nearly 6 Million Customers 

Carnival Corporation disclosed a data breach affecting nearly six million customers after a social engineering attack allowed an unauthorized individual to gain access to part of the company’s IT systems. 

Exposed information may include: 

  • Names 
  • Addresses 
  • Email addresses 
  • Phone numbers 
  • Dates of birth 
  • Government-issued identification numbers

Affected customers should be alert for phishing emails, fake customer support calls, and identity theft attempts. 

Instagram AI Support Tool Exploit Raises Security Questions 

Instagram says it has fixed an issue that reportedly allowed attackers to manipulate its AI-powered support chatbot and gain access to other users’ accounts. 

According to reports, attackers were allegedly able to influence the account recovery process and associate new email addresses with targeted accounts. 

The incident highlights a growing challenge for AI-powered customer support systems: convenience cannot come at the expense of identity verification. 

AI Voice Cloning Scams Continue to Surge 

Voice cloning scams continue to grow as AI tools make it easier than ever to imitate friends, family members, and coworkers. 

According to FBI data cited this week, Americans lost more than $893 million to AI-related scams last year. 

These scams included: 

  • Voice cloning attacks 
  • AI-generated phishing emails 
  • Romance scams 
  • Other AI-assisted fraud schemes 

If someone calls claiming to be a loved one in distress and urgently requests money, verify the situation through another communication channel before taking action. 

McAfee Safety Tips This Week 

Whether you’re downloading a Minecraft mod or answering an unexpected phone call, the same rule applies: 

Slow down before you click, download, or share information. 

Here are a few ways to stay safer: 

  • Download mods, clients, and game tools only from trusted sources. 
  • Be skeptical of download links shared in YouTube comments, Discord servers, or social media posts. 
  • Never disable antivirus software to install a game mod. 
  • Enable multi-factor authentication on gaming, Discord, and email accounts. 
  • Use unique passwords for gaming accounts. 
  • Treat “free cheats,” exclusive hacks, and too-good-to-be-true downloads with caution. 

We’ll be back next week with more scams making headlines. 

The post GTA Cheat Users Exposed in Breach as Minecraft Malware Hits 116,000 Players appeared first on McAfee Blog.

  •  

Welcoming the Philippine Government to Have I Been Pwned

Welcoming the Philippine Government to Have I Been Pwned

Today, we welcome the 46th government onboarded to Have I Been Pwned’s free gov service: the Philippines.

The Philippines’ National CERT, working with the Department of Information and Communications Technology, now has access to monitor official government domains against the data in HIBP. This gives their Cyber Threat Intel and Monitoring Section the ability to identify exposure across government email addresses and respond quickly when those accounts appear in new data breach.

This is precisely what the HIBP government service was built for: helping national cyber teams better understand credential exposure across their government domain space, monitor for compromised accounts on demand via API, and receive notifications when government domains are impacted by newly loaded breach data.

The Philippines joins a growing list of national CERTs and government cybersecurity teams using HIBP to help strengthen national cyber defense, protect government departments and resources, and reduce the risk posed by compromised credentials before attackers can take advantage.

  •  

Strengthening the Foundation: A Predictable, Customer focused Response to AI-Accelerated Vulnerability Discovery

Cisco is moving to a scheduled, twice-monthly security release model to address AI-accelerated vulnerability discovery, providing customers with greater predictability and streamlined, systemic security updates.
  •  

New Malware Targeting Minecraft Infects 2K Daily, and Teens are Becoming Attackers

McAfee Labs has discovered a massive, ongoing malware campaign called WeedHack that disguises itself as free Minecraft mods and game clients to infect players’ computers. Since January 2026, it has logged more than 116,000 victim infections, averaging 2,000 to 3,000 new hits every single day. 

What makes WeedHack different from most malware is how cheap and easy it is to use. 

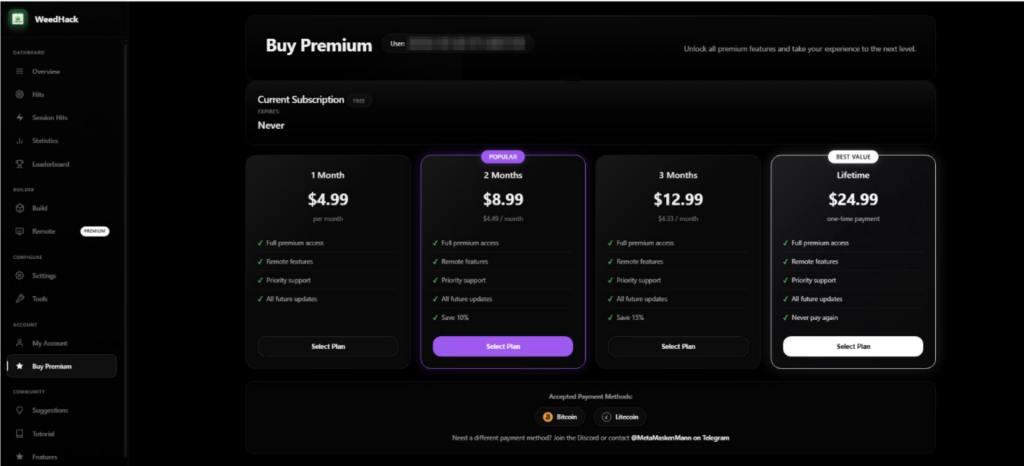
Typically, a hacker would pay hundreds of dollars per month to access attack tools through underground criminal networks. WeedHack offers a free version to anyone with a Discord account and an internet connection. A premium upgrade, which includes the ability to secretly watch victims through their own webcam, starts at just $5 a month. 

This low barrier has attracted a younger crowd of would-be attackers, many of them appear to be teenagers or young adults. Our researchers were startled to discover teens using these tools not just for financial theft, but to harass and bully their peers, a pattern we’ve documented and that makes this campaign especially concerning. 

The good news for McAfee users: Web Protection actively blocks the sites distributing WeedHack, and Threat Explainer tells you exactly why a flagged file is dangerous, so you’re never left guessing. 

Key Facts at a Glance 

What  Details 
Campaign name  WeedHack 
Active since  January 2026 
Total victims logged  116,464+ 
New infections per day  ~2,000–3,000 
Malicious files discovered  3,820+ unique files 
Malicious download URLs  240+ 
Free tier available?  Yes. Anyone can sign up 
Premium price  Starting at $5/month; $24.99 lifetime 
Who is being targeted  Minecraft players worldwide 
Most affected country  United States, followed by Germany, India, the UK, Italy, and others 
What attackers can access  Once installed, it can steal passwords, hijack accounts, and, for paying customers, it can give the attacker live access to the victim’s screen, webcam, and files. 
The financial impact  It can steal Discord tokens, crypto wallet credentials, Minecraft account credentials.  

Hackers will hold your information for ransom, requiring a large payment in exchange for your data. 

Read our research team’s full report here.

What Is WeedHack? 

WeedHack is a Malware-as-a-Service (MaaS) campaign, meaning it’s a criminal business that sells hacking tools to customers, the same way a legitimate software company sells subscriptions. 

The “product” is malware that gets secretly installed on a victim’s computer when they download what they think is a Minecraft mod or client. Once installed, it can steal passwords, hijack accounts, and, for paying customers, it can give the attacker live access to the victim’s screen, webcam, and files. 

The campaign operates a polished, professional-looking dashboard hosted openly on the internet (not the dark web). That dashboard lets customers track their victims, download stolen data, and launch remote access features, all from a browser. 

What it looks like to buy a subscription from WeedHack.

The Cyberbullying Problem 

One of the most disturbing findings from our investigation is how WeedHack is being used. 

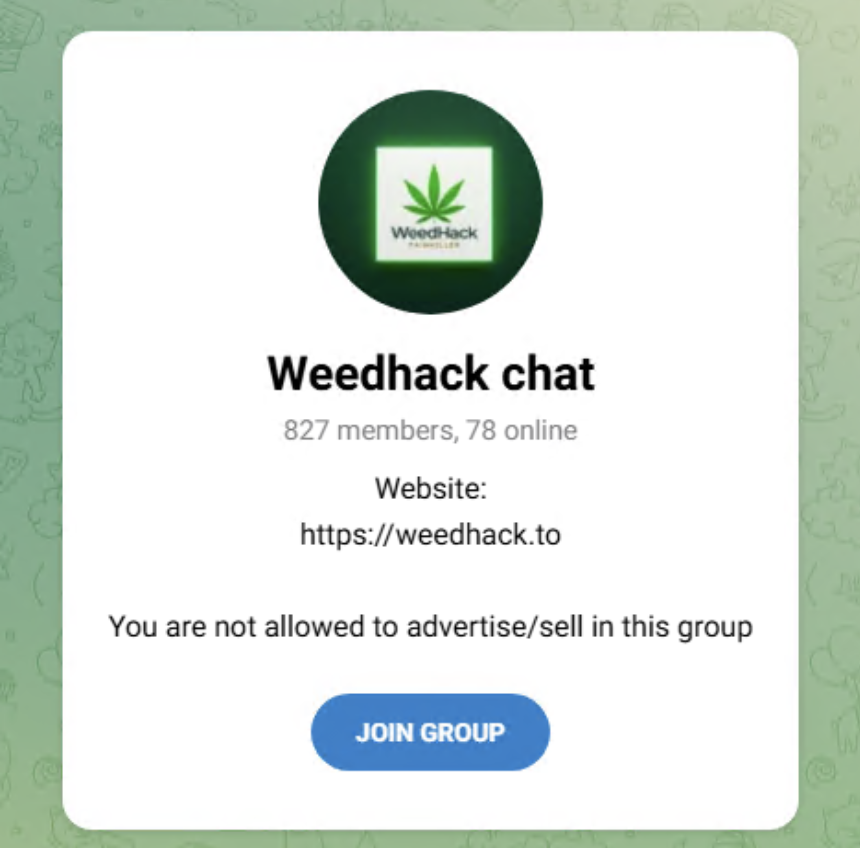
While monitoring the campaign’s Telegram channel, which had over 850 members during the time of our research, we observed that many customers appear to be teenagers and young adults, and a significant portion are using the remote access tools not for financial gain, but to harass and intimidate other players 

We observed attackers recording victims through their webcams without consent and sharing those recordings in the Telegram channel as trophies. Others used knowledge of victims’ IP addresses and system access to threaten them. 

It’s important to note that, at the current time of publishing, the Telegram channel has been taken down, and no replacement channel has appeared. McAfee is continuing to monitor any new channels that may be established by the threat actors for further communication. 

Still, what we observed is a form of cyberbullying with unusually invasive tools behind it. If you or your child has been contacted by someone online claiming they have hacked your computer, have your webcam footage, or know your IP address, take it seriously. 

What to do if this happens: 

  • Do not follow the attacker’s instructions, it makes things worse 
  • Tell a trusted adult immediately (parent, guardian, school counselor) 
  • Contact your local law enforcement, this may constitute criminal conduct.  
  • Do not engage with the attacker or attempt to negotiate 
The Telegram channel uncovered by McAfee.

How Do People Get Infected? 

WeedHack spreads in two main ways, and the campaign even provides its customers with step-by-step tutorials on how to carry out both. 

1. Fake YouTube Videos

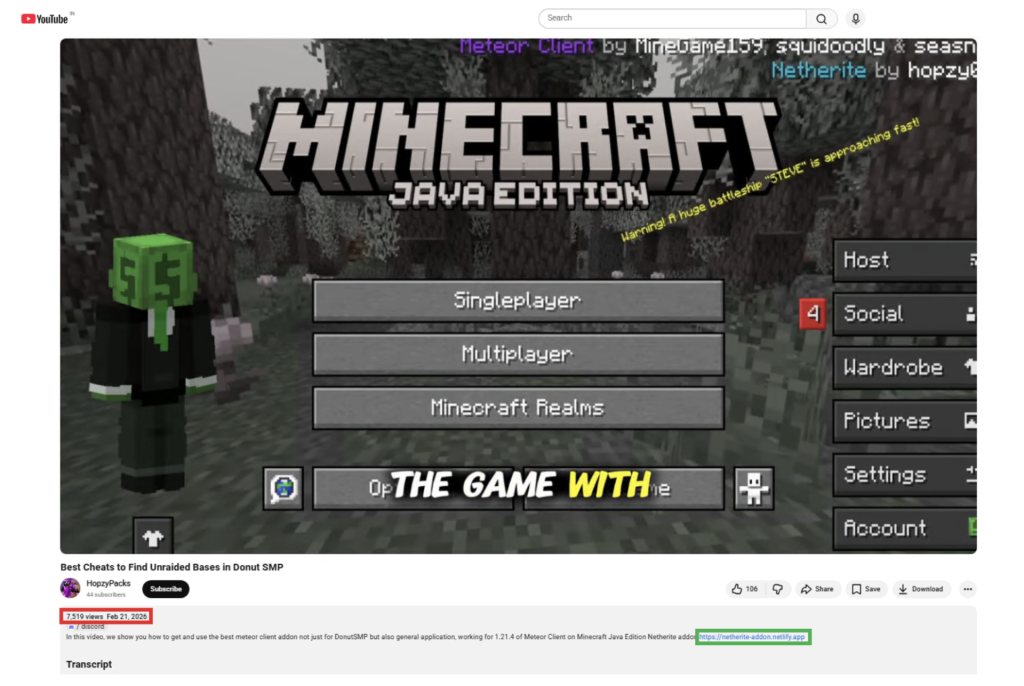
Attackers create convincing YouTube videos reviewing or demonstrating Minecraft clients and mods.  

The videos are well-produced, some include voiceover narration, and link to malicious download sites in the description and comments. 

One video McAfee identified had over 7,500 views before being flagged. Comments are also sometimes planted by the attackers claiming the files are safe. 

2. Fake Mod Websites

WeedHack instructs customers to build convincing-looking websites that mimic official Minecraft mod pages. These sites are deliberately designed to show up high in search engine results for popular mod names, a tactic called SEO poisoning 

Some fake sites include fake security warnings, Discord links, and GitHub references to appear legitimate. In one case, a site warned players to “only download from us,” while actively distributing malware. 

Minecraft clients and mods specifically targeted include: Meteor Client, Radium Client, Wurst Client, LiquidBounce, Impact Client, Future Client, and others. 

An example of a video hiding a malicious link in the description.

What Happens When You’re Infected? 

Infection happens in four stages that happen silently in the background after a victim opens the downloaded file. 

Stage 1 – First Contact: The malicious file launches quietly (without showing a console window), connects to a hidden network, and phones home to receive further instructions. It uses a sophisticated technique involving the Ethereum blockchain to locate its command server in a way that’s difficult to block or take down. 

Stage 2 – Taking Hold: The malware disables Windows Defender protections, gathers detailed information about the victim’s computer (processor, graphics card, RAM, operating system), and takes a screenshot of their screen. It then steals Discord tokens and browser passwords and cookies. For McAfee users, this is where Web Protection would prevent users from visiting the site, and where our Antivirus would prevent any downloaded malware from taking hold. 

Stage 3 – Digging In: The malware installs itself so that it automatically restarts every time the victim logs into their computer. It sets up a hidden scheduled task that runs continuously, even at the highest system privileges. 

Stage 4 – Full Access: For premium customers, an additional component is installed that connects the attacker to the victim’s computer in real time. This includes live screen sharing with keyboard and mouse control, webcam access, keylogging (recording every keystroke), a reverse shell (full command-line access to the computer), and the ability to upload or download any files. 

A separate component specifically hunts for Telegram credentials and cryptocurrency wallets, sending that data to a different server every five minutes. 

What if I’m Infected? 

Visit our guide: How to Quickly Remove Malware in 2026.  

What Can Attackers Steal? 

Free tier steals: 

  • Minecraft session IDs (used to hijack Minecraft accounts) 
  • Saved passwords and cookies from 36 different browsers 
  • Credentials from Discord, Steam, and Telegram 
  • Browser-based crypto wallets (56 supported) and desktop crypto wallets (12 supported) 
  • Files matching 24 different search keywords 
  • Screenshots of the victim’s screen 
  • System information (computer name, IP address, hardware specs) 

Premium tier adds: 

  • Live webcam access 
  • Live screen sharing with keyboard and mouse control 
  • Keylogging (every key the victim types) 
  • Full remote shell (command-line control of the computer) 
  • File management (upload, download, delete files remotely) 

What Parents Need to Know 

Minecraft’s mod ecosystem is enormous and largely unregulated. Kids routinely search YouTube and Google for performance-boosting clients, cosmetic mods, and gameplay cheats, exactly the kinds of things WeedHack exploits.  

Here’s a practical guide for families: 

Red Flag  ✅ Safe Practice 
The mod isn’t on the developer’s official website  Only download from CurseForge, Modrinth, or the mod’s verified GitHub 
A site or video tells you to disable your antivirus to run the file  Never disable antivirus for a game mod. Legitimate mods don’t ask you to 
A site you’ve never heard of claims to be the “only official” source  If you can’t verify the site is official, don’t download from it 
Download links are in YouTube comment sections  Treat comment section links as a red flag, always 
Your antivirus flags a file as malware, but they try to tell you to ignore it, it’s a “false alarm”  Use McAfee’s Threat Explainer to find out why this is malicious. Don’t disable antivirus 

One of the best ways parents can protect their families is with McAfee’s award-winning antivirus and Web Protection, which are specifically designed to detect threats like WeedHack and help block malicious downloads before a device can be compromised. 

Are McAfee Users Protected? 

McAfee has been actively tracking WeedHack samples and detects this threat under the following signatures: 

  • Trojan:Win/Weedhack.AA through Trojan:Win/Weedhack.AE 

McAfee provides multiple layers of protection against threats like WeedHack. 

  • Web Protection helps block access to malicious websites distributing infected Minecraft mods, stopping the threat before a file is ever downloaded.  
  • Award-winning antivirus detects and blocks malware if a malicious file does make it onto your device.  
  • Threat Explainer shows exactly why a file was flagged, helping users understand what happened and avoid similar scams in the future.  

Together, these protections help proactively block risky downloads, reactively stop malware, and explain what to watch for next. 

McAfee Labs continues to monitor WeedHack and will update coverage as new samples and domains are identified. For the full technical report including indicators of compromise, see the McAfee Labs analysis. 

Key Terms Explained 

Term  What it means 
Malware-as-a-Service (MaaS)  A criminal business model where hackers sell or rent attack tools to other people, just like a software subscription 
RAT (Remote Access Trojan)  Malware that gives an attacker remote control over a victim’s device — screen, files, camera, and more 
Infostealer  Malware designed to silently collect and transmit passwords, cookies, and account credentials 
SEO Poisoning  Manipulating search engine results so a malicious website appears near the top when someone searches for a legitimate product 
Minecraft Client/Mod  Third-party software that modifies or enhances the Minecraft game experience. Legitimate ones are common; WeedHack fakes them 
Minecraft Session ID  A token that proves you’re logged into Minecraft. Stealing it lets an attacker take over your account without your password 
Keylogger  Software that secretly records every key a person types — including passwords, messages, and search queries 
Reverse Shell  A connection from the victim’s computer back to the attacker that gives the attacker full command-line control 
EtherHiding  A technique that hides a malware’s server address inside the Ethereum blockchain, making it very difficult to block 
Discord Token  A credential that lets someone access your Discord account. Stealing it gives attackers full access without needing your password 


The post New Malware Targeting Minecraft Infects 2K Daily, and Teens are Becoming Attackers appeared first on McAfee Blog.

  •  
❌