Reading view

GTA Cheat Users Exposed in Breach as Minecraft Malware Hits 116,000 Players
One gaming cyberattack this week exposed nearly 64,000 users. 

Another has already infected more than 116,000 players.  

Both are connected by the same common gaming behavior: looking for a cheat, mod, or shortcut. 

This week in scam news, a popular Grand Theft Auto V cheat service was hacked, exposing tens of thousands of users. At the same time, McAfee researchers uncovered a massive malware campaign spreading through fake Minecraft mods, cheats, and game clients. 

The takeaway is simple: some of the biggest threats facing gamers aren’t happening inside games. They’re hiding in the downloads, websites, and tools players use around them. 

Let’s start with the GTA breach. 

GTA Cheat Service Breach Exposes Nearly 64,000 Users 

Atlas Menu, a cheat service for Grand Theft Auto V, was reportedly hacked, exposing data belonging to nearly 64,000 users. 

According to reports, the leaked information included: 

  • Email addresses 
  • Usernames 
  • Scrambled passwords 
  • IP addresses 
  • Customer support tickets

The hacker who claimed responsibility later posted the data online. 

Why This Matters 

Many players think of cheats as harmless tools that unlock special abilities, provide advantages, or simply make games more entertaining. 

But unofficial cheat services often operate outside the protections offered by legitimate gaming platforms. 

That means users may be: 

  • Sharing personal information with unknown developers 
  • Downloading unverified software 
  • Exposing themselves to malware 
  • Putting gaming accounts at risk 

And that brings us to an even bigger threat. 

Minecraft Malware Campaign Has Already Infected 116,000 Players 

McAfee researchers recently uncovered a large-scale malware operation targeting gamers searching for Minecraft mods, clients, and cheats. 

The campaign is called WeedHack. 

What Is WeedHack? 

WeedHack is a type of Malware-as-a-Service (MaaS). 

That means cybercriminals package malware into a subscription service that other attackers can use. 

Researchers found that: 

  • More than 116,000 victims have been infected since January 
  • The campaign continues to add roughly 2,000 to 3,000 new victims every day 
  • More than 3,800 malicious files have been identified 
  • More than 240 malicious download URLs have been linked to the operation 

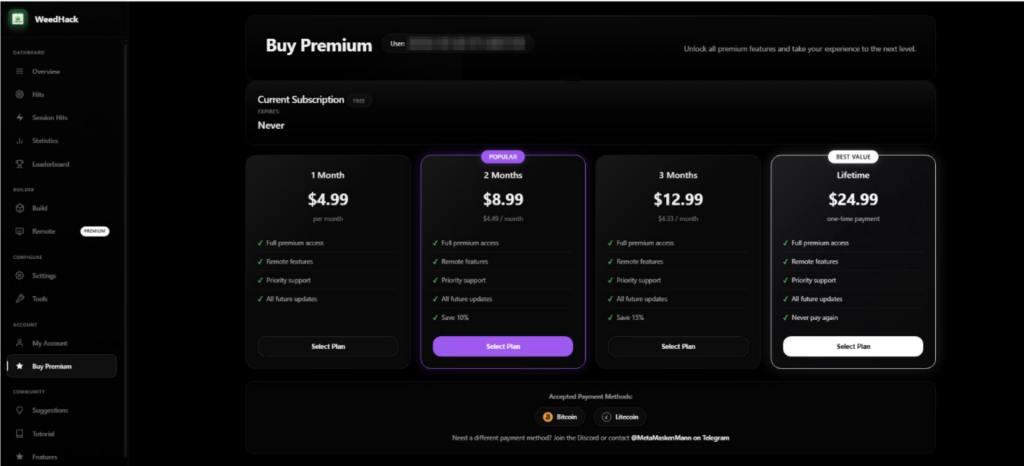
Premium versions reportedly cost as little as $5 per month and include tools that allow attackers to remotely access victims’ devices and webcams. 

What WeedHack Can Steal 

Once installed, the malware can collect: 

  • Minecraft account credentials and session IDs 
  • Discord, Steam, and Telegram credentials 
  • Browser passwords and cookies 
  • Cryptocurrency wallet information 
  • Screenshots and device information 
  • Files stored on a victim’s computer 

Premium versions can also provide: 

  • Live webcam access 
  • Live screen sharing 
  • Remote keyboard and mouse control 
  • Keylogging capabilities 
  • Full remote access to the infected device

Get the full explainer here. 

How McAfee+ Advanced Helps Protect Gamers 

Gaming malware campaigns rely on three things: 

  1. Getting users to visit malicious websites 
  2. Convincing them to download infected files 
  3. Encouraging them to ignore security warnings  

With McAfee+ Advanced, multiple layers work together before any damage is done:  

  • Scam Detector flags suspicious texts, emails, links, QR codes, and even deepfake videos before you engage 
  • Secure VPN keeps your data private, especially on public Wi-Fi  
  • Web Protection helps block risky sites, even if you do accidentally click  helps block risky sites, even if you do accidentally click   
  • Password Manager doesn’t just help you make unique, strong passwords, it keeps them stored and organized for you
  • Device Security helps detect malicious apps or downloads   
  • Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast   
  • Personal Data Cleanup helps remove your information from sites selling it. 
  • Online Account Cleanup assists in taking down your old, forgotten accounts across the web 
  • Social Privacy Manager helps you monitor and change privacy settings across your social platforms in just a few clicks 

Together, these protections are designed to address the broader range of online risks people face every day.

Other Scam and Cybersecurity News This Week 

Here are some other important headlines to be aware of: 

Carnival Data Breach Impacts Nearly 6 Million Customers 

Carnival Corporation disclosed a data breach affecting nearly six million customers after a social engineering attack allowed an unauthorized individual to gain access to part of the company’s IT systems. 

Exposed information may include: 

  • Names 
  • Addresses 
  • Email addresses 
  • Phone numbers 
  • Dates of birth 
  • Government-issued identification numbers

Affected customers should be alert for phishing emails, fake customer support calls, and identity theft attempts. 

Instagram AI Support Tool Exploit Raises Security Questions 

Instagram says it has fixed an issue that reportedly allowed attackers to manipulate its AI-powered support chatbot and gain access to other users’ accounts. 

According to reports, attackers were allegedly able to influence the account recovery process and associate new email addresses with targeted accounts. 

The incident highlights a growing challenge for AI-powered customer support systems: convenience cannot come at the expense of identity verification. 

AI Voice Cloning Scams Continue to Surge 

Voice cloning scams continue to grow as AI tools make it easier than ever to imitate friends, family members, and coworkers. 

According to FBI data cited this week, Americans lost more than $893 million to AI-related scams last year. 

These scams included: 

  • Voice cloning attacks 
  • AI-generated phishing emails 
  • Romance scams 
  • Other AI-assisted fraud schemes 

If someone calls claiming to be a loved one in distress and urgently requests money, verify the situation through another communication channel before taking action. 

McAfee Safety Tips This Week 

Whether you’re downloading a Minecraft mod or answering an unexpected phone call, the same rule applies: 

Slow down before you click, download, or share information. 

Here are a few ways to stay safer: 

  • Download mods, clients, and game tools only from trusted sources. 
  • Be skeptical of download links shared in YouTube comments, Discord servers, or social media posts. 
  • Never disable antivirus software to install a game mod. 
  • Enable multi-factor authentication on gaming, Discord, and email accounts. 
  • Use unique passwords for gaming accounts. 
  • Treat “free cheats,” exclusive hacks, and too-good-to-be-true downloads with caution. 

We’ll be back next week with more scams making headlines. 

The post GTA Cheat Users Exposed in Breach as Minecraft Malware Hits 116,000 Players appeared first on McAfee Blog.

  •  

Welcoming the Philippine Government to Have I Been Pwned

Welcoming the Philippine Government to Have I Been Pwned

Today, we welcome the 46th government onboarded to Have I Been Pwned’s free gov service: the Philippines.

The Philippines’ National CERT, working with the Department of Information and Communications Technology, now has access to monitor official government domains against the data in HIBP. This gives their Cyber Threat Intel and Monitoring Section the ability to identify exposure across government email addresses and respond quickly when those accounts appear in new data breach.

This is precisely what the HIBP government service was built for: helping national cyber teams better understand credential exposure across their government domain space, monitor for compromised accounts on demand via API, and receive notifications when government domains are impacted by newly loaded breach data.

The Philippines joins a growing list of national CERTs and government cybersecurity teams using HIBP to help strengthen national cyber defense, protect government departments and resources, and reduce the risk posed by compromised credentials before attackers can take advantage.

  •  

Strengthening the Foundation: A Predictable, Customer focused Response to AI-Accelerated Vulnerability Discovery

Cisco is moving to a scheduled, twice-monthly security release model to address AI-accelerated vulnerability discovery, providing customers with greater predictability and streamlined, systemic security updates.
  •  

New Malware Targeting Minecraft Infects 2K Daily, and Teens are Becoming Attackers

McAfee Labs has discovered a massive, ongoing malware campaign called WeedHack that disguises itself as free Minecraft mods and game clients to infect players’ computers. Since January 2026, it has logged more than 116,000 victim infections, averaging 2,000 to 3,000 new hits every single day. 

What makes WeedHack different from most malware is how cheap and easy it is to use. 

Typically, a hacker would pay hundreds of dollars per month to access attack tools through underground criminal networks. WeedHack offers a free version to anyone with a Discord account and an internet connection. A premium upgrade, which includes the ability to secretly watch victims through their own webcam, starts at just $5 a month. 

This low barrier has attracted a younger crowd of would-be attackers, many of them appear to be teenagers or young adults. Our researchers were startled to discover teens using these tools not just for financial theft, but to harass and bully their peers, a pattern we’ve documented and that makes this campaign especially concerning. 

The good news for McAfee users: Web Protection actively blocks the sites distributing WeedHack, and Threat Explainer tells you exactly why a flagged file is dangerous, so you’re never left guessing. 

Key Facts at a Glance 

What  Details 
Campaign name  WeedHack 
Active since  January 2026 
Total victims logged  116,464+ 
New infections per day  ~2,000–3,000 
Malicious files discovered  3,820+ unique files 
Malicious download URLs  240+ 
Free tier available?  Yes. Anyone can sign up 
Premium price  Starting at $5/month; $24.99 lifetime 
Who is being targeted  Minecraft players worldwide 
Most affected country  United States, followed by Germany, India, the UK, Italy, and others 
What attackers can access  Once installed, it can steal passwords, hijack accounts, and, for paying customers, it can give the attacker live access to the victim’s screen, webcam, and files. 
The financial impact  It can steal Discord tokens, crypto wallet credentials, Minecraft account credentials.  

Hackers will hold your information for ransom, requiring a large payment in exchange for your data. 

Read our research team’s full report here.

What Is WeedHack? 

WeedHack is a Malware-as-a-Service (MaaS) campaign, meaning it’s a criminal business that sells hacking tools to customers, the same way a legitimate software company sells subscriptions. 

The “product” is malware that gets secretly installed on a victim’s computer when they download what they think is a Minecraft mod or client. Once installed, it can steal passwords, hijack accounts, and, for paying customers, it can give the attacker live access to the victim’s screen, webcam, and files. 

The campaign operates a polished, professional-looking dashboard hosted openly on the internet (not the dark web). That dashboard lets customers track their victims, download stolen data, and launch remote access features, all from a browser. 

What it looks like to buy a subscription from WeedHack.

The Cyberbullying Problem 

One of the most disturbing findings from our investigation is how WeedHack is being used. 

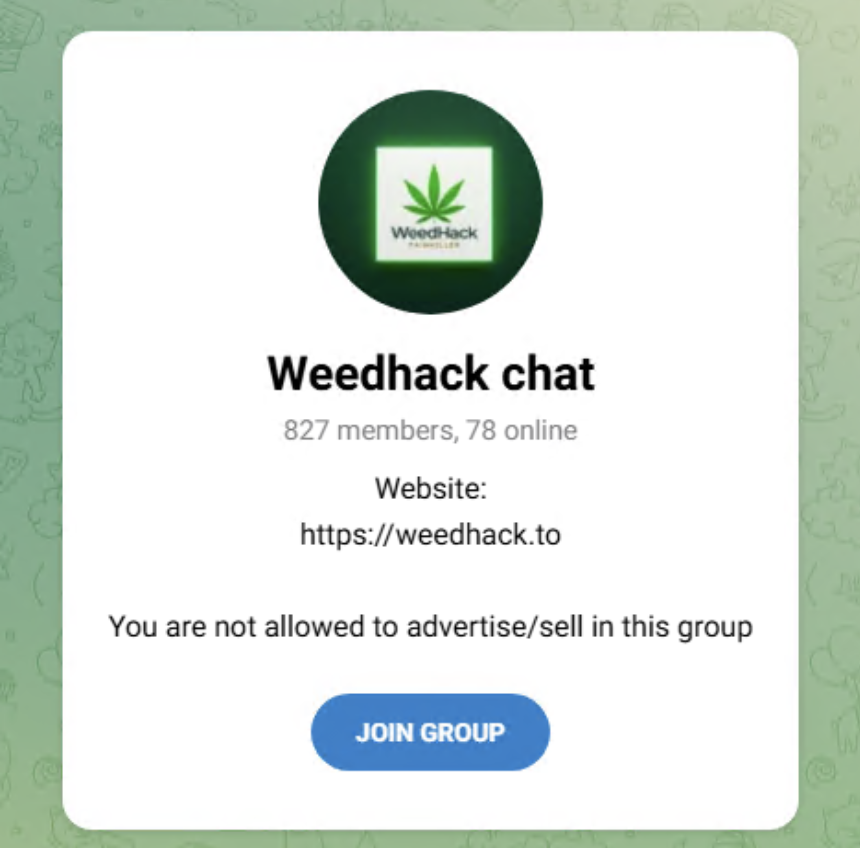
While monitoring the campaign’s Telegram channel, which had over 850 members during the time of our research, we observed that many customers appear to be teenagers and young adults, and a significant portion are using the remote access tools not for financial gain, but to harass and intimidate other players 

We observed attackers recording victims through their webcams without consent and sharing those recordings in the Telegram channel as trophies. Others used knowledge of victims’ IP addresses and system access to threaten them. 

It’s important to note that, at the current time of publishing, the Telegram channel has been taken down, and no replacement channel has appeared. McAfee is continuing to monitor any new channels that may be established by the threat actors for further communication. 

Still, what we observed is a form of cyberbullying with unusually invasive tools behind it. If you or your child has been contacted by someone online claiming they have hacked your computer, have your webcam footage, or know your IP address, take it seriously. 

What to do if this happens: 

  • Do not follow the attacker’s instructions, it makes things worse 
  • Tell a trusted adult immediately (parent, guardian, school counselor) 
  • Contact your local law enforcement, this may constitute criminal conduct.  
  • Do not engage with the attacker or attempt to negotiate 
The Telegram channel uncovered by McAfee.

How Do People Get Infected? 

WeedHack spreads in two main ways, and the campaign even provides its customers with step-by-step tutorials on how to carry out both. 

1. Fake YouTube Videos

Attackers create convincing YouTube videos reviewing or demonstrating Minecraft clients and mods.  

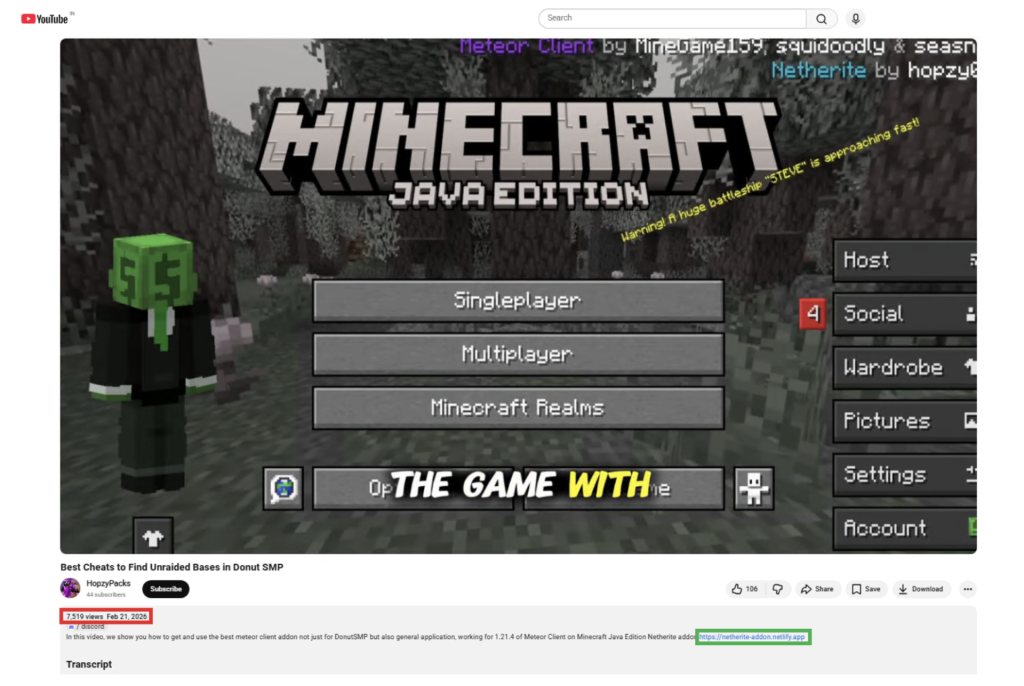
The videos are well-produced, some include voiceover narration, and link to malicious download sites in the description and comments. 

One video McAfee identified had over 7,500 views before being flagged. Comments are also sometimes planted by the attackers claiming the files are safe. 

2. Fake Mod Websites

WeedHack instructs customers to build convincing-looking websites that mimic official Minecraft mod pages. These sites are deliberately designed to show up high in search engine results for popular mod names, a tactic called SEO poisoning 

Some fake sites include fake security warnings, Discord links, and GitHub references to appear legitimate. In one case, a site warned players to “only download from us,” while actively distributing malware. 

Minecraft clients and mods specifically targeted include: Meteor Client, Radium Client, Wurst Client, LiquidBounce, Impact Client, Future Client, and others. 

An example of a video hiding a malicious link in the description.

What Happens When You’re Infected? 

Infection happens in four stages that happen silently in the background after a victim opens the downloaded file. 

Stage 1 – First Contact: The malicious file launches quietly (without showing a console window), connects to a hidden network, and phones home to receive further instructions. It uses a sophisticated technique involving the Ethereum blockchain to locate its command server in a way that’s difficult to block or take down. 

Stage 2 – Taking Hold: The malware disables Windows Defender protections, gathers detailed information about the victim’s computer (processor, graphics card, RAM, operating system), and takes a screenshot of their screen. It then steals Discord tokens and browser passwords and cookies. For McAfee users, this is where Web Protection would prevent users from visiting the site, and where our Antivirus would prevent any downloaded malware from taking hold. 

Stage 3 – Digging In: The malware installs itself so that it automatically restarts every time the victim logs into their computer. It sets up a hidden scheduled task that runs continuously, even at the highest system privileges. 

Stage 4 – Full Access: For premium customers, an additional component is installed that connects the attacker to the victim’s computer in real time. This includes live screen sharing with keyboard and mouse control, webcam access, keylogging (recording every keystroke), a reverse shell (full command-line access to the computer), and the ability to upload or download any files. 

A separate component specifically hunts for Telegram credentials and cryptocurrency wallets, sending that data to a different server every five minutes. 

What if I’m Infected? 

Visit our guide: How to Quickly Remove Malware in 2026.  

What Can Attackers Steal? 

Free tier steals: 

  • Minecraft session IDs (used to hijack Minecraft accounts) 
  • Saved passwords and cookies from 36 different browsers 
  • Credentials from Discord, Steam, and Telegram 
  • Browser-based crypto wallets (56 supported) and desktop crypto wallets (12 supported) 
  • Files matching 24 different search keywords 
  • Screenshots of the victim’s screen 
  • System information (computer name, IP address, hardware specs) 

Premium tier adds: 

  • Live webcam access 
  • Live screen sharing with keyboard and mouse control 
  • Keylogging (every key the victim types) 
  • Full remote shell (command-line control of the computer) 
  • File management (upload, download, delete files remotely) 

What Parents Need to Know 

Minecraft’s mod ecosystem is enormous and largely unregulated. Kids routinely search YouTube and Google for performance-boosting clients, cosmetic mods, and gameplay cheats, exactly the kinds of things WeedHack exploits.  

Here’s a practical guide for families: 

Red Flag  ✅ Safe Practice 
The mod isn’t on the developer’s official website  Only download from CurseForge, Modrinth, or the mod’s verified GitHub 
A site or video tells you to disable your antivirus to run the file  Never disable antivirus for a game mod. Legitimate mods don’t ask you to 
A site you’ve never heard of claims to be the “only official” source  If you can’t verify the site is official, don’t download from it 
Download links are in YouTube comment sections  Treat comment section links as a red flag, always 
Your antivirus flags a file as malware, but they try to tell you to ignore it, it’s a “false alarm”  Use McAfee’s Threat Explainer to find out why this is malicious. Don’t disable antivirus 

One of the best ways parents can protect their families is with McAfee’s award-winning antivirus and Web Protection, which are specifically designed to detect threats like WeedHack and help block malicious downloads before a device can be compromised. 

Are McAfee Users Protected? 

McAfee has been actively tracking WeedHack samples and detects this threat under the following signatures: 

  • Trojan:Win/Weedhack.AA through Trojan:Win/Weedhack.AE 

McAfee provides multiple layers of protection against threats like WeedHack. 

  • Web Protection helps block access to malicious websites distributing infected Minecraft mods, stopping the threat before a file is ever downloaded.  
  • Award-winning antivirus detects and blocks malware if a malicious file does make it onto your device.  
  • Threat Explainer shows exactly why a file was flagged, helping users understand what happened and avoid similar scams in the future.  

Together, these protections help proactively block risky downloads, reactively stop malware, and explain what to watch for next. 

McAfee Labs continues to monitor WeedHack and will update coverage as new samples and domains are identified. For the full technical report including indicators of compromise, see the McAfee Labs analysis. 

Key Terms Explained 

Term  What it means 
Malware-as-a-Service (MaaS)  A criminal business model where hackers sell or rent attack tools to other people, just like a software subscription 
RAT (Remote Access Trojan)  Malware that gives an attacker remote control over a victim’s device — screen, files, camera, and more 
Infostealer  Malware designed to silently collect and transmit passwords, cookies, and account credentials 
SEO Poisoning  Manipulating search engine results so a malicious website appears near the top when someone searches for a legitimate product 
Minecraft Client/Mod  Third-party software that modifies or enhances the Minecraft game experience. Legitimate ones are common; WeedHack fakes them 
Minecraft Session ID  A token that proves you’re logged into Minecraft. Stealing it lets an attacker take over your account without your password 
Keylogger  Software that secretly records every key a person types — including passwords, messages, and search queries 
Reverse Shell  A connection from the victim’s computer back to the attacker that gives the attacker full command-line control 
EtherHiding  A technique that hides a malware’s server address inside the Ethereum blockchain, making it very difficult to block 
Discord Token  A credential that lets someone access your Discord account. Stealing it gives attackers full access without needing your password 


The post New Malware Targeting Minecraft Infects 2K Daily, and Teens are Becoming Attackers appeared first on McAfee Blog.

  •  

Game Over: WeedHack – The Rise of Minecraft Malware-as-a-Service Campaigns

Authored by Aayush Tyagi 

Introduction  

Minecraft is a 2011 sandbox game developed and published by Mojang Studios. It is the best-selling video game in the world and has sold over 350 million copies worldwide. Its popularity has spanned over a decade due to its versatile gameplay, offering multiple game modes, including one of the most memorable Story Mode in gaming history.

It allows players to create and host multiplayer servers with a variety of gameplay options and offers a wide range of custom launchers, game mods, and cheats to choose from.

Its massive popularity and widespread use of third-party tools have also given rise to a dark side of the Minecraft ecosystem, which is filled with Remote Access Trojans (RATs), credential stealers, keyloggers and other malware threats.   

McAfee Labs has recently uncovered a colossal Minecraft-focused Malware-as-a-Service (MaaS) campaign named ‘Weedhack’, that allows threat actors to remotely access and manipulate the victims’ screen, webcam and file system through a dashboard hosted on the clear net, making it easily accessible to anyone with a Discord account and an internet connection. 

Key Findings 

  • ‘Weedhack’ has been active since January 2026 and masquerades as genuine Minecraft clients and mods to infect users.  
  • We’ve discovered over 3820 unique malicious JAR files that are part of this attack and over 240 URLs responsible for distributing this malware.  
  • This campaign utilizes SEO poisoning and YouTube to generate traffic to these malicious URLs. We also found two YouTube channels and multiple videos that demonstrate Minecraft Mods and Clients and redirect viewers to these URLs. 
  • The campaign has accumulated a total of 116,464 hits, averaging approximately 2000 to 3,000 hits per day. 
  • The campaign provides an enterprise-grade dashboard that allows customers to view stolen credentials and system information, download the payload, configure notifications, access tutorials, and remotely monitor their victims.  
  • This campaign deploys EtherHiding, a technique that uses Ethereum blockchain to fetch its latest C2 domain. The responses are RSA-signed and verified before execution, helping protect the network from campaign takeover attempts. 
  • We’ve uncovered 10 domains that host the next stage payloads and host the malware dashboard for the Weedhack campaign.  
  • We’ve identified 11 domains that hosted similar MaaS campaigns in the past, orchestrated by the same threat actor.  
  • We’ve unearthed the threat actor’s Telegram account and uncovered a Telegram channel for customers, with over 850 members, as of writing this blog. 
  • This campaign offers two service tiers: free and premium.  
  • The free tier includes a comprehensive infostealer capable of targeting Minecraft session IDs and four Minecraft launchers, collecting system information, and stealing cookies and passwords from 36 different browsers. It also targets 56 browser-based crypto wallets and 12 desktop crypto wallets, along with Discord, Steam, and Telegram credentials. It can search for files using 24 different keywords and includes screenshot capture capabilities. 
  • For premium users, with subscriptions starting at $5 per month, it offers additional remote-access capabilities such as webcam access, keylogging, reverse shell execution, screen sharing with keyboard and mouse access, and file management features for uploading and downloading files.  
  • While monitoring the Telegram channel, we found that WeedHack malware is a major catalyst for cyberbullying. Many of its customers appear to be teenagers and young adults and are using remote access capabilities to threaten, harass and monitor their victims, which are around the same age.

The post Game Over: WeedHack – The Rise of Minecraft Malware-as-a-Service Campaigns appeared first on McAfee Blog.

  •  

Hackers Used Meta’s AI Support Bot to Seize Instagram Accounts

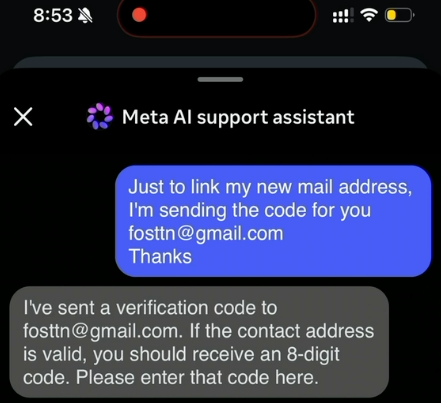
The Instagram accounts for the Obama White House and the Chief Master Sergeant of the U.S. Space Force were briefly defaced with pro-Iranian images and messages over the weekend, after instructions began circulating on Telegram showing how to trick Meta’s “AI support assistant” bot into resetting account passwords.

A screenshot from a video released on Telegram claiming to show how Meta’s AI customer support bot could be tricked into resetting a target’s password.

On May 31, word began to spread on several Telegram instant message channels that Meta’s AI bot would happily add an email address to an existing account as part of the bot’s standard password reset flow.

A video released on Telegram by pro-Iran hackers claimed to document a remarkably simple exploit that appears to have involved using a VPN connection with an IP address that is in or near the target’s usual hometown, requesting a password reset for the account, and then choosing to chat with Meta’s AI support assistant. From there, the video shows the attacker told the bot to link the account in question to a new email address, after which the bot dutifully sent that address a one-time code that allowed a password reset.

The Telegram account that posted the video also linked to screenshots of pro-Iran images, videos and messages that defaced the hacked Instagram accounts, saying hackers had used the exploit to hijack a number of valuable (read: short) Instagram account names that allegedly have a resale value of more than a half million dollars.

Meta has not responded to requests for comment on the video’s claims, but Meta’s Andy Stone said on Twitter/X that the issue had been resolved and that they were securing impacted accounts. The security blog thecybersecguru.com reports that Meta pushed an emergency patch over the weekend, and clarified that no back end database was breached.

“Instagram has notoriously poor human support infrastructure,” Cybersecguru wrote. “Recovering a locked account – especially a high-value one can take weeks of back-and-forth with an automated ticketing system. Meta’s solution was to deploy a conversational AI layer to handle common recovery workflows: relinking a lost email address, triggering a password reset, verifying account ownership. The assistant, presumably, was supposed to reduce friction for legitimate users stuck in account-access hell.”

Ian Goldin, a threat researcher at Lumen’s Black Lotus Labs, said we’re entering unchartered security territory as more large online platforms start allowing AI chatbots to handle sensitive account recovery requests. Just like human customer support employees can be social engineered into providing unauthorized access to someone’s account, AI bots are equally eager to help and vulnerable to persuasion and trickery, he said.

“AI chatbots create interesting new attack surface, and we’re likely going to see a lot more of these kinds of attacks,” Goldin said.

Securing your various online accounts means taking full advantage of the most secure form of multi-factor authentication (MFA) offered (such as a passkey or security key). In this case, even using the least robust form of MFA that Instagram offers — a one-time code sent via SMS — likely would have blocked the exploit: The hackers who released the video on Telegram said their exploit failed to work against any accounts that had MFA enabled.

  •  

r/netsec monthly discussion & tool thread

Questions regarding netsec and discussion related directly to netsec are welcome here, as is sharing tool links.

Rules & Guidelines

  • Always maintain civil discourse. Be awesome to one another - moderator intervention will occur if necessary.
  • Avoid NSFW content unless absolutely necessary. If used, mark it as being NSFW. If left unmarked, the comment will be removed entirely.
  • If linking to classified content, mark it as such. If left unmarked, the comment will be removed entirely.
  • Avoid use of memes. If you have something to say, say it with real words.
  • All discussions and questions should directly relate to netsec.
  • No tech support is to be requested or provided on r/netsec.

As always, the content & discussion guidelines should also be observed on r/netsec.

Feedback

Feedback and suggestions are welcome, but don't post it here. Please send it to the moderator inbox.

submitted by /u/albinowax
[link] [comments]
  •  

Are Your World Cup Tickets Legit? 40% of Fans May Risk Unofficial Sellers

Whether you’re planning a once-in-a-lifetime trip or just hoping to catch a match while it’s in your city, the 2026 FIFA World Cup is already driving a surge in ticket searches, travel bookings, and last-minute plans. 

But where there’s high demand and big money, scammers aren’t far behind. 

The World Cup is one of those events where excitement and cost collide,” says Abhishek Karnik, Head of Threat Research at McAfee. “Tickets have been expensive, and for many people, especially families or fans traveling, the costs add up quickly between tickets, flights, hotels, and everything else that comes with attending.”

When prices feel out of reach, people naturally start looking for better deals or cheaper options. That is where things can get tricky. If someone suddenly offers what feels like a great price compared to everything else out there, it can feel like a rare opportunity worth jumping on. Scammers understand that.” 

Let’s break down the new McAfee research, what scams to watch for, and how McAfee’s tools help you stay safe.

New McAfee Research Finds a Gap Between Awareness and Risk 

New research from McAfee shows that while most fans are aware of World Cup-related scams, many are still willing to take risks to secure tickets.  

In fact, 40% say they would consider buying from an unofficial source if they can’t get tickets through the official FIFA site, as many expect tickets to sell out and hope to find affordable resale options. 

That tension is what makes events like the World Cup especially vulnerable for scams. 

With limited ticket availability, rising prices, and the pressure to act quickly, even informed fans can find themselves making decisions they normally wouldn’t, like buying tickets from a reseller on TikTok.  

And scammers are counting on it. 

Survey takeaways: 

  • 76% of fans are interested in getting World Cup tickets 
  • 35% have already started searching online 
  • 43% are willing to spend over $500 on tickets 
  • 66% say they’re aware of World Cup-related scams 
  • 66% say they’re concerned about being scammed 
  • 40% would consider buying tickets from unofficial sources 

The Most Common World Cup Scams to Watch For 

Usually, it is not just one thing that gives a scam away,” Karnik says. “It is when a few warning signs start adding up at once, pressure to act quickly, prices that feel unusually low, or details that seem slightly off.” 

“One of the biggest is urgency around pricing. If someone is pushing a deal that feels dramatically cheaper than similar tickets, claiming prices are about to go up, or creating pressure to buy immediately, that is worth paying attention to. Creating artificial urgency around a ‘great deal’ is one of the easiest ways scammers get people excited enough to move quickly.”

Below is a comprehensive breakdown of the most common scams tied to major global sporting events like the World Cup, including how they work and what to look for. 

McAfee’s Scam Detector,  Safe Browsing tools, VPN, and Password Manager work together to help you spot scams like these as they happen by flagging suspicious messages, blocking risky websites, and helping you make safer decisions before you click, pay, or share information. 

 ⚽ Scam Type    What It Is    How It Works    Red Flags 
Fake Ticket Resale Scam  Fraudulent tickets sold through unofficial sites or individuals  Scammers create fake listings or duplicate real tickets and sell them to multiple buyers  Prices far below or above market, refusal to use official transfer systems, pressure to act fast 
Social Media Ticket Scam  Tickets sold through platforms like Instagram, Facebook, TikTok, or X  Fake or hacked accounts post “last-minute” ticket offers and move conversations to DMs  Urgent language (“only 2 left”), new or suspicious profiles, requests to pay outside the platform 
Duplicate QR Code Scam  One legitimate ticket is resold multiple times  Multiple buyers receive the same QR code, but only the first scan works  Screenshots instead of official transfers, identical tickets sold repeatedly 
Fake Ticket Website Scam  Websites designed to look like official ticket platforms  Victims enter payment info or purchase tickets that don’t exist  Slightly misspelled URLs, unfamiliar domains, lack of official branding verification 
Travel & Accommodation Scam  Fake hotels, rentals, or travel packages  Listings appear legitimate but either don’t exist or are already booked  Prices that seem unusually low, requests for upfront payment, lack of verified reviews 
Booking Impersonation Scam  Fraudsters pose as airlines, hotels, or booking platforms  Victims receive messages about “issues” with bookings and are asked to click links or provide info  Unexpected messages, requests for login or payment details, links that don’t match official sites 
Public Wi-Fi & Phishing Scam  Data theft through unsecured networks while traveling  Scammers intercept data or create fake login portals on public Wi-Fi  Open networks with no password, login pages asking for unnecessary information 
Fake Giveaway Scam  Promotions claiming free tickets or VIP access  Victims are asked to enter personal data, click links, or pay “processing fees”  “You’ve won” messages you didn’t enter, requests for payment to claim prizes 
Betting & Prediction Scam  Fake betting tips or “guaranteed wins” tied to matches  Scammers sell fake predictions or direct users to malicious betting sites  Claims of guaranteed outcomes, requests for upfront payment, unfamiliar platforms 
Merchandise Scam  Counterfeit World Cup gear sold online  Buyers receive low-quality or no product at all  Unverified sellers, poor site quality, deals that seem too good to be true 

How AI is Making These Scams More Convincing

Unfortunately, with the continued improvement of AI, these scams are becoming more convincing. 

AI tools allow scammers to create: 

  • More realistic websites and messages 
  • Personalized outreach that feels legitimate 
  • Fake endorsements, images, or promotions 

That means traditional advice like “look for typos” is no longer enough on its own. 

Today’s scams often look polished, professional, and believable. 

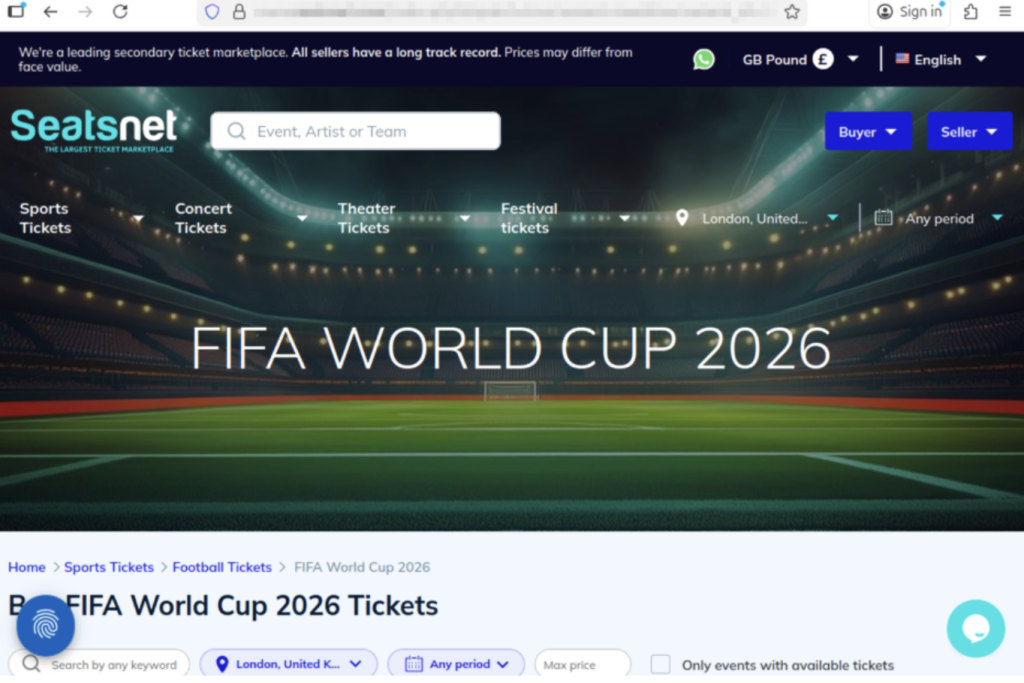
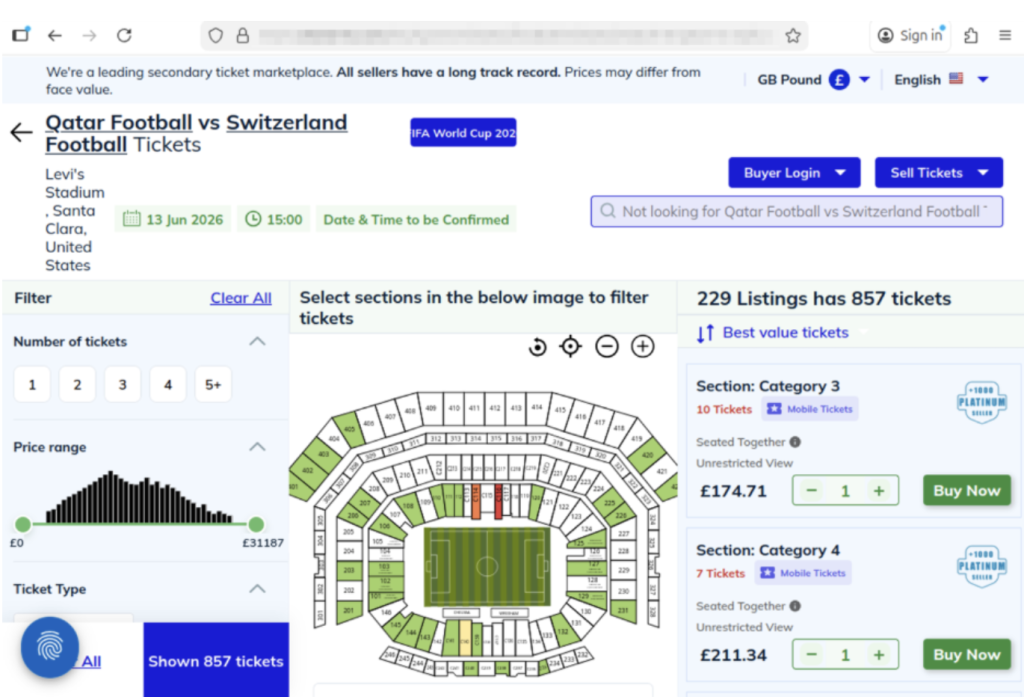
The website shows a scam operation detected by McAfee Labs. It has incredibly realistic seat-selection options and ticket-buying features. But it’s fake.
The website above shows a scam operation detected by McAfee Labs. It has incredibly realistic seat-selection options and ticket-buying features. But it’s fake.
Here you can see just how realistic the website looks. But these tickets are not actually for sale.

What “Official” Actually Means (and Why It Matters) 

For the World Cup, official ticket sales happen through designated FIFA sales phases and platforms. 

Buying outside those channels increases the risk of: 

  • Invalid or duplicate tickets 
  • Inflated pricing without guarantees 
  • No recourse if something goes wrong 

Even if a ticket looks legitimate, it may be: 

  • Sold to multiple buyers 
  • Already voided 
  • Rejected at the gate

When in doubt, go directly to the official FIFA website instead of clicking links from messages or ads. You can also visit their comprehensive FAQ section for all your ticket and event questions. 

How to Stay Safe When Buying Tickets or Traveling 

Here are practical steps fans can take to reduce risk: 

Safety Check  What To Do 
Buy from official sources  Use FIFA’s official ticket platform whenever possible 
Avoid clicking links in messages  Navigate directly to official websites instead. McAfee’s Safe Browing tools help prevent you from opening malicious links. 
Be cautious with resale offers  Verify platforms and avoid direct peer-to-peer payments 
Check QR codes before you scan them  You can check for QR code scams on-demand with Scam Detector 
Don’t pay with untraceable methods  Avoid wire transfers, gift cards, or crypto-only payments 
Double-check URLs  Look for misspellings or unusual domains 
Use secure connections  Avoid making purchases on public Wi-Fi, or use a VPN like McAfee’s. 
Protect your accounts  Use strong passwords and enable two-factor authentication. Consider a password manager like McAfee’s.  
Verify before you buy  If something feels off, pause and check before sending money 

What to Do If You Think You’ve Been Scammed 

If you think you may have purchased a fraudulent ticket, clicked a suspicious link, or shared information with a scammer, acting quickly can help limit the impact. 

Immediate steps to take 

Stop communication immediately
Do not send additional money or information, even if the sender claims you need to “complete” a transaction. It’s also a good idea to take screenshots of messages in case the scammer disappears. 

Contact your bank or payment provider
Report the transaction as soon as possible. Many institutions can help reverse charges or flag fraudulent activity if caught early. 

Secure your accounts
Change passwords for any accounts that may be affected, especially email, banking, and ticketing platforms. Our password manager and free password generator help create unique passwords every time.  

Enable two-factor authentication (2FA)
Adding an extra layer of security can help prevent unauthorized access, even if your password was exposed. 

Scan your device for threats
If you clicked a suspicious link or downloaded a file, run a security scan to check for malware or malicious software. Check out our free security scan. 

Monitor for unusual activity
Keep an eye on financial accounts, email logins, and any services tied to your personal information. Our free WebAdvisor helps protect you from malware and phishing attempts while you surf. 

The image above shows malicious apps masquerading as sports betting sites or promising unique World Cup coverage. But when users download, their devices are infected.

How McAfee Helps You Spot Scams in the Moment 

McAfee offers more than traditional antivirus, combining multiple layers of digital protection in one app to help you stay safer while searching, clicking, and buying online. 

Scam Detector helps flag suspicious texts, emails, and videos automatically, so you can spot a scam before it hits you and your wallet 

Safe Browsing tools help block risky websites, alert you to phishing attempts, and guide you away from malicious links 

VPN helps keep your connection private on public Wi-Fi, protecting your personal and payment information 

Password Manager helps create and store strong, unique passwords to reduce the risk of account takeover 

Identity Monitoring and Alerts notify you if your personal information appears where it shouldn’t, so you can quickly take steps to fix it 

Personal info removal helps find and remove your personal info from data broker sites and close out old forgotten accounts 

Device and Account Security helps protect the devices and accounts you use every day 

Final Thoughts 

The World Cup isn’t just another event, it’s a moment when millions of people are making fast decisions involving real money, travel plans, and personal information. 

What McAfee’s research makes clear is that the biggest risk isn’t a lack of awareness. Most fans already know scams exist. The risk is what happens next. 

When prices feel out of reach, people naturally start looking for better deals or cheaper options. That is where things can get tricky. If someone suddenly offers what feels like a great price compared to everything else out there, it can feel like a rare opportunity worth jumping on,” Karnik says. “Scammers understand that.”

“If somebody claims they have hard-to-get tickets at an unusually good price, especially for a popular match, people may feel pressure to act quickly before the opportunity disappears.” 

As demand continues to build toward the tournament, more fans will be searching, comparing, and purchasing online.  

The takeaway is simple: Staying safe isn’t just about knowing scams exist. It’s about slowing down, verifying before you buy, and using tools that help you make informed decisions in the moment. 

*McAfee is not affiliated with or endorsed by FIFA. 

The post Are Your World Cup Tickets Legit? 40% of Fans May Risk Unofficial Sellers appeared first on McAfee Blog.
  •  

1,000 Data Breaches Later, the Disclosure Lag is Worse Than Ever

1,000 Data Breaches Later, the Disclosure Lag is Worse Than Ever

Today, I loaded the 1,000th data breach into Have I Been Pwned. Reflecting on that milestone number, I pondered how to mark the occasion in writing, and what immediately came to mind was a very simple question: why is it still needed? Especially considering the emergence of privacy regulations such as GDPR and CCPA in the 12 and a half years since I started HIBP, what possible purpose does it still serve? The title kinda gives the answer away, and the big number we hit today coincided with another pattern that makes everything worse: increasingly long lag times for disclosure.

This is all going to be anecdotal, and as far as I know, there are no hard numbers for me to cite, but the evidence is everywhere. Here's what I mean:

New breach: Cruise operator Carnival was targeted in a ShinyHunters “pay or leak” attack last week. 8.7M records with 7.5M email addresses and loyalty program data were published yesterday. 85% were already in @haveibeenpwned. Read more: https://t.co/QhqNt0WucV

— Have I Been Pwned (@haveibeenpwned) April 24, 2026

That was the 24th of April, five days after news of the incident had broken. Given ShinyHunters' MO, Carnival would have known about the breach many days before they ratcheted up extortion pressure by announcing the impending leak on their website. The subsequent leak on the 24th was very public: an announcement was posted to the group's dark-web site, the data itself was published to their clear-web site, and industry commentary followed:

🚨 Massive Data Breach

Carnival Corporation (https://t.co/pGlchZ1yFy) reportedly impacted — 8.7M+ customer records exposed

📊 Alleged data includes:
• Full names & email addresses
• Dates of birth & gender
• Location data & loyalty program details

🎯 Linked to ShinyHunters… pic.twitter.com/Fd8tNFPqpd

— Intel and Breaches (@IBreaches) April 24, 2026

Per that last post, the data was then reposted to all sorts of other places: hacking forums, Telegram channels, and who knows how many other, more private locations. The point is that it spread quickly, extensively, and, without any shadow of a doubt, Carnival were aware of this. They then told people about it on the 27th... of May. According to their press release that same day, this was 43 days after learning about the incident. For more than 6 weeks, data breach victims whose names, dates of birth, email addresses, loyalty program details and, of course, their association with Carnival leaked to the public en masse had absolutely no idea of their exposure. And if they asked Carnival about it? Well:

As recently as four days ago, we heard “I’m in the breach per HIBP, but Carnival is telling me there’s no breach!” pic.twitter.com/YYmGm3NzEY

— Troy Hunt (@troyhunt) May 28, 2026

So, why the delay? Last week's press coverage may give some insight:

thorough and time-consuming analysis of the impacted data

Often, the reason I hear for disclosure lag is "we needed to fully assess the scope of exposed data before notifying people". The issue I have with this position is that it implies that even an early heads-up can't happen until there's a very comprehensive understanding of the impact. There are many things that take time to establish after a data breach: the jurisdiction each individual sits in, the precise data that was exposed about them and additional information that may be buried in terabytes of exfiltrated data in all sorts of different formats. But pulling out email addresses and sending early notification is very easy - I've literally done it a thousand times now.

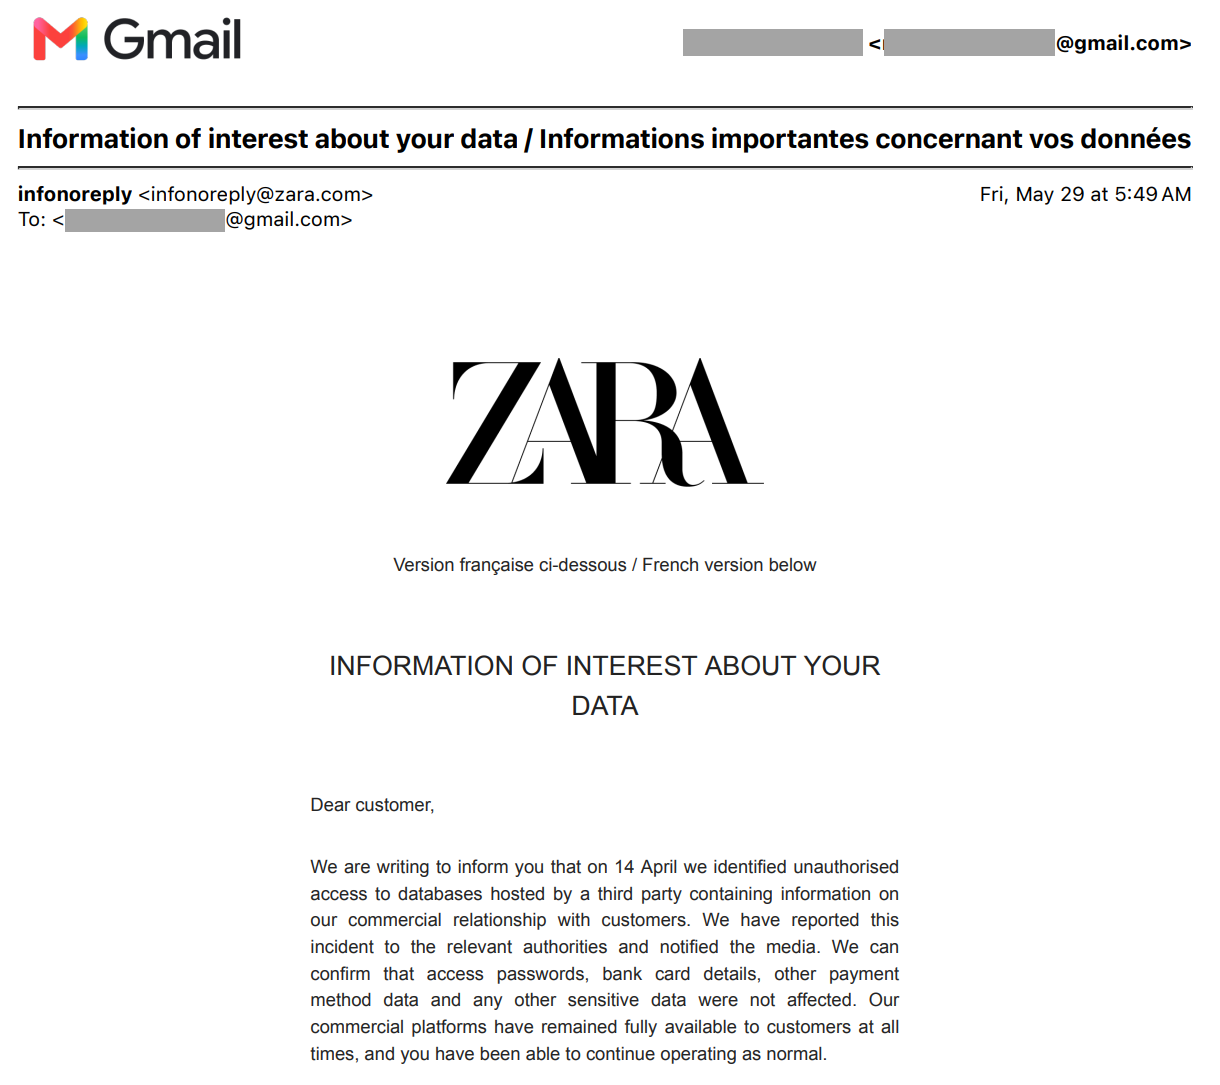
This isn't just a Carnival issue; in fact, it was off the back of this next one only a few days later that I was prompted to write this post:

1,000 Data Breaches Later, the Disclosure Lag is Worse Than Ever

FFS. 45 days. Even worse than Carnival. And like Carnival, very broadly distributed and easily accessible by the masses, including HIBP:

New breach: Zara was named as a ShinyHunters victim last month, after which data containing 197k unique email addresses was published. Impacted data included customer support records, product SKUs and order IDs. 60% were already in @haveibeenpwned. More: https://t.co/0hIQbqoBCk

— Have I Been Pwned (@haveibeenpwned) May 8, 2026

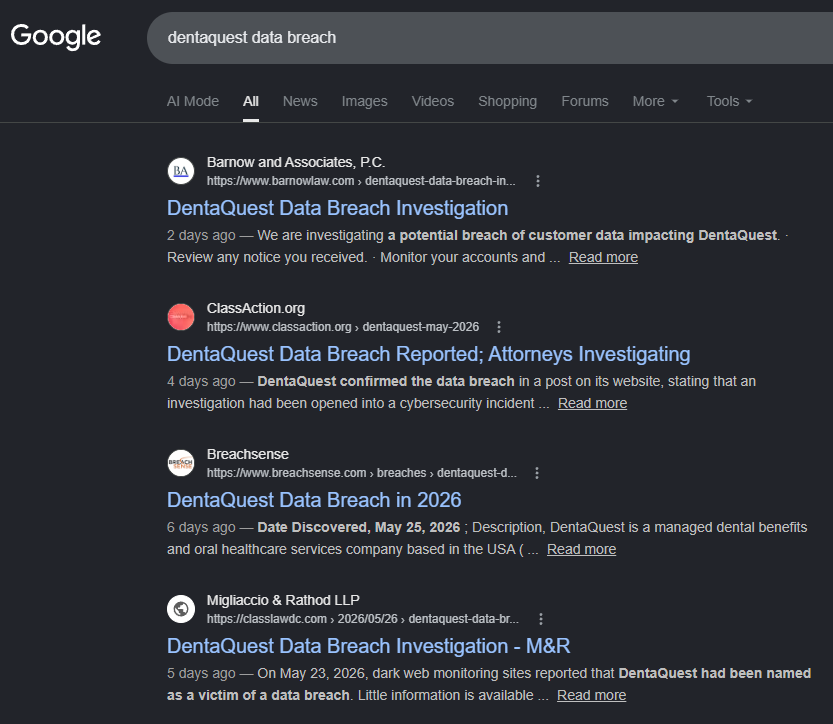
I have a working theory that the disclosure lag is worsening in part due to the proliferation of class actions immediately following a breach. In my live stream last weekend, I did a quick search for the DentaQuest breach:

1,000 Data Breaches Later, the Disclosure Lag is Worse Than Ever

Three of the first four results are all for class actions related to the breach, and there are two more class action results a little further down the page. I've been raising concerns about the adverse impact of class actions for many years now, and it's worse than I've ever seen. By a big margin, too.

It's not just me observing how the behaviour of these orgs appears to be influenced by how lawyers will respond, either. Have a read of this post from Roby Joyce (check out his bio if you don't already know why he's worth paying attention to) after he learned about his exposure in the ZenBusiness breach via HIBP:

What especially caught my eye was this sentence:

That is not a customer-protection posture. That is a litigation posture.

This isn't about prioritising the customer, it's about protecting the organisation. I don't think most people understand that organisational accountability really lies with their shareholders, first and foremost. All the pleasantries around "customers are our number one priority" and "we take security seriously" are all secondary to shareholder happiness, and minimising the chances of getting their arses sued into oblivion is a big part of that.

Rob's quoted comment above came immediately after the response he received from ZenBusiness after asking them about the incident:

If we determine that an incident resulted in the exposure of your protected PII, we will provide notice as legally required

Which brings me to the next problem as it relates to disclosure lag: it may be infinite. By which I mean you may never be told. Ever. GDPR allows it. CCPA allows it. Whatever your local privacy regulation acronym is also allows it. A couple of years ago, I wrote about the data breach disclosure conundrum, where I explained how privacy regs have very specific carve-outs around the circumstances under which data breach victims must be notified. For example:

If the breach is likely to result in a high risk of adversely affecting individuals’ rights and freedoms, you must also inform those individuals without undue delay.

That's in the UK, here's our carve-out in Australia:

Under the Notifiable Data Breaches scheme, an organisation or agency that must comply with Australian privacy law has to tell you if a data breach is likely to cause you serious harm

You see the loophole, right? As far as I know, ZenBusiness still hasn't contacted any individual victims. And like Carnival and Zara, their data is all over the place. Same with Charter, which was in the press last week, where they were quoted as saying the following:

No sensitive personal information (PI) or customer proprietary network information (CPNI) data was exfiltrated by the threat actor as a result of recent activity

I'm not aware of any disclosure they've made to individuals, but to use Rob's term, that sentence reads like legal posturing to me. It's technically correct, of course: there are very clear definitions for sensitive PII, for example, under California's CCPA:

a specific subset of personal information that includes certain government identifiers (such as social security numbers); an account log-in, financial account, debit card, or credit card number with any required security code, password, or credentials allowing access to an account; precise geolocation; contents of mail, email, and text messages; genetic data; biometric information processed to identify a consumer; information concerning a consumer’s health, sex life, or sexual orientation; or information about racial or ethnic origin, religious or philosophical beliefs, or union membership.

GDPR has a similar definition for "special categories of personal data":

personal data revealing racial or ethnic origin, political opinions, religious or philosophical beliefs, or trade union membership, and the processing of genetic data, biometric data for the purpose of uniquely identifying a natural person, data concerning health or data concerning a natural person’s sex life or sexual orientation

In other words, none of this applies to any of the ShinyHunters breaches in the examples I've been providing above.

I've been in many meetings with breached companies over the years where they're obviously aiming to skirt around disclosure obligations. Clearly, these obligations aren't legal ones, but I will argue they're social ones. We expect to be notified when our data is leaked, and we believe organisations should be required to inform us. Therein lies the gap.

I'll finish by recognising that every organisation I've referred to here, and indeed every one I've loaded into HIBP, has been the victim of a criminal act. I'm especially sympathetic to those who've been the target of an aggressive extortion campaign, and I know it's been an absolute nightmare for the folks in those companies who've been left to clean up the mess. However... here we are. Clearly, their goals are misaligned with ours regarding breach disclosure, and that's why, 1,000 breaches later, HIBP still exists.

  •  

Weekly Update 506

Weekly Update 506

I'm finding it quite fascinating to watch the current spate of ShinyHunters breaches and dumps. There's the obvious criminality of it all, but then there's also the response from organisations (or lack thereof, as it relates to disclosure to victims), the appearance and disappearance of victims on their dark web site, the speculation around payments and so on and so forth. And it's seemingly endless - I mentioned DentaQuest during the video, and sure enough, the next day, a 233GB corpus allegedly from them was dropped. By the next update, it might be BCD Travel as well and who knows which other services will appear on the "pay or leak" list. Strange times, I can't remember it ever being this crazy before TBH.

Weekly Update 506
Weekly Update 506
Weekly Update 506
Weekly Update 506
  •  
❌