❌

Reading view

Cloud Storage Scam Emails and Record-Breaking Fraud Losses: This Week in Scams 
Fake cloud email example

You open your inbox and see it: Your cloud storage is full. 

There’s a warning about photos being deleted, your account being suspended, or a renewal failing. There’s a button to “fix it now.” Or a warning to “act today.” 

It looks routine. Maybe even urgent enough to click. 

That’s exactly the point. 
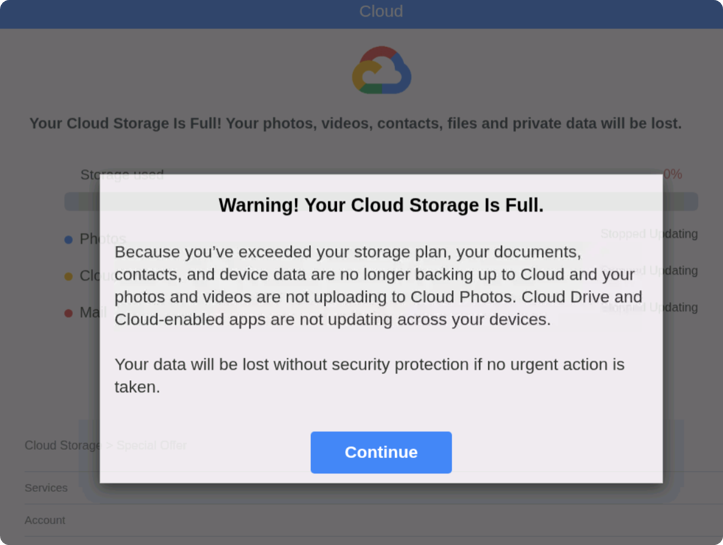
An example of a cloud storage scam detected by McAfee.

Cloud storage scams are making headlines again, building on patterns we flagged earlier this year in our State of the Scamiverse research.  

These emails have circulated steadily since 2025, often impersonating trusted brands like Apple, Microsoft, and Google. Many are timed to moments when people are already thinking about storage, backups, or subscriptions. 

The safest move is simple: pause and don’t click. If there’s a real issue, go directly to your account through the official app or website. 

You can also protect yourself with McAfee’s Scam Detector, which flags suspicious links and messages, including cloud storage scams, and explains why they may be risky. 

What Is A Cloud Storage Scam And How Does It Work? 

Cloud storage scams are phishing attacks designed to trick you into believing there’s an issue with your account so you’ll click a malicious link.

They often look like this, and include 3 key red flags:  

  • Messages that create urgency like “act now or lose your data”  
  • Generic greetings instead of your name  
  • Links that don’t match the official domain  

How the scam works (step-by-step) 

Step  What happens  What to do  How McAfee helps 
1. You receive a message  Email or text claims your storage is full or your account has an issue  Don’t click links directly from the message  Scam Detector flags suspicious messages before you interact 
2. Urgency is introduced  Warning that files or photos will be deleted if you don’t act  Pause. Urgency is a red flag  Scam Detector identifies pressure-based scam patterns 
3. You’re pushed to a link  Link mimics a real login or billing page  Go directly to the official website instead  Safe browsing tools help block malicious sites 
4. You’re asked for info  Login credentials or payment details requested  Never enter info from a link you didn’t verify  Scam Detector explains why a page or link is risky 
5. Data is captured  Scammers collect your data or payment  Monitor accounts and report suspicious activity  Identity monitoring alerts you if your data is exposed 

 Why This Scam Works 

  • Familiar brands: Messages often appear to come from trusted platforms like Apple iCloud or Google Drive  
  • Emotional pressure: The threat of losing photos or files triggers quick decisions  
  • Routine context: Storage alerts feel normal, so people don’t question them  

And that, my friends, is scam number one in this week’s This Week in Scams. 

Let’s get into what else is on our radar. 

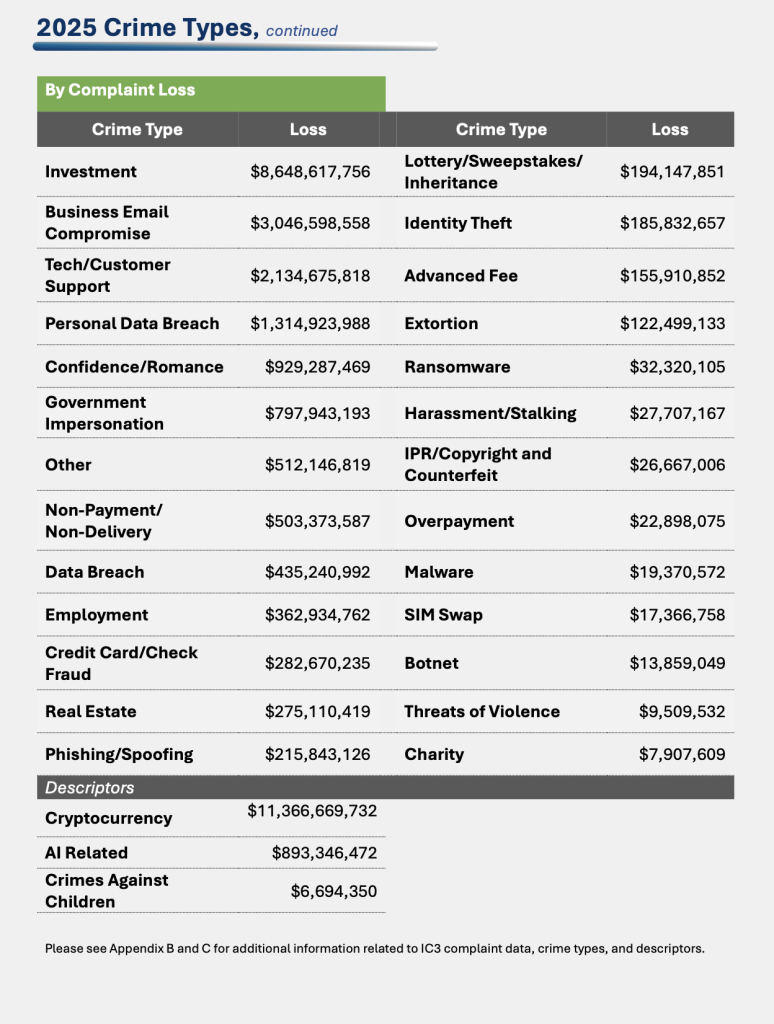
FBI Report: Over $20 Billion Lost to Scams in 2025

New data from the FBI’s Internet Crime Complaint Center (ICC) shows just how large the scam economy has become. 
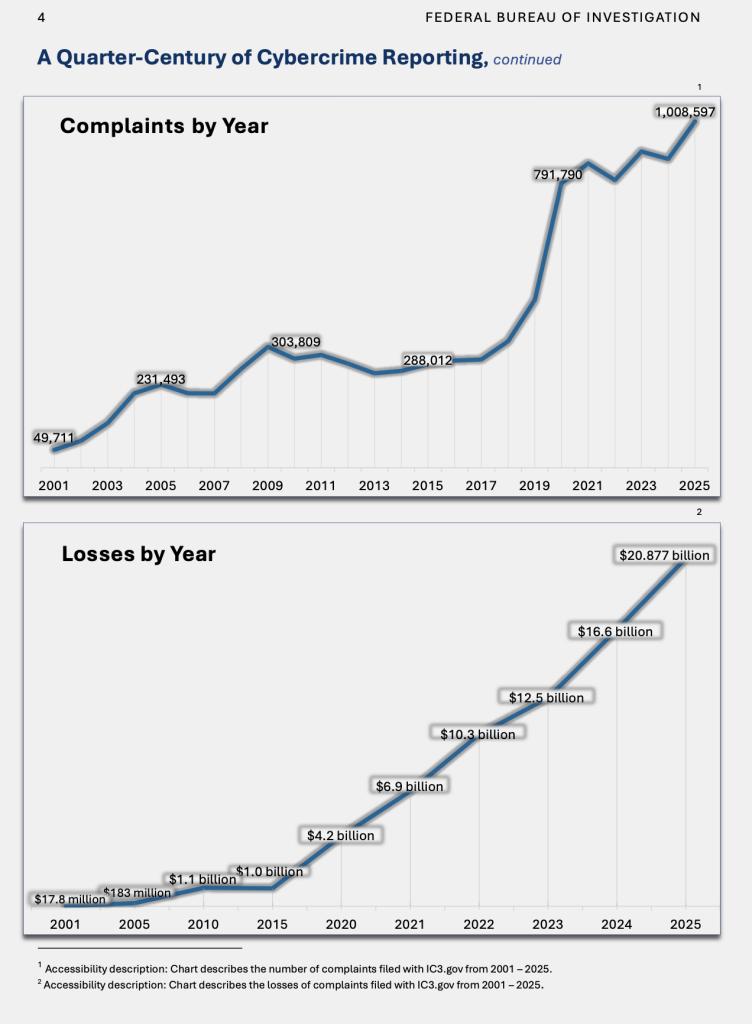
 Accessibility description: Chart describes the number of complaints filed with IC3.gov from 2001 – 2025. 2 Accessibility description: Chart describes the losses of complaints filed with IC3.gov from 2001 – 2025. (Image Courtesy, FBI)
Cybersecurity-related fraud losses topped $20 billion in 2025. (Image Courtesy, FBI)

In 2025 alone: 

  • Americans reported over $20.8 billion in losses  
  • More than 1 million complaints were filed  
  • That’s roughly 3,000 complaints per day  
(Image Courtesy, FBI)
Investment-related fraud topped the charts, with over $8.5 billion lost to investment cybercrime in 2025. And that’s just losses that were reported. Not everyone reports when they were scammed. (Image Courtesy FBI)

This is where layered protection matters. It’s not just about catching one bad link. It’s about recognizing patterns across messages, platforms, and moments when something feels slightly off. 

How McAfee Protects You From Scams and Cyber Threats 

McAfee+ Advanced gives you multiple layers working together so you are not left figuring it out after the damage is done:  

  • Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast 
  • Personal Data Cleanup helps remove your information from data broker sites, making you harder to target in the first place 
  • Scam Detector flags suspicious texts, emails, links, and even deepfake videos before you engage 
  • Safe Browsing helps block risky sites if you do click 
  • Device Security helps detect malicious apps or downloads 
  • Secure VPN keeps your data private, especially on public Wi-Fi   

McAfee Safety Tips This Week 

As always, we have some best practices and safety tips for navigating life online: 

  • Pause before clicking, especially when a message creates urgency  
  • Go directly to websites or apps instead of using email links  
  • Be skeptical of routine account alerts that push immediate action  
  • Double-check sender addresses and URLs closely  
  • Use tools like McAfee’s Scam Detector to flag suspicious links and messages before interacting  
  • Turn on identity monitoring so you’re alerted if your data is exposed 

And we’ll be back next week with more scams making headlines. 

The post Cloud Storage Scam Emails and Record-Breaking Fraud Losses: This Week in Scams  appeared first on McAfee Blog.
  •  

Here's What Agentic AI Can Do With Have I Been Pwned's APIs

Here's What Agentic AI Can Do With Have I Been Pwned's APIs

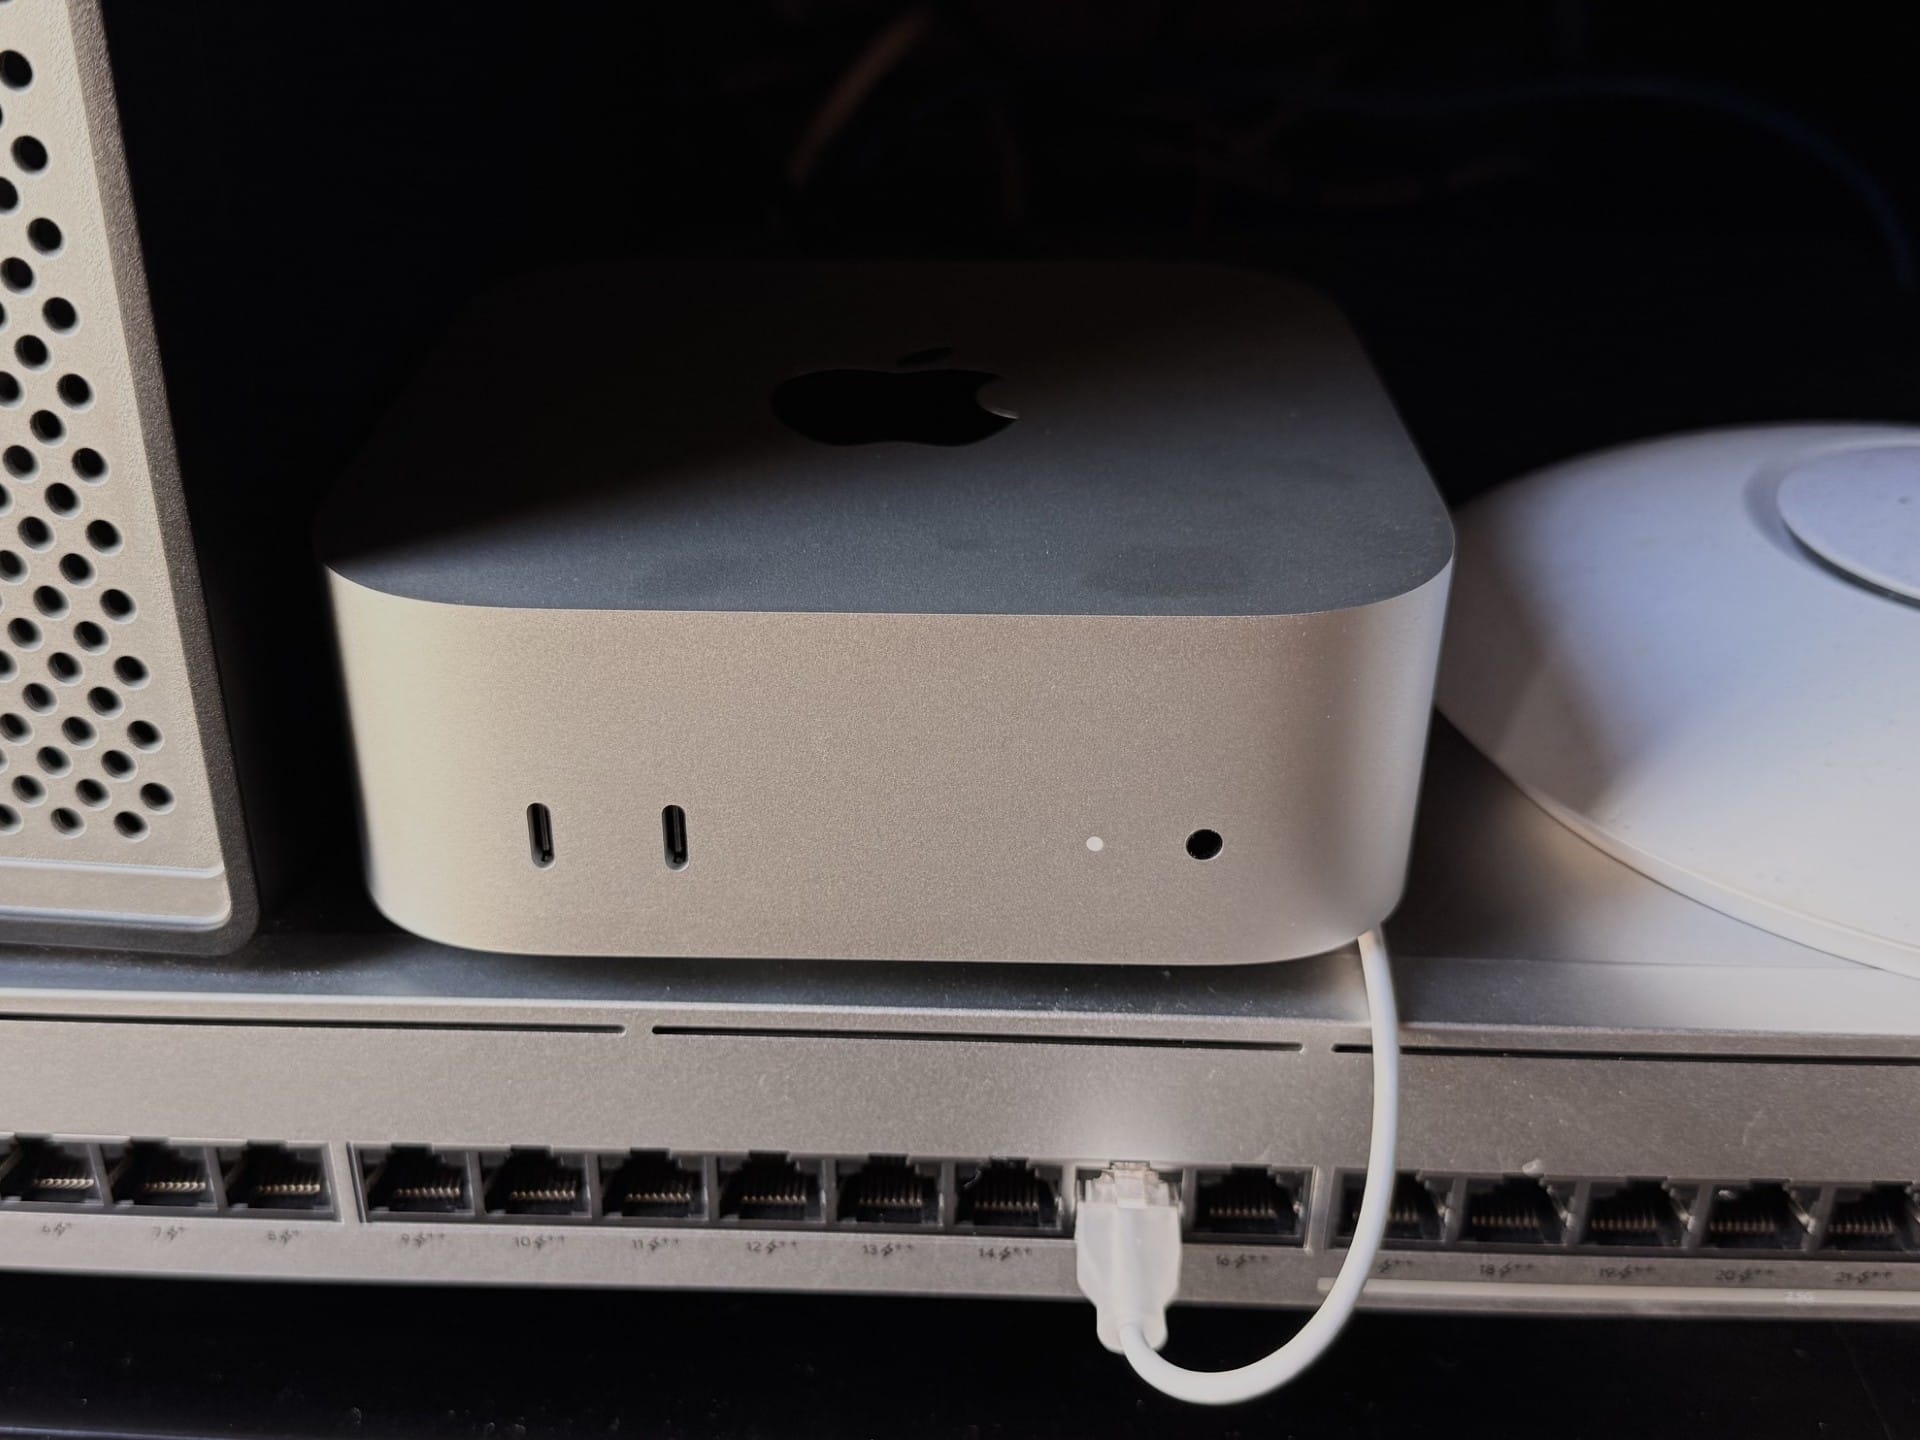
I love cutting-edge tech, but I hate hyperbole, so I find AI to be a real paradox. Somewhere in that whole mess of overnight influencers, disinformation and ludicrous claims is some real "gold" - AI stuff that's genuinely useful and makes a meaningful difference. This blog post cuts straight to the good stuff, specifically how you can use AI with Have I Been Pwned to do some pretty cool things. I'll be showing examples based on OpenClaw running on the Mac Mini in the hero shot, but they're applicable to other agents that turn HIBP's data into more insightful analysis.

So, let me talk about what you can do right now, what we're working on and what you'll be able to do in the future.

Model Context Protocol (MCP)

A quick MCP primer first: Anthropic came up with the idea of building a protocol that could connect systems to AI apps, and thus the Model Context Protocol was born:

Using MCP, AI applications like Claude or ChatGPT can connect to data sources (e.g. local files, databases), tools (e.g. search engines, calculators) and workflows (e.g. specialized prompts)—enabling them to access key information and perform tasks.

If I'm honest, I'm a bit on the fence as to how useful this really is (and I'm not alone), but creating it was a no-brainer, so we now have an MCP server for HIBP:

https://haveibeenpwned.com/mcp

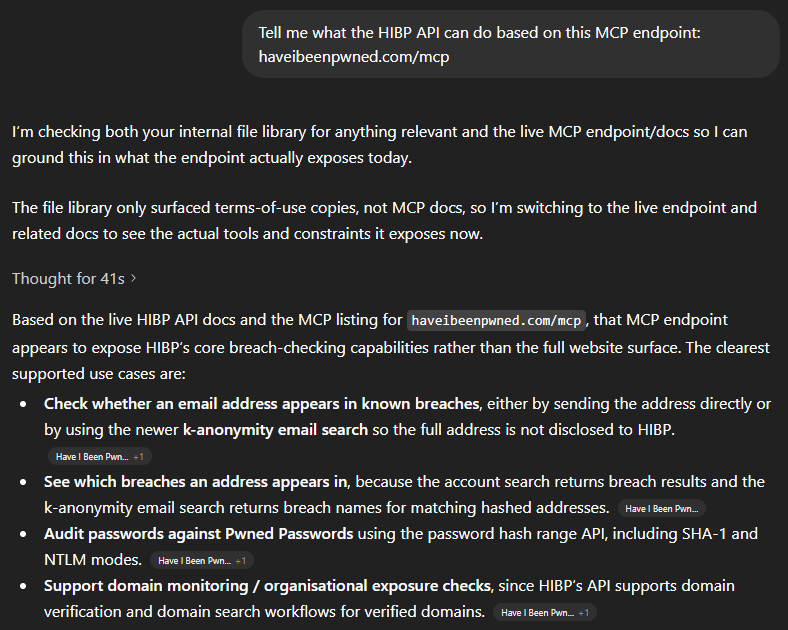
You can't just make an HTTP GET to the endpoint, but you can ask your favourite AI tool to explain what it does:

Here's What Agentic AI Can Do With Have I Been Pwned's APIs

In other words, all the stuff we describe in the API docs 🙂 That's an overly simplistic statement, and there are many nuances MCP introduces beyond a computer reading docs intended for humans, but the point is that we've implemented MCP and it's there if you want it. Which means you can easily use the JSON below to, for example, extend GitHub Copilot:

"HIBP": {
  "url": "https://haveibeenpwned.com/mcp",
  "headers": {
    "hibp-api-key": "YOUR_STANDARD_HIBP_API_KEY"
  },
  "type": "http"
}

Now let's do something useful with it.

Human Use Cases

This is really the point of the whole thing - how can humans use it to do genuinely useful stuff? In particular, how can they use it to do stuff that was hard to do before, and how can "normies" (non-technical folks) use it to do stuff they previously needed developers for? I've been toying with these questions for a while now. Here's what I've come up with:

Firstly, I'm going to do all these demos on OpenClaw. I've been talking a lot about that on my weekly live streams over the past month, and the "agentic" nature of it (being able to act as an independent agent tying together multiple otherwise independent acts) is enormously powerful. Every company worth its AI salt is now focusing on building out agentic AI so whilst I'm using OpenClaw for these demos, you'll be able to do exactly the same thing in your platform of choice either now or in the very near future.

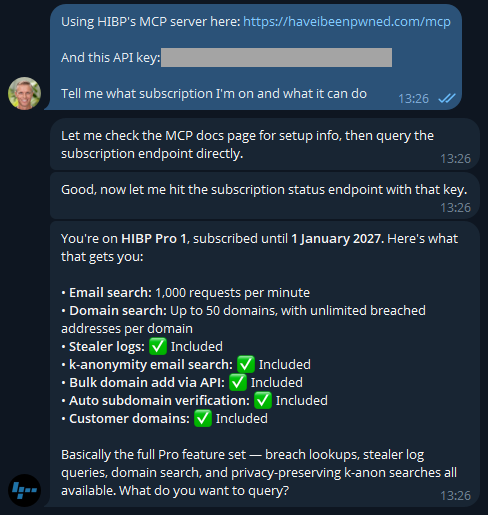
I'm using a Telegram bot as my interface into OpenClaw, let's kick it off:

Here's What Agentic AI Can Do With Have I Been Pwned's APIs

Easy, right? 🙂 There's a different discussion around how secrets are stored and protected, but that's a story for another time (and is also obviously dependent on your agent). But the key is easily rotated on the HIBP dashboard anyway. If you don't have a key already, go and take out a subscription (they start at a few bucks a month), and you'll be up and running in no time.

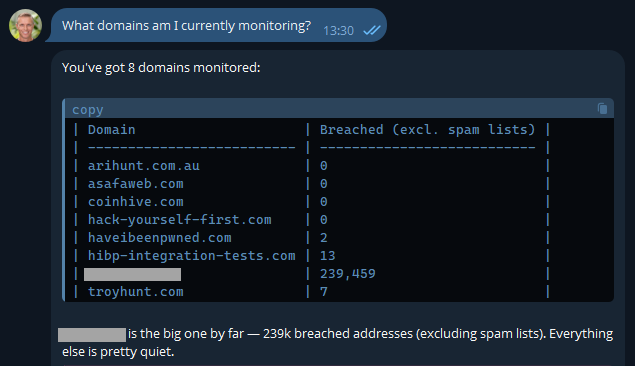
Now that I know I'm connected, let's learn about how I'm presently using the service:

Here's What Agentic AI Can Do With Have I Been Pwned's APIs

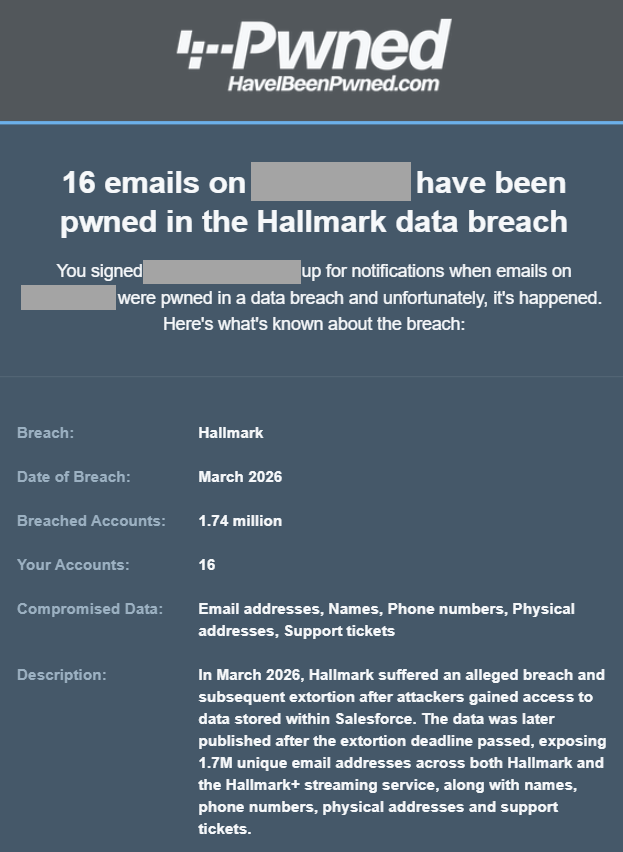
Most of these are pretty obvious, but I've also included another here that I use to monitor how the service is behaving with a large organisation. It's a real domain with real data, so I'm going to obfuscate it to preserve privacy, but it's a great demonstration of how useful AI is. In fact, the inspiration of this blog post was when I received this notification last week:

Here's What Agentic AI Can Do With Have I Been Pwned's APIs

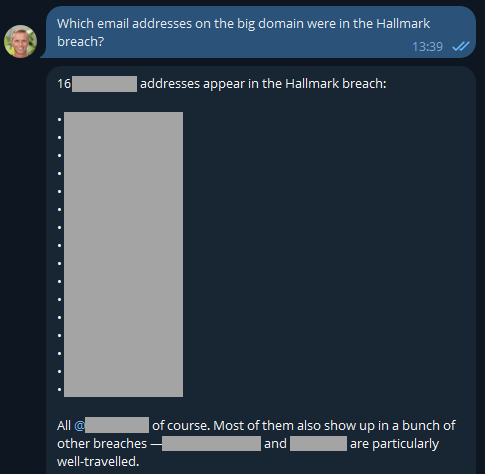
One of the most asked questions after someone in a large org receives an email like this is "who are those 16 people in the breach"? Because we can't reliably filter large domains in the UI, I'd normally suggest they either download the CSV or JSON format in the dashboard, then search for "Hallmark" in there or use the API and write some code. But now, there's a much easier way:

Here's What Agentic AI Can Do With Have I Been Pwned's APIs

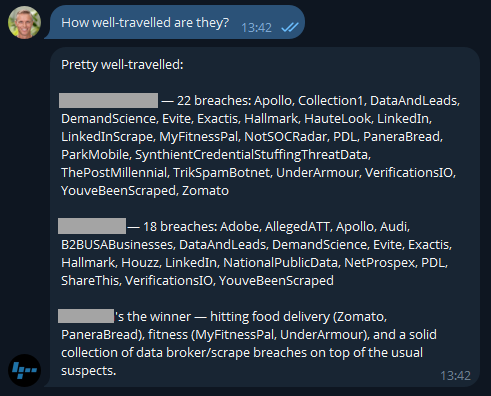
Well that was easy 😎 I like the additional context too, and now it has me curious: what have these people been up to?

Here's What Agentic AI Can Do With Have I Been Pwned's APIs

Because I'm on a Pro plan (or if you're still on the old Pwned 5 plan), I've also got access to stealer logs. Let's see what's going on there:

Here's What Agentic AI Can Do With Have I Been Pwned's APIs

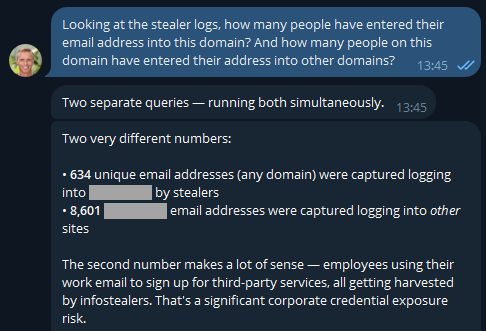
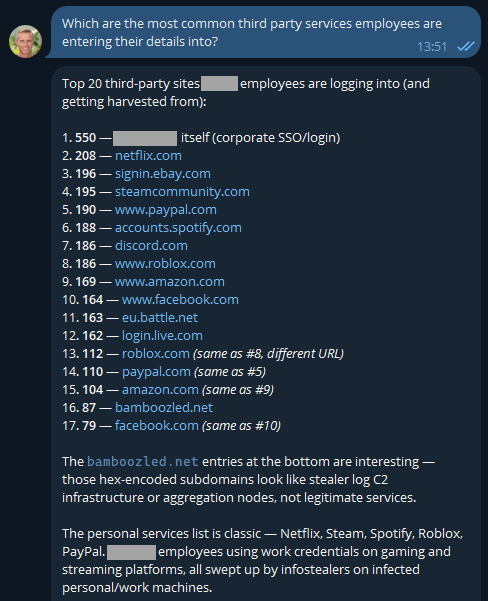
If you were running an online service, that first number would indicate compromised customers. But as OpenClaw has suggested here, the second number is the one that's interesting in terms of employees entering their data into other websites using the corporate email address. But they'd never reuse the same password as the work one, right? 🤔 Best check which services they're entering organisational assets into:

Here's What Agentic AI Can Do With Have I Been Pwned's APIs

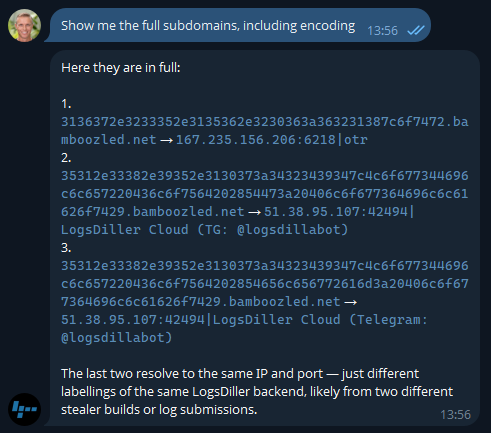
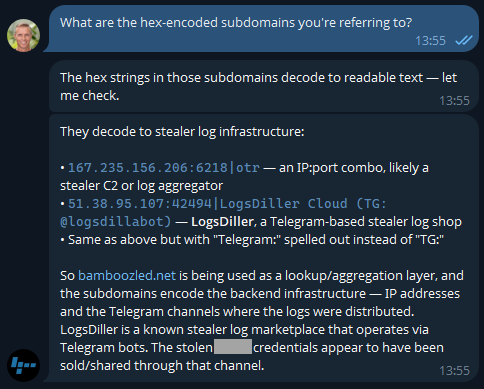
The first one makes sense and is extra worrying when you consider these are people infected with infostealers. That's not necessarily malware on a corporate asset; they could always be using an infected personal device to sign into a corporate asset... ok, that's also pretty bad! I was a bit surprised to see Steam in there TBH - who's using their corporate email address to sign into a gaming platform?! A quiet chat with them might be in order. And the bamboozled.net stuff is weird, I want to understand a bit more about that:

Here's What Agentic AI Can Do With Have I Been Pwned's APIs

Now I'm losing interest in this blog post and am really curious as to what's actually in the data!

Here's What Agentic AI Can Do With Have I Been Pwned's APIs

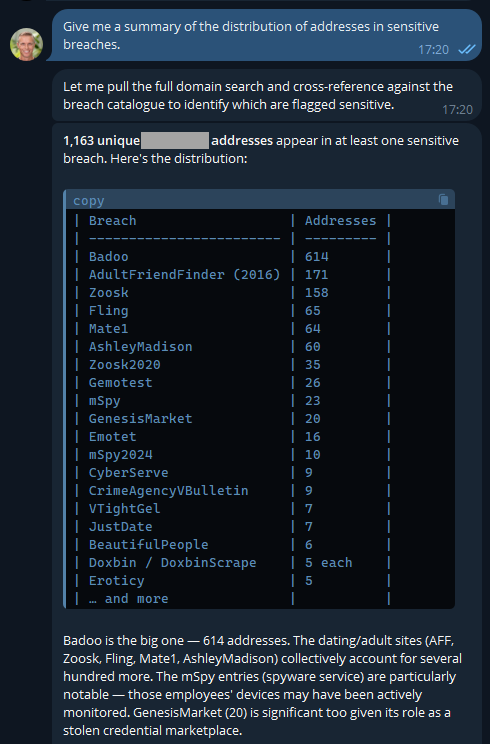
Ok, so there's an entire rabbit hole over there! Let's park that, but think about how useful information like this is to infosec teams when you can pull it so easily. Or how useful info like this is to HR teams 😬

Here's What Agentic AI Can Do With Have I Been Pwned's APIs

Keep in mind, these are corporate addresses tied to the company and are the company's property, so, yeah...

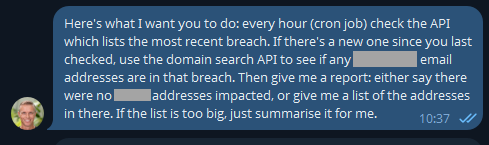
But remember the agentic nature of OpenClaw means we can ask it to go off and run tasks in the background, tasks like this:

Here's What Agentic AI Can Do With Have I Been Pwned's APIs

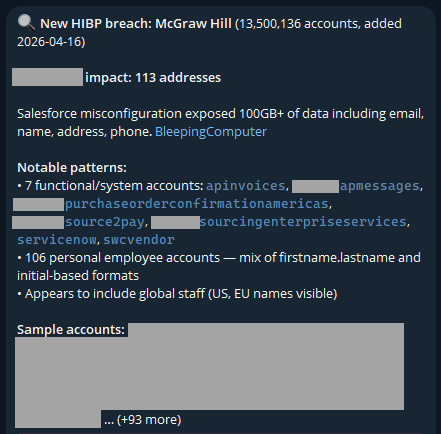
This was just a little thought experiment I set up a few days ago and forgot about until yesterday, when I loaded a new breach:

Here's What Agentic AI Can Do With Have I Been Pwned's APIs

I never asked it to look for "functional/system accounts"; it just decided that was relevant. And it is - this breach clearly had a lot of data in it related to purchases of services, which is an interesting aspect.

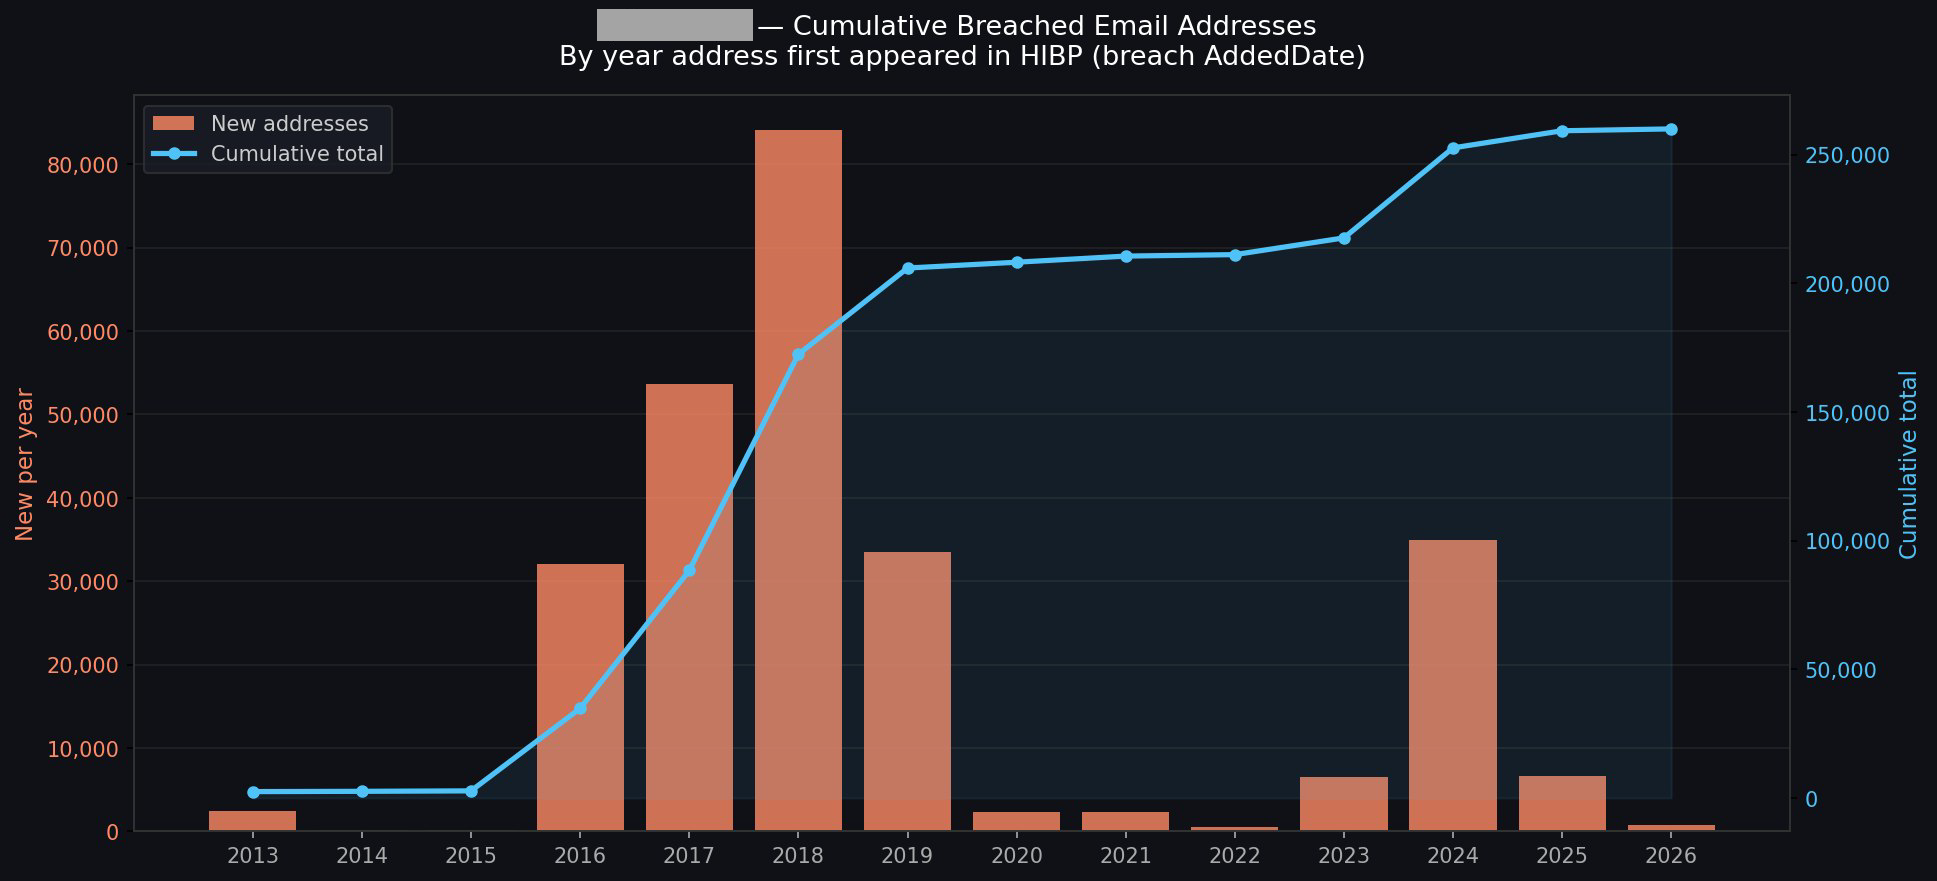
The idea of running stuff on a schedule opens up a whole raft of new opportunities. For example, monitoring your family's email addresses: "let me know when mum@example.com appears in a new breach". From here, your creativity is the only limit (and even that statement is debatable, given how much stuff AI agents come up with on their own). For example, creating visualisations of the data:

Here's What Agentic AI Can Do With Have I Been Pwned's APIs

I could go on and on (I started going down another rabbit hole of having it generate executive-level reports with all the data), but you get the idea.

The AI Pipeline

This is about what's in our pipeline, and the primary theme is putting tooling where it's more easily accessible to the masses. Creating a connector in Claude, an app in ChatGPT, and similar plumbing in the other big players' AI tools is an obvious next step. This will likely involve adding an OAuth layer to HIBP, allowing end users to configure the respective tools to query those HIBP APIs under their identity and achieve the same results as above, but built into the "traditional" AI tooling in a way people are familiar with.

Future

A big part of this is about AI enabling more human conversations to achieve technical outcomes. I spotted this from Cloudflare just yesterday, and it's a perfect example of just this:

Cloudflare dashboard can now complete tasks for you.

- "Create a Worker and bind a new R2 bucket to it"
- "Change my DNS records to 1.1.1.1"
- "How many errors have happened this week"

Not only do we tell you, but we show you with generative UI.

PROTIP: Use full-screen mode. pic.twitter.com/Q1o1vyoOwk

— Brayden (@BraydenWilmoth) April 15, 2026

I've been pretty blown away by both how easy this process has been and how much insight I've been able to draw from data I've been sitting on for ages. We'll be building out more tooling and easily reproducible demos in the future, and I'm sure a lot of that will do stuff we haven't even thought of yet. If you give this a go and find other awesome use cases, please leave a comment and tell me what you've done, especially if you've cut through the hyperbole and created some genuinely awesome stuff 😎

  •  

Designing for What’s Next: Securing AI-Scale Infrastructure Without Compromise

6100 Series is an ultra-high-end firewall, delivering exceptional performance, line-rate threat protection, and modular scalability at AI-ready data centers.
  •  

Patch Tuesday, April 2026 Edition

Microsoft today pushed software updates to fix a staggering 167 security vulnerabilities in its Windows operating systems and related software, including a SharePoint Server zero-day and a publicly disclosed weakness in Windows Defender dubbed “BlueHammer.” Separately, Google Chrome fixed its fourth zero-day of 2026, and an emergency update for Adobe Reader nixes an actively exploited flaw that can lead to remote code execution.

A picture of a windows laptop in its updating stage, saying do not turn off the computer.

Redmond warns that attackers are already targeting CVE-2026-32201, a vulnerability in Microsoft SharePoint Server that allows attackers to spoof trusted content or interfaces over a network.

Mike Walters, president and co-founder of Action1, said CVE-2026-32201 can be used to deceive employees, partners, or customers by presenting falsified information within trusted SharePoint environments.

“This CVE can enable phishing attacks, unauthorized data manipulation, or social engineering campaigns that lead to further compromise,” Walters said. “The presence of active exploitation significantly increases organizational risk.”

Microsoft also addressed BlueHammer (CVE-2026-33825), a privilege escalation bug in Windows Defender. According to BleepingComputer, the researcher who discovered the flaw published exploit code for it after notifying Microsoft and growing exasperated with their response. Will Dormann, senior principal vulnerability analyst at Tharros, says he confirmed that the public BlueHammer exploit code no longer works after installing today’s patches.

Satnam Narang, senior staff research engineer at Tenable, said April marks the second-biggest Patch Tuesday ever for Microsoft. Narang also said there are indications that a zero-day flaw Adobe patched in an emergency update on April 11 — CVE-2026-34621 — has seen active exploitation since at least November 2025.

Adam Barnett, lead software engineer at Rapid7, called the patch total from Microsoft today “a new record in that category” because it includes nearly 60 browser vulnerabilities. Barnett said it might be tempting to imagine that this sudden spike was tied to the buzz around the announcement a week ago today of Project Glasswing — a much-hyped but still unreleased new AI capability from Anthropic that is reportedly quite good at finding bugs in a vast array of software.

But he notes that Microsoft Edge is based on the Chromium engine, and the Chromium maintainers acknowledge a wide range of researchers for the vulnerabilities which Microsoft republished last Friday.

“A safe conclusion is that this increase in volume is driven by ever-expanding AI capabilities,” Barnett said. “We should expect to see further increases in vulnerability reporting volume as the impact of AI models extend further, both in terms of capability and availability.”

Finally, no matter what browser you use to surf the web, it’s important to completely close out and restart the browser periodically. This is really easy to put off (especially if you have a bajillion tabs open at any time) but it’s the only way to ensure that any available updates get installed. For example, a Google Chrome update released earlier this month fixed 21 security holes, including the high-severity zero-day flaw CVE-2026-5281.

For a clickable, per-patch breakdown, check out the SANS Internet Storm Center Patch Tuesday roundup. Running into problems applying any of these updates? Leave a note about it in the comments below and there’s a decent chance someone here will pipe in with a solution.

  •  

Can Your Wearable Health Monitors Be Compromised?

Wearable health devices are designed to give you more control over your body and your data. 

But in 2026, the bigger risk isn’t someone spying on your smartwatch or smartring in real time. It’s what happens if the data connected to that device gets exposed. 

Health data, login credentials, and behavioral patterns tied to wearables can become valuable signals for cybercriminals. And once that data is out, it can fuel everything from identity theft to highly targeted scams. 

Here’s what’s actually at risk, and how to protect yourself. 

What Is Wearable Health Data (and Why It Matters) 

Wearable health data refers to the personal information collected and stored by devices like fitness trackers, smartwatches, and connected medical monitors. 

This can include: 

  • Heart rate and activity levels  
  • Sleep patterns  
  • Location data  
  • Medical metrics (like glucose levels)  
  • Account credentials tied to apps and dashboards  

On its own, this data may seem harmless. But combined, it creates a highly detailed profile of your habits, routines, and health status. 

The Real Risk in 2026 Isn’t the Device. It’s the Data. 

Early conversations around wearable security focused on device hacking or surveillance. 

Today, the bigger concern is data exposure. 

If wearable platforms, apps, or connected services are breached, your data could be: 

  • Sold on the dark web  
  • Used to impersonate you  
  • Leveraged in targeted phishing or health-related scams  

And because this data is personal and specific, scams built from it can feel far more convincing than generic spam. 

How Exposed Wearable Data Can Lead to Scams 

When cybercriminals gain access to personal data, they don’t just sit on it. They use it. 

Here’s how that plays out: 

Scenario  What It Looks Like  Why It Works 
Health-related phishing  “Your insurance claim was denied” or “Update your health profile”  Feels relevant and urgent 
Account takeover attempts  Password reset emails tied to known apps  Uses real account signals 
Personalized scams  Messages referencing routines, devices, or conditions  Builds trust quickly 
Fake alerts or services  “Device security issue detected”  Mimics real product behavior 


This is where the risk shifts from data privacy → real-world financial and identity impact. 

6 Smart Ways to Protect Your Wearable Data 

1)Install updates immediately
Security patches fix known vulnerabilities. Delaying updates leaves gaps open.  

2) Use layered protection, not just device settings
A VPN and security software help protect data in transit and block threats before they reach you.  

3) Strengthen your login credentials
Use strong, unique passwords and enable two-factor authentication wherever possible.  

4) Limit what you share
Review app permissions and only connect devices to services you trust.  

5) Verify every message or alert
If you receive a message tied to your device or health data, double-check the source before clicking.  

6) Monitor your accounts regularly
Small signs of unusual activity can be early indicators of larger issues. 

How McAfee Helps Protect Your Data Beyond the Device 

Protecting your wearable doesn’t stop at the device itself. It extends to what happens if your data is exposed or targeted. 

Identity Monitoring 

McAfee helps track your personal information across known breach sources and alerts you if your data appears where it shouldn’t. 

This gives you early warning if wearable-related accounts or associated data are compromised. 

Scam Detector 

If your data is exposed, scammers often follow. 

McAfee’s Scam Detector helps identify suspicious messages, links, and communications before you engage, and explains why something was flagged, so you can make informed decisions quickly. 

Together, these tools help protect not just your device, but the chain reaction that can follow a data breach. 

The post Can Your Wearable Health Monitors Be Compromised? appeared first on McAfee Blog.

  •  

Weekly Update 499

Weekly Update 499

I'm starting to become pretty fond of Bruce. Actually, I've had a bit of an epiphany: an AI assistant like Bruce isn't just about auto-responding to tickets in an entirely autonomous manner; it's also pretty awesome at responding with just a little bit of human assistance. Charlotte and I both replied to some tickets today that were way too specific for Bruce to ever do on his own, but by feeding in just a little bit of additional info (such as the number of domains someone was presently monitoring), Bruce was able to construct a really good reply and "own" the ticket. So maybe that's the sweet spot: auto-reply to the really obvious stuff and then take just a little human input on everything else.

Weekly Update 499
Weekly Update 499
Weekly Update 499
Weekly Update 499
  •  

Social Security Scam Emails and a Healthcare Data Breach: This Week in Scams

Emails claiming to be from Social Security are making the rounds right now. 

They look official. They sound official. And they’re designed to get you to click before you think twice. 

The Social Security Administration’s Office of Inspector General is warning about a spike in messages that claim your Social Security statement is ready to download. The goal is simple. Get you to click a link or open an attachment. 

From there, things can go sideways fast. 

Before interacting with anything like this, it’s worth pausing and running it through a tool like McAfee’s Scam Detector. This is exactly the kind of message it’s built to flag. Something that looks legitimate, but feels just slightly off. 

How The Scam Works 

The email mimics official government communication, using logos, formatting, and language that feels familiar. It might say your statement is ready, your account needs attention, or you need to review a document. 

Once you click: 

  • You may be sent to a fake website designed to capture your personal information  
  • You may download malware without realizing it  
  • Or you may be prompted to enter sensitive financial details  
  • Either way, the goal is the same: get access to your identity. 

The Red Flags In These Emails 

  • Messages claiming your social security statement is ready to download  
  • Links or attachments labeled as official documents  
  • Urgency pushing you to act quickly  
  • Sender addresses that do not end in “.Gov”  

The biggest tell: Social Security does not send emails like this asking you to download statements or provide sensitive information. 

What To Do If You Get One 

  • Do not click links or download attachments  
  • Delete the email immediately  
  • Access your account by going directly to the official SSA website  
  • Report the message to the SSA Office of Inspector General  

If you already clicked: 

  • Stop communication immediately  
  • Contact your financial institutions  
  • Monitor your accounts closely  
  • Report the incident to the FTC or the FBI’s IC3  

And that, my friends, is scam number one in this week’s This Week in Scams. 

Let’s get into what else is on our radar. 

A Healthcare Data Breach That Could Lead to Follow-Up Scams 

Healthcare data breaches don’t always make headlines the same way big tech breaches do, but they can be just as serious. 

According to reporting from Fox News, CareCloud, a company that supports electronic health records for tens of thousands of providers, recently confirmed a security incident involving unauthorized access to one of its systems.  

The access lasted several hours. And while it’s still unclear whether any data was taken, that uncertainty is exactly what makes situations like this risky. 

Because even if you’ve never heard of the company, your doctor might use it. 

Why This Matters 

Healthcare data is incredibly valuable. It can include: 

  • Names and social security numbers  
  • Insurance details  
  • Medical history  
  • Billing information  

Unlike a credit card, you can’t just cancel your medical history. 

And when that kind of data is exposed or even potentially exposed, scammers often follow up with messages that feel highly specific and personal. 

What To Watch For Next 

After incidents like this, scammers often move quickly: 

  • Emails or texts pretending to be your provider  
  • Messages about billing issues or medical records  
  • Requests to “verify” your information  
  • Links to log in or update your account  

These scams work because they’re timed perfectly and feel relevant. 

This is another moment where Scam Detector can help flag suspicious links or messages before you engage, even when they reference real healthcare providers. 

How To Protect Yourself 

  • Review medical bills and insurance statements for unfamiliar activity  
  • Enable two-factor authentication on patient portals  
  • Use strong, unique passwords  
  • Avoid clicking links in unexpected healthcare-related messages  
  • Consider identity monitoring to catch misuse early  

Where McAfee Steps In (So You Don’t Have to Guess) 

Scams today are layered. 

A fake email leads to stolen credentials. A breach leads to targeted phishing. And those follow-ups are getting harder to spot. 

McAfee+ Advanced gives you multiple layers working together so you are not left figuring it out after the damage is done: 

  • Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
  • Personal Data Cleanup helps remove your information from data broker sites, making you harder to target in the first place
  • Scam Detector flags suspicious texts, emails, links, and even deepfake videos before you engage
  • Safe Browsing helps block risky sites if you do click
  • Device Security helps detect malicious apps or downloads
  • Secure VPN keeps your data private, especially on public Wi-Fi  

Safety Tips To Carry Into Next Week 

  • Be cautious of emails that look official but create urgency  
  • Never trust unsolicited messages asking for personal or financial information  
  • Go directly to official websites instead of clicking links  
  • Stay alert after any breach or security incident makes headlines  
  • Use tools like McAfee that help you verify what’s real before you act  

Because the reality is, scams are designed to look legitimate. You shouldn’t have to figure it out on your own. We’re safer together. 

We’ll be back next week with more scams making headlines. 

The post Social Security Scam Emails and a Healthcare Data Breach: This Week in Scams appeared first on McAfee Blog.
  •  

McAfee’s Scam Detector Named Webby Awards Finalist for AI Innovation

We’re excited to share that McAfee’s Scam Detector has been named a finalist in the 2026 Webby Awards. 

Recognized in the AI Experiences & Applications – Consumer Application category and named a Webby Honoree for Best Use of AI & Machine Learning, Scam Detector is being acknowledged for its effectiveness as an AI-driven consumer tool. 

This recognition of Scam Detector validates something key in research findings. According to McAfee’s 2026 State of the Scamiverse report, Americans now spend 114 hours a year trying to decide what’s real and what’s fake online. 

Scam Detector was built with this era of uncertainty in mind, designed to help people cut through confusion and identify scams as they appear. The Webby recognition reinforces to us that McAfee’s Scam Detector is doing exactly that. 

What Are the Webby Awards? 

The Webby Awards are presented by the International Academy of Digital Arts & Sciences and recognize excellence across the internet, including apps, software, AI, and digital experiences. 

Each year, thousands of entries are evaluated, with finalists representing the top work in their category globally. 

In addition to judged awards, the Webby Awards include a People’s Voice Award, which is decided by public vote. 

How McAfee’s Scam Detector Uses AI to Stop Scams 

Scam Detector is designed to help people identify scams where they’re most likely to happen, always ready to help you spot what’s real and what’s not when you least expect it. 

It uses AI to analyze and flag suspicious: 

  • Text messages and emails  
  • Links and websites  
  • QR codes  
  • Social media messages  
  • AI-generated and deepfake content  

Beyond detection, Scam Detector explains why something was flagged as risky. That transparency helps show how decisions are made, so people can quickly understand the risk and feel more confident trusting what’s flagged.

As scams become more personalized and harder to detect, this combination of automatic detection and clear guidance is critical to preventing financial loss and identity theft. 

Vote for McAfee’s Scam Detector 

Scam Detector is eligible for the Webby People’s Voice Award, which is decided by public vote. 

If you would like to support McAfee’s Scam Detector, you can vote here: https://vote.webbyawards.com/PublicVoting#/2026/ai/ai-experiences-applications/consumer-application 

Voting is open through Thursday, April 16 at 11:59 pm PDT. 

Winners will be announced on April 21, 2026. 

And a big thank you to the McAfee teams who brought Scam Detector to life and who continuously improve how Scam Detector identifies new threats and adapts to the evolving world of AI-driven scams. 

The post McAfee’s Scam Detector Named Webby Awards Finalist for AI Innovation appeared first on McAfee Blog.

  •  

Russia Hacked Routers to Steal Microsoft Office Tokens

Hackers linked to Russia’s military intelligence units are using known flaws in older Internet routers to mass harvest authentication tokens from Microsoft Office users, security experts warned today. The spying campaign allowed state-backed Russian hackers to quietly siphon authentication tokens from users on more than 18,000 networks without deploying any malicious software or code.

Microsoft said in a blog post today it identified more than 200 organizations and 5,000 consumer devices that were caught up in a stealthy but remarkably simple spying network built by a Russia-backed threat actor known as “Forest Blizzard.”

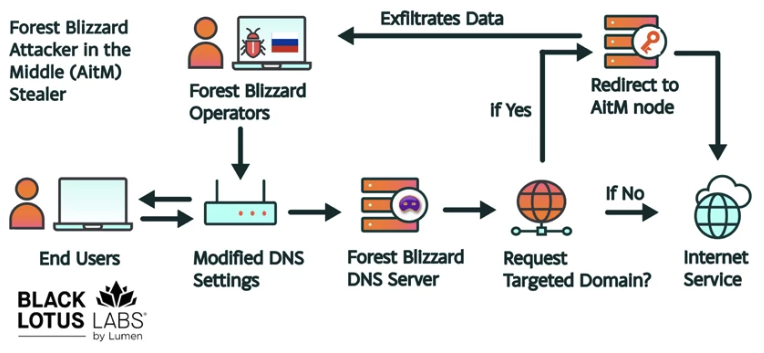
How targeted DNS requests were redirected at the router. Image: Black Lotus Labs.

Also known as APT28 and Fancy Bear, Forest Blizzard is attributed to the military intelligence units within Russia’s General Staff Main Intelligence Directorate (GRU). APT 28 famously compromised the Hillary Clinton campaign, the Democratic National Committee, and the Democratic Congressional Campaign Committee in 2016 in an attempt to interfere with the U.S. presidential election.

Researchers at Black Lotus Labs, a security division of the Internet backbone provider Lumen, found that at the peak of its activity in December 2025, Forest Blizzard’s surveillance dragnet ensnared more than 18,000 Internet routers that were mostly unsupported, end-of-life routers, or else far behind on security updates. A new report from Lumen says the hackers primarily targeted government agencies—including ministries of foreign affairs, law enforcement, and third-party email providers.

Black Lotus Security Engineer Ryan English said the GRU hackers did not need to install malware on the targeted routers, which were mainly older Mikrotik and TP-Link devices marketed to the Small Office/Home Office (SOHO) market. Instead, they used known vulnerabilities to modify the Domain Name System (DNS) settings of the routers to include DNS servers controlled by the hackers.

As the U.K.’s National Cyber Security Centre (NCSC) notes in a new advisory detailing how Russian cyber actors have been compromising routers, DNS is what allows individuals to reach websites by typing familiar addresses, instead of associated IP addresses. In a DNS hijacking attack, bad actors interfere with this process to covertly send users to malicious websites designed to steal login details or other sensitive information.

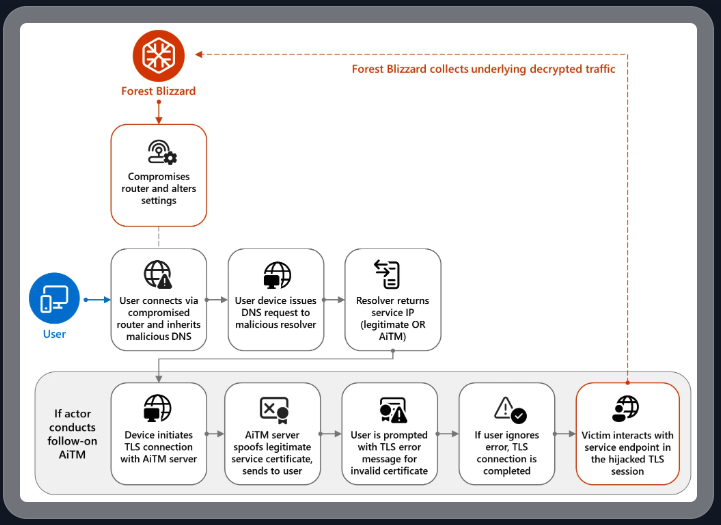
English said the routers attacked by Forest Blizzard were reconfigured to use DNS servers that pointed to a handful of virtual private servers controlled by the attackers. Importantly, the attackers could then propagate their malicious DNS settings to all users on the local network, and from that point forward intercept any OAuth authentication tokens transmitted by those users.

DNS hijacking through router compromise. Image: Microsoft.

Because those tokens are typically transmitted only after the user has successfully logged in and gone through multi-factor authentication, the attackers could gain direct access to victim accounts without ever having to phish each user’s credentials and/or one-time codes.

“Everyone is looking for some sophisticated malware to drop something on your mobile devices or something,” English said. “These guys didn’t use malware. They did this in an old-school, graybeard way that isn’t really sexy but it gets the job done.”

Microsoft refers to the Forest Blizzard activity as using DNS hijacking “to support post-compromise adversary-in-the-middle (AiTM) attacks on Transport Layer Security (TLS) connections against Microsoft Outlook on the web domains.” The software giant said while targeting SOHO devices isn’t a new tactic, this is the first time Microsoft has seen Forest Blizzard using “DNS hijacking at scale to support AiTM of TLS connections after exploiting edge devices.”

Black Lotus Labs engineer Danny Adamitis said it will be interesting to see how Forest Blizzard reacts to today’s flurry of attention to their espionage operation, noting that the group immediately switched up its tactics in response to a similar NCSC report (PDF) in August 2025. At the time, Forest Blizzard was using malware to control a far more targeted and smaller group of compromised routers. But Adamitis said the day after the NCSC report, the group quickly ditched the malware approach in favor of mass-altering the DNS settings on thousands of vulnerable routers.

“Before the last NCSC report came out they used this capability in very limited instances,” Adamitis told KrebsOnSecurity. “After the report was released they implemented the capability in a more systemic fashion and used it to target everything that was vulnerable.”

TP-Link was among the router makers facing a complete ban in the United States. But on March 23, the U.S. Federal Communications Commission (FCC) took a much broader approach, announcing it would no longer certify consumer-grade Internet routers that are produced outside of the United States.

The FCC warned that foreign-made routers had become an untenable national security threat, and that poorly-secured routers present “a severe cybersecurity risk that could be leveraged to immediately and severely disrupt U.S. critical infrastructure and directly harm U.S. persons.”

Experts have countered that few new consumer-grade routers would be available for purchase under this new FCC policy (besides maybe Musk’s Starlink satellite Internet routers, which are produced in Texas). The FCC says router makers can apply for a special “conditional approval” from the Department of War or Department of Homeland Security, and that the new policy does not affect any previously-purchased consumer-grade routers.

  •  

Weekly Update 498

Weekly Update 498

This week, more time than I'd have liked to spend went on talking about the trials of chasing invoices. This is off the back of a customer (who, for now, will remain unnamed), who had invoices stacking back more than 6 months overdue and despite payment terms of 30 days, paid on an average of 80 days. But as I say in this week's video, more than anything, it was the gall of the CEO to take issue with my frustrated tone rather than with their complete lack of respect for basic business etiquette and paying one's suppliers. And so, Copilot and I spent the weekend fixing up a nice little Xero integration to ensure this never happens again. If you arrive at this post sometime in the future after finding your HIBP enterprise service no longer functioning weeks after an unpaid invoice was due, at least you'll know it's not personal... and pay your damn bills!

Weekly Update 498
Weekly Update 498
Weekly Update 498
Weekly Update 498
  •  

Germany Doxes “UNKN,” Head of RU Ransomware Gangs REvil, GandCrab

An elusive hacker who went by the handle “UNKN” and ran the early Russian ransomware groups GandCrab and REvil now has a name and a face. Authorities in Germany say 31-year-old Russian Daniil Maksimovich Shchukin headed both cybercrime gangs and helped carry out at least 130 acts of computer sabotage and extortion against victims across the country between 2019 and 2021.

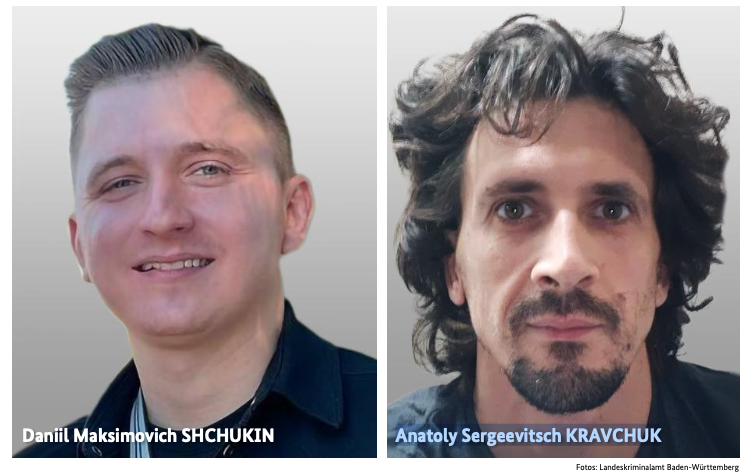
Shchukin was named as UNKN (a.k.a. UNKNOWN) in an advisory published by the German Federal Criminal Police (the “Bundeskriminalamt” or BKA for short). The BKA said Shchukin and another Russian — 43-year-old Anatoly Sergeevitsch Kravchuk — extorted nearly $2 million euros across two dozen cyberattacks that caused more than 35 million euros in total economic damage.

Daniil Maksimovich SHCHUKIN, a.k.a. UNKN, and Anatoly Sergeevitsch Karvchuk, alleged leaders of the GandCrab and REvil ransomware groups.

Germany’s BKA said Shchukin acted as the head of one of the largest worldwide operating ransomware groups GandCrab and REvil, which pioneered the practice of double extortion — charging victims once for a key needed to unlock hacked systems, and a separate payment in exchange for a promise not to publish stolen data.

Shchukin’s name appeared in a Feb. 2023 filing (PDF) from the U.S. Justice Department seeking the seizure of various cryptocurrency accounts associated with proceeds from the REvil ransomware gang’s activities. The government said the digital wallet tied to Shchukin contained more than $317,000 in ill-gotten cryptocurrency.

The GandCrab ransomware affiliate program first surfaced in January 2018, and paid enterprising hackers huge shares of the profits just for hacking into user accounts at major corporations. The GandCrab team would then try to expand that access, often siphoning vast amounts of sensitive and internal documents in the process. The malware’s curators shipped five major revisions to the GandCrab code, each corresponding with sneaky new features and bug fixes aimed at thwarting the efforts of computer security firms to stymie the spread of the malware.

On May 31, 2019, the GandCrab team announced the group was shutting down after extorting more than $2 billion from victims. “We are a living proof that you can do evil and get off scot-free,” GandCrab’s farewell address famously quipped. “We have proved that one can make a lifetime of money in one year. We have proved that you can become number one by general admission, not in your own conceit.”

The REvil ransomware affiliate program materialized around the same as GandCrab’s demise, fronted by a user named UNKNOWN who announced on a Russian cybercrime forum that he’d deposited $1 million in the forum’s escrow to show he meant business. By this time, many cybersecurity experts had concluded REvil was little more than a reorganization of GandCrab.

UNKNOWN also gave an interview to Dmitry Smilyanets, a former malicious hacker hired by Recorded Future, wherein UNKNOWN described a rags-to-riches tale unencumbered by ethics and morals.

“As a child, I scrounged through the trash heaps and smoked cigarette butts,” UNKNOWN told Recorded Future. “I walked 10 km one way to the school. I wore the same clothes for six months. In my youth, in a communal apartment, I didn’t eat for two or even three days. Now I am a millionaire.”

As described in The Ransomware Hunting Team by Renee Dudley and Daniel Golden, UNKNOWN and REvil reinvested significant earnings into improving their success and mirroring practices of legitimate businesses. The authors wrote:

“Just as a real-world manufacturer might hire other companies to handle logistics or web design, ransomware developers increasingly outsourced tasks beyond their purview, focusing instead on improving the quality of their ransomware. The higher quality ransomware—which, in many cases, the Hunting Team could not break—resulted in more and higher pay-outs from victims. The monumental payments enabled gangs to reinvest in their enterprises. They hired more specialists, and their success accelerated.”

“Criminals raced to join the booming ransomware economy. Underworld ancillary service providers sprouted or pivoted from other criminal work to meet developers’ demand for customized support. Partnering with gangs like GandCrab, ‘cryptor’ providers ensured ransomware could not be detected by standard anti-malware scanners. ‘Initial access brokerages’ specialized in stealing credentials and finding vulnerabilities in target networks, selling that access to ransomware operators and affiliates. Bitcoin “tumblers” offered discounts to gangs that used them as a preferred vendor for laundering ransom payments. Some contractors were open to working with any gang, while others entered exclusive partnerships.”

REvil would evolve into a feared “big-game-hunting” machine capable of extracting hefty extortion payments from victims, largely going after organizations with more than $100 million in annual revenues and fat new cyber insurance policies that were known to pay out.

Over the July 4, 2021 weekend in the United States, REvil hacked into and extorted Kaseya, a company that handled IT operations for more than 1,500 businesses, nonprofits and government agencies. The FBI would later announce they’d infiltrated the ransomware group’s servers prior to the Kaseya hack but couldn’t tip their hand at the time. REvil never recovered from that core compromise, or from the FBI’s release of a free decryption key for REvil victims who couldn’t or didn’t pay.

Shchukin is from Krasnodar, Russia and is thought to reside there, the BKA said.

“Based on the investigations so far, it is assumed that the wanted person is abroad, presumably in Russia,” the BKA advised. “Travel behaviour cannot be ruled out.”

There is little that connects Shchukin to UNKNOWN’s various accounts on the Russian crime forums. But a review of the Russian crime forums indexed by the cyber intelligence firm Intel 471 shows there is plenty connecting Shchukin to a hacker identity called “Ger0in” who operated large botnets and sold “installs” — allowing other cybercriminals to rapidly deploy malware of their choice to thousands of PCs in one go. However, Ger0in was only active between 2010 and 2011, well before UNKNOWN’s appearance as the REvil front man.

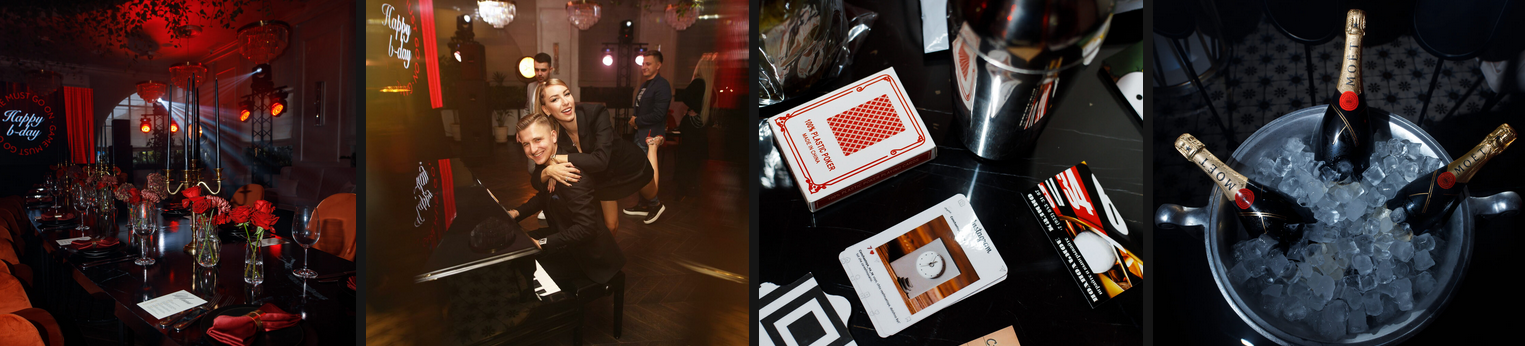
A review of the mugshots released by the BKA at the image comparison site Pimeyes found a match on this birthday celebration from 2023, which features a young man named Daniel wearing the same fancy watch as in the BKA photos.

Images from Daniil Shchukin’s birthday party celebration in Krasnodar in 2023.

Update, April 6, 12:06 p.m. ET: A reader forwarded this English-dubbed audio recording from a ccc.de (37C3) conference talk in Germany from 2023 that previously outed Shchukin as the REvil leader (Shchuckin is mentioned at around 24:25).

  •  

Oklahoma Tax Breach and FBI Impersonation Scam: This Week in Scams

Suspects wanted by the FBI

A tax system breach in Oklahoma is putting highly sensitive personal information at risk. And unfortunately, this is exactly the kind of situation scammers love to exploit. 

Hackers reportedly accessed W-2 and 1099 files through Oklahoma’s online tax portal, according to state officials, exposing the kind of information that can open the door to tax fraud, identity theft, and highly targeted phishing attempts. 

Before the follow-up scams start rolling in, this is the kind of moment where layered protection matters. McAfee+ Advanced includes identity monitoring and data cleansup that can help alert you if your personal information starts circulating where it shouldn’t, and Scam Detector can flag suspicious messages if scammers try to use this breach as a hook. 

What Happened in Oklahoma 

According to a statement by the Oklahoma Tax Commission and reported by KOCO News 5, a local ABC affiliate, suspicious activity inside the state’s Oklahoma Taxpayer Access Point system was identified in December 2025. The agency says impacted individuals have been notified directly by mail, and complimentary credit monitoring and fraud assistance are being offered. 

When W-2s, 1099s, Social Security numbers, and tax-related records are exposed, scammers can use that information to: 

  • File fraudulent tax returns  
  • Try to open new accounts  
  • Build phishing emails or texts that feel unusually real  

Either way, the goal is the same: use real information to make the next scam more believable. 

Red Flags of a Scam After a Breach Like This 

The breach itself is real. But what often follows is a second wave of scams pretending to help. 

Watch For: 

  • Emails or texts about your “tax account” that create urgency  
  • Messages asking you to verify personal information  
  • Fake alerts about refunds, filings, or suspicious activity  
  • Links telling you to log in and “secure” your account  

That’s where people can get hit twice: once by the breach, and again by the scam that follows it. 

What To Do If You’re Impacted 

First, don’t panic. Then: 

  • Take advantage of any free credit monitoring or fraud assistance being offered  
  • Monitor your bank accounts, tax records, and credit reports closely  
  • Consider placing a fraud alert or credit freeze if needed  
  • Be extra careful with any message referencing taxes, refunds, or account access 
  • Go directly to official sites instead of clicking links in emails or texts  

And that, my friends, is scam number one in this week’s This Week in Scams. 

Let’s get into what else is on our radar. 

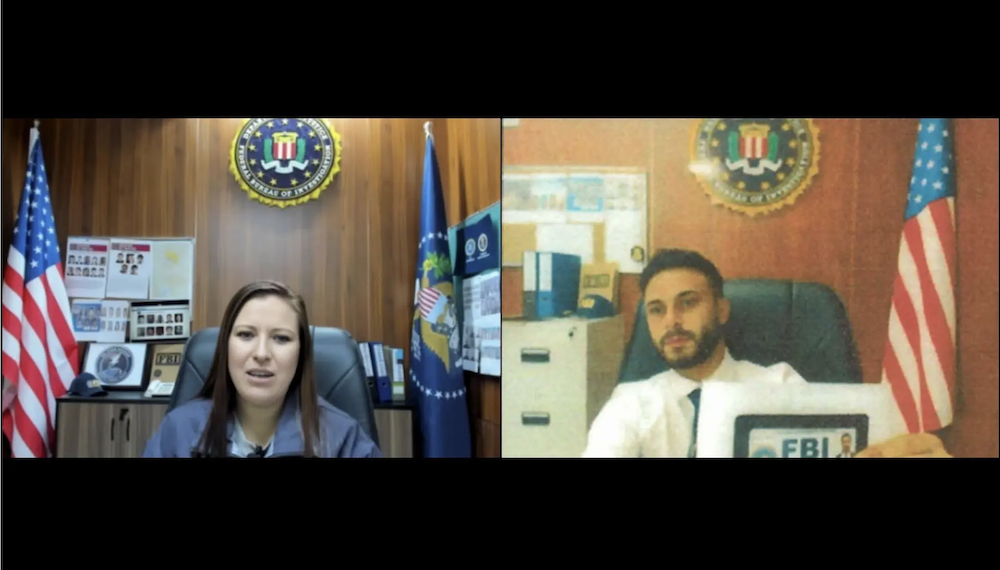
The FBI Impersonation Scam Showing Up Across the U.S. 

Scammers pretending to be federal agents are making the rounds across the country, and this one is built to make people panic fast. 

Field offices, including Chicago and Houston, are warning the public about fraudsters posing as FBI agents in calls, texts, and emails. In some cases, the scammers claim you’re connected to an investigation. In others, they say you’re a victim of fraud and need to act immediately to protect yourself. 

Sometimes they do not stop there. They may also pretend to be bank employees working alongside the FBI, all to make the story feel more convincing and get access to your money or personal information. 

Suspects wanted by the FBI
The FBI has shared images of these suspects pretending to be agents. If you are contacted by these officials, report it to the FBI.

Why This Scam Works

This scam plays on the same pressure tactics we’ve seen over and over again: authority, urgency, and confusion. 

If someone claims to be a federal agent, many people freeze up and assume they need to cooperate immediately. That’s exactly what scammers are counting on. 

The FBI has been clear about this: federal law enforcement will not ask you for money or sensitive personal information over the phone, by text, or by email. 

The Red Flags in This Message

  • Unsolicited outreach from someone claiming to be federal law enforcement  
  • Pressure to act immediately  
  • Requests for money, gift cards, prepaid cards, or personal information  
  • Instructions to keep the conversation secret  
  • Stories involving a bank “working with” the FBI  

If it feels dramatic, high-pressure, and just a little off, trust that instinct. 

What To Do if You Get One Of These Messages

  • Do not respond  
  • Do not send money or share personal information  
  • Contact the agency directly using publicly listed contact information  
  • Save the message for your records  
  • Report it to the FBI: 1-800-CALL-FBI (225-5324), or online at tips.fbi.gov.

This is also exactly the kind of message McAfee’s Scam Detector is built to flag before you get pulled in. 

How McAfee Helps You Stay Ahead of Scams and Breaches 

McAfee+ Advanced gives you multiple layers working together so you are not left figuring it out after the damage is done: 

  • Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
  • Personal Data Cleanup helps remove your information from data broker sites, making you harder to target in the first place
  • Scam Detector flags suspicious texts, emails, links, and even deepfake videos before you engage
  • Safe Browsing helps block risky sites if you do click
  • Device Security helps detect malicious apps or downloads
  • Secure VPN keeps your data private, especially on public Wi-Fi  

This kind of layered protection is critical in cases like ghost student scams, where the first sign of fraud often comes after financial damage has already happened. 

Safety tips to carry into next week 

  • Be extra cautious after any real breach makes headlines  
  • Do not trust unsolicited messages just because they reference real institutions  
  • Never send money to someone claiming to be law enforcement  
  • Go directly to official websites instead of clicking links  
  • Use tools that flag suspicious messages in real time so you do not have to guess 

The reality is, scams are getting better at looking official. 

You should not have to be an expert to spot them. That’s why McAfee is here to help. We’re Safer Together.

We’ll be back next week with more scams making headlines. 

The post Oklahoma Tax Breach and FBI Impersonation Scam: This Week in Scams appeared first on McAfee Blog.
  •  

Why Was My Tax Refund Intercepted? The “Ghost Student” Scam Explained

Rob J., 31, an internal auditor in California, thought he was doing everything right this tax season. He filed his return as usual, even early, and expected a state refund just short of $400. 

Instead, he got a letter saying the state had taken it. 

The notice from the California Franchise Tax Board said his refund had been intercepted to pay a debt owed to a local community college. 

There was just one problem: Rob had never attended that school. 

“How could the state be taking my tax refund to pay a debt to a community college I’ve never attended?” he told us at McAfee. “I immediately knew something was wrong.” 

“I started researching and came across the term ‘ghost student,’ and that’s when it clicked. Someone had used my identity to enroll in a college like they were me.” 

How McAfee+ Advanced Helps Protect You from Identity Theft  

Scams like this do not start with a suspicious text or email. They start with your data being exposed somewhere you cannot see. 

That is why protection has to go beyond one moment and cover the full lifecycle of identity theft. 

McAfee+ Advanced gives you multiple layers working together so you are not left figuring it out after the damage is done: 

  • Identity Monitoring alerts you if your personal info shows up where it should not, so you can act fast
  • Personal Data Cleanup helps remove your information from data broker sites, making you harder to target in the first place
  • Scam Detector flags suspicious texts, emails, links, and even deepfake videos before you engage
  • Safe Browsing helps block risky sites if you do click
  • Device Security helps detect malicious apps or downloads
  • Secure VPN keeps your data private, especially on public Wi-Fi  

This kind of layered protection is critical in cases like ghost student scams, where the first sign of fraud often comes after financial damage has already happened. 

What Is a Ghost Student Scam? 

A ghost student scam is a form of identity theft where someone uses your stolen personal information, often your Social Security number, to enroll in a college or university under your name. 

The scammer is not trying to attend school. They are trying to use your identity to access financial aid, create accounts, or generate funds tied to a real person. 

In many cases, the victim has no idea anything happened until the consequences show up later, such as a tax refund being taken, a debt appearing, or a loan being opened in their name. 

That is exactly what happened to Rob. 

“I started researching and came across the term ‘ghost student,’ and that’s when it clicked,” he said. “Someone had used my identity to enroll in a college like they were me.”  

How Ghost Student Scams Happen 

These scams typically follow a predictable pattern, even if the victim does not see it happening in real time: 

Stage  What happens  Why it matters 
Data exposure  Your personal information is leaked in a data breach or collected from data broker sites  Scammers get the core details they need to impersonate you 
Identity misuse  Your information is used to apply to colleges or financial aid programs  The scam is tied to your real identity, not a fake one 
Enrollment activity  Fake students may enroll just long enough to access funds or create accounts  This helps scammers avoid early detection 
Financial impact  Debts, balances, or aid obligations are created in your name  You become financially responsible on paper 
Discovery  You find out later through a notice, refund interception, or account alert  By this point, damage has already been done 

In Rob’s case, the starting point was a data breach the year before. His Social Security number had been exposed, but he had not frozen his credit. 

Someone used that information to enroll at Pasadena City College. When the balance went unpaid, the state redirected his tax refund to cover it. 

“Despite Being the Victim, I’m Trying to Prove My Identity” 

Once Rob realized what happened, he moved quickly. He froze his credit, set up identity monitoring, filed a police report, and began working with the college to prove he was not the student. 

He says the process has been slow and frustrating. 

“I’ve spent hours on the phone trying to fix this… I’m exhausted,” he said. “Despite being the victim I am the one dealing with the consequences and trying to prove my identity to the same institution that let a fake me register.”  

When he contacted campus police, he learned something else: “this has been happening to other people too.” 

Why Ghost Student Scams Are Increasing 

Ghost student scams are part of a broader shift in how identity theft works. 

Instead of quick-hit fraud like a stolen credit card, scammers are using real identities to create more complex, longer-term opportunities for financial gain. 

In higher education, that can include: 

  • Enrolling fake students using stolen identities  
  • Accessing financial aid  
  • Holding seats in classes long enough to collect funds  

This trend has already affected thousands of suspected cases across education systems and continues to grow as scammers scale their tactics  

What to Do If Your Identity Is Used in a Ghost Student Scam 

If something like this happens, speed matters: 

  • Freeze your credit with all three bureaus  
  • Check your FAFSA and student loan records  
  • Contact the school and dispute the enrollment  
  • File a police report  
  • Set up identity monitoring and alerts  
  • Remove your personal information from data broker sites  

These steps help contain the damage, but they are reactive. The goal is to catch exposure earlier. McAfee+ Advanced can help you with freezing your credit, ongoing identity monitoring, and data removal from the dark web. 

How Rob’s Story Ends: ‘I’m Waiting for the Other Shoe to Drop’ 

Rob has confirmed there are no federal loans in his name, but the situation is not fully resolved. 

“I still feel like I’m waiting for the other shoe to drop,” he said.  

That uncertainty is part of what makes identity theft so difficult. You are often reacting to something that started months or even years earlier. Rob said he currently has an outstanding police report and is in the process of getting his refund reclaimed.  

How to Stay Ahead of Identity Theft Like This 

Ghost student scams work because they operate quietly, using real data in systems most people are not actively watching. That is where ongoing protection matters. 

McAfee+ Advanced helps close those gaps by: 

  • Alerting you early when your personal data appears on the dark web or in risky environments  
  • Reducing your exposure by removing your data from broker sites that scammers rely on  
  • Blocking scam entry points across texts, emails, links, and deepfakes  
  • Protecting your devices and connections so attackers have fewer ways in  

Because the goal is not just to respond to identity theft, it’s to catch the signals early enough that someone cannot become a “student” in your name in the first place. 

The post Why Was My Tax Refund Intercepted? The “Ghost Student” Scam Explained appeared first on McAfee Blog.
  •  

McAfee’s “Keep It Real” Campaign Named Shorty Awards Finalist

We’re proud to share that McAfee’s “Keep It Real” campaign has been named a finalist in the 2026 Shorty Awards Social Good Campaign category. 

This category recognizes work that doesn’t just perform, it matters: campaigns that raise awareness, inspire action, and make a real-world impact. 

That’s exactly what “Keep It Real” set out to do. 

Because behind every scam statistic is a person who thought they were making the right call. And too often, what follows isn’t just financial loss. It’s embarrassment, silence, and stigma. 

We wanted to change that. 

The campaign launched alongside McAfee Scam Detector to address a growing reality: scams powered by AI are becoming harder to recognize and easier to fall for. 

“Keep It Real” paired real survivor stories with AI-driven protection to show how scams actually happen and how people can stop them in the moment. 

The goal was simple: 

  • Normalize the experience  
  • Remove shame around being scammed 
  • Help more people recognize scams faster  

Because when people feel safe talking about scams, they’re more likely to spot them and stop them. 

What Are the Shorty Awards? 

The Shorty Awards honor the best work in social media, digital campaigns, and online storytelling across brands, creators, and organizations. 

Now in their 18th year, the awards recognize campaigns that combine creativity, impact, and real-world relevance. Finalists are selected alongside leading global brands and judged on both industry evaluation and public voting. 

How McAfee’s Scam Detector Fits In 

McAfee’s Scam Detector is designed to help people identify scams across everyday digital moments. 

It uses AI to fight AI by flagging suspicious: 

  • Text messages and emails  
  • QR codes and links  
  • Social media messages  
  • AI-generated and deepfake content  

By combining automatic detection with clear guidance, Scam Detector helps people better understand what they’re seeing and decide what to trust. 

Real Stories Behind the Campaign 

A core part of “Keep It Real” was giving space to people who experienced scams to share what happened, in their own words. 

These stories helped show that scams can happen to anyone and played a key role in breaking the stigma around being targeted. 


This recognition reflects the work across McAfee teams who built and brought this campaign to life, including product, engineering, research, creative, and communications. 

It also reflects the individuals who chose to share their real scam stories to help others recognize scams, stay safer, and end the shame and stigma around being scammed. 

Support the Campaign 

The Shorty Awards include a public voting component. 

If you’d like to support the campaign, you can vote here:
https://shortyawards.com/18th/keep-it-real-mcafees-ai-scam-media-relations-campaign 

Voting is open through April 8, and you can vote once per day. 

Examples of real messages sent in response to our campaign.

The post McAfee’s “Keep It Real” Campaign Named Shorty Awards Finalist appeared first on McAfee Blog.
  •  
❌