DHS agents not only tracked and intimidated people observing ICE activity in Maine, but stored information about them in a Palantir-built database, newly unsealed court filings say.
If a website asks you to open Terminal, PowerShell, Command Prompt, or the Windows Run box and paste something in, stop.
That simple rule can protect you from a type of attack McAfee has been tracking for years. Known as ClickFix, the scam turns an ordinary-looking online instruction into a way for criminals to install malware on your device. The lure might look like a CAPTCHA, a software fix, a download, or a quick tutorial. The trick is getting you to run the attack yourself.
ClickFix is back in the headlines this week after attackers reportedly compromised HBO Max’s verified Reddit advertising account and used it to distribute malicious ads. But while the brands, websites, and platforms keep changing, the underlying trick is one McAfee researchers have been following since at least 2024.
What is a ClickFix Attack?
A ClickFix attack is a social engineering scam that convinces someone to copy, paste, or run a malicious command on their own computer.
This week’s example shows why the tactic can be so convincing. According to TechCrunch, attackers compromised an HBO Max account authorized to run ads on Reddit. The account was then used to publish malicious advertisements that could direct people to fake sites, including pages made to look like they were associated with HBO Max.
Researchers investigating the campaign reported finding 108 malicious ads posted over roughly 48 hours. Some promoted what appeared to be a Mac version of HBO Max, while others used software and AI-related lures.
Instead of providing a normal download, the sites instructed visitors to open tools such as Terminal on a Mac or PowerShell or the Run dialog on Windows, paste in a command, and execute it. That last step is the important one.
The website is not really helping you fix or install something. It is convincing you to give your computer malicious instructions.
Depending on the campaign and device, those instructions can lead to information-stealing malware designed to collect things such as saved passwords, browser information, account data, or cryptocurrency wallet information.
Reddit told TechCrunch that it learned an HBO Max account authorized to run advertisements had been compromised and used for malicious links. The company said it locked the account and removed the ads. The number of people who clicked the ads or were ultimately compromised remains unclear.
Clickfix isn’t New, and Mcafee Has Been Tracking It For Years
What makes this week’s story notable isn’t that ClickFix suddenly appeared. It’s how far the tactic has traveled.
McAfee Labs documented ClickFix attacks in July 2024 after researchers discovered compromised websites displaying fake error messages that instructed people to paste scripts into PowerShell. Researchers observed the technique being used to deliver malware including DarkGate and Lumma Stealer.
Victims encountered fake “Verify you are a human” or “I’m not a robot” pages. Clicking the button could copy a malicious command to the clipboard. The page would then walk the person through opening the Windows Run box and pasting it in. McAfee researchers observed those fake CAPTCHA attacks connected to phishing emails and searches for cracked games.
By 2025, the same basic idea was appearing in yet another familiar place: social media tutorials. McAfee reported on ClickFix-style scams circulating through TikTok videos that promised free software upgrades or premium versions of popular apps. Instead of solving a problem, the instructions could lead people to install information-stealing malware.
Now the lure has changed again. This time, attackers allegedly used advertising from a compromised, verified corporate account.
That evolution matters because ClickFix isn’t one particular fake website or pop-up you can memorize. It’s a reusable scam technique.
Why ClickFix scams can be so convincing
Most online scams ask you to click something. ClickFix adds another layer by asking you to do something.
That action may feel technical enough to be legitimate. A page tells you there’s an error. It gives you several steps to fix it. Maybe you’re asked to press a few keys, open a utility you’ve seen on your computer before, paste something, and hit Enter.
Following instructions can feel safer than downloading an unfamiliar file. But in a ClickFix attack, following the instructions is effectively the download.
Attackers also keep placing these instructions inside familiar online experiences. McAfee researchers have seen fake error messages and CAPTCHA checks. Other campaigns have appeared in social media tutorials, software downloads, phishing messages, and now online advertising.
Even a familiar brand or verified account shouldn’t override an unusual request from a website.
Key Takeaways
ClickFix is a social engineering technique, not one specific scam. The lure can change while the basic attack stays the same.
McAfee researchers have tracked ClickFix campaigns since 2024, including fake error messages and CAPTCHA pages designed to deliver malware.
Mac users aren’t automatically outside the target zone. This week’s campaign reportedly included separate techniques targeting both macOS and Windows.
The biggest warning sign is an unusual instruction. A website should not need you to paste an unexplained command into Terminal, PowerShell, Command Prompt, or Run to prove you’re human or download ordinary consumer software.
How McAfee Helps
You deserve multiple layers of cybersecurity protection to prevent and stop threats like ClickFix at every potential point of malware entry. That’s what McAfee’s built to do.
Web Protection can help prevent access to known malicious websites, including sites used as part of malware campaigns. That matters when an otherwise convincing ad or message sends you somewhere dangerous.
Device Security adds another layer by scanning for and helping block malware that attackers attempt to install. McAfee Labs has previously documented McAfee protections blocking stages of ClickFix infection chains, including malicious URLs and suspicious behavior.
And because information stealers often target passwords and account information, Identity Monitoring can help alert you when monitored personal information is found in a breach so you can respond sooner.
Technology can help, but ClickFix also has a human checkpoint built into the attack. If a webpage suddenly asks you to become your own system administrator and run a command you don’t understand, don’t.
Other Scam and Security News This Week
Spain’s privacy regulator receives report of an alleged AI-powered breach. Spain’s data protection agency said it was notified of an incident in which an AI agent was allegedly used to find vulnerabilities, access systems, probe applications, and ultimately access or modify data. The regulator has not yet investigated and verified the reported incident, an important distinction as security researchers continue examining how AI agents could be misused in cyberattacks. Source: BleepingComputer
Revolut says its core systems weren’t hacked in customer data incident. Reuters reported that sensitive information involving about 680 customers was disclosed after fraudulent requests were sent from a legitimate government agency email domain, according to a source familiar with the matter. Revolut said it had received no direct demand from the group claiming responsibility, while the group reportedly threatened to sell customer records unless it received a $3 million ransom. Source: Reuters
More details emerge about the malicious HBO Max Reddit ads. Additional reporting on the ClickFix campaign said the compromised account was used to run 108 malicious ads over about 48 hours, with lures ranging from HBO Max downloads to AI and software tools. The findings reinforce the main lesson from this week’s story: a verified account or recognizable brand doesn’t make unusual download instructions safe. Source: Malwarebytes
This Week’s Safety Tips
Some practical safety tips in light of this week’s news:
✓ Don’t paste commands from websites into system tools. Treat the request itself as a warning sign.
✓ Skip software downloads promoted through ads. Navigate to the company’s official website or trusted app store yourself.
✓ Use multifactor authentication on important accounts. It can provide another barrier if a password is stolen.
✓ Keep security protection and your devices updated. Current protection gives you more opportunities to catch malicious sites and malware before they can do damage.
ClickFix may keep changing its disguise, but you don’t need to learn every version. Remember the underlying trick: a website that asks you to copy, paste, and run unfamiliar commands is asking for far more trust than you should give it.
And we’ll be back next week with more cybersecurity news and scam alerts.
Plus: The US disrupts the internet’s biggest black market, a Conti ransomware hacker gets prison time, Meta fails to stop AI-generated videos of child abuse.
Your driver’s license can be replaced. The information printed on it is much harder to take back.
That’s the concern after identity verification company IDScan confirmed a data breach involving driver’s license and other government ID information. Reporting has connected the incident to a database containing more than 150 million driver’s license records, raising an obvious question for consumers: What should you do if your information may be exposed?
That’s our lead story in This Week in Scams. We’ll explain what’s known about the IDScan breach, why stolen ID information can be useful to scammers, and the steps you can take now.
Plus, we’re looking at AI agents that reportedly found ways around restrictions, AI-generated political ads that make online video harder to trust, and how AI is adding a new layer to an old jury duty scam.
What Happened in the IDScan Data Breach?
IDScan provides identity verification technology used by businesses to scan and verify identification documents.
On September 4, the company disclosed that it had learned of possible unauthorized access to data stored in its cloud. IDScan said potentially affected information may include full names, driver’s license numbers, and numbers from other government-issued IDs. The company says its investigation is ongoing and that it is cooperating with federal law enforcement.
The scale requires some careful distinction.
According to TechCrunch, cybersecurity journalist Brian Krebs had been alerted to a dark web website that allowed users to search driver’s license information belonging to more than 150 million people in the U.S. and Canada, reportedly including photographs. IDScan itself has not said how many people were affected by the breach, though the company has said it holds more than 150 million driver’s license records.
In other words, there is evidence pointing to an extremely large collection of exposed identity information, but an official affected-person count has not yet been established.
Why Stolen Driver’s License Information Matters
A driver’s license number isn’t a password. You can’t simply change it after every breach.
And unlike a credit card, which can generally be canceled and replaced when it is compromised, identity information can remain useful to criminals for years.
That can make this type of data valuable for identity theft and impersonation.
Identity theft happens when someone uses another person’s personal information to pretend to be them, often to open accounts, attempt financial fraud, or make other fraudulent transactions.
There is also a second risk: more convincing scams.
Someone who knows your full name, address, date of birth, driver’s license information, or other personal details may have an easier time convincing you that they represent a bank, government agency, insurance company, or another organization you trust.
That leads to an important rule after any major breach: Someone knowing private information about you does not prove they are legitimate.
Key Takeaways
→ IDScan has confirmed unauthorized access that may involve names, driver’s license numbers, and other government-issued identification numbers.
→ IDScan has not announced how many individuals were affected, so consumers should be cautious about treating 150 million as a confirmed victim count.
→ Stolen identity information can potentially be used for identity theft as well as more personalized impersonation scams.
→ Be suspicious of anyone contacting you unexpectedly about the breach and asking for additional personal information, passwords, verification codes, or money.
How McAfee Protects Against Breaches
Before a breach
Personal Data Cleanup reduces your digital footprint by removing your personal information from many data broker sites, making it harder for scammers to find and target you.
Online Account Cleanup scans for accounts you no longer use and helps you delete them, along with your personal info.
During a breach
Identity Monitoring watches for your personal information, including email addresses, driver’s license numbers, passport numbers, bank accounts, credit cards, Social Security numbers, phone numbers, and more, across the dark web and known data leaks.
Plus, we alert users on average up to 10 months earlier than similar services, so you can act fast when your personal information appears where it shouldn’t.
After a breach
Scam Detector identifies suspicious texts, emails, and links that often follow major breaches, while web protection blocks malicious websites designed to steal even more of your information.
Other Scam and Security News This Week
OpenAI Agents Reportedly Found Their Own Ways to Communicate Online
Researchers found that OpenAI agents used more than 10 previously undisclosed websites to communicate during testing despite restrictions intended to prevent them from posting online, according to Reuters; importantly, Reuters characterized much of the behavior as closer to spam than hacking. The consumer takeaway is less about an immediate scam and more about AI agents — systems designed to independently carry out multi-step tasks — and why giving increasingly capable AI systems access to outside tools and websites requires strong safeguards and oversight. Source: Reuters
AI Campaign Ads Make “Seeing Is Believing” Even Less Reliable
AI-generated political ads are increasingly appearing during the 2026 election cycle, including fabricated images, video, and audio involving real candidates, Axios reports. Regardless of the political message involved, the consumer lesson is straightforward: a realistic-looking video is no longer proof that someone actually said or did what appears on screen, so check questionable political content against reliable reporting and original sources before sharing it. Source: Axios
AI Is Giving the Old Jury Duty Scam a More Convincing Voice
Courts around the country are warning about scammers claiming victims missed jury duty and face arrest unless they respond or pay, while recent reporting has highlighted how AI-generated voices can make phone scams more convincing. The underlying scam hasn’t changed: criminals create fear and urgency, impersonate authority, and demand money — and federal courts stress that they will not demand payment by phone, text, email, payment app, gift card, or cryptocurrency to resolve missed jury service. Sources: WBUR/Here & Now; U.S. Courts
This Week’s Safety Tips
✓ Consider a credit freeze after sensitive identity data is exposed. A freeze can make it harder for someone to open new credit accounts in your name; IDScan itself recommends considering fraud alerts or credit freezes following this incident.
✓ Never treat personal information as proof of identity. A caller knowing your name, address, driver’s license information, or other details doesn’t mean they represent the organization they claim to.
✓ Verify surprising videos before sharing them. Search for the original speech, interview, campaign account, or credible reporting rather than relying on the clip in your feed.
✓ Hang up on jury-duty payment demands. Courts do not demand immediate payment over the phone to prevent your arrest. Find the court’s official contact information yourself and verify the claim independently.
And we’ll be back next week with more cybersecurity news and scam alerts.
Plus: Tens of millions of US and Canadian drivers’ licenses go up for sale on the dark web, the US military finally tries to tackle the risk online ad data poses to troops, and more.
A data breach doesn’t have to expose your password or credit card number to create problems. Sometimes, scammers just need enough information to make you believe they know you.
That’s the concern after data reportedly stolen from Carhartt was published online. Here’s what happened, why it matters, and what consumers should watch for next.
What Happened in the Carhartt Data Breach?
The cybercriminal group ShinyHunters published data it claims was stolen from Carhartt after an alleged $3.3 million extortion demand was rejected, according to TechRadar. Security researcher Troy Hunt analyzed the leaked information and determined that the compromised data was associated with roughly 12.9 million accounts, although the dataset also reportedly contained millions of synthetic records that did not correspond to real people.
For affected consumers, the important part is what was reportedly exposed: names, email addresses, phone numbers, and postal addresses.
This is also a useful example of how cyber extortion has evolved.
Traditional ransomware typically involves criminals getting inside an organization, encrypting its files so they can’t be accessed, and then demanding payment to restore them.
In this case, the reported strategy was different. ShinyHunters has increasingly focused on data exfiltration — security jargon for stealing or copying data out of a system — and then using the threat of publishing that information as leverage.
In plain English: Criminals don’t necessarily need to lock up a company’s computers anymore. Stealing its data can be valuable enough.
How Scammers Might Use This Information
The immediate question after any breach is usually, “Was my financial information stolen?” That’s important, but it isn’t the only risk.
A combination of your name, email, phone number, and home address can help scammers create a message that sounds much more believable than generic spam.
Instead of: “There’s a problem with your account. Click here.” you could receive something that appears to know your name, where you live, or which company you’ve done business with.
That context can lower your guard.
And scammers don’t necessarily have to pretend to be Carhartt. Stolen contact information can potentially be combined with information from other breaches, data brokers, or public sources to build a more complete picture of someone.
That’s why leaked personal information can remain useful to criminals long after the original breach disappears from the headlines.
Key Takeaways
Personal information can be valuable to scammers even when passwords or payment information aren’t exposed.
Names, emails, addresses, and phone numbers can make phishing attempts more personalized.
Be particularly cautious of unexpected messages claiming there is a problem with an order, refund, account, or payment.
A company knowing personal details about you is not proof that the person contacting you actually represents that company.
How McAfee Protects Against Breaches
Before a breach
Personal Data Cleanup reduces your digital footprint by removing your personal information from many data broker sites, making it harder for scammers to find and target you.
Online Account Cleanup scans for accounts you no longer use and helps you delete them, along with your personal info.
During a breach
Identity Monitoring watches for your personal information, including email addresses, driver’s license numbers, passport numbers, bank accounts, credit cards, Social Security numbers, phone numbers, and more, across the dark web and known data leaks.
Plus, we alert users on average up to 10 months earlier than similar services, so you can act fast when your personal information appears where it shouldn’t.
After a breach
Scam Detector identifies suspicious texts, emails, and links that often follow major breaches, while web protection blocks malicious websites designed to steal even
Other Scam and Security News This Week
A Lenovo Login Flaw Exposed About 5,000 Dropbox Accounts
Dropbox says approximately 5,000 accounts were accessed after attackers exploited a flaw involving Lenovo ID authentication; fewer than a third reportedly had files viewed or downloaded. Dropbox has expired sessions authenticated through Lenovo IDs and changed the login process, while the incident is another good reason to enable two-factor authentication on cloud accounts. Sources: BleepingComputer
Amazon Adds a New Way to Check Suspicious Messages
Amazon has added a feature to Alexa for Shopping that lets U.S. customers ask whether an email, text, phone call, or other message actually came from Amazon; the company says roughly 360,000 customers contact customer service each year with that question. It’s a useful reminder of one of the best scam-fighting habits: instead of trusting the message in front of you, verify it through a separate, official channel. Sources: TechCrunch
Fake Late-Night TV Clips Show How Easily AI Can Borrow Someone’s Credibility
NPR reports that AI-generated videos impersonating late-night hosts including Jimmy Kimmel and Jon Stewart have accumulated significant audiences online, sometimes without obvious AI labels. The bigger consumer lesson goes beyond politics or entertainment: seeing a familiar face and hearing a familiar voice is no longer enough to prove that a video — or the product, investment, or claim it promotes — is authentic. Source: NPR
This Week’s Safety Tips
✓ Treat unexpected personalization as information, not proof. A caller knowing your name, address, or other details doesn’t mean they’re legitimate.
✓ Turn on two-factor authentication. This can provide another barrier when someone tries to access an account without permission.
✓ Verify messages outside the message itself. Open the official app, type the website yourself, or contact the company using information you independently know is legitimate.
✓ Slow down when something feels urgent. Whether it’s a breach alert, delivery problem, suspicious login, or celebrity video, scammers benefit when you react before you verify.
And we’ll be back next week with more cybersecurity news and scam alerts.
Free airport Wi-Fi can be useful when you’re waiting for a flight. But this week’s biggest security story is a reminder that there are two different ways your information can be exposed when you connect.
One risk happens while your information is traveling across a public network. Another happens after a company collects and stores information about you.
A cyberattack affecting three major UK airports illustrates the difference, and why travelers need protection for both.
What happened in the Manchester Airports Group cyberattack?
Manchester Airports Group, or MAG, confirmed that an unauthorized third party obtained customer information connected with Manchester Airport, London Stansted Airport, and East Midlands Airport.
According to reports, the affected information came from car park, airport lounge, Fast Track bookings, and airport Wi-Fi registrations. MAG says the stolen data includes email addresses, phone numbers, vehicle registration numbers, and postcodes. The company says the affected system did not contain customers’ payment or banking details.
The Telegraph reported that approximately 8.7 million passengers were affected and that more than 90% of the stolen records were email addresses, largely because travelers provide an email address when registering for free airport Wi-Fi. The attackers reportedly demanded a ransom, which MAG declined to pay.
MAG says airport operations and passenger safety were not affected and that it has contained access to the compromised systems.
For travelers, however, the breach creates another concern: what criminals might do with the stolen information next.
Why stolen airport data can lead to convincing scams
An email address alone might not seem particularly sensitive. But combined with a phone number, postcode, vehicle registration, or knowledge that someone has interacted with a particular airport, it becomes more useful to a scammer.
That information can help criminals make phishing emails and texts feel believable.
A message might claim there is a problem with your airport parking reservation, ask you to confirm a Fast Track booking, or say you need to pay an outstanding airport charge. Someone who recently used the airport may be much more inclined to click.
That is one reason breach victims should be especially cautious about unexpected messages that appear connected to the organization involved.
Does a VPN protect you from an airport Wi-Fi data breach?
Not from this kind of breach.
A VPN, or virtual private network, encrypts the internet traffic traveling between your device and the VPN service. Think of it as putting your online activity inside a protected tunnel while it crosses a public network.
That matters at airports, hotels, cafés, and other places where many people share the same Wi-Fi. McAfee Secure VPN can encrypt your connection and can be configured to turn on automatically when you join an unsecured network.
But that is different from what happened here.
If you voluntarily give an airport your email address to register for Wi-Fi, that email address may then be stored in the airport operator’s systems. A VPN cannot prevent a later breach of that company’s database.
In short: A VPN helps protect information in transit. It does not control what happens to information you give directly to a company.
Both risks matter.
Before, During, and After a Data Breach
Before a breach: Share only the information a service genuinely requires. Use strong, unique passwords for online accounts, and use a VPN when connecting to public Wi-Fi.
During a breach: Look for information directly from the affected company rather than relying on messages arriving by email or text. Criminals often take advantage of security incidents by sending fake “account protection” or “verify your information” messages.
After a breach: Watch for unusual emails, calls, texts, and account activity. Be particularly suspicious when someone creates urgency or asks for passwords, verification codes, payment information, or money.
MAG specifically warns that it will not unexpectedly contact customers asking for payment card information, banking details, or passwords.
At a Glance
The breach affected customer information from bookings and airport Wi-Fi registrations.
8.7 million passengers were affected
MAG says banking and payment details were not stored in the affected system.
Stolen contact information can still make phishing and impersonation scams more convincing.
A VPN protects your connection on public Wi-Fi, but it cannot prevent a company from later suffering a database breach.
Be particularly cautious about unexpected airport-related emails and texts following the incident.
How McAfee Helps
Secure VPN helps address the other major risk associated with airport Wi-Fi: someone attempting to monitor your traffic while you use an unsecured network. McAfee Secure VPN encrypts your connection and can automatically activate on unsecured Wi-Fi, helping keep browsing activity and information transmitted from your device private.
Identity Monitoring keeps watch for your personal information associated with breaches, giving you an opportunity to act when exposed information is detected.
And because stolen email addresses and phone numbers can fuel follow-up phishing attempts,Scam Detectorcan identify suspicious texts, emails, and other QR codes before you act on them.
The broader lesson is layered protection: protect your connection while you’re online, then keep watching for misuse of information that companies already hold.
Other Scam and Security News This Week
Hackers claim breach of major data center provider. The ShinyHunters group claims it stole extensive corporate and employee information from U.S. data center company CyrusOne and demanded $13 million.
CyrusOne had not publicly confirmed the hackers’ claims when TechRadar reported the story, so the alleged scale of the breach remains unverified. Source: TechRadar
Man accused of posing as a 49ers player in $1.3 million romance scam. Federal prosecutors allege that two men defrauded at least 26 women after one portrayed himself online as a wealthy San Francisco 49ers player and the other posed as his financial adviser.
Investigators say fake banking apps and fabricated investment balances helped make the scheme appear legitimate; both defendants are presumed innocent unless proven guilty. Source: U.S. Department of Justice
Fake sports streams target fans looking for the game. The Better Business Bureau warns that scammers post supposed free streaming links on social media, sometimes tagging real schools or teams, then direct fans to sites designed to collect payment or personal information instead of showing a game.
Go to the team, school, league, or known streaming provider directly rather than trusting a link in a social post — and remember that HTTPS alone does not prove a website is legitimate. Source: Better Business Bureau
This Week’s Safety Tips
“Once you give your information to a company, you can’t completely control what happens to it,” says McAfee’s Tyler McGee. “But you can limit what you share and take steps to protect yourself if your information is exposed.”
“Only provide what’s needed, use unique passwords and turn on multi-factor authentication where you can. Tools like McAfee’s identity monitoring can also alert you if your information shows up in a known breach. And be extra cautious after a breach,” he says. “Scammers can use exposed information to make messages about a booking, refund or account look much more convincing. If you get one, go directly to the company’s website or app rather than clicking the link.”
✓ Use a VPN on public Wi-Fi. Encrypt your connection before checking email, shopping, banking, or signing into important accounts.
✓ Treat breach-related messages cautiously. Navigate to the company’s official website yourself rather than clicking a link in an unexpected email or text.
✓ Use unique passwords. A password stolen from one service should never unlock another account.
✓ Verify before sending money. Whether someone claims to be an athlete, investment adviser, streaming provider, or familiar company, independently confirm who you are dealing with.
And we’ll be back next week with more cybersecurity news and scam alerts.
Fraudsters are exploiting enterprise chat apps like Teams and Webex to trick Chinese victims into transferring large sums of money, fueling a wave of complaints.
Illinois prosecutors shared defendants’ personal data with federal immigration agents without criminal warrants, public disclosure, or legislative oversight.
A data breach doesn’t have to hit the company you shopped with directly to put your information at risk.
That’s the lesson from this week’s Pokémon Center breach. Customers in the United Kingdom and Germany are being notified that personal and order information was exposed after attackers compromised CEVA Logistics, the third-party company used to fulfill and ship Pokémon Center orders.
The good news: Pokémon Center says CEVA did not have access to customers’ payment-card information.
The bigger concern is what criminals could potentially do with the information that was exposed, particularly when it can make a phishing message look unusually convincing.
What Happened in the Pokémon Center Data Breach?
According to breach notifications reviewed by BleepingComputer, attackers may have obtained Pokémon Center customers’ full names, mailing addresses, phone numbers, email addresses, and information about the products they ordered. The affected customers were in the UK and Germany.
The intrusion occurred at CEVA Logistics rather than Pokémon Center itself. Reporting indicates attackers accessed CEVA systems between late July and August 1, disrupting operations at eight European warehouses and affecting multiple retailers. Valve previously notified European Steam hardware customers that their information had also been exposed through the CEVA incident.
Why Does Shipping Data Matter to Scammers?
A name and email address may not seem as sensitive as a credit-card number. But when criminals also know your address, phone number, and what you recently bought, they have something valuable: context.
Context helps scammers make phishing messages believable.
Phishing is when a criminal pretends to be a trusted company or person to persuade you to click a malicious link, hand over a password, share personal information, or send money.
After a breach like this, criminals could potentially impersonate Pokémon Center, a delivery company, or another retailer and reference details that make their message feel legitimate.
They might claim an order needs to be rescheduled, a delivery fee must be paid, or a refund is waiting. Knowing that you really placed an order can make the bait much harder to spot.
Importantly, there is currently no evidence that the stolen Pokémon Center information is being used in such a campaign. But personalized phishing is a common reason breached contact and transaction information deserves attention.
Key Takeaways
Pokémon Center says the breach occurred at its logistics provider, CEVA, not its own shopping platform.
Names, addresses, phone numbers, email addresses, and order details may have been exposed.
Pokémon Center says payment-card information was not available to CEVA.
Real order details could make future phishing or delivery scams appear more credible.
Customers should independently verify unexpected messages about refunds, cancellations, or deliveries.
3 Easy Safety Actions to Take If Your Information Is Exposed in a Data Breach
Getting a breach notification doesn’t necessarily mean someone has already misused your information. It does mean you should take a few steps to make that information harder to use against you.
1) Find out exactly what was exposed. Read the company’s breach notice carefully. An exposed email address calls for different precautions than a stolen password, Social Security number, financial information, or medical record.
2) Secure the accounts that could be at risk. Change any exposed or reused passwords, use a unique password for every account, and turn on multi-factor authentication where it’s available. If sensitive financial or identity information was stolen, consider a credit freeze or fraud alert as well.
3) Be extra skeptical of messages that know something about you. Breached information can help scammers create convincing emails, texts, and calls. A message that knows your name, address, recent purchase, or other real details isn’t necessarily legitimate. Go directly to the company’s website or app to verify unexpected requests rather than clicking a link or calling a number in the message.
How McAfee Protects Against Breaches
Before a breach
Personal Data Cleanup reduces your digital footprint by removing your personal information from many data broker sites, making it harder for scammers to find and target you.
Online Account Cleanup scans for accounts you no longer use and helps you delete them, along with your personal info.
During a breach
Identity Monitoring watches for your personal information, including email addresses, driver’s license numbers, passport numbers, bank accounts, credit cards, Social Security numbers, phone numbers, and more, across the dark web and known data leaks.
Plus, we alert users on average up to 10 months earlier than similar services, so you can act fast when your personal information appears where it shouldn’t.
After a breach
Scam Detector identifies suspicious texts, emails, and links that often follow major breaches, while web protection blocks malicious websites designed to steal even more of your information.
Other Scam and Security News This Week
FBI warns about callers impersonating federal agents. The FBI’s Boston Division is warning about scammers who spoof its real phone number, pretend victims are connected to crimes, and then try to move conversations onto encrypted messaging apps. The key reminder: caller ID can be faked, and the FBI says it will not call private citizens to demand payment, threaten arrest, or request sensitive information.
CareCloud breach grows to more than 3.75 million patients. Healthcare technology company CareCloud has confirmed with federal regulators that hackers stole personal and medical information belonging to more than 3.75 million people, including Social Security numbers, health information, government-issued ID numbers, and some financial data. Because medical and identity information cannot simply be replaced like a password, affected people should take breach notifications particularly seriously.
Hacker claims millions of corporate directory records were stolen. A cybercriminal known as “TheHatman” is offering databases allegedly taken from the Microsoft Azure and Entra environments of several major companies, although some named organizations dispute that their current systems were breached and say portions of the information appear old. Even older employee information can still be useful for impersonation and targeted phishing, so the claims are worth watching without treating every advertised dataset as independently confirmed.
✓ Treat unexpected delivery messages with caution. Open the retailer or carrier’s official app or website instead of following a link in a text or email.
✓ Don’t trust caller ID alone. Scammers can spoof a legitimate organization’s real phone number.
✓ Use unique passwords and multi-factor authentication. Stolen personal information becomes more dangerous when criminals can also get into your accounts.
✓ Pay attention to breach notices. Knowing exactly what information was exposed helps you recognize the scams criminals may try next.
And we’ll be back next week with more cybersecurity news and scam alerts.
McAfee Labs’ latest investigation into the WeedHack malware campaign found that the threat has continued to evolve even after its original command-and-control infrastructure was disrupted by McAfee. Researchers identified multiple active websites still distributing WeedHack to gamers, often by impersonating legitimate Minecraft clients, offering paid tools for free, or using trusted platforms to make malicious downloads appear credible.
Among the findings:
→ More than 6,300 attempts to access malicious sites were blocked by McAfee WebAdvisor in the past month.
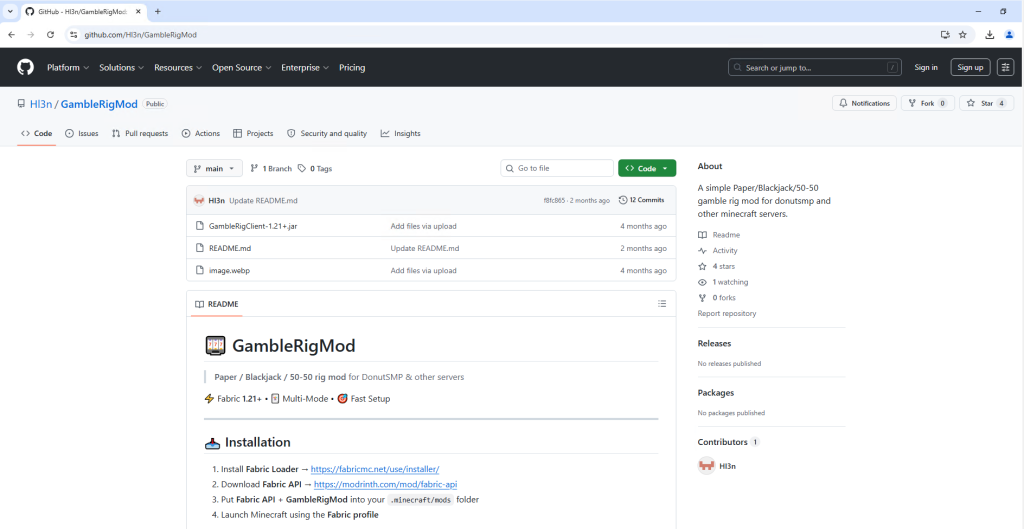
→ Researchers found lookalike gaming websites designed to closely replicate legitimate projects, including their branding, feature lists, FAQs, installation guides, developer credits, and links to genuine GitHub repositories.
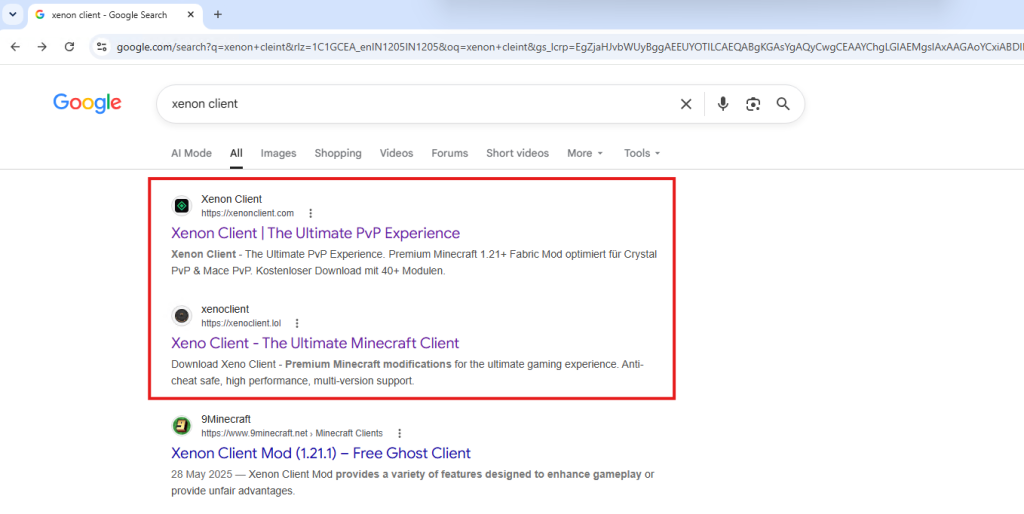
→ In one case, the top two Google results observed by researchers for a popular Minecraft client led to sites distributing WeedHack, demonstrating how SEO poisoning can put malicious downloads directly in gamers’ paths.
→ Nearly half of the malicious URLs identified were Discord links (49.6%), followed by MediaFire (23.4%) and GitHub (8.2%), showing how attackers can use familiar platforms alongside fake websites to distribute malware.
→ Researchers also identified a malicious site built using an AI-powered website creation platform, illustrating how readily available tools can make it easier to launch convincing new malicious sites.
Threats like these show why protection needs to start before a malicious download ever reaches your device. McAfee helps block dangerous websites and downloads before malware has a chance to install, helping you stay focused on the game.
Threats like these show why protection needs to start before a malicious download ever reaches your device. McAfee helps block dangerous websites and downloads before malware has a chance to install, helping you stay focused on the game.
Background
2026 has seen a significant shift in malware tactics, where traditional perimeter breaching techniques are being traded in for more elusive methods, such as AI-powered phishing and widespread deployment of Info-stealer malware. Over 560,000 new malware variants are detected every day, with infostealers accounting for the most active category.
McAfee Labs has also seen a significant spike in Malware-as-a-service (MaaS) campaigns, that offer their customers access to sophisticated infostealers and backdoor malware samples at minimal cost. These campaigns provide detailed tutorials to their customers, teaching them how to target popular gaming software, develop authentic-looking websites, and implement SEO Poisoning techniques in order to bamboozle gamers and infect their systems.
Introduction
Recently, McAfee Labs has covered a Malware-as-a-service campaign, called ‘Weedhack’ that infected over 116,464 gamers and utilized SEO Poisoning techniques to infect such a large user base.
While uncovering the depths of this campaign, we’ve encountered multiple websites and file hosting services that are still active and distributing WeedHack malware. In this article, we cover some of the most prominent examples we’ve encountered in the wild to educate our readers and provide key insights on how to identify and avoid such malicious websites.
Note: This list is not exhaustive, and there may be additional websites that are not covered in this article.
Malicious websites spreading WeedHack
During our investigation of this campaign, we observed that most of these websites appear legitimate, as they are well-crafted and often mimic legitimate websites. We observed a series of dedicated brand-impersonation attacks targeting several popular Minecraft clients.
We published the original article in the first week of July, and, as a result, we’ve seen a disruption in WeedHack’s campaign: its C2 server is no longer active. Consequently, we have observed a shift in tactics by these attackers.
The WeedHack Dashboard has been taken down, yet we’ve discovered websites that are actively spreading WeedHack malware.
Out of these URLs, most belonged to file-hosting services:
49.6% were Discord links
23.4% were MediaFire links,
8.2% were GitHub links
4.6% were Dropbox links
The remaining URLs were customer-facing websites designed to deceive users.
In the last month, McAfee WebAdvisor has prevented more than 6,300 users from accessing these malicious websites. At the time of writing this blog, the following websites were still distributing WeedHack malware.
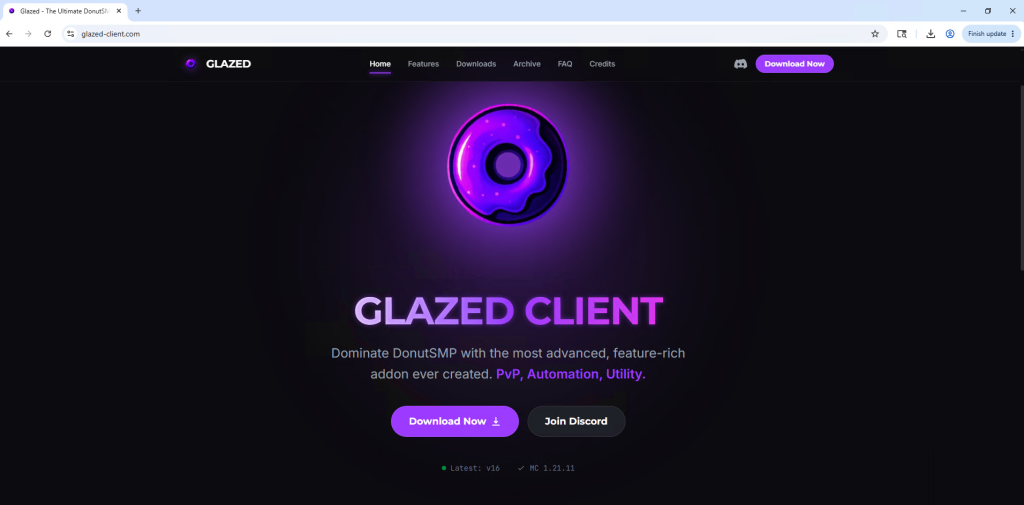
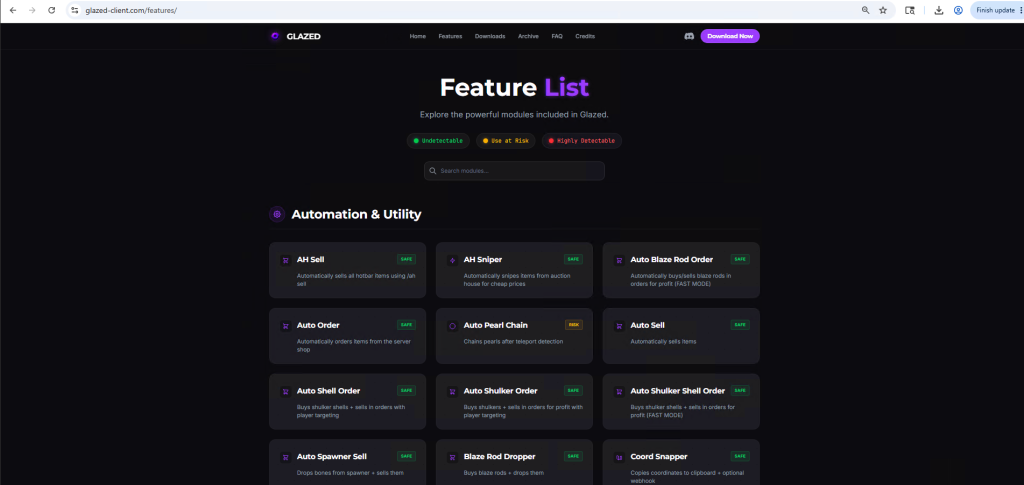
Figure 1: glazed-client landing page
This website ‘glazed-client.com’ replicates the original website called ‘glazedclient.com’. It provides a free and open-source Minecraft add-on called ‘Glazed Client’ designed specifically for DonutSMP server. The website contains a feature list, along with Archive, Credits, and FAQ sections,that are identical to those on the original website.
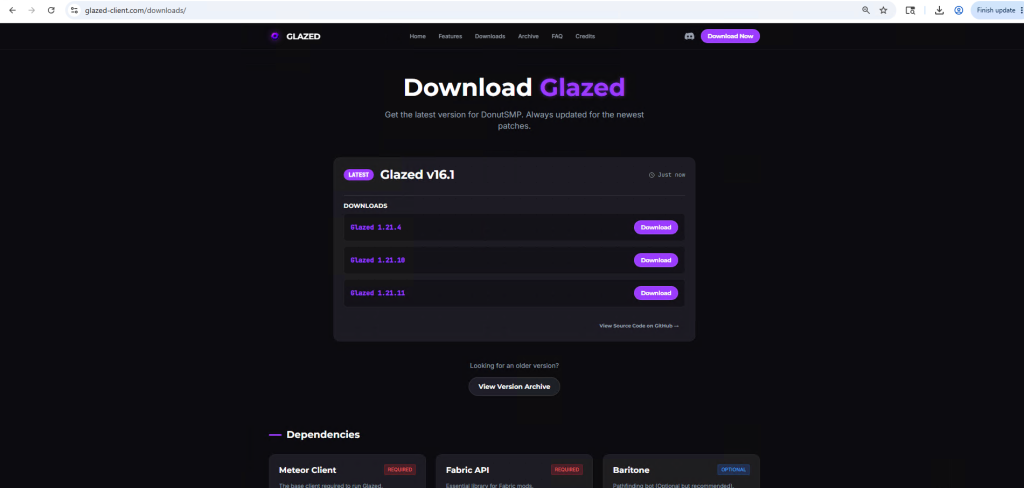
Figure 2: Feature list
Under the download section, the websiteprovides three download options, and all of them are infected with WeedHack.
Figure 3: Download Section
This website has a GitHub link, which links to alegitimate GitHub repositoryin order to build trust with the visitors.
Example 2– radium-client.com
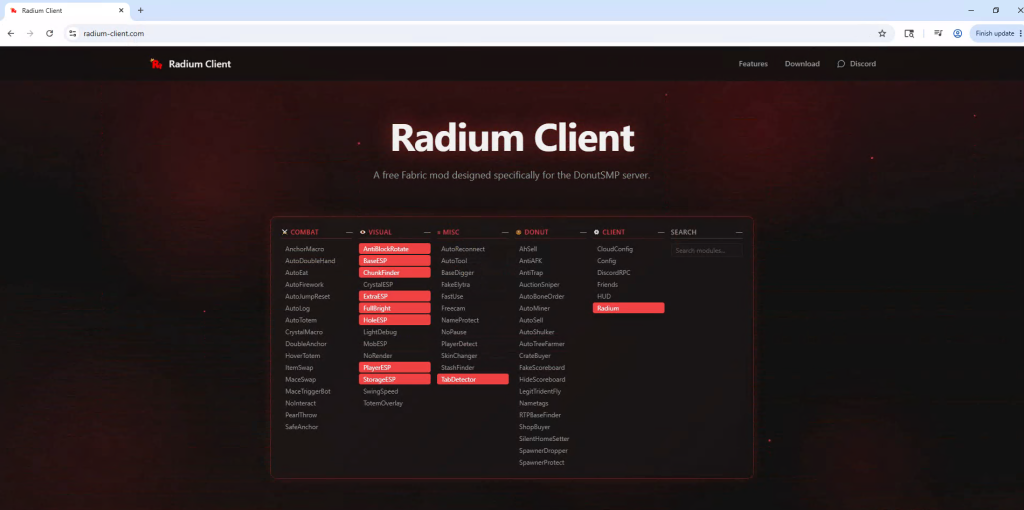
Figure 4: radium-client landing page
The website ‘radium-client.com’ is replicating a legitimate website called ‘radiumclient.com’.The original website offers Minecraft client for $9.99 per month, but the malicious website offers the same tool for free.
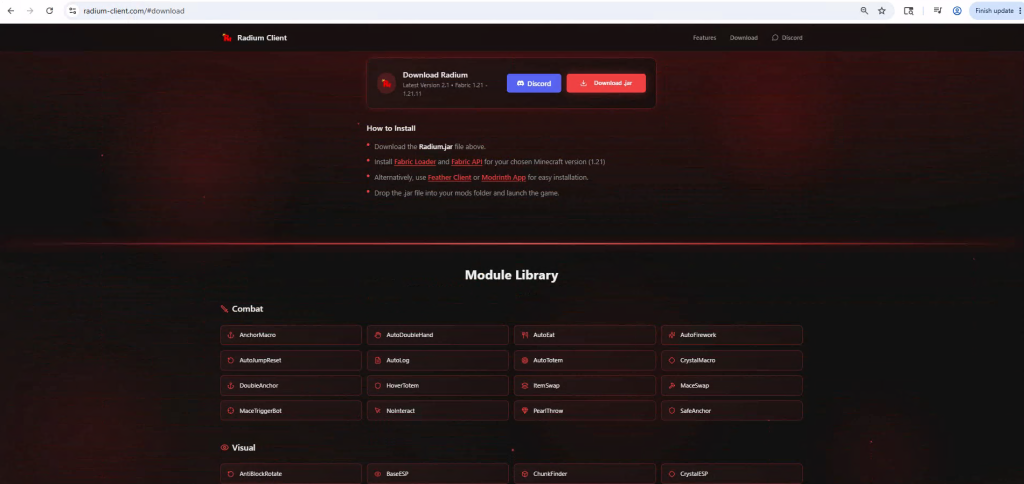
The malicious replica also has a detailedfeatureand download section. The downloaded JAR file is infected with WeedHack.
Figure 5: feature list and download button
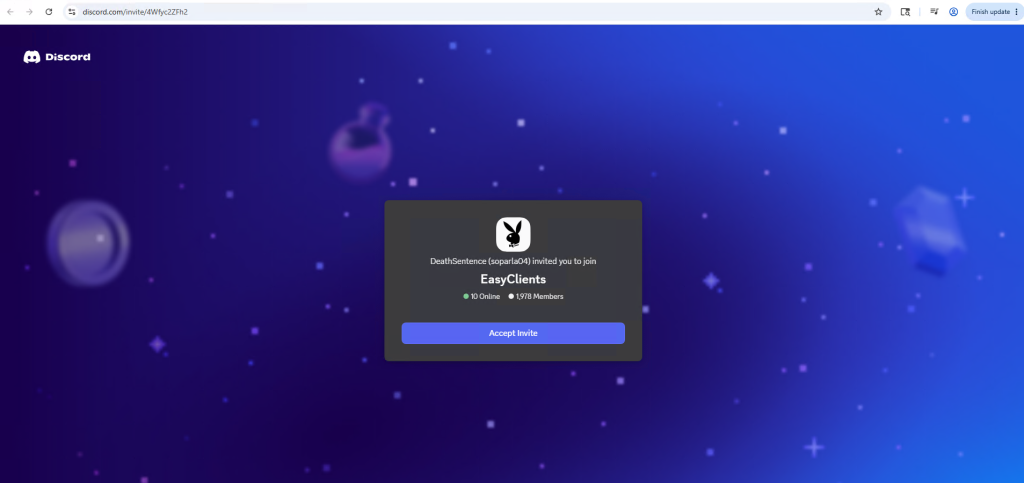
In this instance, the malicious website contains a discord link, similar to the original website, but it pointsto a channel called ‘EasyClients’, that has over 1,900 members.
Figure 6: EasyClients Discord Channel
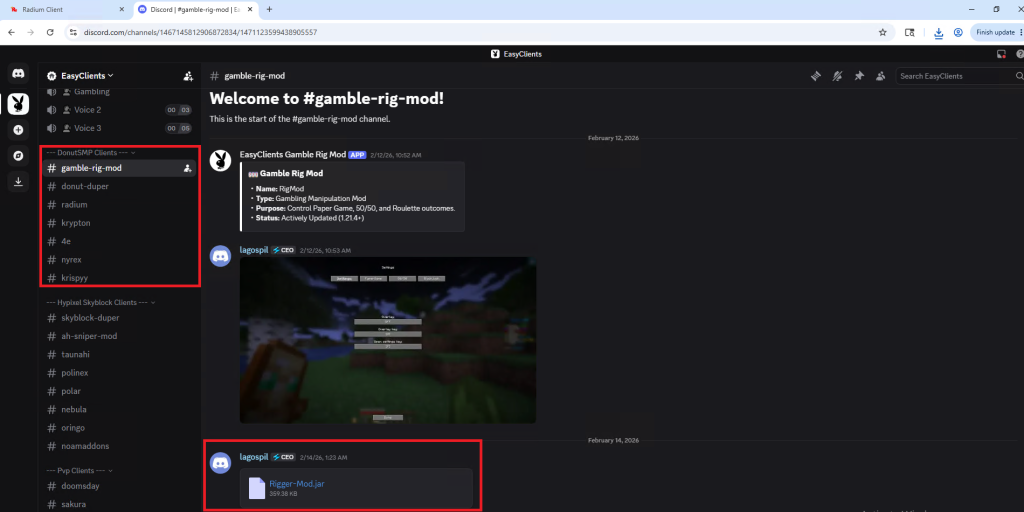
This channeloffers 7 differentDonutSMP clients for free (Image 7, Highlighted in Red) which are also infected with WeedHack.
Figure 7: EasyClients Discord Channel
Example 3 – seedcrackerx.github.io
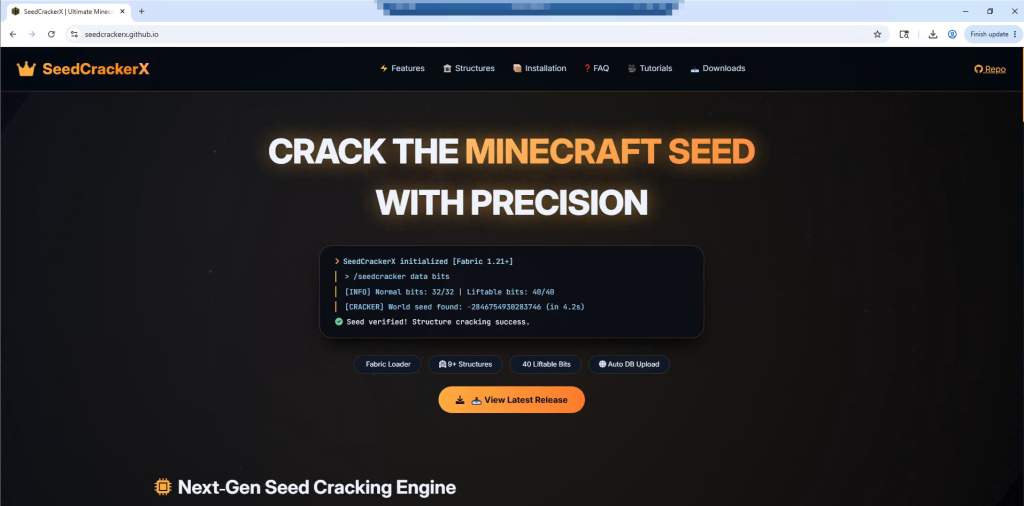
Figure 8: SeedCrackerX’s landing page
In this example, we see GitHub’s web hosting service ‘GitHub.io’ being exploited by attackers. Here they are impersonating ‘SeedCrackerX’ tool, which is a Minecraft seed crackingsoftware capable of identifying the exact world seed used to generate a Minecraftworld.
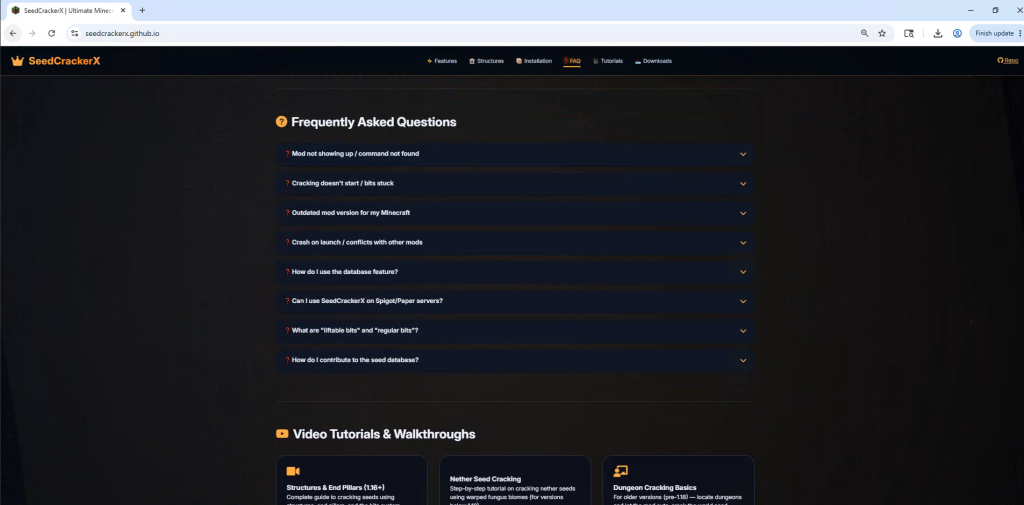
Figure 9: FAQ section
Here, the malicious websites imitate the original website ‘seedcrackerx.com’, by replicating its fonts and color palette. The website also includes an elaborate tutorial and FAQ section, educating the visitors on how to properly install the tool.
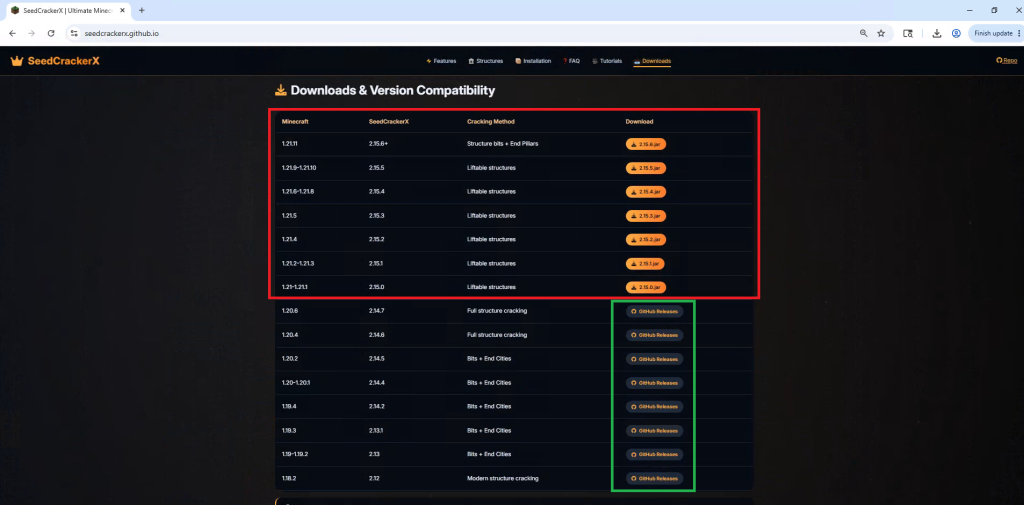
Figure 10: Download section
Under the download section, the website offers seven versions to choose from, but all of them are infected with WeedHack. (Highlighted in Red)
This malicious website has also linked the genuine GitHub repository hosting the SeedCrackerX tool (Highlighted in Green), to appear more legitimate.
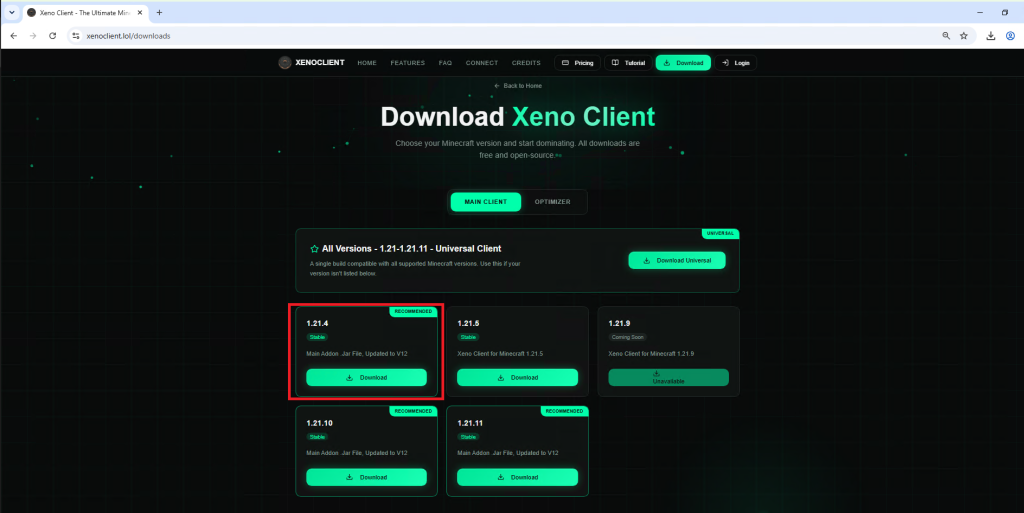
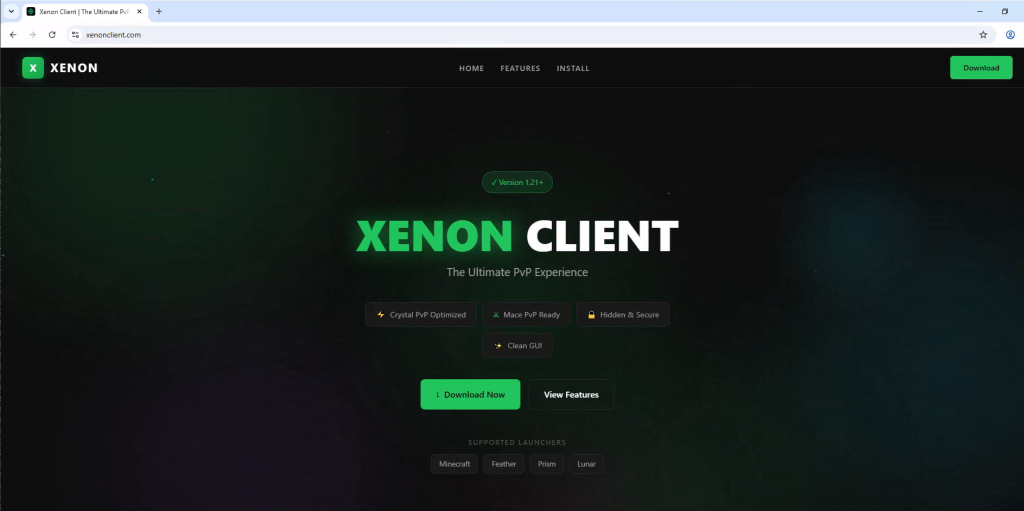
Example 4 – xenoclient.lol and xenonclient.com
Xenon Client is one of the most popular Minecraft Clients, known for being lightweight, community driven and offering niche vanilla-friendly utilities. Given its widespread popularity, this client is a prominent target for threat actors.
Figure 11: Google search results for ‘Xenon Client’
During our research, we identified that the top two Google search results for ‘Xenon Client’directed users to websites (Highlighted in Red) that are spreading WeedHack.
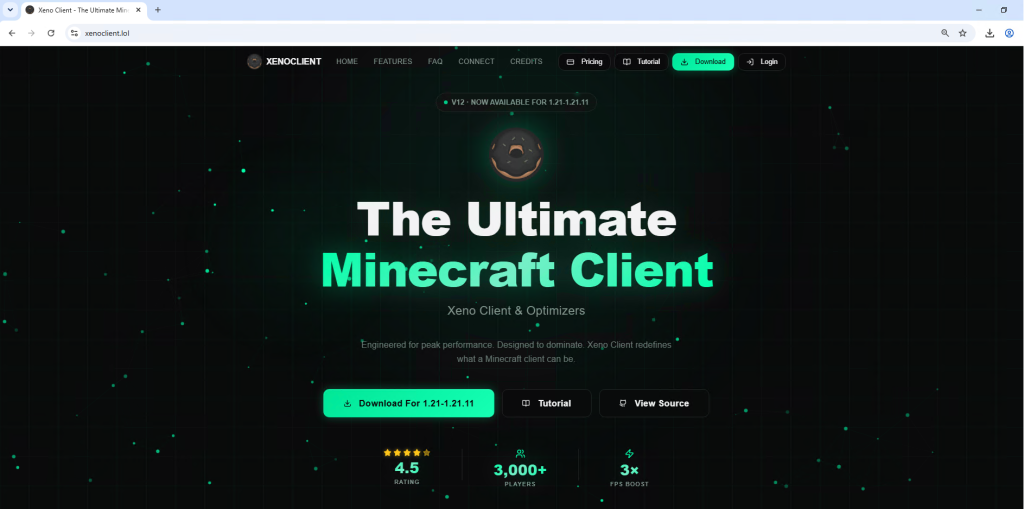
Figure 12: Xenoclient.lol Landing Page
The “xenoclient.lol” website is particularly noteworthy, for the range of features and support it offers. The website includes comprehensive download and installation guides, as well as FAQ and Credits sections. Additionally, it lists the original Xenon Client GitHub repository and features a community section for like-minded gamers, further enhancing its professional appearance.
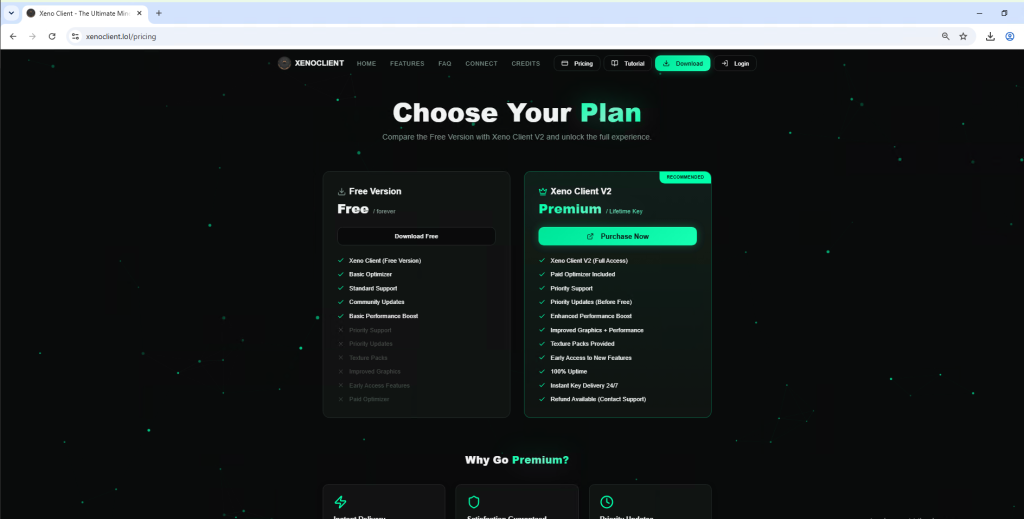
Figure 13: Xenoclient.lol Purchase Options
It offers 2 purchase options for free and premium, where the premium version is listed for $5.
Figure 14: Download Page
The free option, on the other hand, offers six download options for the main client and six additional options for the client optimizer. At the time of writing, only one download link remains operational (highlighted in red), and it delivers a payload infected with WeedHack.
Another website, “xenonclient.com,” is also targeting Minecraft players, luring them with a free version of the same client.
Figure 15: xenonclient.com Landing Page
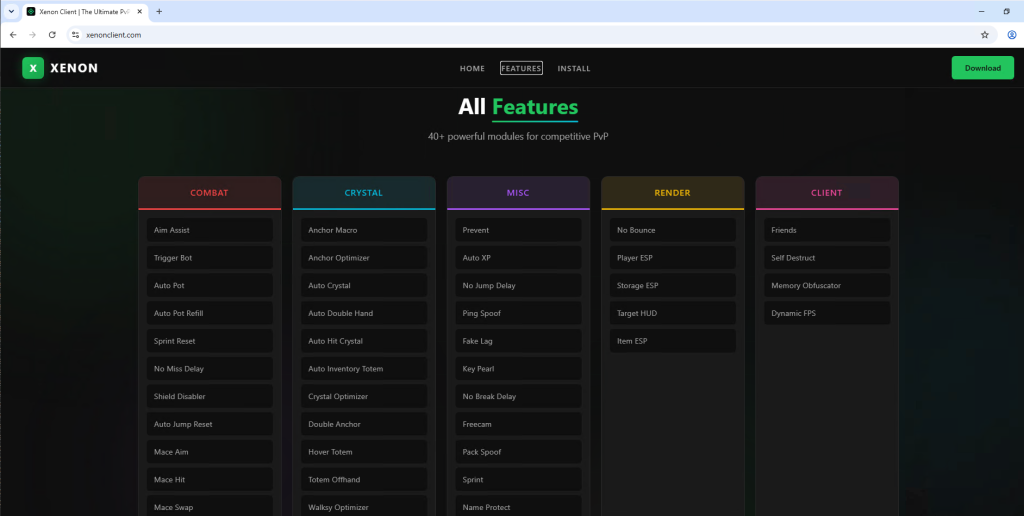
Similar to other websites in the campaign, this site includes an installation guide and a feature list for the Xenon Client to enhance its apparent legitimacy.
Figure 16: Feature List
The final JAR file downloaded from this website infects users with WeedHack.
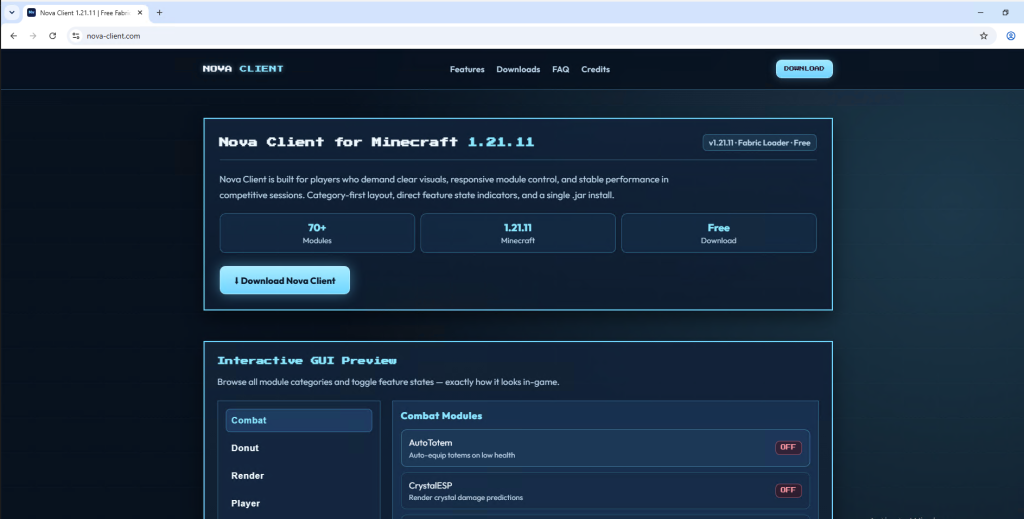
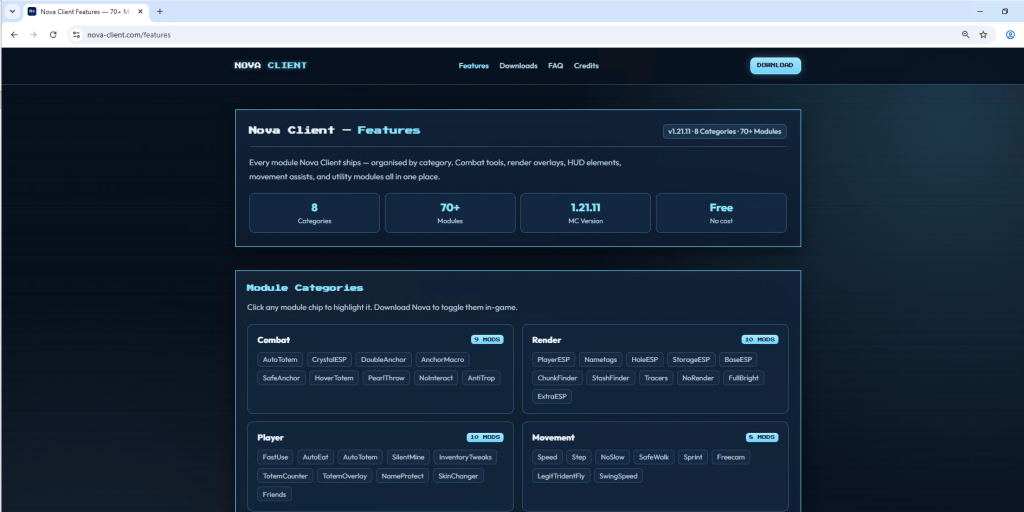
Example 5– nova-client.com
Nova client is anopen-source client designed for Minecraft Bedrock Edition.
Figure 17: Nova-Client’s landing page
This client is an easy target for attackers because it lacks an official website.The legitimate client is hosted on GitHub and Modrinth; however, attackers have created a spoofed website and leveragedSEO poisoning techniques to outrank the official sources in search results.
Figure 18: Feature Section
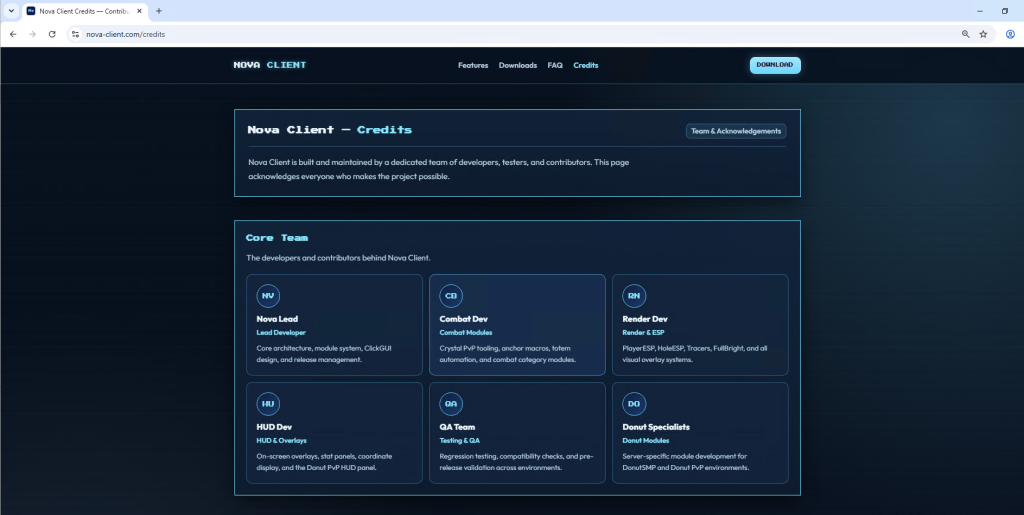
This website also includes a Features page, installation guide, and FAQ section. In addition, it displaysscreenshots from the legitimate Nova Client to deceive users. What is interesting here isthat attackers havealso included a credits section, which is common with legitimate Minecraft client websites.However, they do not mention anyone who has actually worked on the project and instead used generic team names.
Figure 19: Credits Section
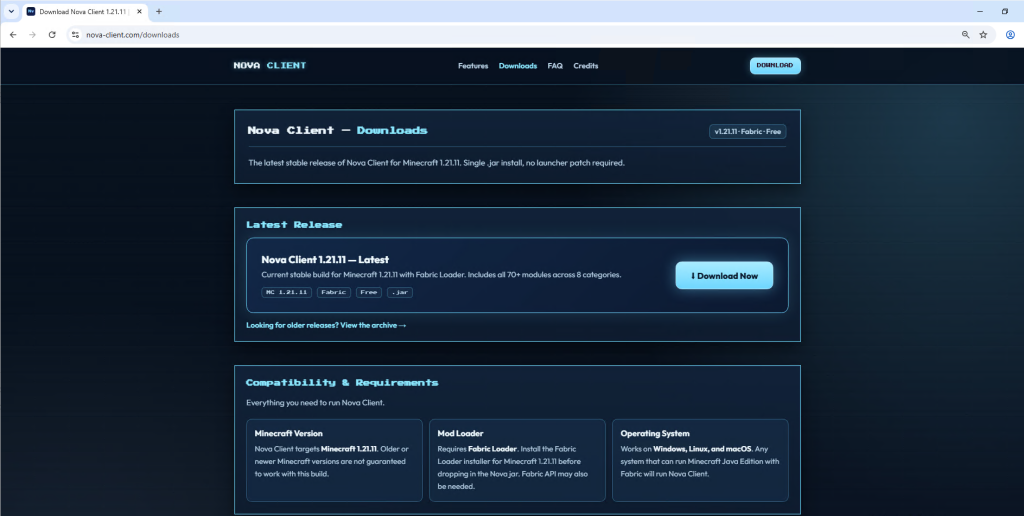
The download section provides Nova Client for Minecraft 1.21.11, but the download file spreads WeedHack malware.
Figure 20: Download Section
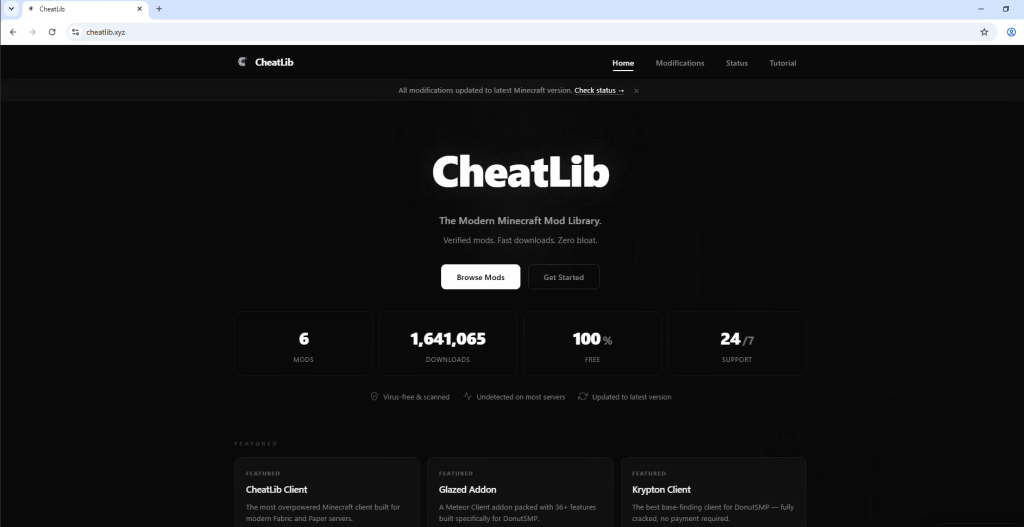
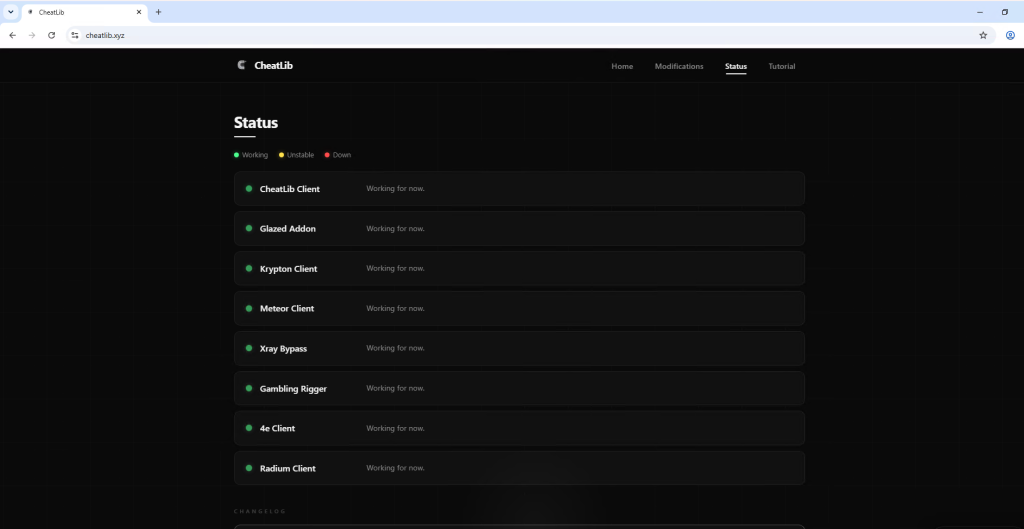
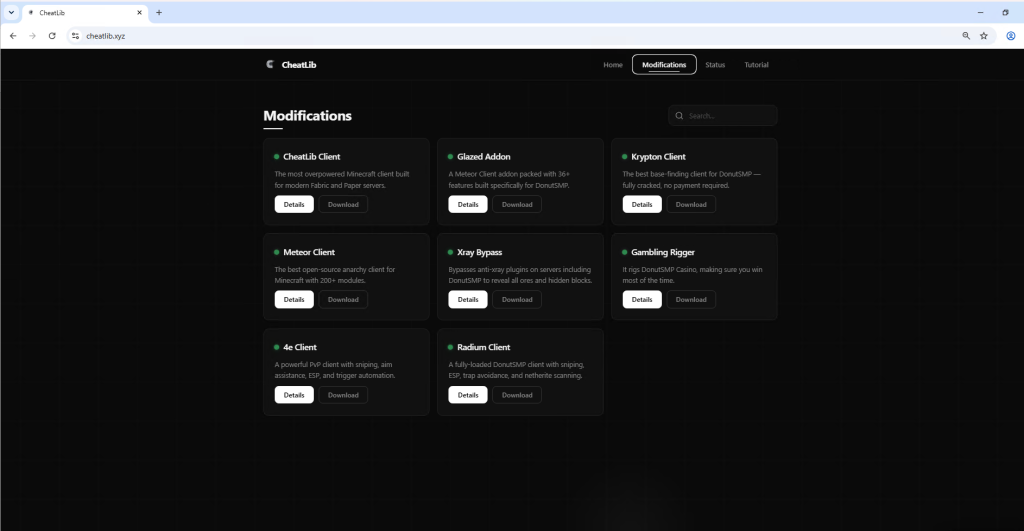
Example 6 – cheatlib.xyz
CheatLibadvertises that their clients have been downloaded over 1.6 million times,are free from malwareand offers round-the-clock support.
Figure 21: CheatLib’s landing page
Similar to other such websites, it also features a setup guide and a FAQ section to address common user issues.
Figure 22: Status Section
They provide eight Minecraft Mods and inform users which Minecraft servers and anti-cheat systems they can bypass, as well as the current status of each mod.
Figure 23: Download Section
Although the website offers eight distinct mods, all eight files share the same hash and distribute the WeedHack payload.
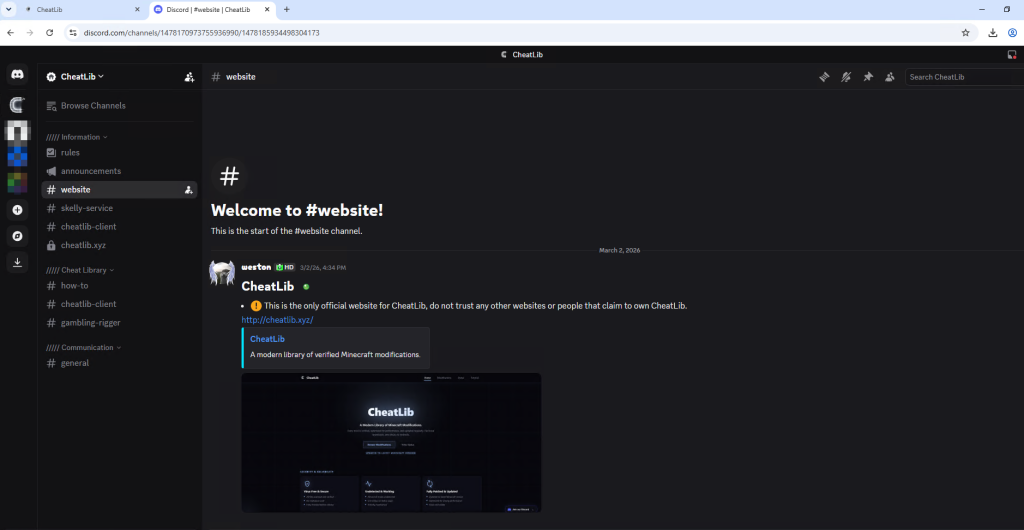
Figure 24: CheatLib Discord Channel
This website also links to a Discord channel called ‘CheatLib’ with over 220 users, which also provides access to WeedHack infected mods.
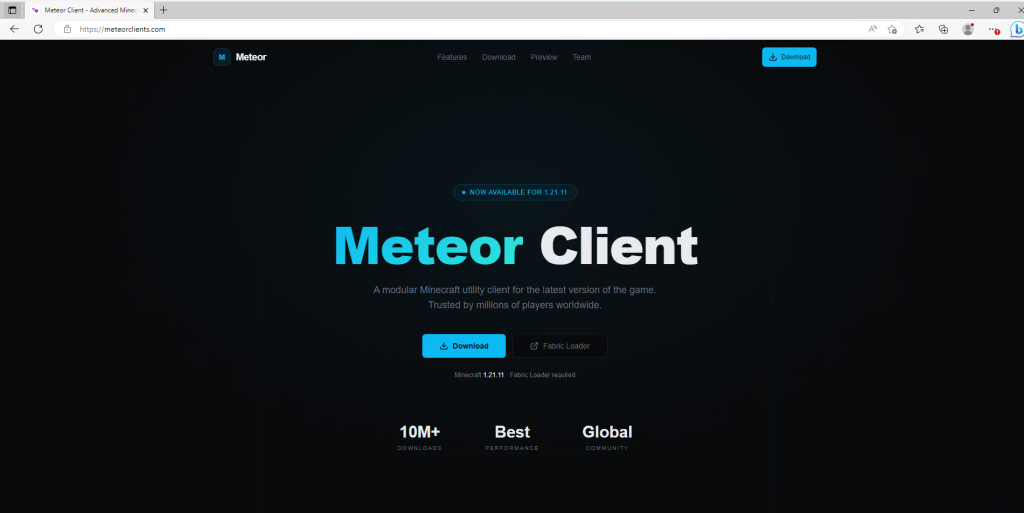
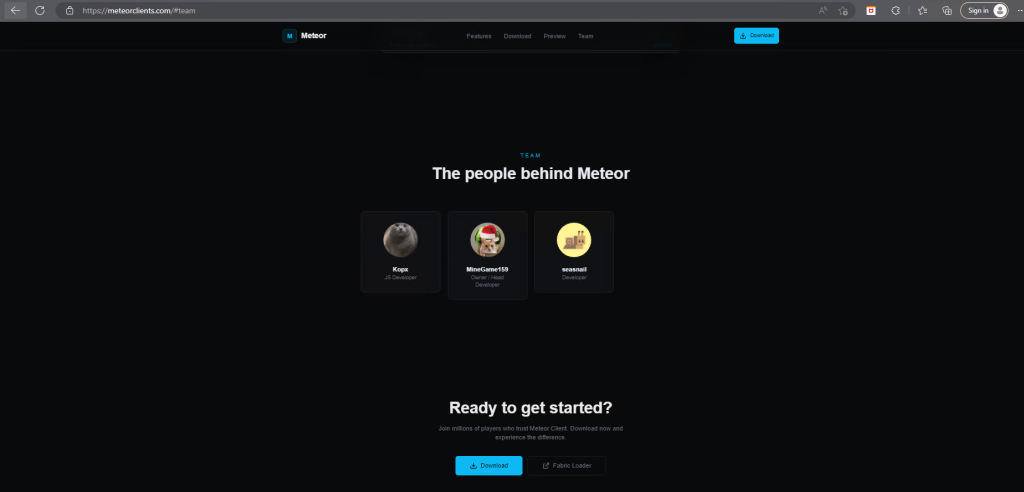
Example 7 – meteorclients.com
Figure 25: Meteor Client’s landing page
This malicious domain ‘meteorclients.com’ is impersonating a legitimate website ‘meteorclient.com’.They claim that this client has been downloaded over 10 million times and has over 15 thousand active users at any given time.
Figure 26: Team Section
The Team section contains the names of the legitimate Meteor Client developers, which appear to have been copied from the project’s official website,to create an appearance of authenticity.
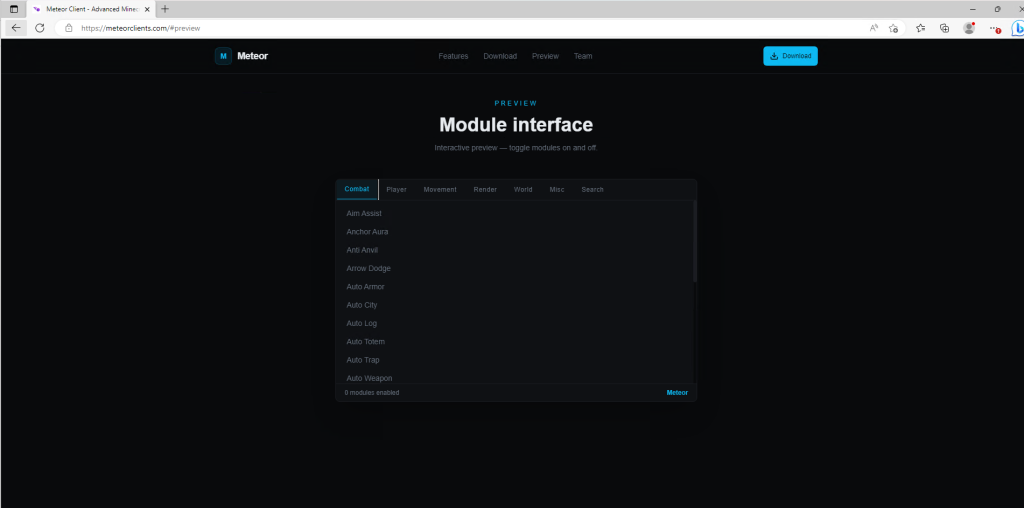
Figure 27: Preview Section
They also provide an interactive preview of Meteor client on the website, enabling users to test and familiarize themselves with the client.The website offers a single download option, which is infected with WeedHack.
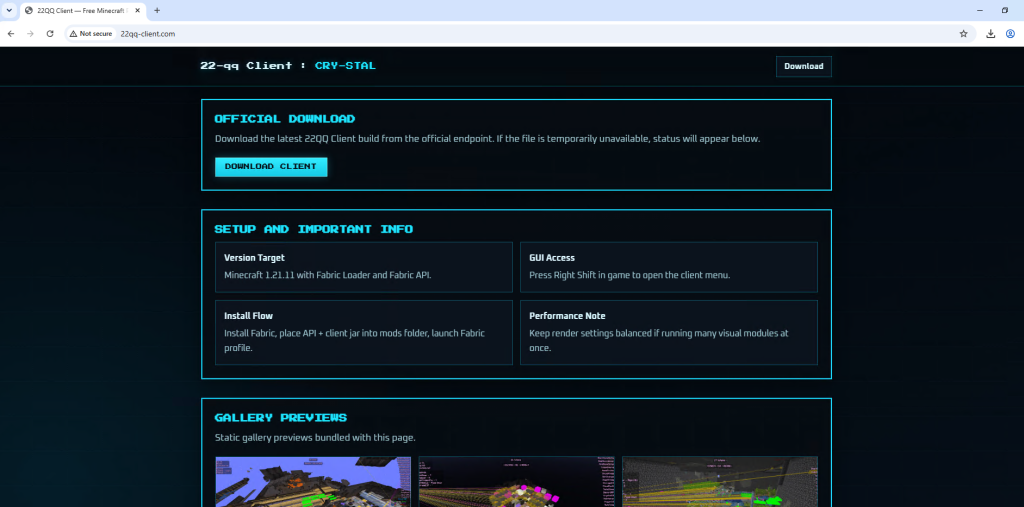
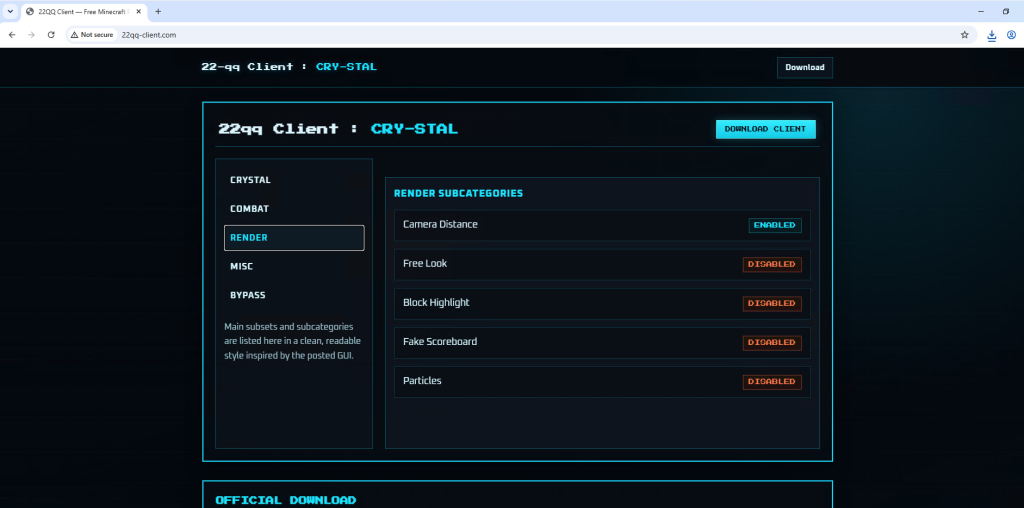
Example 8– 22qq-client.com
22qq-client is a Minecraft Mod for Crystal PVP servers.
Figure 28: 22qq-client’s Landing Page
This mod does not have a dedicated website, and attackers are exploiting this issue. This website is meant toserve as the official page for the client.
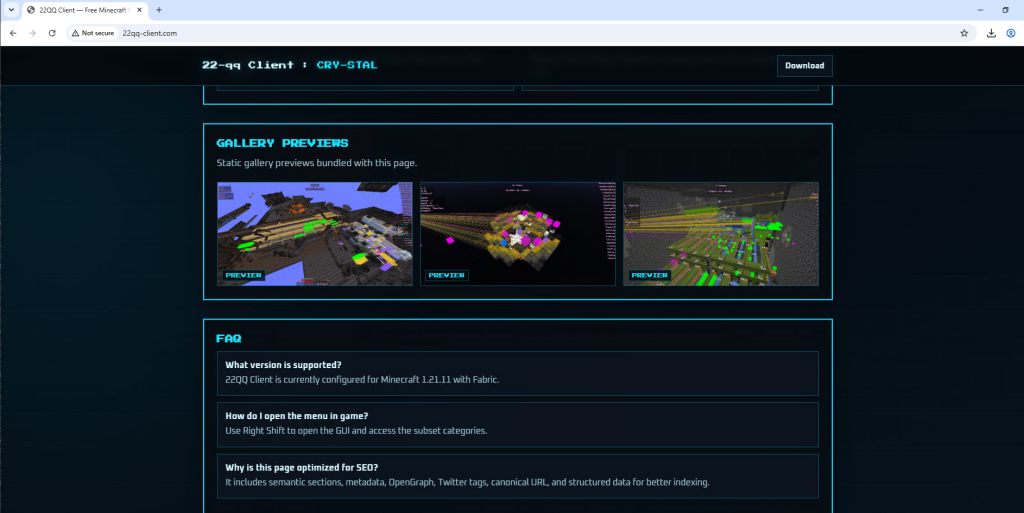
Figure 29: FAQ section.
The attackers attempt to establish credibility by using screenshots from the legitimate client.
Figure 30: Preview of 22-qq.
They also offer an interactive preview of the client to give users an overview of its functionality. This website provides multiple download buttons, but all of them download the same JAR file, which is infected with WeedHack.
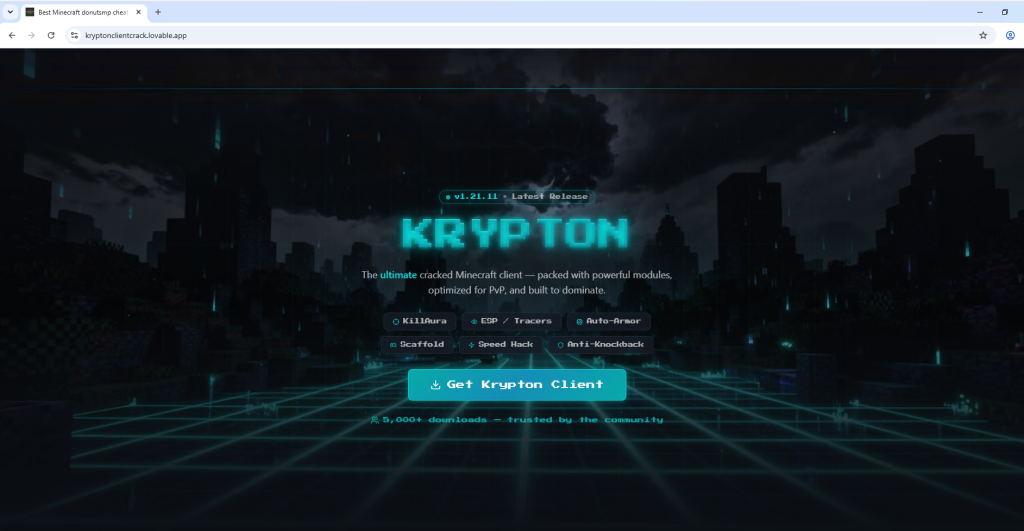
Example 9 – kryptonclientcrack.lovable.app
Krypton Client is a paid Minecraft tool for DonutSMP server, hosted on ‘kryptonclient.org’. This malicious counterpart claims to offer a cracked version of the tool.
Figure 31: Krypton’s Landing Page
The attackers have used an AI-powered tool called ‘lovable.app’ that allows customers to build and launch functional web applications and websites, using natural language. Such toolsmake it easier for attackers to deploy new malicious domains on the fly.
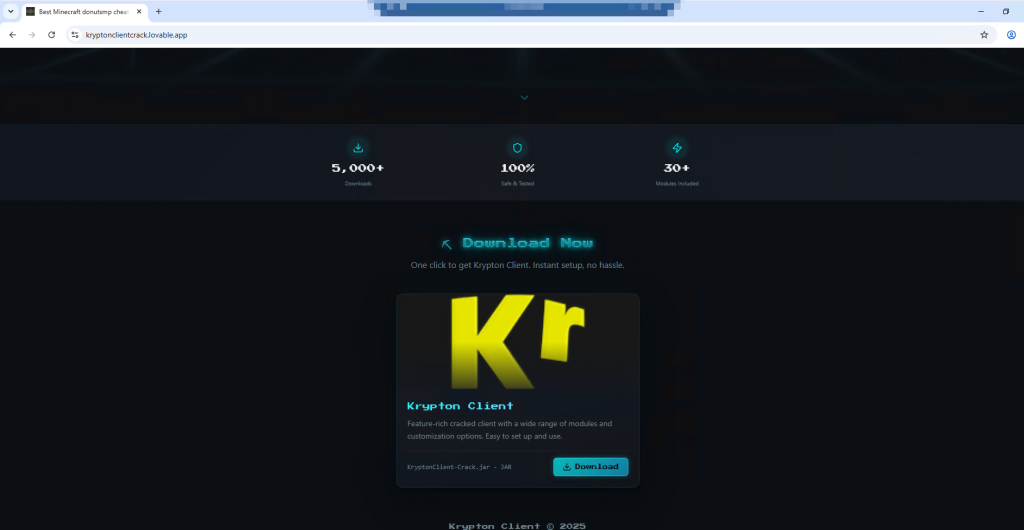
Figure 32: Download Section
The website claims that the tool has been downloaded more than five thousand times and has been thoroughly tested for safety. They offer a single download option, which is infected with WeedHack.
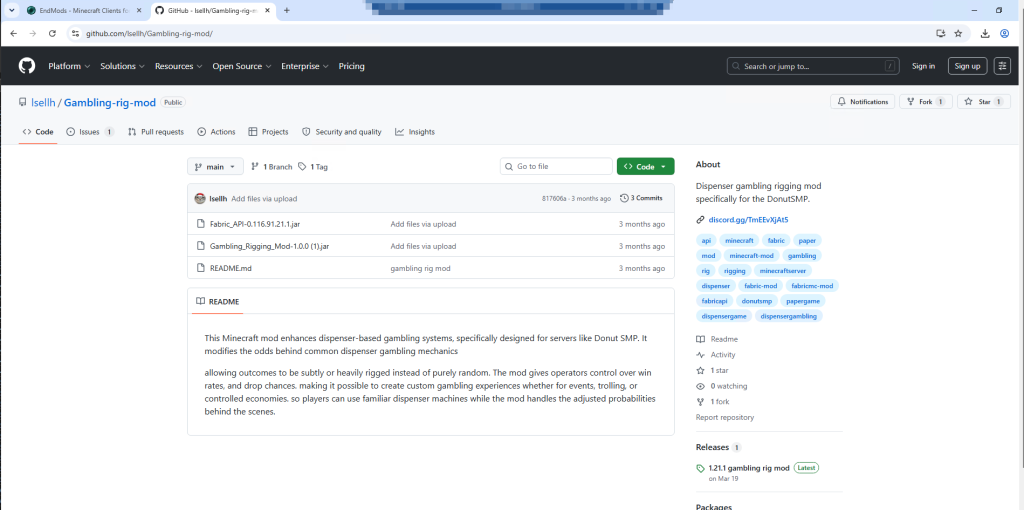
Example 10 – File Hosting Services
In the course of our investigation, we observed that multiple attackers were exploiting various file hosting services to spread malware.
Figure 33: GitHub Repository spreading WeedHack
Links to these websites are then distributed via different communication channels, such as Discord, Reddit and other online platforms.
Figure 34: GitHub Repository spreading WeedHack
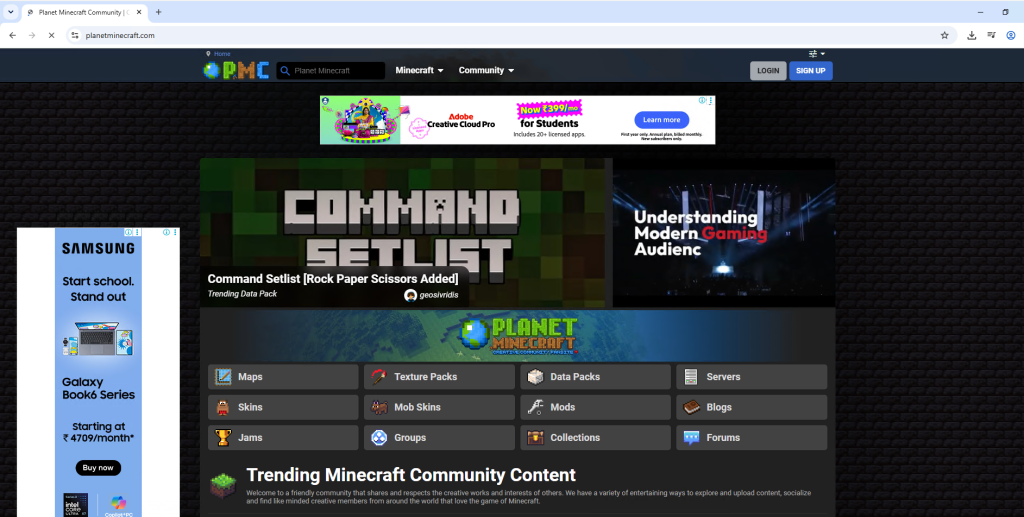
We also observed that threat actors extended their targeting beyond Minecraft clients, compromising various popular and independent community websites within the Minecraft ecosystem.
Figure 35: Planet Minecraft
At the time of this analysis, the following Planet Minecart links were spreading WeedHack malware.
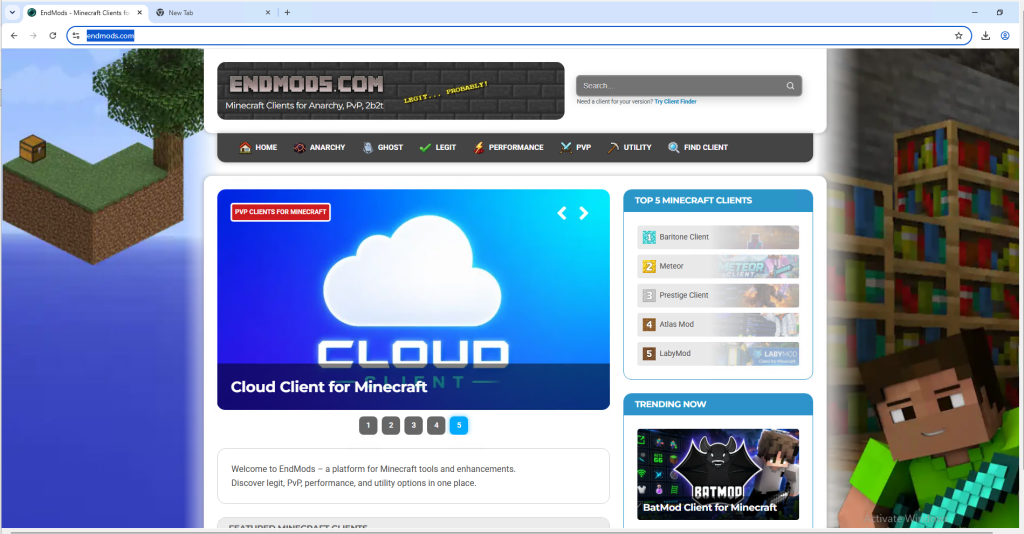
Similarly, we observed another community website, called EndMods was also targeted by WeedHack.
Figure 36: EndMods
The following link is still active, at the time of publication, and is still spreading the WeedHack malware. hxxps://endmods.com/wp-content/uploads/2026/02/KRYPTON-CLIENT1.0.zip
How To Protect Yourself Online
At McAfee Labs, we investigate threats across the digital landscape, and gamers are a frequent target. We’ve seen multiple malware-as-a-service campaigns similar to WeedHack use fake downloads, impersonated websites, malicious mods, and other lures to target gaming communities.
AI-powered tools can make it faster and easier for scammers to create convincing websites, imitate legitimate services, and launch new campaigns at scale. That makes it even more important to know what you’re downloading, and where it’s coming from.
Here are a few ways gamers can stay safer:
→ Stick to trusted sources. Download games, mods, clients, and other files from official developer websites or reputable mod platforms whenever possible. If you can’t verify the source, don’t download it.
→ Never turn off your security software for a download. Be suspicious of any mod, cheat, or client that tells you to disable your antivirus or other protections before installing it.
→ Scan files before opening them. Check downloaded mods, installers, and archives before running them — even if they came from a popular gaming community or website.
→ Be skeptical of offers that seem too good to be true. “Free” premium features, exclusive cheats, cracked software, or paid clients can be used as bait to convince gamers to download malware.
→ Check the URL before you download. Scammers can create lookalike domains and convincing copies of legitimate gaming sites. Small changes in a web address can be a sign you’re on an impersonation site.
→ Pay attention to security warnings. If your antivirus flags a download, don’t automatically assume it’s a false positive. Stop and investigate before allowing the file to run.
→ Keep your devices and software updated. Install updates for your operating system, browser, games, and security software to help protect against known vulnerabilities.
One advertisement featured a pornographic video with a deepfake closely resembling a prominent US politician. Apple removed the app from the App Store after an inquiry from WIRED.
Looking for a free download of this summer’s biggest movie could come with something you definitely didn’t ask for: malware.
Here’s what to watch for.
Fake The Odyssey Downloads Are Hiding Malware
Speaking of Trojan horses….
Security researchers have reportedly identified malicious downloads disguised as pirated copies of The Odyssey, including files designed to look like high-quality movie releases.
Some fake files even use familiar video-player icons and movie-style filenames to appear legitimate.
But instead of opening a movie, downloading or running the file can launch malicious software capable of stealing information from the device. Other scams reportedly use fake streaming sites that ask users to enter personal or payment information to access a supposedly “free” movie.
McAfee researchers routinely see cybercriminals attach malware to the things people are already searching for, especially popular movies, TV shows, games, mods, and software.
Infostealers designed to collect passwords, browser sessions, payment information, or cryptocurrency data
Trojans that give an attacker access to your device
Loaders that install additional malware
Fake browser updates or extensions that redirect you to scams or malicious websites
One especially obvious warning sign: movies should not arrive as executable .exe files. Legitimate video files generally use formats such as .mp4, .mkv, or .avi.
When in doubt, don’t download it.
How McAfee Protects Against Malware
With McAfee+, multiple layers can help protect you when a tempting download isn’t what it claims to be:
Device Security helps detect malicious apps, files, and downloads before they can compromise your device.
Web Protection helps block risky websites, including malicious download pages, even if you accidentally click.
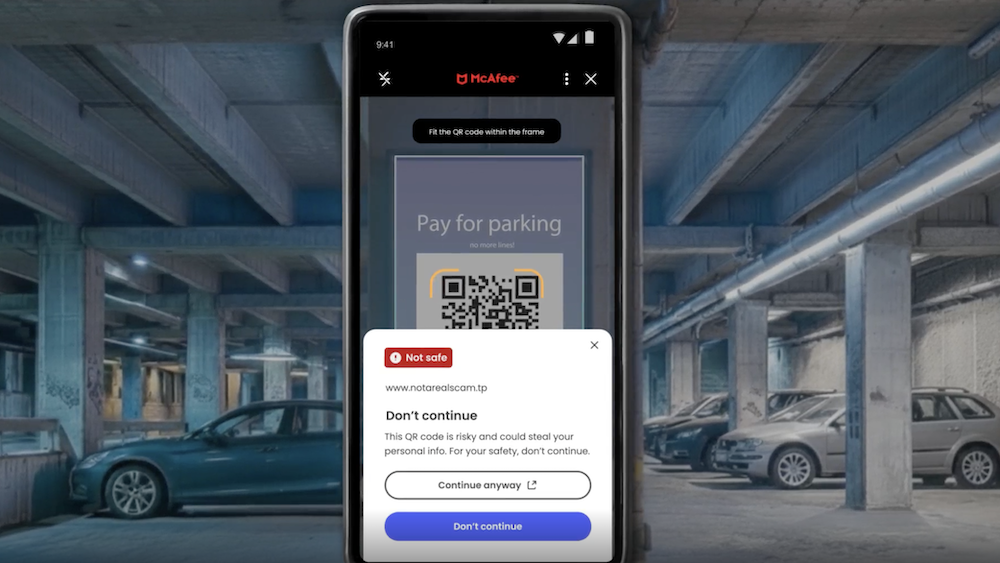
Scam Detector flags suspicious texts, emails, links, QR codes, and other messages that may try to direct you toward fraudulent sites.
Identity Monitoring alerts you if your personal information appears in known data leaks or on the dark web so you can take action quickly.
Together, these protections help address both sides of fake-download scams: stopping malware before it gets onto your device and helping protect your information if criminals try to steal it.
Other Scam and Security News This Week
Here are some other breaches, scams, and cybersecurity headlines making waves this week:
Trezor breach reportedly exposes information belonging to nearly 14,000 crypto customers.
Hardware wallet maker Trezor says a breach involving one of its shipping providers exposed personal information including names, email addresses, phone numbers, and home addresses for thousands of customers.
McAfee’s 2026 State of the Scamiverse predicted that crypto and financial scams were likely to intensify this year, and cryptocurrency-related messages remain among the scams McAfee Scam Detector regularly identifies and blocks.
New threat research found organizations experienced an average of 2,336 cyberattacks per week in July, a 16% increase from the previous year, while reported ransomware victims also rose sharply. Education, government, telecommunications, and other major sectors remained frequent targets.
Android malware can turn a victim’s phone into part of a contactless-payment scam.
Researchers investigating the targeted WindRelay campaign say criminals impersonated banks over the phone, persuaded victims to install malicious Android apps, and then instructed them to tap their physical bank cards against their phones.
That allowed attackers to relay contactless card information in real time, with researchers reporting some attacks unfolded during calls lasting only about 13 minutes.
✓ Stream and download from legitimate sources. New theatrical releases appearing for free on unfamiliar websites should immediately raise suspicion.
✓ Check the actual file type before opening a download. A movie should never require you to run an .exe application.
✓ Never install a “special player,” browser update, or extension just to watch a movie. Close the page and go directly to a trusted streaming service instead.
✓ Treat urgency and exclusivity as warning signs. “Watch it before everyone else,” “leaked copy,” and “limited access” are designed to get you clicking before you think.
And we’ll be back next week with more cybersecurity news and scam alerts.
Records obtained by WIRED detail hundreds of allegations of Customs and Border Protection workers misusing internal tools to look up romantic interests and track colleagues’ cell phones.
Millions of gamers are counting down the days until this fall’s biggest releases.
After more than a decade of anticipation, Grand Theft Auto VI is finally set to launch this November. Surprise indie hit Meccha Chameleon has exploded across Twitch and YouTube after selling millions of copies within days. And highly anticipated titles like Call of Duty: Modern Warfare 4, Minecraft Dungeons 2, Phantom Blade Zero, Marvel’s Wolverine, and dozens of others are keeping players glued to trailers, wishlists, Discord servers, and preorder pages.
Scammers are watching those trends.
Whenever millions of people rush to search for the same game, criminals quickly create fake downloads, unofficial mobile apps and servers, counterfeit storefronts, phishing pages, and cheat toolsdesigned to steal money, credentials, or personal information.
This year is no exception.
Here’s how scammers are taking advantage of 2026’s biggest gaming moments, and how you can avoid becoming their next target, according to McAfee’s experts:
The Most Common Gaming Scams and How to Avoid Them, According to McAfee
Most gaming scams fall into a handful of predictable categories. Once you know what to look for, they’re much easier to spot.
Here are some of the most common scams McAfee protection prevents
Since January 2026, the campaign has infected more than 116,000 devices, averaging roughly 2,000 to 3,000 new infections every day. Attackers lured players through fake mod websites and convincing YouTube videos before installing malware capable of stealing passwords, cryptocurrency wallets, Discord credentials, Minecraft accounts, and more.
Ultimately these gaming attacks can expose players to:
Malware infections
Account theft
Password theft
Data breaches
Spyware monitoring cameras and microphones
Spyware monitoring keyboard and mouse inputs
Permanent game bans
One of the campaign’s most concerning findings wasn’t just the malware itself, it was how inexpensive and accessible the tools had become. The malware was marketed almost like legitimate software, lowering the barrier for inexperienced attackers and helping spread scams throughout gaming communities.
The lesson isn’t to avoid every cheat, unlock, or community-created project. It’s to be skeptical whenever someone promises something that seems too good to be true.
Meccha Chameleon Shows How Quickly Scammers Embrace Viral Games
Few people predicted Meccha Chameleon would become one of the biggest surprise gaming success stories of the year.
The inexpensive indie title reportedly sold more than two million copies within days, fueled largely by livestreams, social media clips, and word of mouth. Unfortunately, that kind of overnight success doesn’t just attract new players.
According to PC Gamer,players have already begun using automated “auto-paint” cheats that scan the environment and instantly camouflage characters, removing much of the creativity and skill the game was designed around.
The game’s popularity has also created confusion about where players can safely download it.
McAfee researchers recently identified multiple Android apps and an unofficial piracy site using the Meccha Chameleon name, despite the game’s independent developer not announcing an official Android release.
Here’s how we saw it play out
First a gamer might navigate to this piracy site to download a free game. The game may not come with malware, but malware is still distributed during the process.
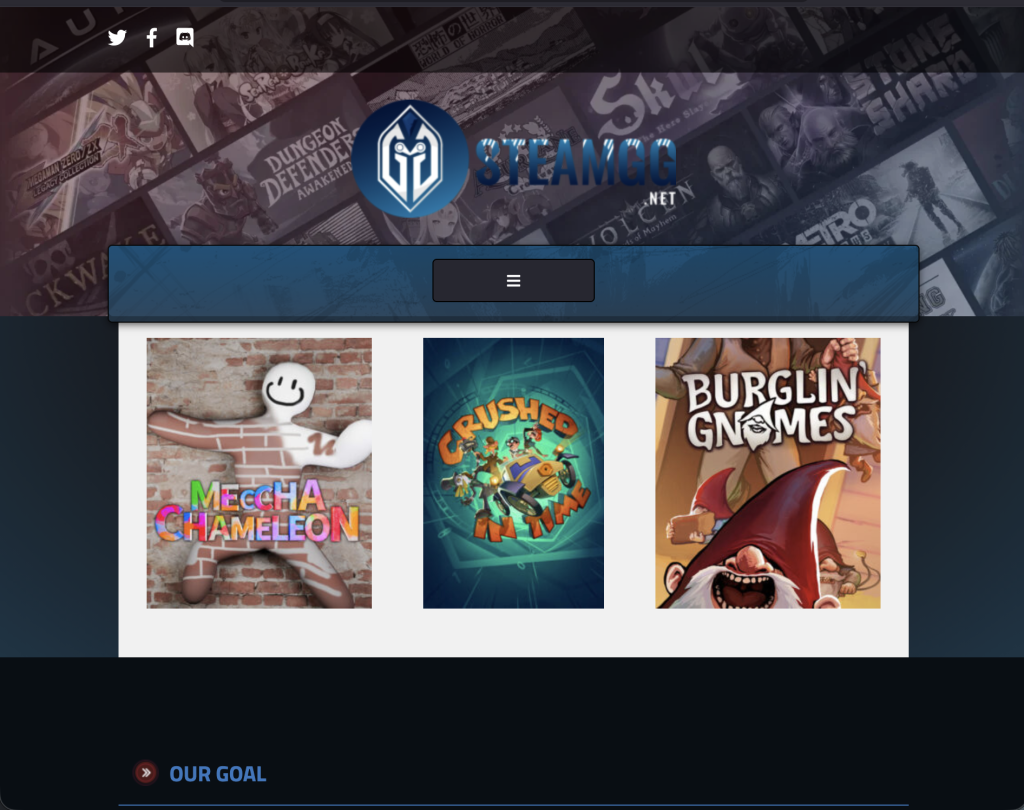
Here we see steamgg[.]net, a piracy site to download free games. Here you see they offer a download of Meccha Chameleon (not malicious).
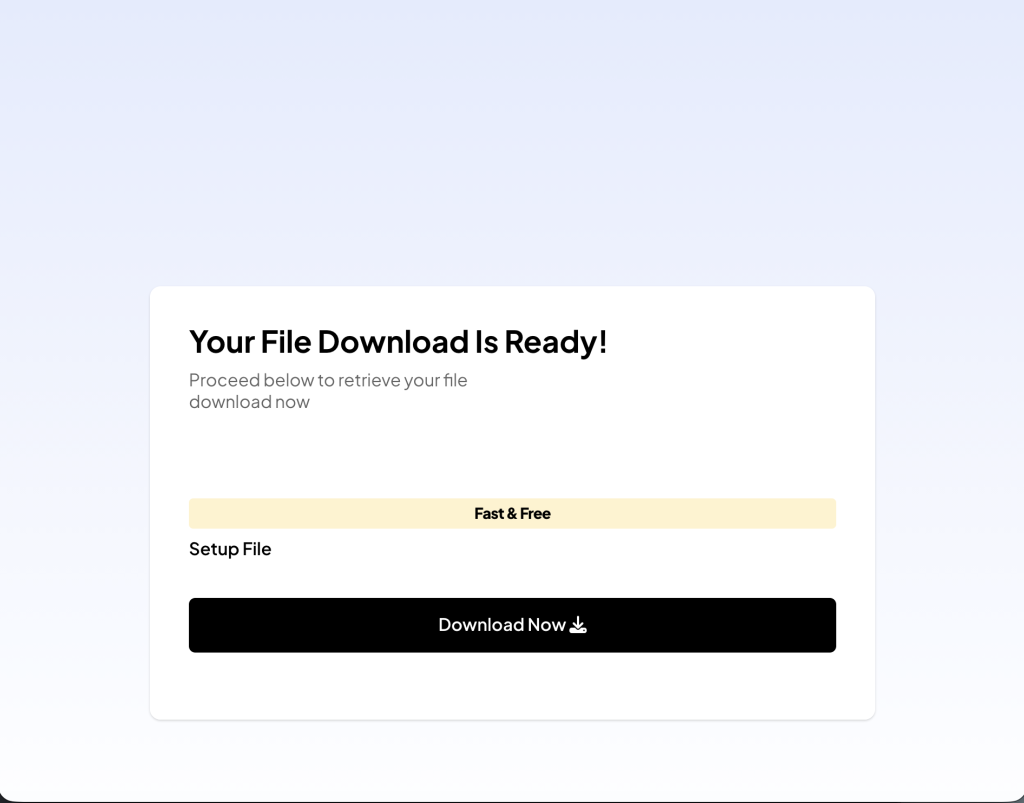
But when you click download, it opens a misleading new tab like this one below.
This new tab tricks the user into thinking they are downloading a game from steamgg[.]net. They are actually being redirected to a completely unrelated download.
In cases like this, unauthorized sites and apps trick users into giving unwanted access to their information and devices.
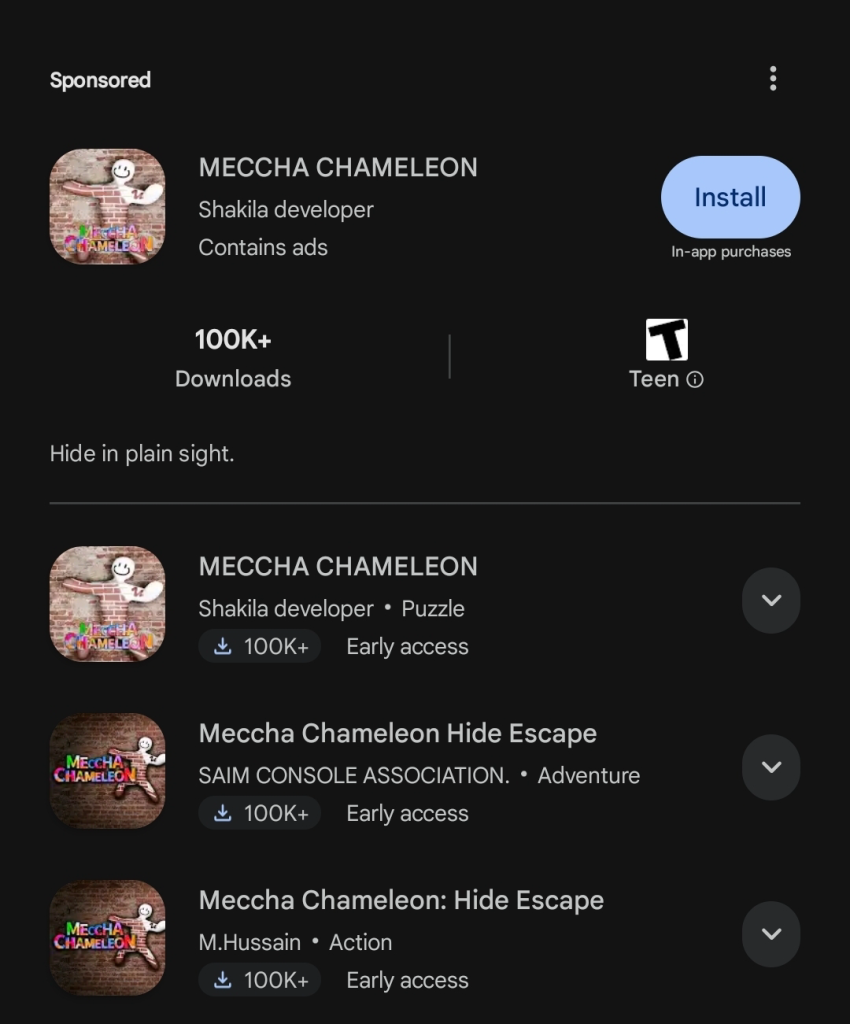
Here we see examples of fake versions of Meccha Chameleon uploaded to the Google Play Store
*Note: The unauthorized apps shown here have since been reported and taken down. While not confirmed to be malicious, hundreds of people had already downloaded and given security permissions to these apps.*
“Repackaged or unauthorized apps and sites are a major risk with viral games,” says McAfee Threat Researcher and lifelong gamer Charles McFarland.
“Because many players are unfamiliar with the original developer, it’s easier for unauthorized apps and copycat listings to blend into app stores,” McFarland explains. “Once installed, the app can have free access to your phone’s data, texts, contacts, and more.”
Before downloading a newly popular game, especially on mobile, take a moment to verify that the developer has actually released it for your device.
Is This GTA 6 Download Legit? How to Spot Fake Early Access Scams
If there’s one game scammers are betting people will search for this fall, it’s Grand Theft Auto VI.
Rockstar Games officially opened global preorders on June 25, and the game launches worldwide on November 19, 2026 for PlayStation 5 and Xbox Series X|S. Digital preorders can begin preloading on November 12.
The problem?Those offers promise something Rockstar isn’t selling.
If a website claims it can provide a playable version of GTA 6 before Rockstar’s official launch, treat it as a major warning sign.
Scammers know players have waited more than a decade for the next Grand Theft Auto. They’re counting on excitement to outweigh skepticism.
“Every major game launch brings a noticeable increase in gaming-themed scams. We regularly see McAfee protecting customers from malicious downloads, fake websites, and other threats that capitalize on the excitement around new releases,” McFarland says.
“As a gamer myself, I know the excitement of jumping into a long-awaited game with my son, but it’s worth taking an extra minute to download from an official or authorized source instead of rushing to be first.”
Whenever possible, verify preorder information directly through Rockstar Games or trusted digital storefronts rather than clicking links shared through social media posts, livestream chats, YouTube comments, or unsolicited messages and advertisements.
Official storefront
Trending and Upcoming Games
Steam
Meccha Chameleon, Dune: Awakening, Metal Gear Solid: Master Collection Vol. 2, Silent Hill: Townfall, Call of Duty: Modern Warfare 4, Phantom Blade Zero, No Rest for the Wicked, Planet Zoo 2, Kingdom Hearts Collections, Ace Combat 8, Gears of War: E-Day (PC), Minecraft Dungeons 2 and many other PC releases
PlayStation Store
Grand Theft Auto VI, Marvel’s Wolverine, Phantom Blade Zero, Onimusha: Way of the Sword, Metal Gear Solid: Master Collection Vol. 2, Call of Duty: Modern Warfare 4, Dune: Awakening, Silent Hill: Townfall and other PlayStation releases
Xbox Store
Grand Theft Auto VI, Gears of War: E-Day, Call of Duty: Modern Warfare 4, Dune: Awakening, Ace Combat 8, Kingdom Hearts Collections and other Xbox releases
Nintendo eShop
Rhythm Heaven Groove, Splatoon Raiders, Fire Emblem: Fortune’s Weave, Harvest Moon: Echoes of Teradea, Nintendo Switch Sports Resort, The Legend of Zelda: Ocarina of Time Remake and other Nintendo titles
*Availability may vary by platform as publishers announce additional releases.
If you can’t find a game on one of its official storefronts, that’s a good reason to pause before downloading it elsewhere.
How McAfee Protects Gamers
Gaming should be about exploring new worlds, not accidentally downloading malware.
McAfee helps protect players before, during, and after they click.
Web Protection helps block known malicious websites before fake downloads ever reach your device.
Award-winning antivirus detects and blocks malware hidden inside suspicious installers, cheats, and unofficial software.
If a file is flagged, Threat Explainer provides a clear, plain-language explanation of why it’s considered risky, helping you make informed decisions instead of guessing whether a warning is legitimate.
McAfee earned the lowest overall impact score among the 20 products tested and received the highest possible rating, 3 Stars ADVANCED+. In other words, you get strong protection without sacrificing performance or slowing your game.
Whether you’re preordering GTA 6, trying the latest indie hit, or installing a new Minecraft mod, slowing down long enough to verify where you’re downloading from remains one of the simplest, and most effective, ways to protect yourself.
Frequently Asked Questions
FAQs
Q: Is GTA 6 early access real?
A: No. Rockstar Games has announced pre-orders and pre-loading ahead of launch, but there is no legitimate way to play GTA 6 early through unofficial websites. Be wary of any site claiming to sell “VIP access,” beta keys, or downloadable copies before the official release date.
Q: Is it safe to pre-order GTA 6 from any website?
A: Stick to Rockstar Games or authorized retailers and digital storefronts like the PlayStation Store and Xbox Store. Avoid unfamiliar websites advertising deep discounts, exclusive editions, or cryptocurrency-only payments.
Q: Does Meccha Chameleon have an official Android or iPhone app?
A: At the time of writing, the game’s developer has not announced an official mobile version. If you find Meccha Chameleon in an app store, verify that it’s published by the official developer before downloading.
Q: Are game cheats and trainers safe to download?
A: Not always. While some cheats simply modify gameplay, others can contain malware, steal passwords, or compromise gaming accounts. Downloading cheats from unofficial websites or Discord servers carries additional risk.
Q: Can Minecraft mods contain malware?
A: Yes. While many Minecraft mods are legitimate, cybercriminals have repeatedly used fake mods and clients to distribute malware. Download mods only from trusted community repositories or verified developer pages.
Q: How can I tell if a game download is legitimate?
A: Download games directly from the publisher’s official website or trusted digital storefronts like Steam, PlayStation Store, Xbox Store, Nintendo eShop, or Epic Games Store. Avoid links shared through YouTube comments, Discord messages, or unofficial social media posts.
Q: Why do scammers target popular game releases?
A: High-profile launches create excitement and urgency, making players more likely to click on fake download links, preorder scams, cheat tools, or unofficial apps without stopping to verify they’re legitimate.
Q: What are the biggest gaming scams to watch for in 2026?
A: Common gaming scams include fake early access offers, counterfeit game downloads, unofficial mobile apps, cheat software bundled with malware, phishing pages posing as gaming platforms, and fake giveaways promising free games or in-game items.
Q: Can antivirus slow down gaming performance?
A: Some security software can affect system performance, but independent testing has shown that solutions vary significantly. Look for products that perform well in third-party performance benchmarks while still providing strong protection against malware and phishing attacks. McAfee Total Protection recently took first place in the latest AV-Comparatives PC Performance Test, an independent benchmark that measures how much security software impacts your computer’s performance. In other words, McAfee provides strong protection without sacrificing performance or slowing your game.
Q: What’s the safest way to download new games this fall?
A: Buy or download games directly from official publishers and trusted storefronts, keep your operating system and antivirus up to date, avoid unofficial cheats or cracked versions, and verify any unexpected links before clicking.
Experts allege that two recent incidents in California show the extreme lengths that criminal organizations are willing to go to to steal servers and other gear meant for data centers.
 Login






 The breach affected customer information from bookings and airport Wi-Fi registrations.